
CatSniffer-Firmware
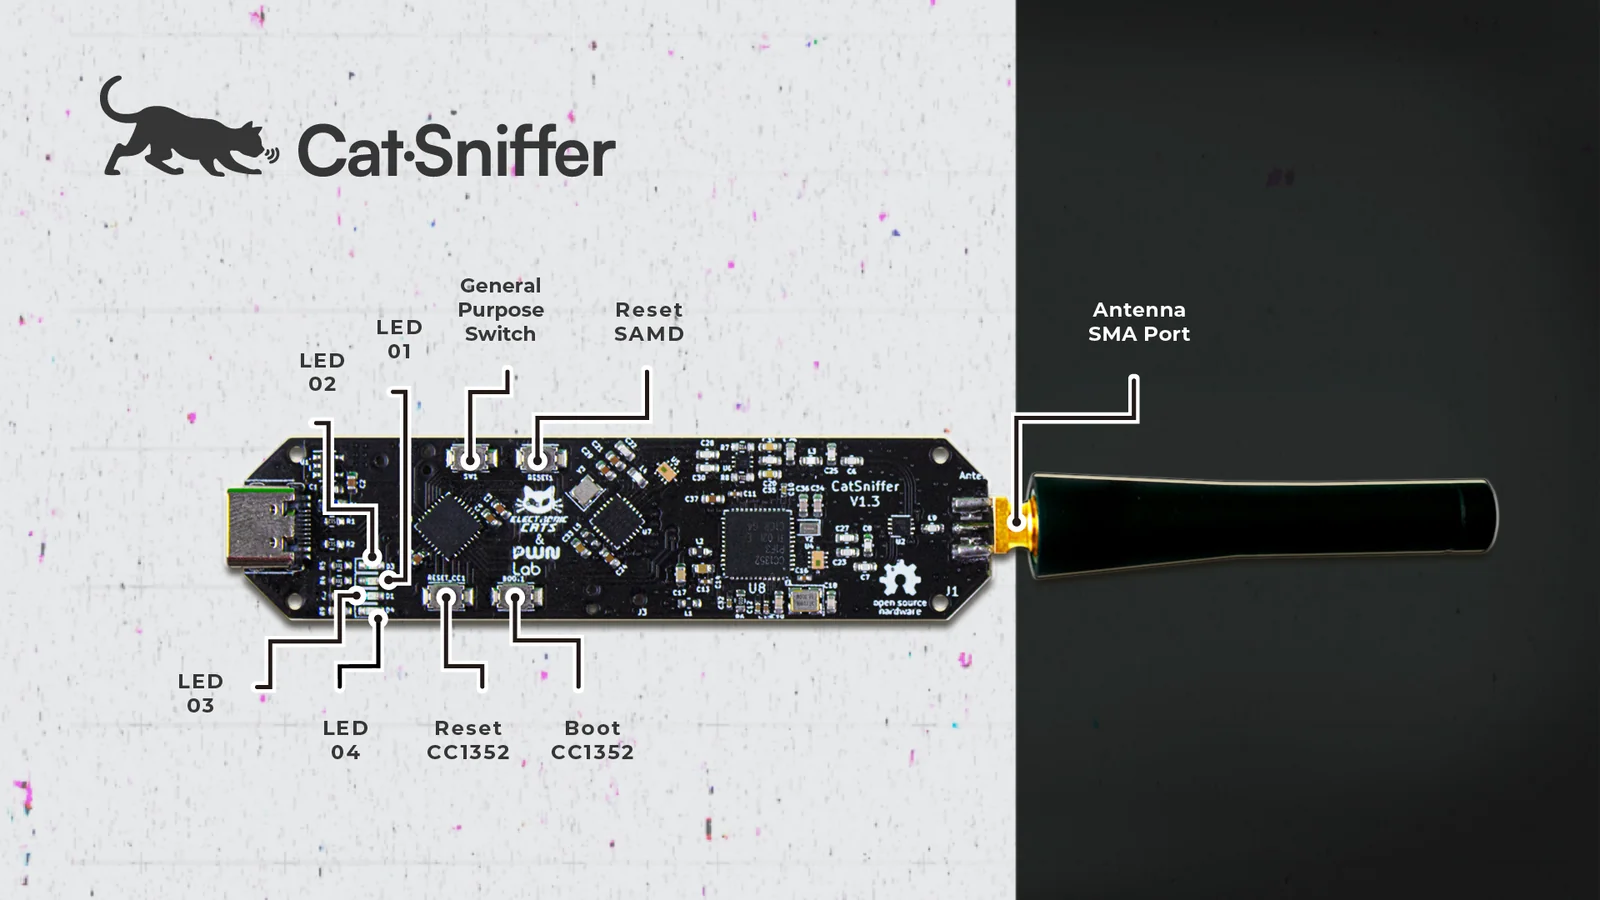
Firmware repository for CatSniffer, a multi-protocol IoT security research board supporting BLE, Zigbee, Sub-1 GHz, and more, with version-specific…

Firmware repository for CatSniffer, a multi-protocol IoT security research board supporting BLE, Zigbee, Sub-1 GHz, and more, with version-specific…

Kernel source tree for Renesas AOSP10 R33 with a patch for CVE-2021-33034, addressing a use-after-free vulnerability in the Bluetooth HCI event…

The open-source wireless research platform for ESP32.

Flipper Zero firmware source code

Active Bluetooth BR/EDR Sniffer/Injector as cheap as any ESP32 board can get. Works with Scapy ;-)

Firmware for getting a power trace of the behavior of the bluetooth module on the ESP32 when the ESP32 is sent the undocumented hci bluetooth…

Simulated BLE peripheral exposing an unauthenticated GATT firmware-update characteristic; demonstrates critical CVE-2026-22017 device-takeover…

BLEBoy is a training tool to teach users about BLE security by providing a single BLE peripheral that can be used to experiment with each BLE pairing…

BLESuite_CLI is a command line tool to enable an easier way to test Bluetooth Low Energy (BLE) devices

cabin partial analysis

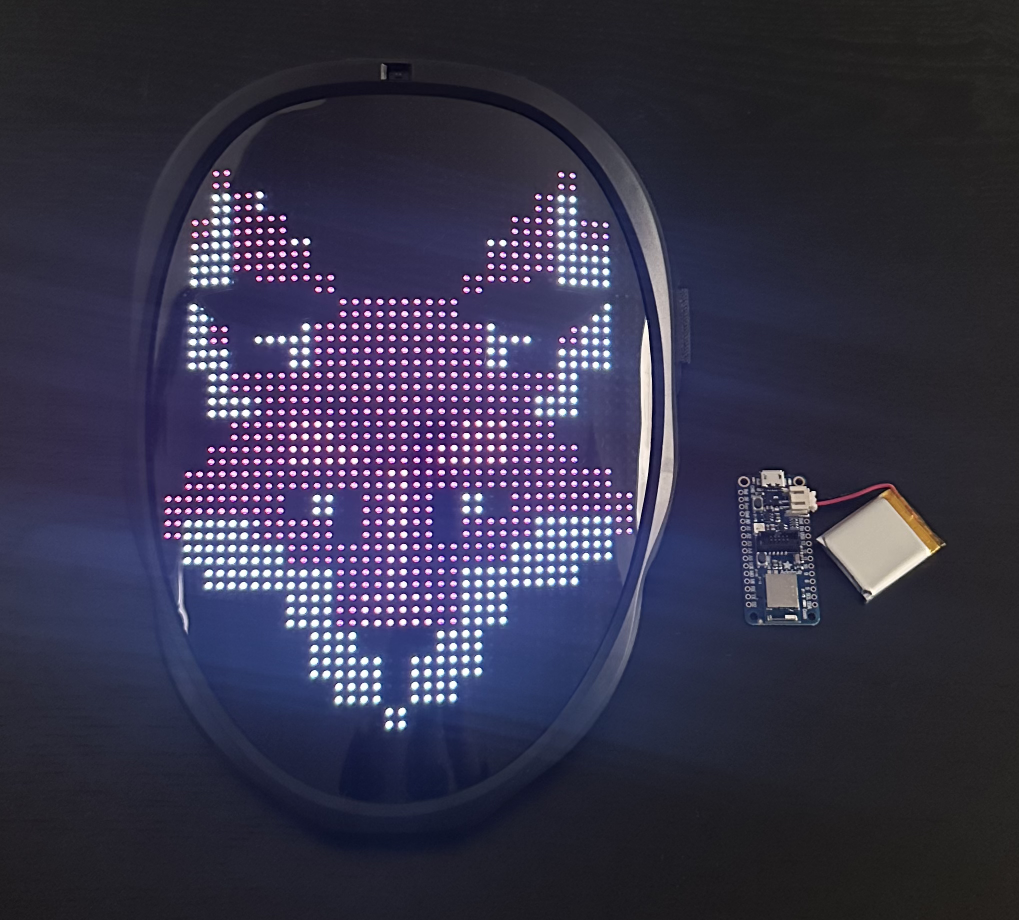
BLE-based tool that automatically discovers and exploits Shining LED Masks by uploading a custom image without user interaction, proving security…

Android Bluetooth stack (Fluoride) source code for AOSP 10 r33, specifically related to CVE-2021-0431 Bluetooth vulnerability research and…

A writeup and theoretical Proof-of-Concept for CVE-2019-19194

Proof-of-concept for CVE-2025-63895: Bluetooth Classic LMP buffer overflow exploitation in JXL 9-inch Android car infotainment systems, enabling…

CVE-2020-12351

Documentation of CVE-2025-67399: physical UART debug interface exploitation on AIRTH Smart Home AQI Monitor (BK7231N SoC) enabling unauthorized…

repo for CVE-2025-52413

Bluetooth 5 and 4.x LE sniffer for TI CC1352/CC26x2 hardware with support for extended advertising, all PHY modes, MAC/RSSI filtering, and PCAP…