cve-2026-43499-firetv-sheldonp-writeup

Security research write-up on exploiting CVE-2026-43499 on the Amazon Fire TV Stick 3rd Gen (sheldonp), from temporary root to bootloader unlock.

Security research write-up on exploiting CVE-2026-43499 on the Amazon Fire TV Stick 3rd Gen (sheldonp), from temporary root to bootloader unlock.

Patching and hooking the Linux kernel with only a stripped Linux kernel image.

Patches and hooks the Linux kernel using only a stripped kernel image, extracting symbols and injecting code for inline and syscall hooking on arm64.

Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…

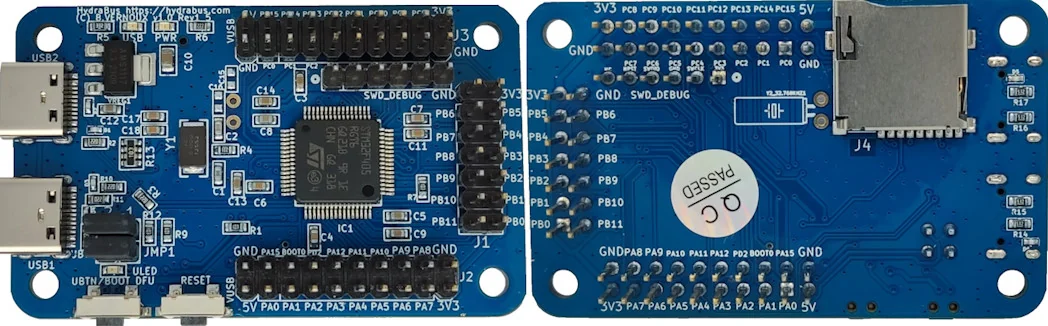
Open-source firmware for HydraBus, a multi-tool for embedded hardware debugging, hacking, and penetration testing, supporting protocols like SPI,…

Backports of three published f_hid fixes (incl. CVE-2026-31721, CVE-2026-31606) to an EOL Linux 4.14.190 Android vendor kernel, with on-device…

Android Bluetooth stack (Fluoride) with a specific patch for CVE-2021-0474, providing source code for building and testing the Bluetooth component on…

Android Fluoride Bluetooth stack source code with a focus on CVE-2021-0474, providing a foundation for vulnerability research and security analysis…

Android Bluetooth stack (Fluoride) with build instructions for AOSP and Linux, including dependency setup and GN/Ninja build steps.

High-risk vulnerability CVE-2026-43499, implementation on the 5.10 kernel and MediaTek MT6983V

UNISOC BootROM/FDL flasher for macOS: patched spd_dump with CVE-2022-38694 exec_addr2, protocol reference, partition rules, backup verification…

CVE-2024-56426 Exynos9830 Bootrom Exploit - SM-G985F

Step-by-step guide to building custom Kali NetHunter kernels for Android: source retrieval, toolchain selection, cross-compilation, and flashing.

A curated list of public TEE resources for learning how to reverse-engineer and achieve trusted code execution on ARM devices

Unlock the Meta Quest 1 bootloader and gain root access using GhostLock + CVE-2021-1931.


Patched wpa_supplicant and hostapd for Android 10 (r33) addressing CVE-2021-0326 vulnerability in Wi-Fi client and AP components, enhancing wireless…

Patched Bluetooth stack for Android 10 (AOSP r33) fixing buffer overflow vulnerability CVE-2021-0316.