
Archived
CVE-2020-27368
 swzhouu/cve-2020-27368
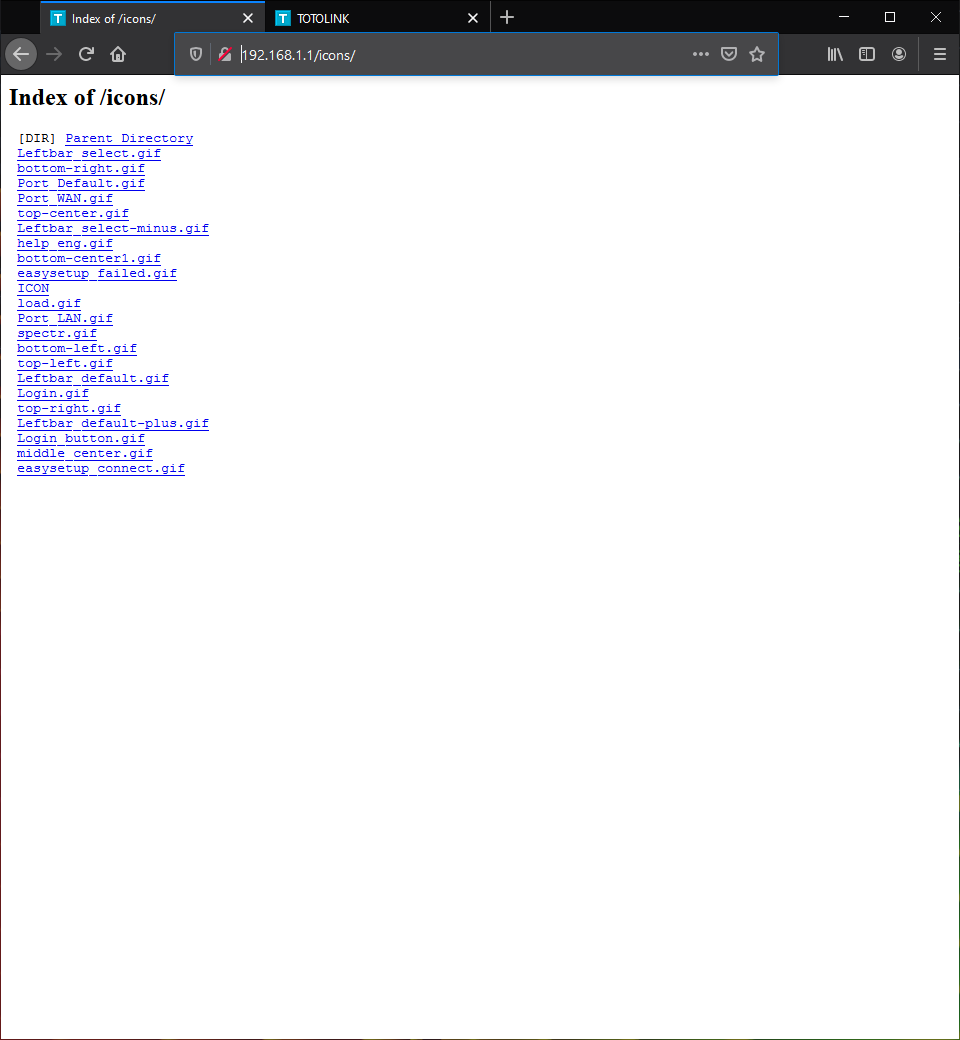
TOTOLINK-A702R-V1.0.0-B20161227.1023 Directory Indexing Vulnerability
embedded-systems-securityinformation-gatheringiot-security+3
swzhouu/cve-2020-27368TOTOLINK-A702R-V1.0.0-B20161227.1023 Directory Indexing Vulnerability
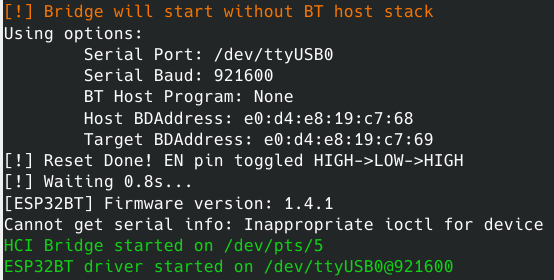 matheus-garbelini/esp32_bluetooth_classic_sniffer
Active Bluetooth BR/EDR Sniffer/Injector as cheap as any ESP32 board can get. Works with Scapy ;-)
 chrisneagu/ftc-skystone-dark-angels-romania-2020
NOTICE This repository contains the public FTC SDK for the SKYSTONE (2019-2020) competition season. If you are looking for the current season's FTC…
 george0papasotiriou/cve-2026-22013-hardware-wallet-usb-descriptor-buffer-overflow
Stack buffer overflow PoC for a hardware wallet USB descriptor parser (CVE-2026-22013), showing return-address overwrite and code execution via…
 zzz66686/cve-2017-14262
Exploit for CVE-2017-14262 targeting Samsung NVR devices: extracts admin MD5 password hash via unauthenticated CGI request and logs in with the hash…
 insecurityofthings/uc_mousejack
Mousejack for ATmega32u4
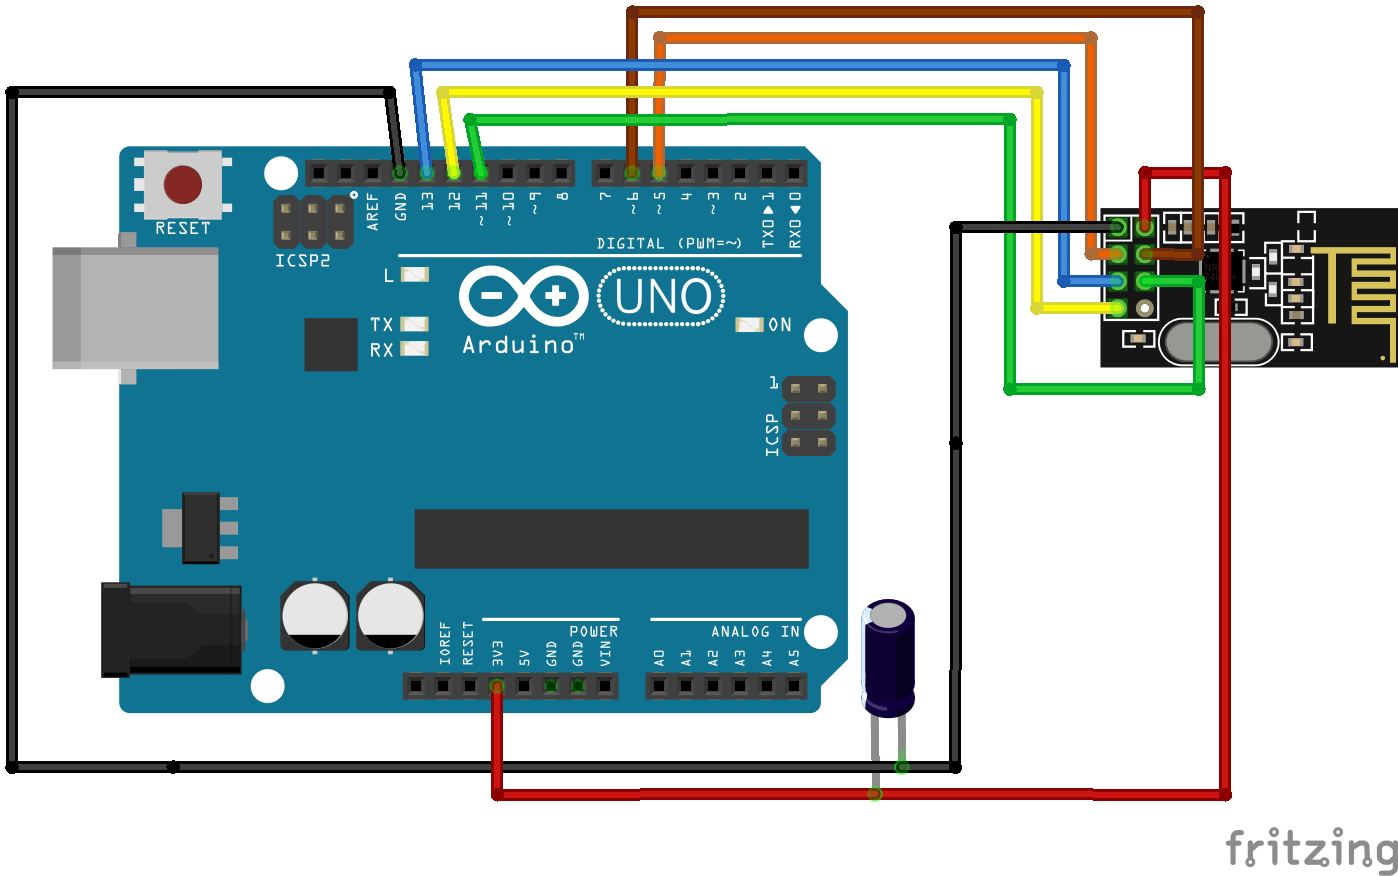 dnatividade/arduino_mousejack
Mousejack for Arduino UNO
 synacktiv/netgear_pwn2own2021
Exploit used against the Netgear R6700v3 during Pwn2Own Austin 2021
 nsbogam/cve-2022-26269
Suzuki connect app is used to get the car information like Fuel, Ignition status, Current location, Seat buckle status etc. In Ignis, Zeta variant…
 ethancunt/cve-2022-45600
Proof-of-concept exploit for command injection vulnerability in Aztech WMB250AC routers, enabling authenticated privilege escalation to root shell…
 resi-le/nxloader
An app that enables payload injection into a Switch console from an Android device by exploiting the CVE-2018-6242 vulnerability

 cryptoadvocate/dcsgonefwbsp
The firmware board support package home of the Circuit Crafters first electronic badge project.
 dylvie/cve-2020-35575-tp-link-tl-wr841nd-password-disclosure
Weaponized exploit script for CVE-2020-35575, a password-disclosure vulnerability in TP-Link router web interfaces, granting remote administrative…