

CANToolz
 eik00d/cantoolz
CANToolz - framework for black-box CAN network analysis
embedded-systems-securityfuzzinghardware-security+2
eik00d/cantoolzCANToolz - framework for black-box CAN network analysis
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 m4cs/digiduck-framework
Framework for Digiduck Development Boards running ATTiny85 processors and micronucleus bootloader!
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
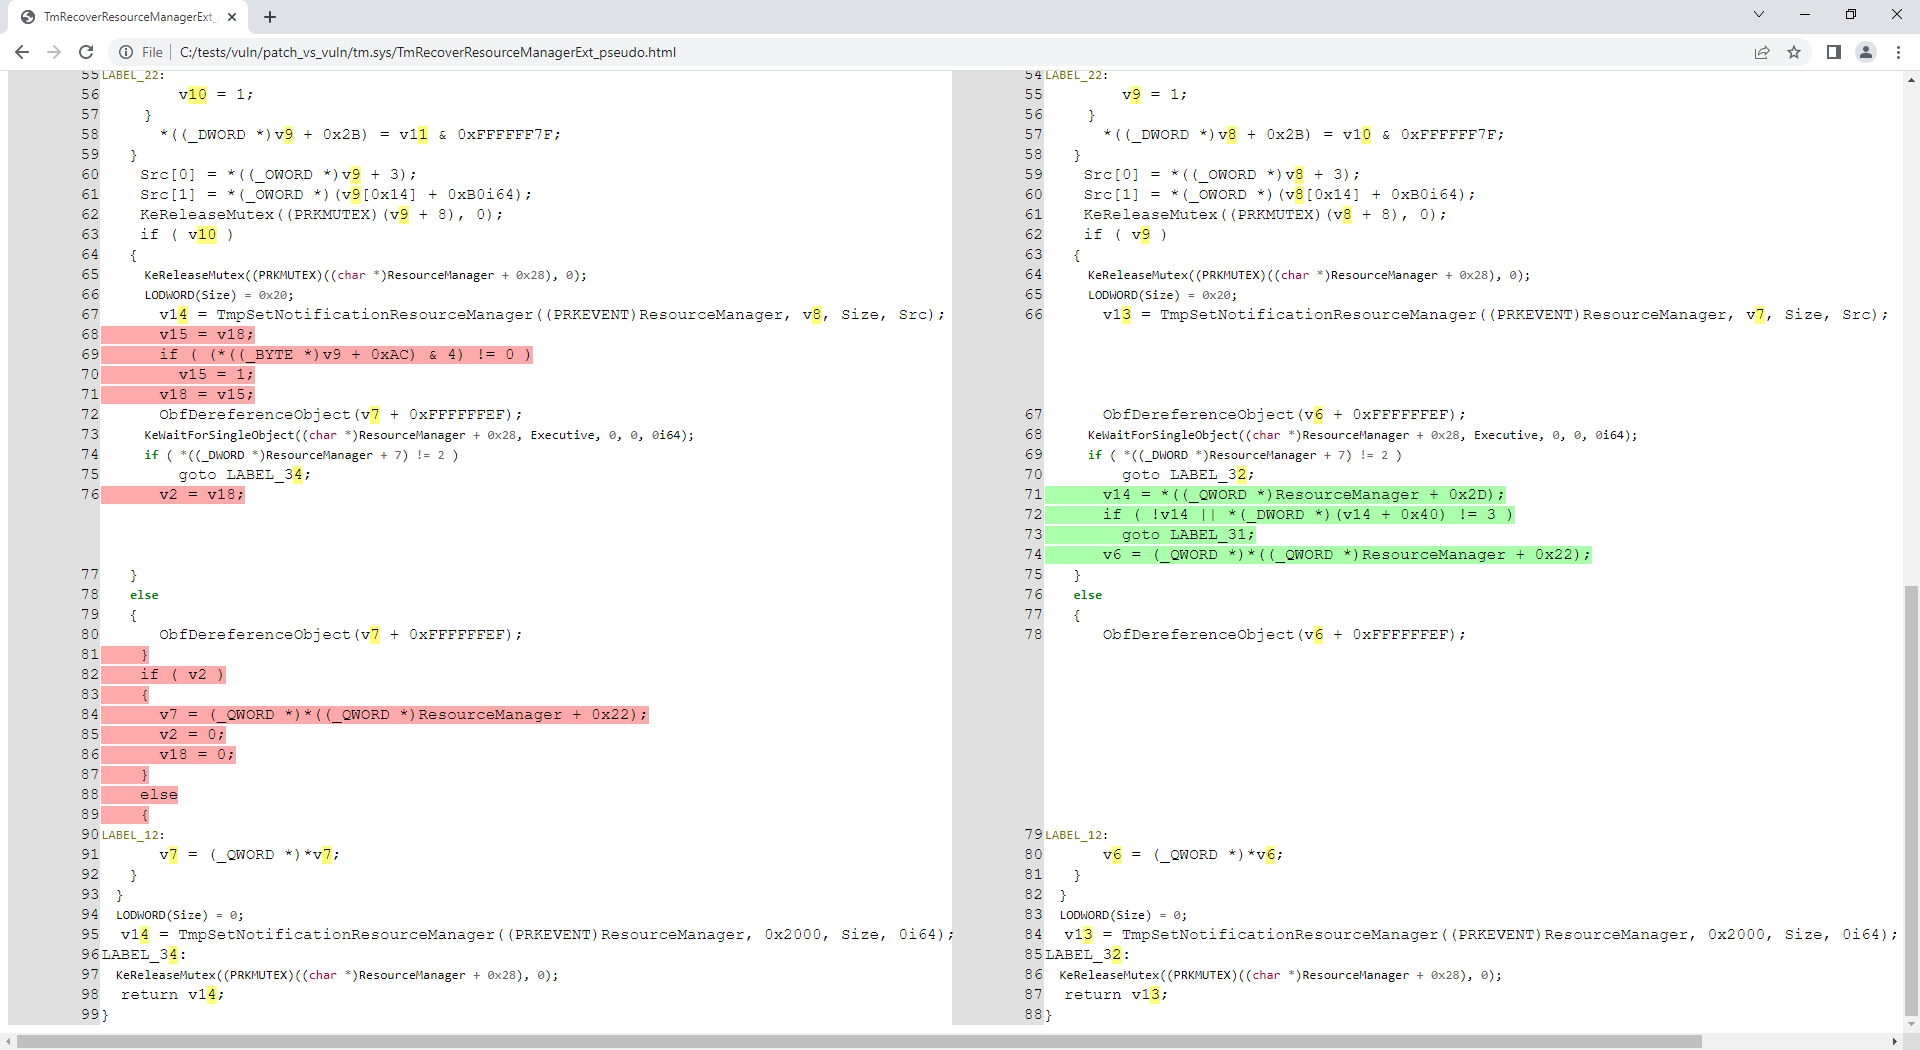 nccgroup/idahunt
idahunt is a framework to analyze binaries with IDA Pro and hunt for things in IDA Pro
 threat9/routersploit
Exploitation Framework for Embedded Devices
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
 thorat-shubham/jxl_infotainment_cve-2025-69515
Proof-of-concept exploit for CVE-2025-69515 demonstrating static GPS spoofing on JXL 9-inch Android infotainment units via SDR-based signal…
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 abrarkhan/g3_frameworks_av_cve-2024-0023
Proof-of-concept exploit for CVE-2024-0023 in Android's frameworks/av, implemented in C++ to demonstrate the media framework vulnerability.
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 angr/angr
A powerful and user-friendly binary analysis platform!
 openwrt/openwrt
Linux operating system for embedded devices with writable filesystem, package management, and build framework. Enables custom firmware creation for…
 theos/sdks
Patched sdks that include private framework tbds
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 cantoolz/cantoolz
CANToolz - Black-box CAN network analysis framework
 sacriphanius/zhilly
🛡️ AI-powered portable cybersecurity & pentesting assistant built on ESP32-S3 (LilyGO T-Embed CC1101 & T-Watch S3). Features voice-controlled RF…