
Evil-M5Project
 7h30th3r0n3/evil-m5project
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…
bluetooth-securitycommand-and-controleducation+9
2.8k
7h30th3r0n3/evil-m5projectMulti-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…
 lord-feistel/power_analysis
Proof-of-concept demonstrating a power analysis side-channel attack against a vulnerable RSA implementation on Arduino (Atmega328P), with detailed…
 nfc-tools/mfcuk
Recovers cryptographic keys from MiFare Classic RFID cards using DarkSide and nested-auth attacks for security testing of NFC/RFID systems.
 newaetech/chipwhisperer
Open-source hardware security toolchain for power trace capture, side-channel analysis, and glitching/fault-injection attacks on embedded devices and…
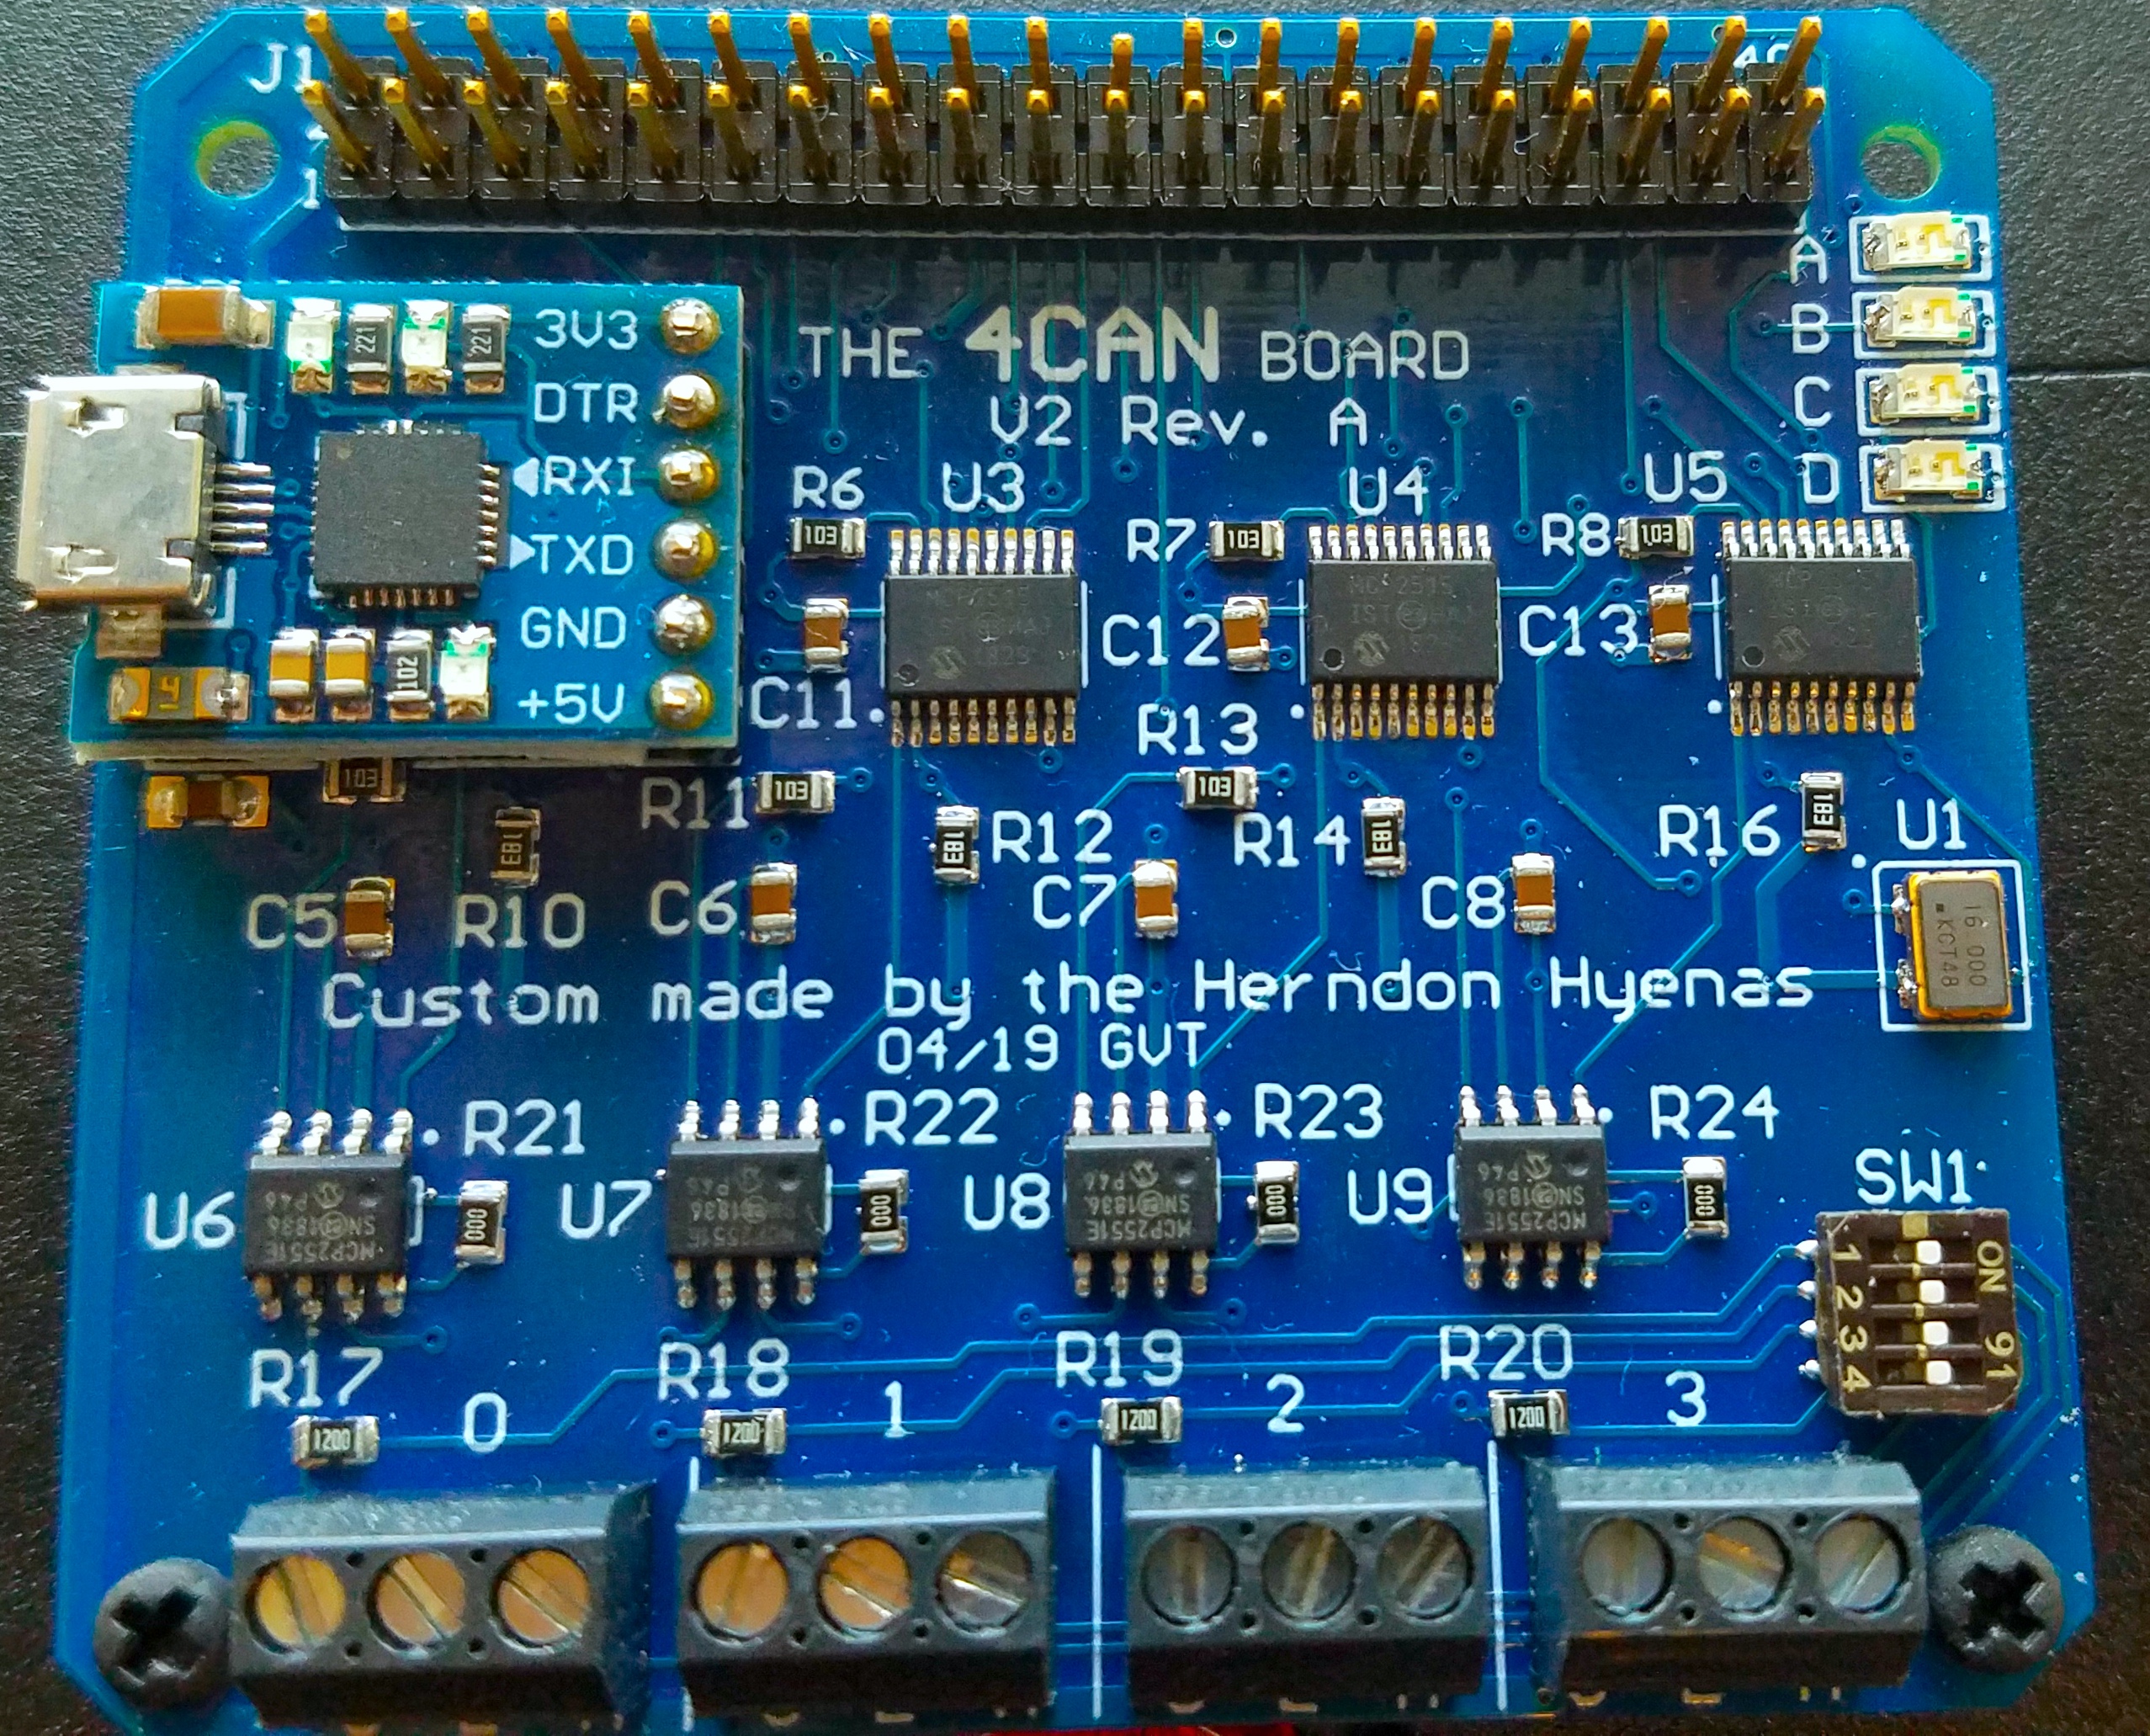 alexdetrano/4can
Open-source Raspberry Pi HAT providing 4 CAN interfaces for automotive bus testing, CAN-in-the-middle attacks, and simultaneous multi-bus traffic…
 souravbaghz/carpunk
CAN bus injection toolkit for automotive security testing. Performs interface control, sniffing, and CAN injection attacks on vehicle networks,…
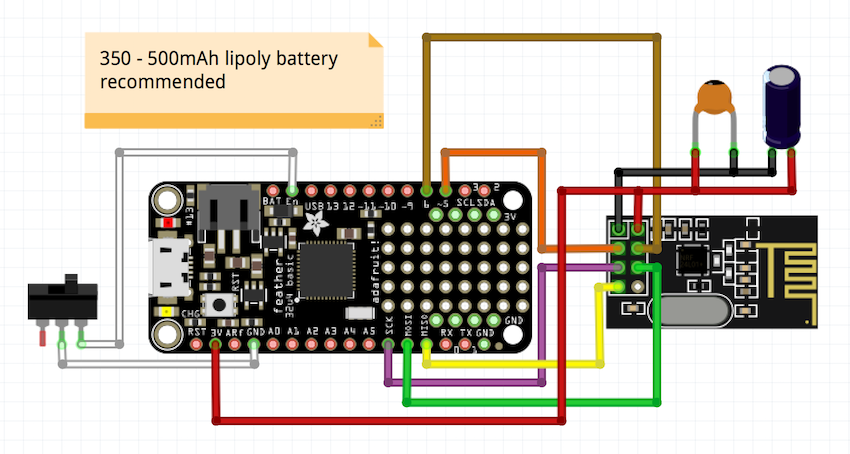 insecurityofthings/uc_mousejack
Mousejack for ATmega32u4
 geeoon/fault-injection-finder
Automatically find and execute fault injection attacks
 demining/ramnesia-attack
Scientific investigation of hardware vulnerabilities (CVE-2025-6202, CVE-2023-39910) enabling ECDSA key recovery from Bitcoin infrastructure via…
 jasondoyle/google-nest-cam-bug-disclosures
PoC vulnerability disclosures for consumer IoT cameras, detailing BLE buffer overflow and WiFi disassociation attacks that can take devices offline.
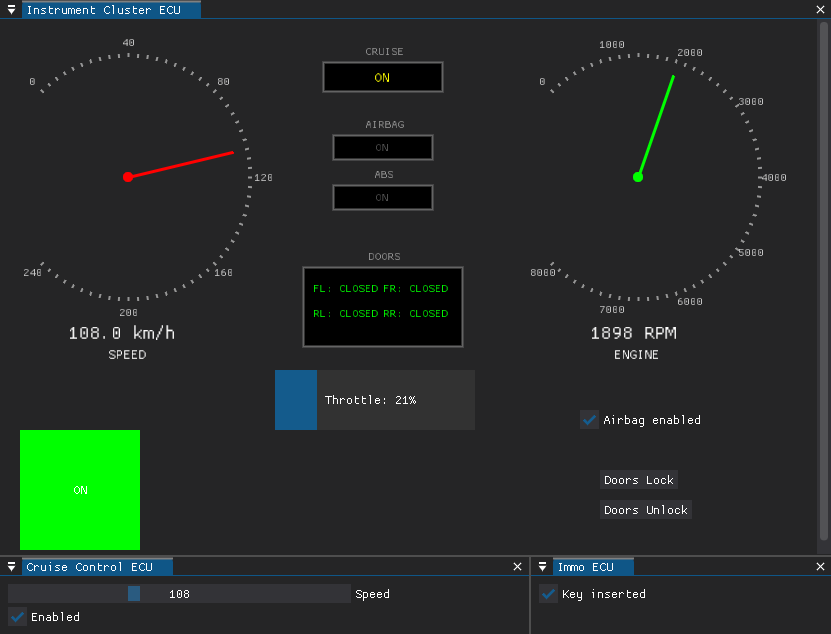 infobyte/doggie_workshop
CAN Bus vehicle simulator for practicing offensive automotive security attacks. Emulates multiple ECUs to enable sniffing, injection, and…
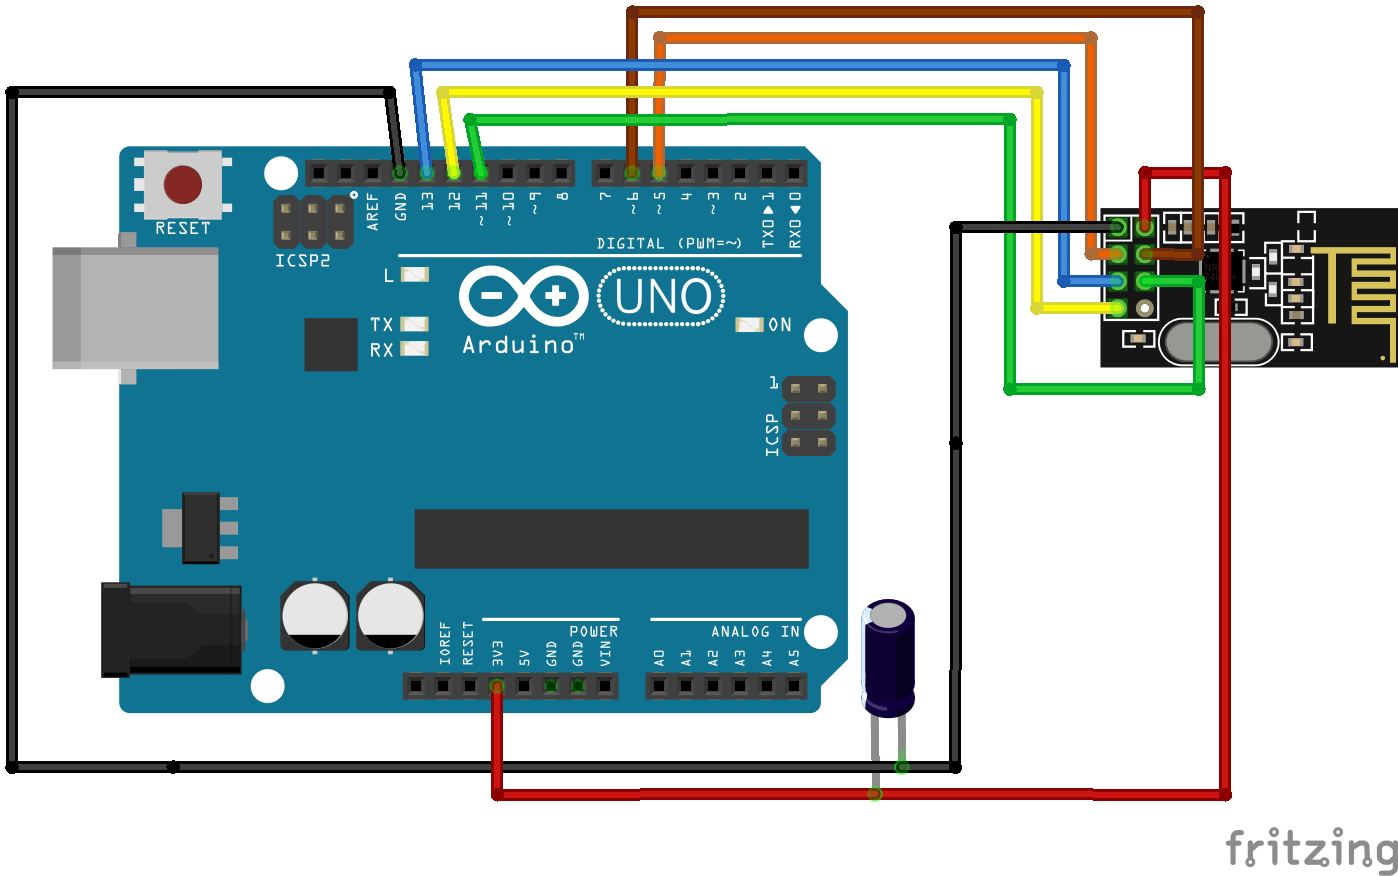 dnatividade/arduino_mousejack
Mousejack for Arduino UNO
 ahmaaaaadbntaaaaa-byte/tid-the-instant-destroyer
Hardware-level security protocol for mitigating cache-based side-channel attacks.
 wolffcorentin/cve-2019-1663-binary-analysis
Binary analysis and exploitation of CVE-2019-1663, a buffer overflow in Cisco router web management, including root cause, exploit steps, and ROP…
 infobyte/doggie
Welcome to the Doggie and EvilDoggie repository by Faraday Security! Doggie is a modular DIY CAN Bus to serial adapter (USB, BLE, UART) using the…
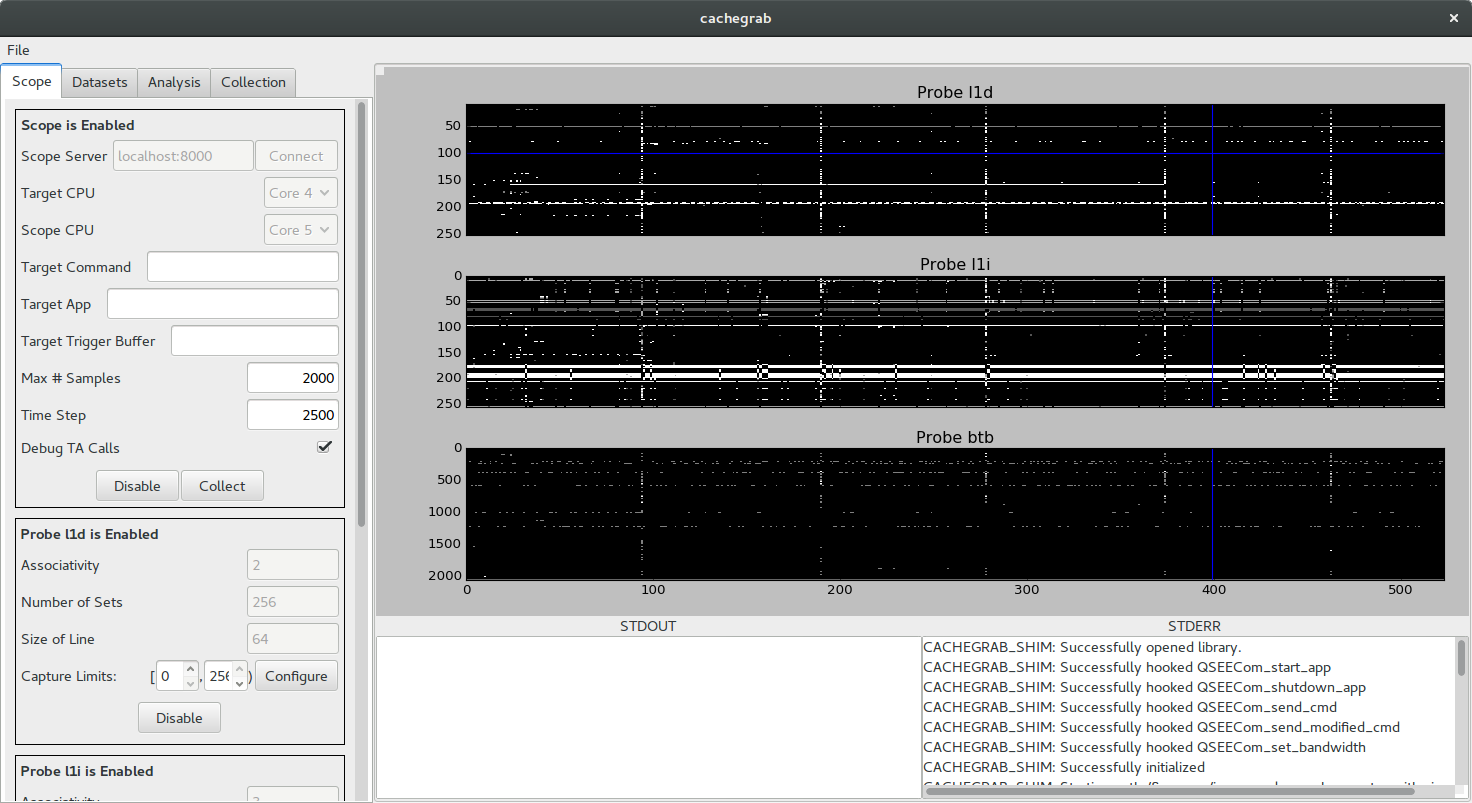 nccgroup/cachegrab
a tool designed to help perform and visualize trace-driven cache attacks against software in the secure world of TrustZone-enabled ARMv8 cores