

emba
 e-m-b-a/emba
EMBA - The firmware security analyzer
binary-analysisdynamic-analysis-sandboxingembedded-systems-security+8
e-m-b-a/embaEMBA - The firmware security analyzer
 o7-machinehum/phantomdrive
Seemingly normal USB drive with a hidden security feature
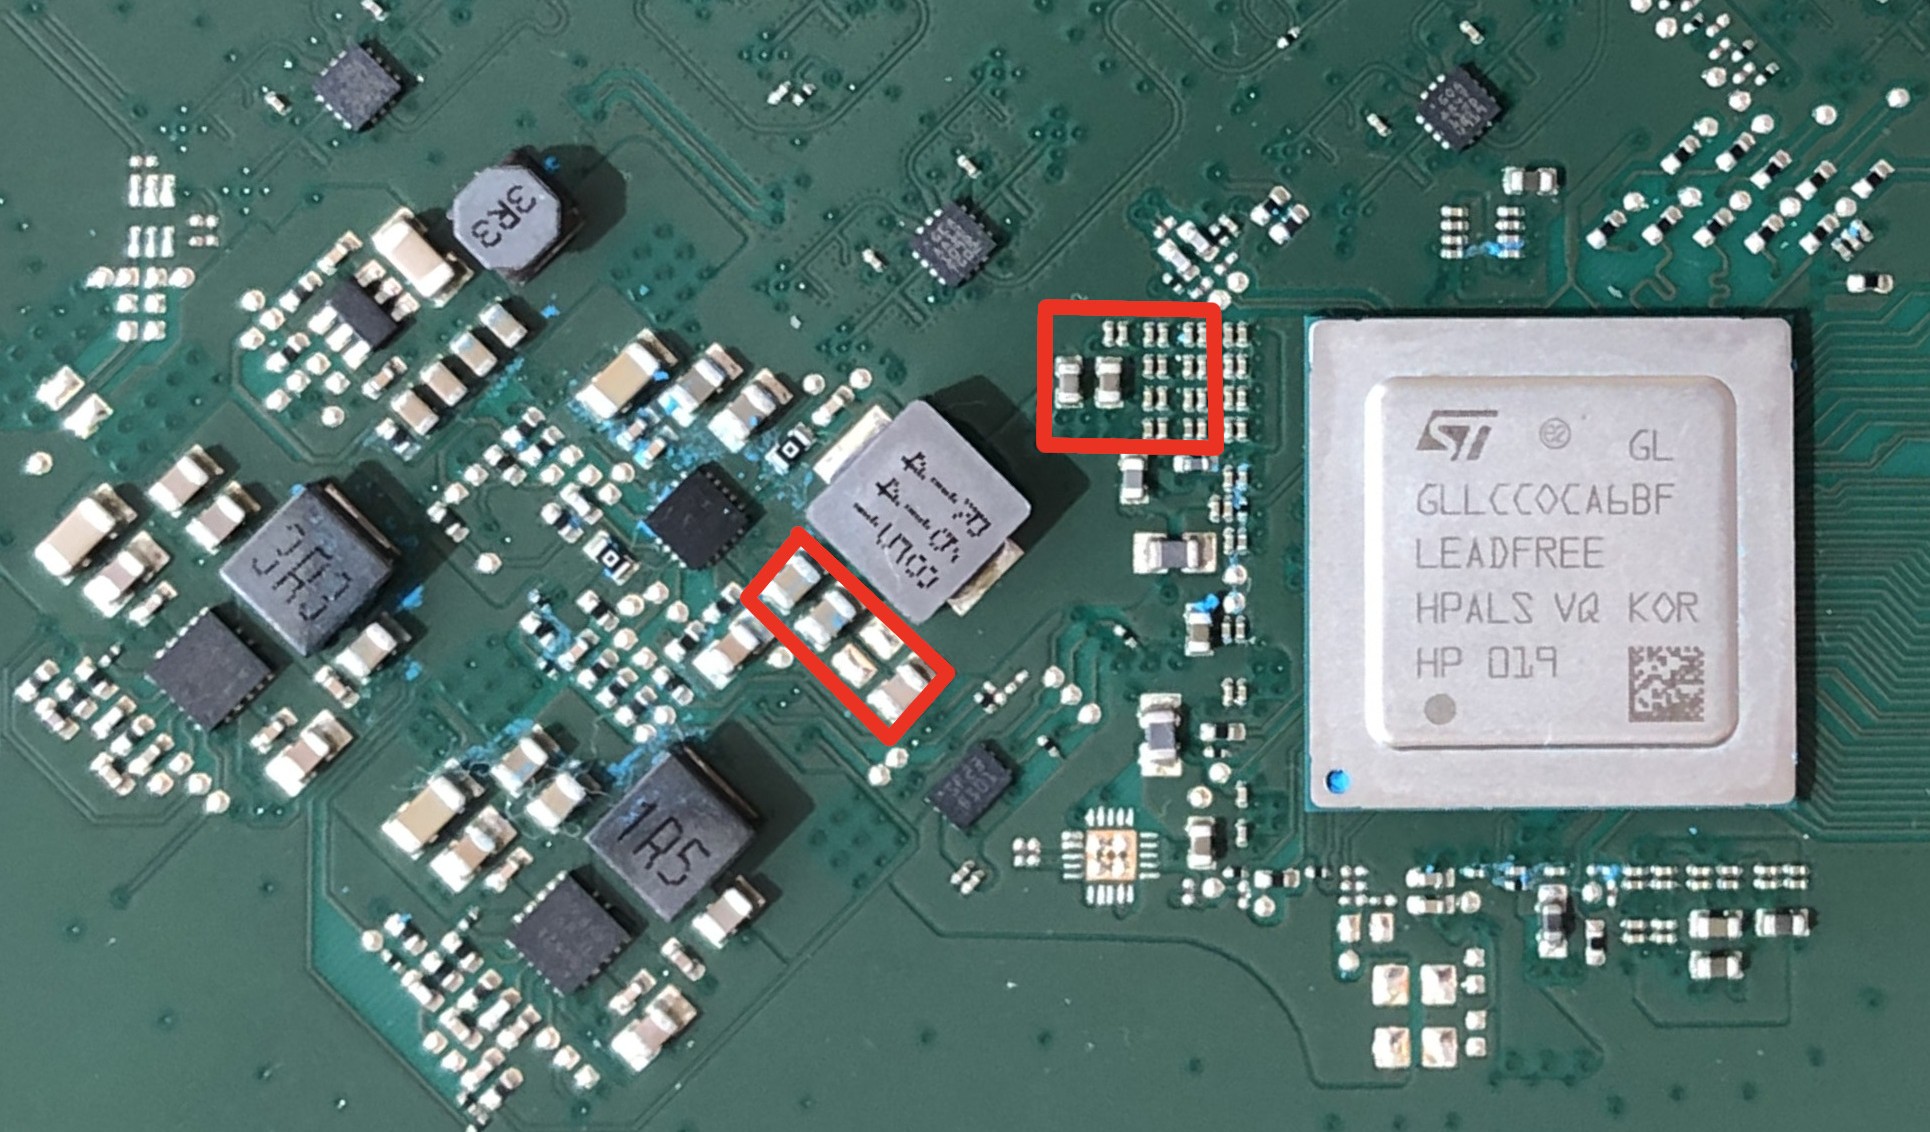 kuleuven-cosic/starlink-fi
Voltage fault-injection modchip for black-box security evaluation of Starlink terminals, bypassing bootloader signature verification to execute…
 ffri/shadebios
PoC code of Shade BIOS (stripped) presented at Black Hat USA 2025
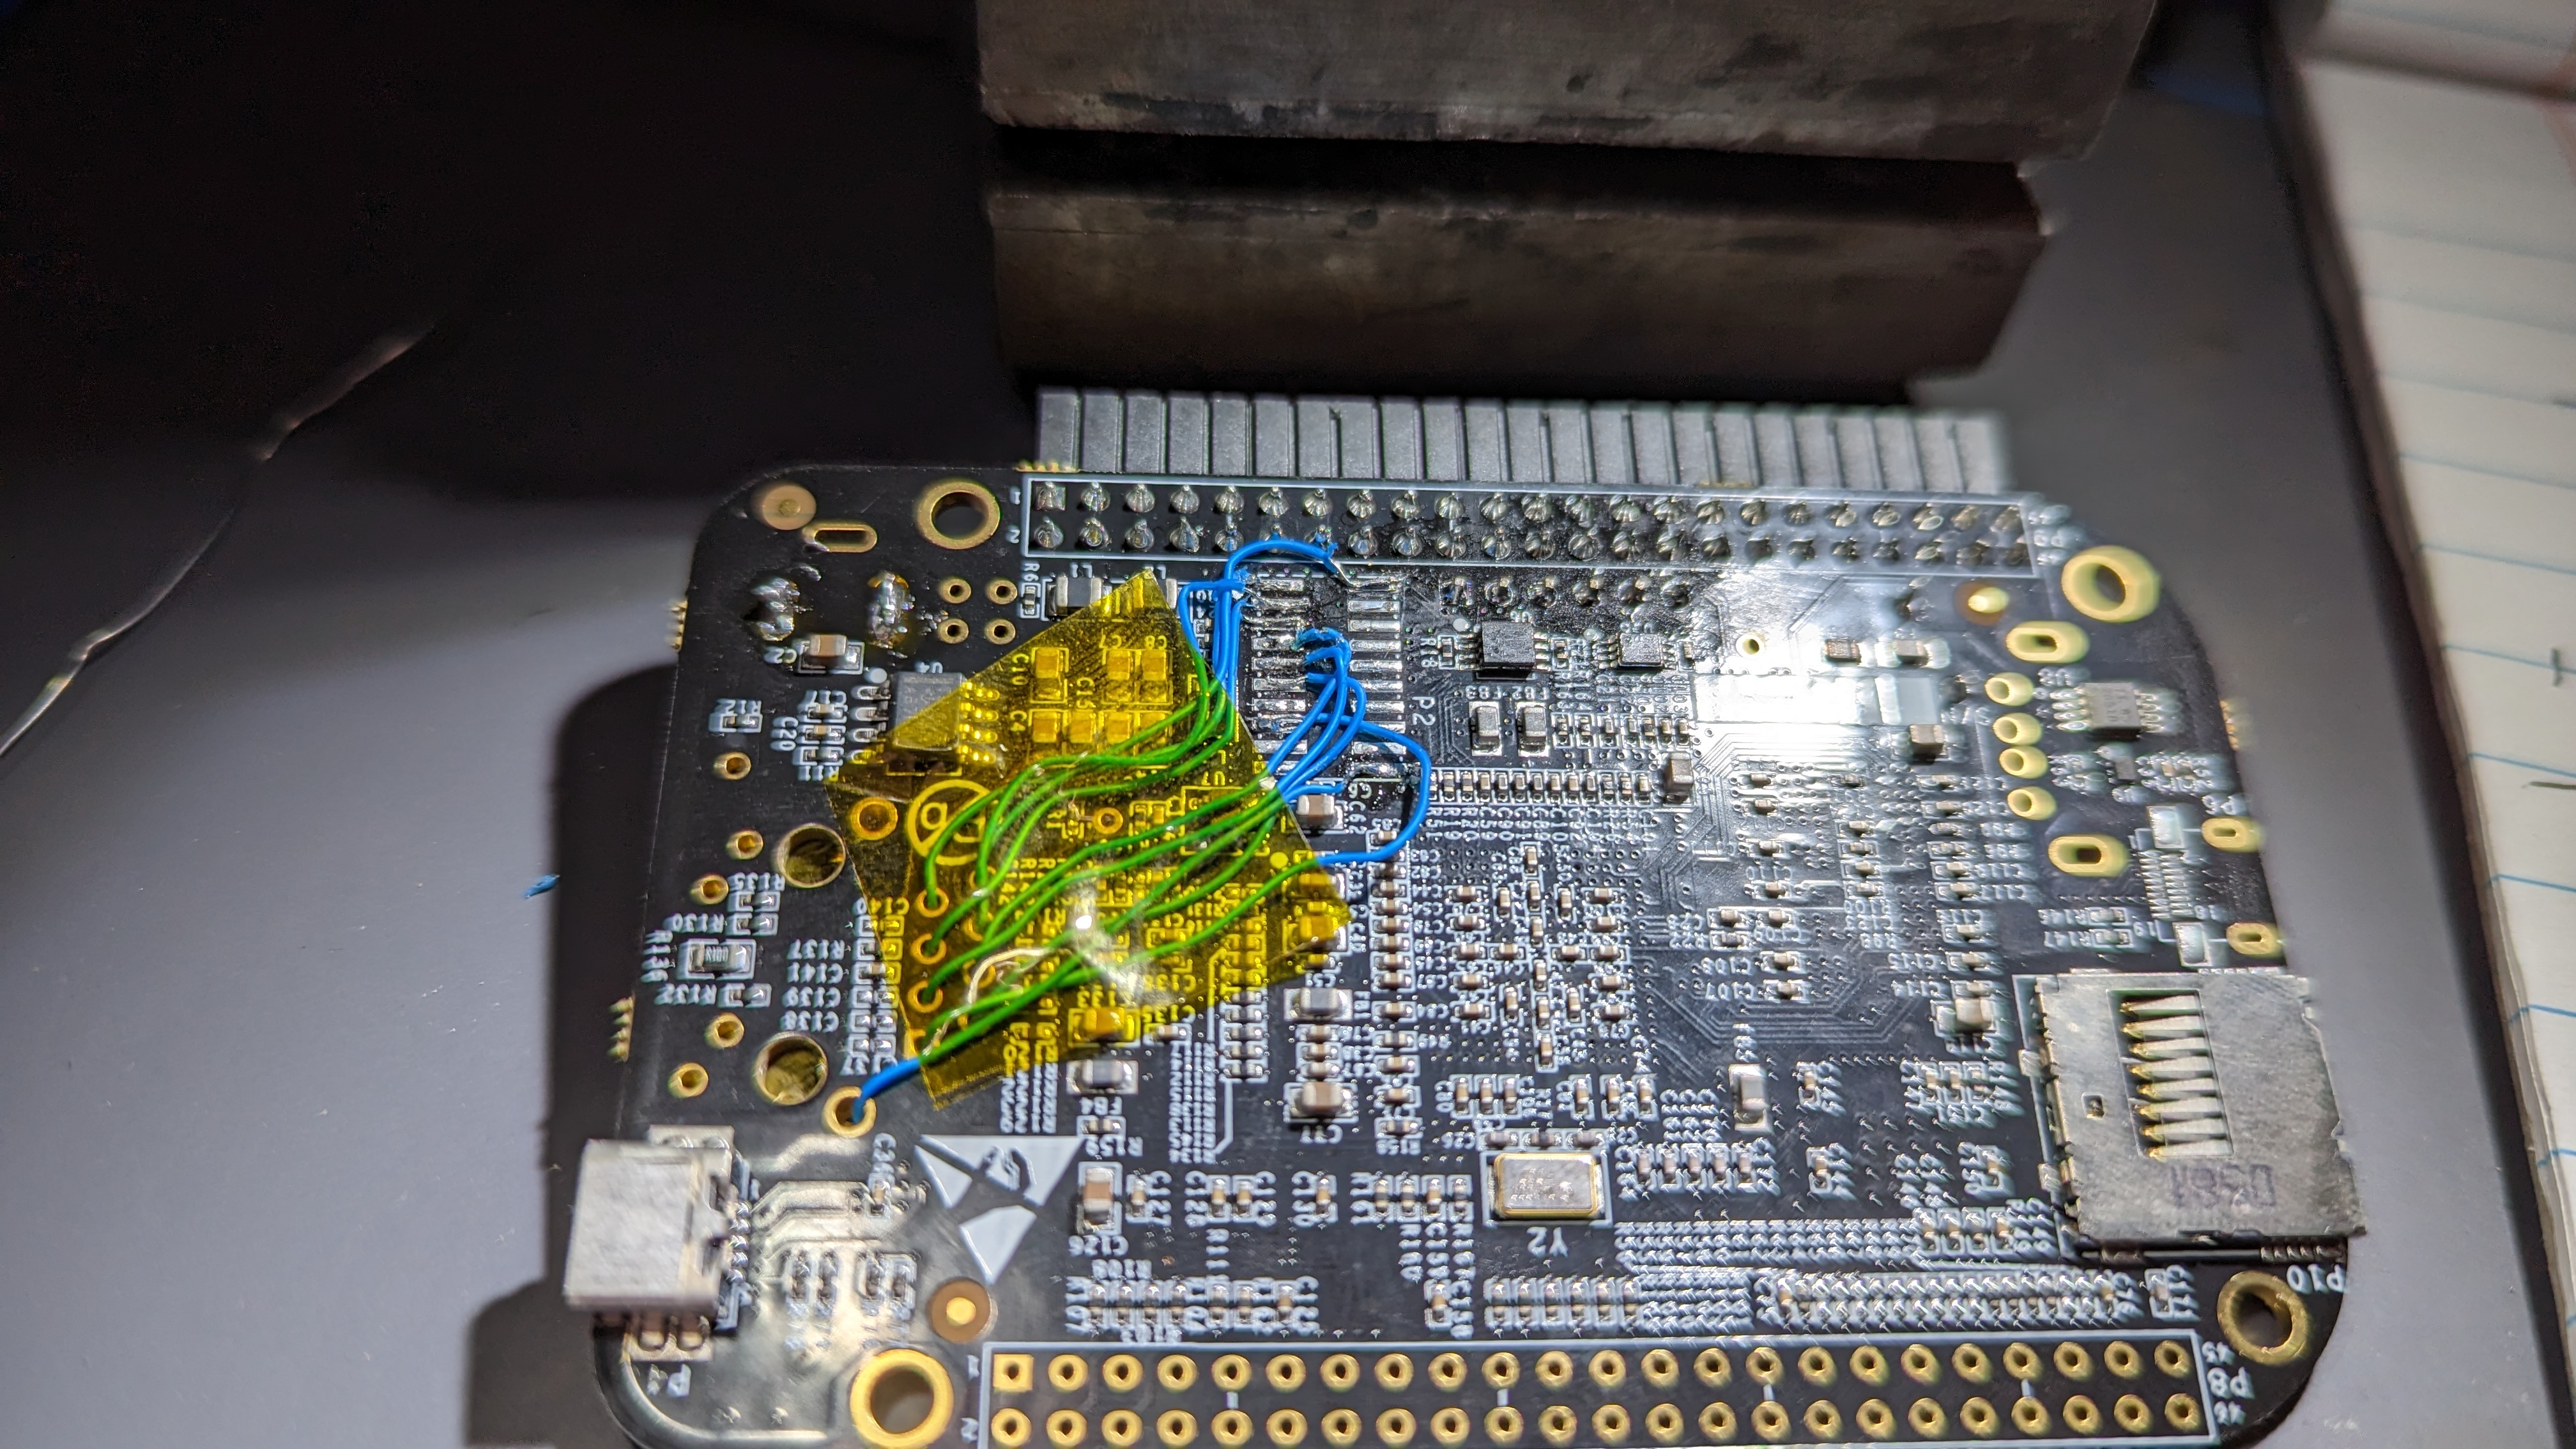 sjgallagher2/am335xbootrom
Reverse engineering the TI AM3358 boot ROM
 kkamagui/napper-for-tpm
TPM vulnerability checking tool for CVE-2018-6622. This tool will be published at Black Hat Asia 2019 and Black Hat Europe 2019