
cve-2023-23397
 bronzebee/cve-2023-23397
Python script for sending e-mails with CVE-2023-23397 payload using SMTP
email-securityexploitationpassword-attacks+3
bronzebee/cve-2023-23397Python script for sending e-mails with CVE-2023-23397 payload using SMTP
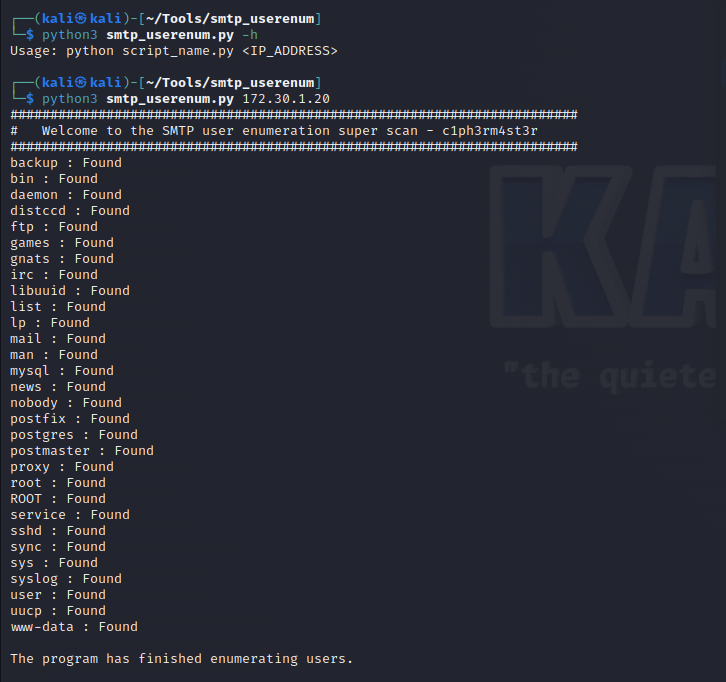 h3x0v3rl0rd/smtp_userenum
Python script for enumerating SMTP users by leveraging VRFY and EXPN commands to identify valid email accounts on a target mail server.
 jishino567/cve-2026-73570
Python PoC for CVE-2026-73570, an SMTP command injection in Zimbra. Sends malformed RCPT TO payloads to trigger shell command execution via…
 hackerxphantom/spoof_anymail
Most Powerful Send Fake Mail Using Any Mail I'd undetectable
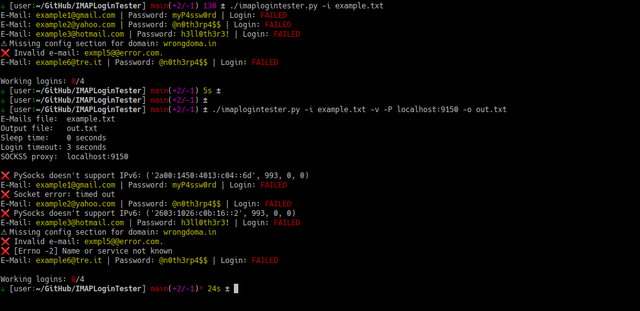 rm1984/imaplogintester
A simple Python script that reads a text file with lots of e-mails and passwords, and tries to check if those credentials are valid by trying to…
 grn-bogo/cve-2023-23397
Python script to create a message with the vulenrability properties set
 liamromanis101/dead.letter-cve-2026-45185
Shell-based vulnerability scanner for CVE-2026-45185 (Dead.Letter) in Exim MTA. Detects use-after-free in GnuTLS builds, checks version, TLS library,…
 george0papasotiriou/cve-2026-11113-smtp-header-injection-in-contact-form
Proof-of-concept exploit for CVE-2026-11113, demonstrating SMTP header injection in a Flask contact form via unsanitized email input; includes…
 emalderson/thephish
ThePhish: an automated phishing email analysis tool