

 themehackers/cve-2024-21413
CVE-2024-21413 | Microsoft Outlook Remote Code Execution Vulnerability PoC
 r00tb1t/cve-2024-21413-poc
Microsoft Outlook Information Disclosure Vulnerability (leak password hash) - CVE-2024-21413 POC
 natasaka/cve-2025-30349
Horde IMP (through 6.2.27) vulnerability – obfuscation via HTML encoding – XSS payload
 v4d1/spoofthatmail
Bash script to check if a domain or list of domains can be spoofed based in DMARC records
 black-scorp10/email-vulnerability-checker
Automated SPF and DMARC configuration checker that identifies email spoofing vulnerabilities across single or bulk domains using DNS lookups.
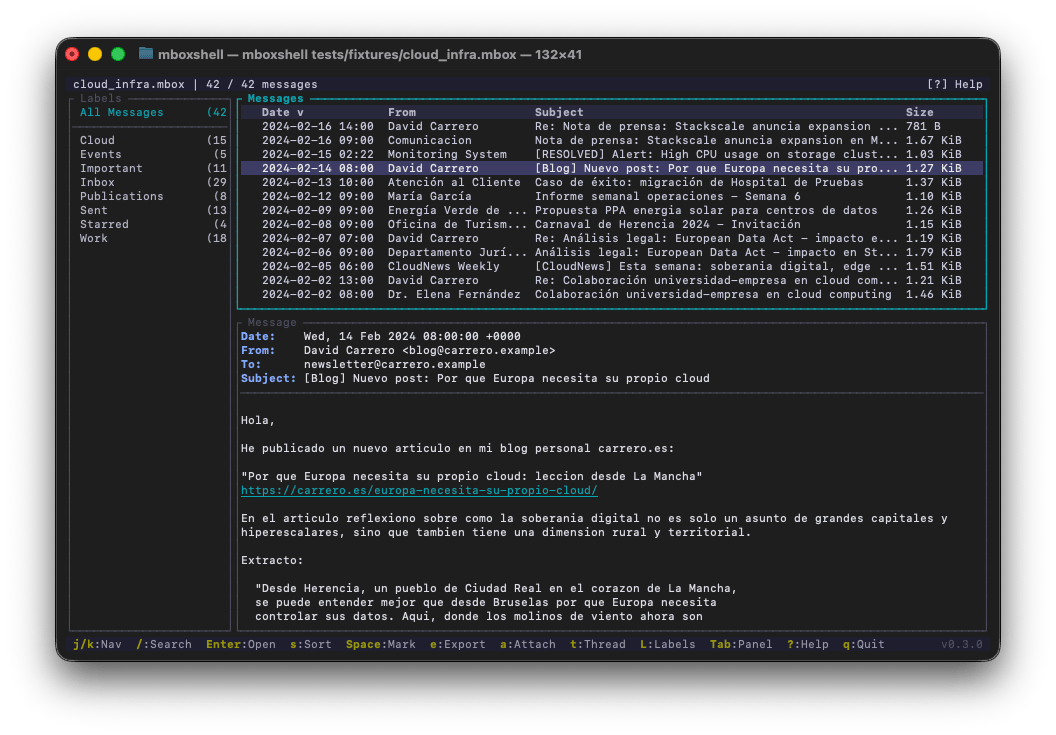 dcarrero/mboxshell
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
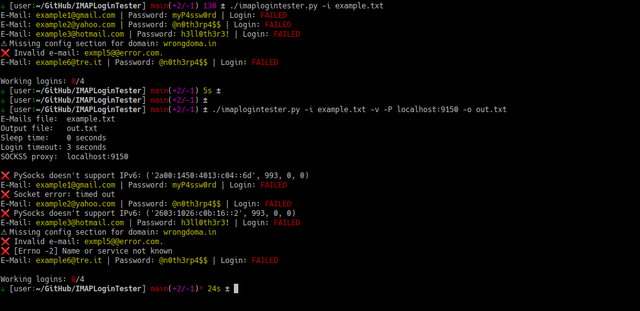 rm1984/imaplogintester
A simple Python script that reads a text file with lots of e-mails and passwords, and tries to check if those credentials are valid by trying to…
 cscli/cve-2017-5223
Proof-of-concept exploit for CVE-2017-5223 demonstrating arbitrary file read via PHPMailer's attachment and email content injection.
 crimsonforge-io/king-phisher
Simulate realistic phishing campaigns with credential harvesting, email tracking, and landing page cloning for security awareness training and…