

flanker
 mailgun/flanker
Python email address and Mime parsing library
email-securitygeneral-purpose-utilitiesscripting-automation+1
mailgun/flankerPython email address and Mime parsing library
 derrickschoen/laravel-framework
Fork of laravel/framework 10.50.2 with CVE-2026-48019 (CRLF injection in default email rule) backported into ValidatesAttributes::validateEmail.…
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
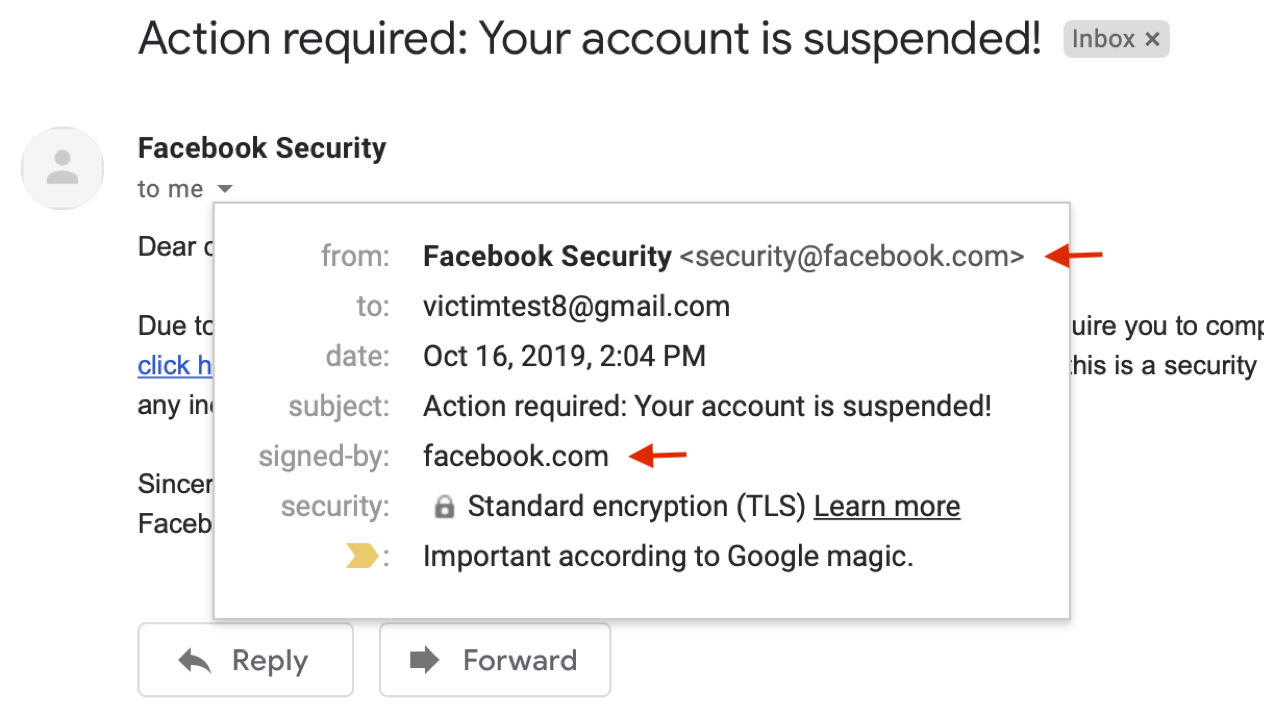 chenjj/espoofer
An email spoofing testing tool that aims to bypass SPF/DKIM/DMARC and forge DKIM signatures.🍻
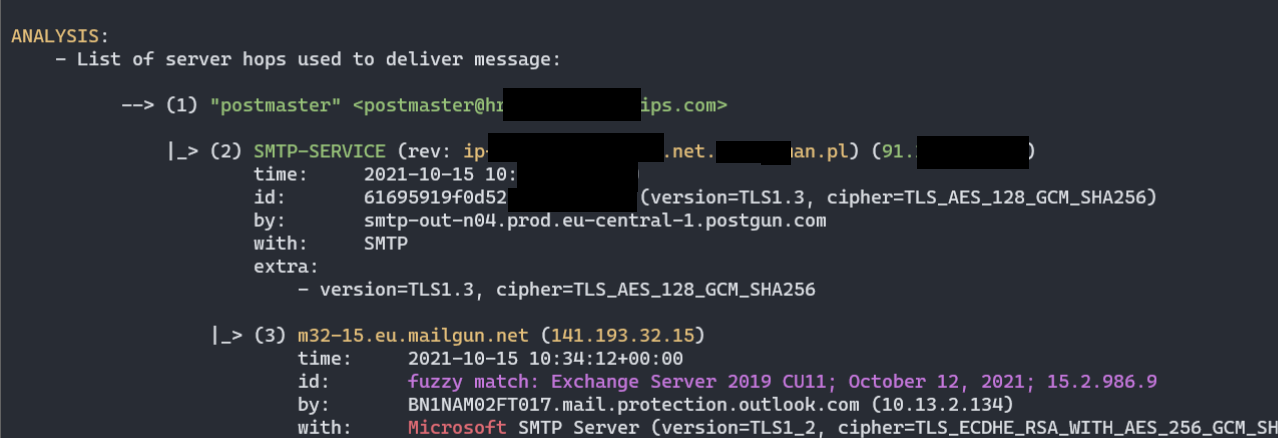 mgeeky/decode-spam-headers
A script that helps you understand why your E-Mail ended up in Spam
 apache/spamassassin
Open-source email filtering framework that detects spam and phishing using content analysis, header checks, Bayesian scoring, and DNS blocklists.
 api0cradle/cve-2023-23397-poc-powershell
PowerShell script to exploit CVE-2023-23397 by sending or saving malicious Outlook calendar invitations that trigger NTLM credential leakage via the…
 eksperience/knockoutlook
C# tool for red team operations that extracts contacts, mailbox metadata, and searches emails via Outlook COM object, with built-in Programmatic…
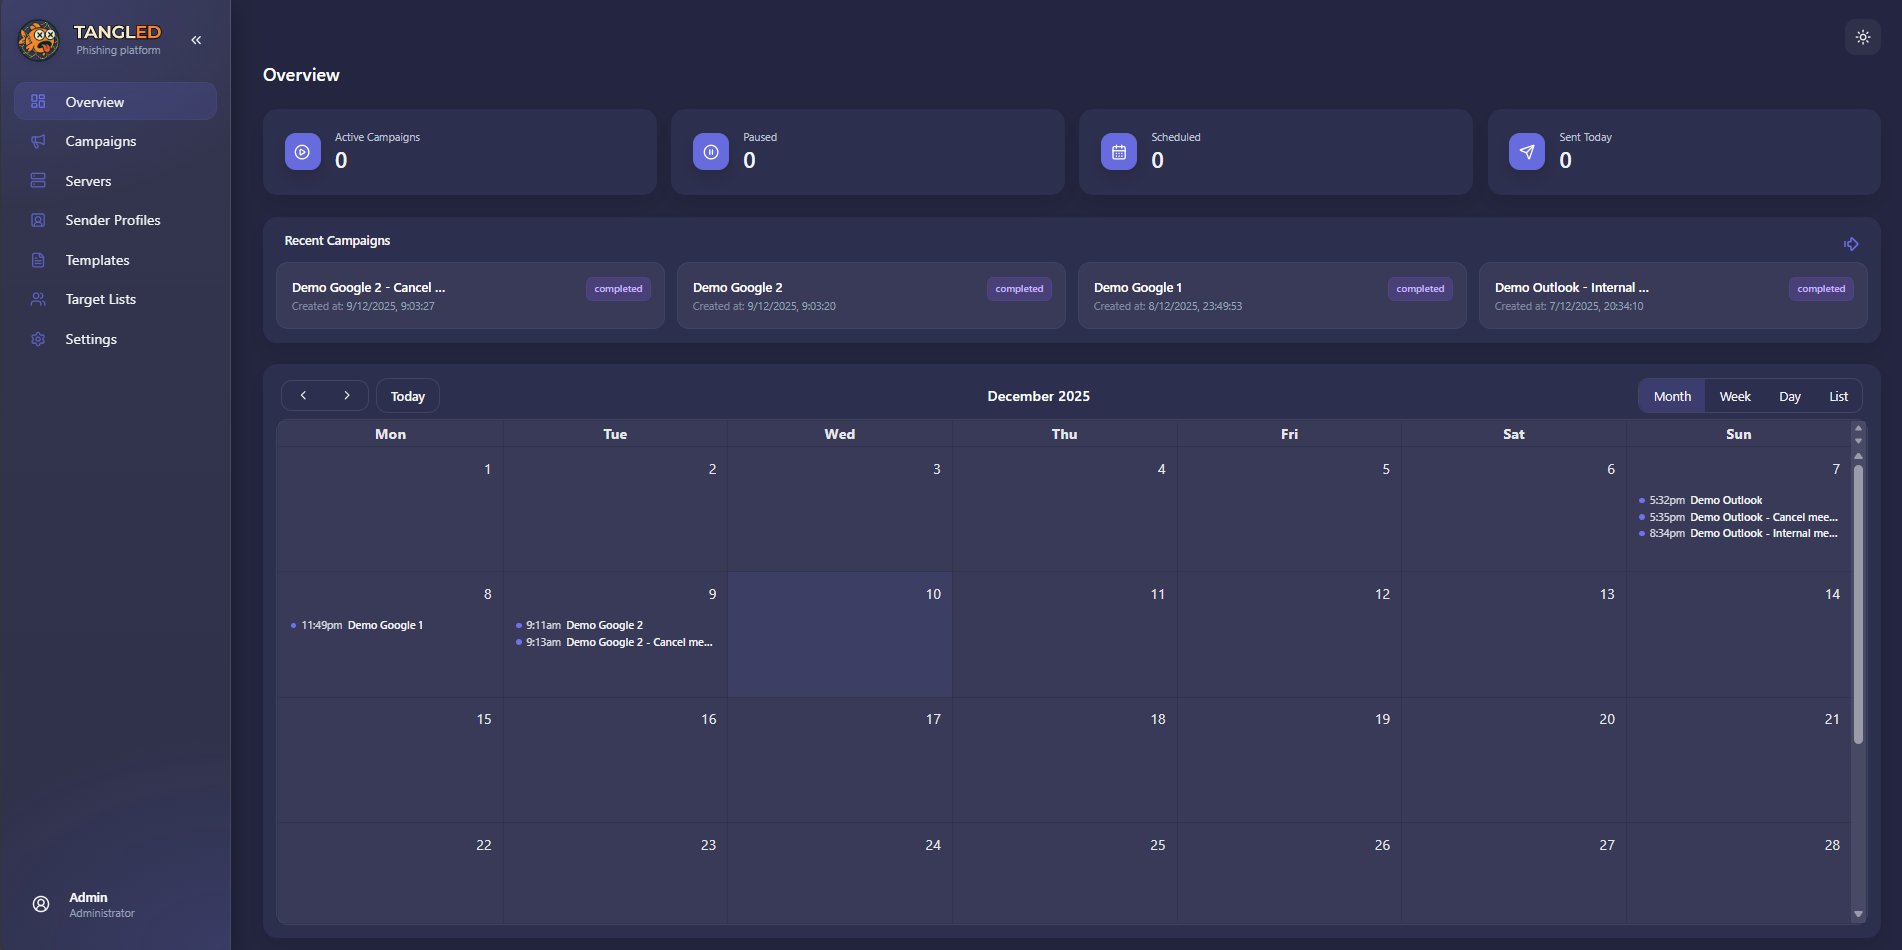 ineesdv/tangled
Open-source offensive security platform for conducting phishing campaigns that weaponizes iCalendar automatic event processing.
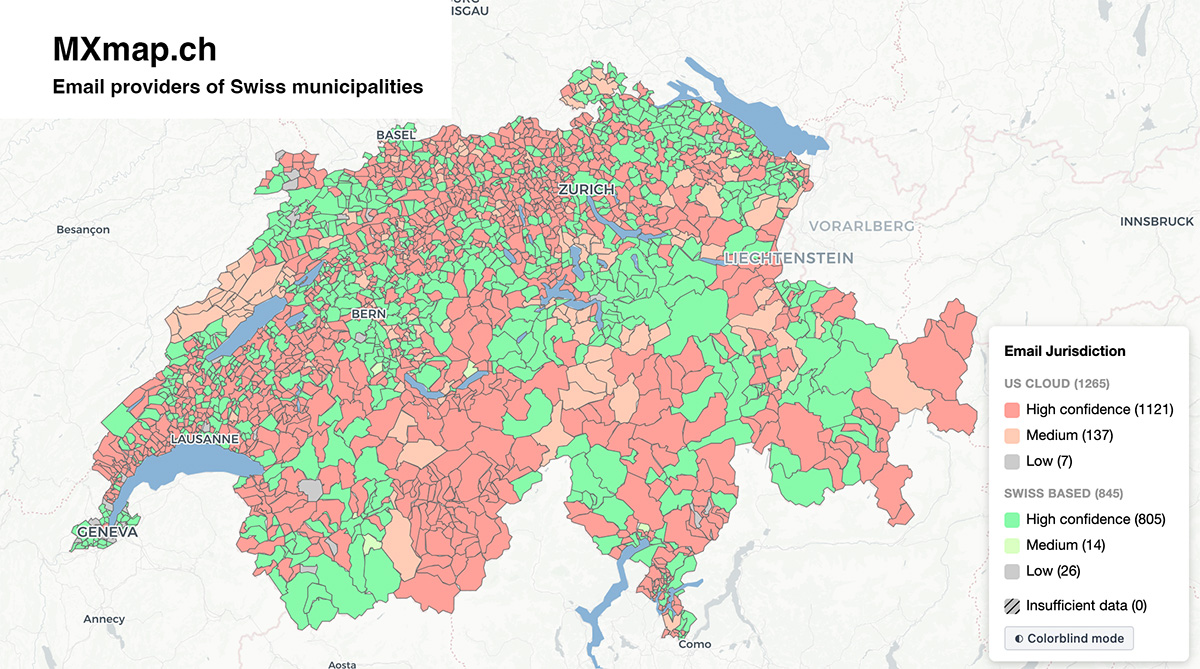 davidhuser/mxmap
Automated pipeline that resolves Swiss municipality domains, scrapes websites for email addresses, and classifies email providers via MX, SPF, DKIM,…
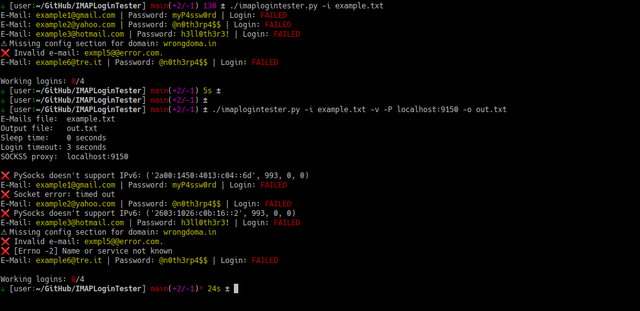 rm1984/imaplogintester
A simple Python script that reads a text file with lots of e-mails and passwords, and tries to check if those credentials are valid by trying to…
 black-scorp10/email-vulnerability-checker
Automated SPF and DMARC configuration checker that identifies email spoofing vulnerabilities across single or bulk domains using DNS lookups.
 djackreuter/cve-2023-23397-poc
C# PoC exploit for CVE-2023-23397 that sends malicious Outlook meeting invites with a UNC path trigger for NTLM credential theft.
 machine1337/smtpshell
A simple Reverse Shell that can communicate through Gmail SMTP or any other SMTP to evade network restrictions
 j0eyv/cve-2023-23397
Proof-of-concept exploit for CVE-2023-23397, an Outlook/Exchange privilege escalation vulnerability that triggers NTLM credential theft via a…
 rspamd/rspamd
Spam filtering and email processing framework with regex rules, statistical analysis, custom Lua plugins, and external blocklists for MTA integration.