Moniker-Link--CVE-2024-21413-

Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…

Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…

LetsDefend SOC336 case study on CVE-2025-21298

Insecure Direct Object Reference (IDOR vulnerability) in SOGo Webmail Allows a user to send emails on behalf of another user.

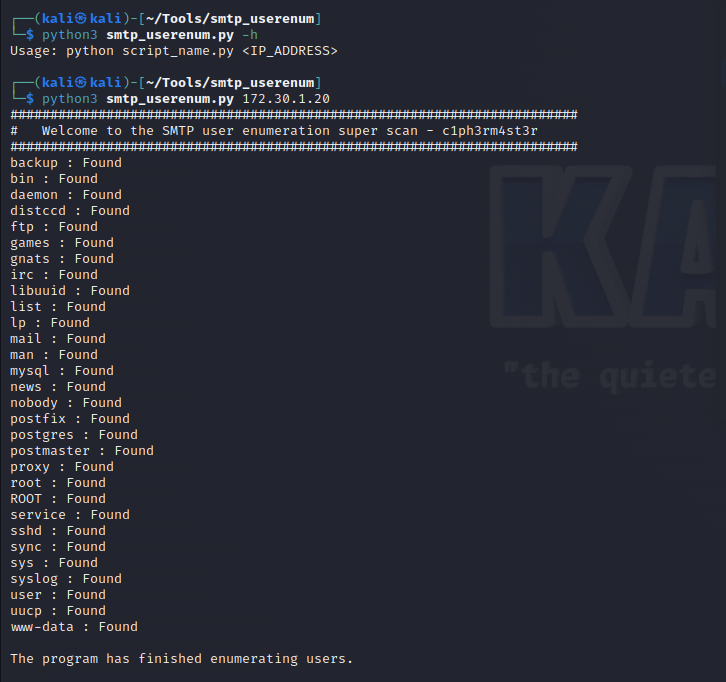
Python script for enumerating SMTP users by leveraging VRFY and EXPN commands to identify valid email accounts on a target mail server.

Simulate realistic phishing campaigns with credential harvesting, email tracking, and landing page cloning for security awareness training and…

ThePhish: an automated phishing email analysis tool

Bulk domain spoofability checker using authoritative SPF and DMARC record analysis with custom, real-world tested spoof logic and optional DKIM…

Open source platform for cyber security analysts with many features for threat intelligence and detection engineering.

Disposable email inbox powered by serverless mailgun kittens

small python3 tool to check common vulnerabilities in SMTP servers

Open-source interactive security awareness training library with 130+ SCORM exercises covering phishing, vishing, BEC, MFA fatigue, and OWASP AI/LLM…

Tool to find SMTP servers vulnerable to open relay

amavis is a high-performance email content filter framework written in Perl.

Automated SPF and DMARC configuration checker that identifies email spoofing vulnerabilities across single or bulk domains using DNS lookups.

Open .eml test set for evaluating how email security controls and AI mailbox assistants handle indirect prompt injection across disclosure,…

Instructions for installing a vulnerable version of Exim and its expluatation

A curated portfolio showcasing my SOC investigations, threat hunting projects, DFIR labs, detection engineering, technical blogs, and cybersecurity…

Lab write-up analyzing CVE-2024-21413 Outlook Moniker Link exploitation, NetNTLMv2 credential leakage via SMB, detection with YARA/Wireshark, and…