
CVE-2021-34473-Exchange-ProxyShell
 je6k/cve-2021-34473-exchange-proxyshell
对Exchange Proxyshell 做了二次修改,精确的拆分、实现辅助性安全测试。
email-securityexploitationpayload-generation+3
17
je6k/cve-2021-34473-exchange-proxyshell对Exchange Proxyshell 做了二次修改,精确的拆分、实现辅助性安全测试。

 r00tb1t/cve-2024-21413-poc
Microsoft Outlook Information Disclosure Vulnerability (leak password hash) - CVE-2024-21413 POC
 d0rb/cve-2024-21378
This repository contains an exploit for targeting Microsoft Outlook through Exchange Online, leveraging a vulnerability to execute arbitrary code via…
 djackreuter/cve-2023-23397-poc
C# PoC exploit for CVE-2023-23397 that sends malicious Outlook meeting invites with a UNC path trigger for NTLM credential theft.
 biutrap/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, demonstrating SMTP command injection via crafted RCPT TO header to trigger service status changes.
 romain-deperne/cve-2026-34975
CRLF email header injection in Plunk raw MIME construction — CVE-2026-34975 / CVSS 8.5
 hainhc/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…
 praneethnaidu1910-cmd/cve-2023-23397-purple-team
Purple team project exploiting CVE-2023-23397 Outlook NTLM leak with phishing delivery, plus Sigma/Wazuh detections mapped to MITRE ATT&CK for the…
 grn-bogo/cve-2023-23397
Python script to create a message with the vulenrability properties set
 ahmetkarakayaoffical/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Bu betik, Microsoft Outlook'ta keşfedilen ve CVSS değeri 9.8 olan önemli bir güvenlik açığı olan CVE-2024-21413 için bir kavram kanıtı (PoC)…
 r3dcl1ff/cve-2022-41040
mitigation script for MS Exchange server vuln
 alicangnll/cve-2023-23397
CVE-2023-23397 - Microsoft Outlook Vulnerability
 michael-david-fry/cve-2024-39929
POC to test CVE-2024-39929 against EXIM mail servers
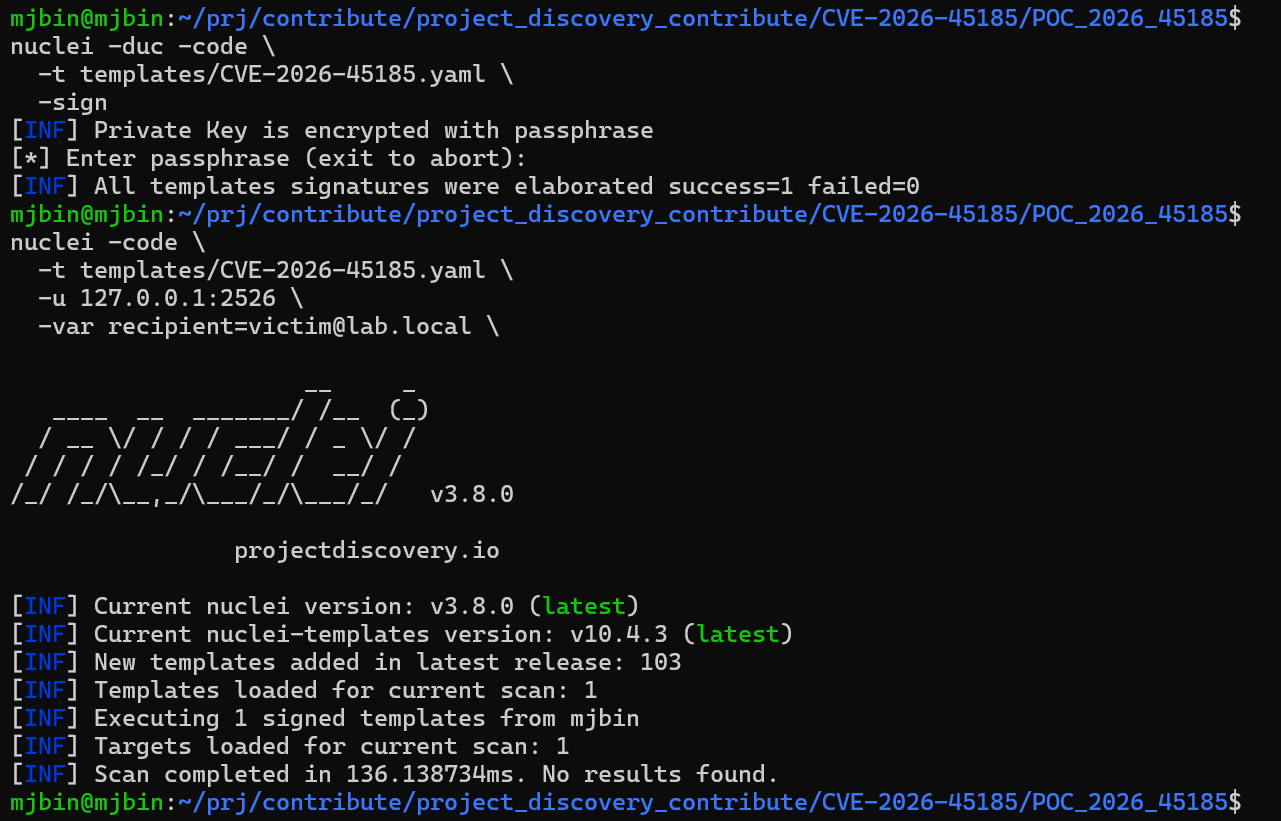 mj-bin/poc_cve-2026-45185
POC_CVE-2026-45185 for nuclei-templates
 ashwesker/ashwesker-cve-2025-68645
POC BLH Magelang CSIRT 2026 by babyrootkid