
splitting-the-email-atom
 portswigger/splitting-the-email-atom
Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
ctfeducationemail-security+7
100
portswigger/splitting-the-email-atomResearch materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
 oisf/suricata
Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…
 noxxi/mime-is-broken
Test cases for broken MIME and tools to generate and process these
 saykino/cve-2026-31283
Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…
 saykino/cve-2025-54320
Proof-of-concept for CVE-2025-54320: an email bombing vulnerability in Ascertia SigningHub's Invite User API due to missing rate limiting, allowing…
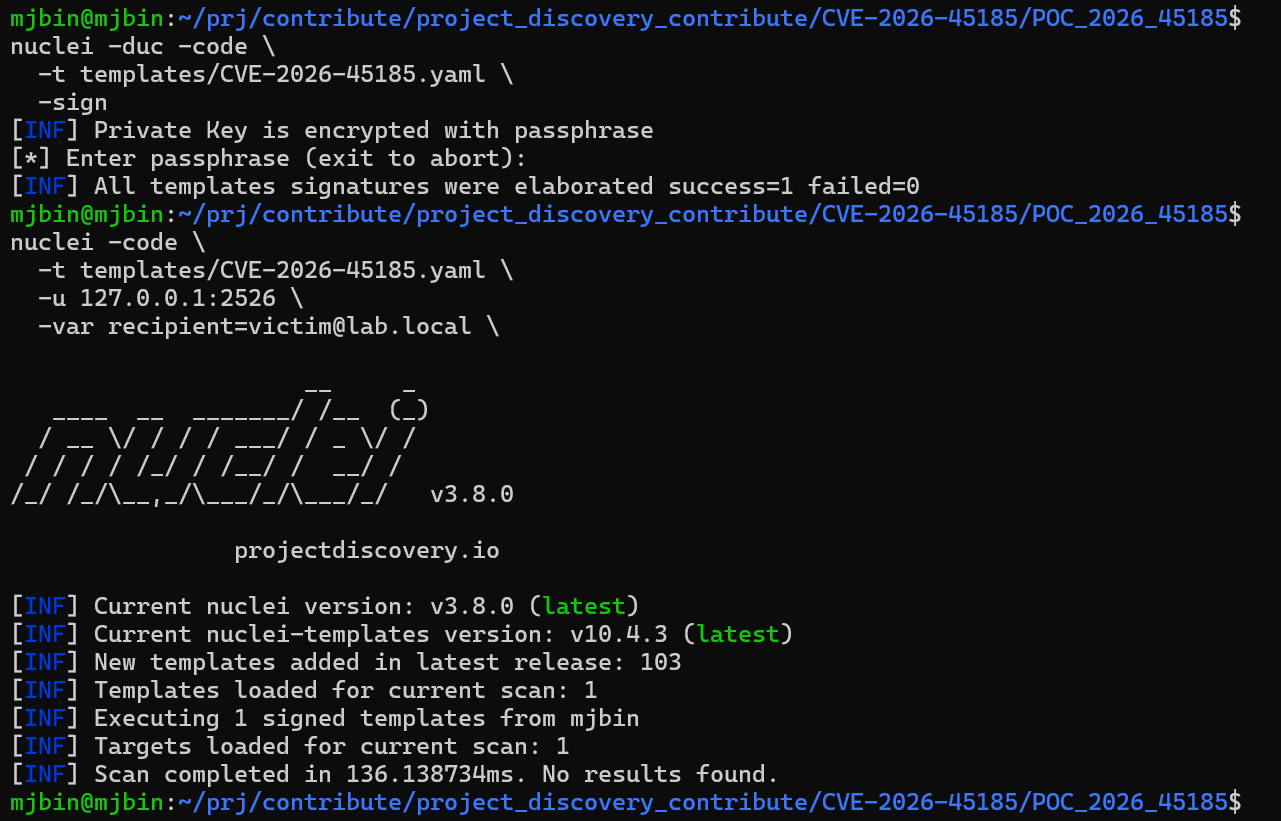 mj-bin/poc_cve-2026-45185
POC_CVE-2026-45185 for nuclei-templates
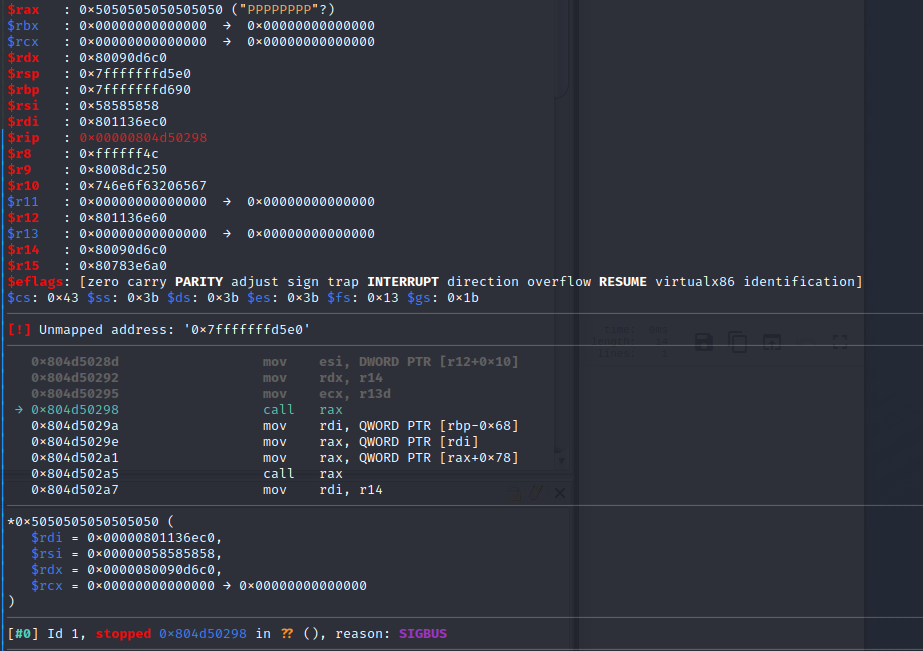 ly1g3/cisco-cve-2023-31488
Cisco Email Security Appliance: Email to zero-click RCE as root - Remote Code Execution/Memory Corruption/ROP-chain
 derrickschoen/laravel-framework
Fork of laravel/framework 10.50.2 with CVE-2026-48019 (CRLF injection in default email rule) backported into ValidatesAttributes::validateEmail.…
 0neb1n/cve-2020-16947
Proof-of-concept exploit for CVE-2020-16947, a Microsoft Outlook RCE triggered by malformed HTML content leading to a heap buffer overflow and remote…
 0neb1n/cve-2020-1493
Technical analysis and PoC details for CVE-2020-1493, a zero-click Outlook RCE triggered by malformed MS-TNEF attachments leading to remote code…
 sublime-security/ics-phishing-toolkit
Open source tooling to stop ICS phishing (malicious calendar invites)