
RedTeamScripts
 mr-un1k0d3r/redteamscripts
Collection of offensive red team scripts including process termination, SPF bypass for phishing, password spraying, and ColdFusion password…
email-securityexploitationpassword-attacks+4
148
mr-un1k0d3r/redteamscriptsCollection of offensive red team scripts including process termination, SPF bypass for phishing, password spraying, and ColdFusion password…
 mbanyamer/cve-2026-25916-roundcube-webmail-dom-based-xss-exploit-via-svg-href-attribute
Python exploit for Roundcube Webmail DOM-based XSS (CVE-2026-25916) via SVG href attributes, enabling session hijacking and data exfiltration through…
 jishino567/cve-2026-73570
Python PoC for CVE-2026-73570, an SMTP command injection in Zimbra. Sends malformed RCPT TO payloads to trigger shell command execution via…
 jenderal92/shadow-vault
Shadow Vault – Add shadow users with SHA-512 hash, auto aging match, multiple write fallbacks.
 pedro-lucas-melo/estudo-de-caso-cve-2024-21413
Um estudo de caso do CVE-2024-21413. Usado como parâmetro a sala do TryHackMe Moniker Link (CVE-2024-21413). Feito edições com claude code no exploit.
 p4x1s/cve-2023-23397-poc
CVE-2023-23397漏洞的简单PoC,有效载荷通过电子邮件发送。
 th3hellion/cve-2024-21413
Python exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Sends a crafted email via SMTP to trigger code execution…
 phaedrik/cve-2023-23397-poc
Two POCs I created for the CVE-2023-23397 Outlook NTLM vulnerability, to be used internally.
 tiepologian/cve-2023-23397
Proof of Concept for CVE-2023-23397 in Python
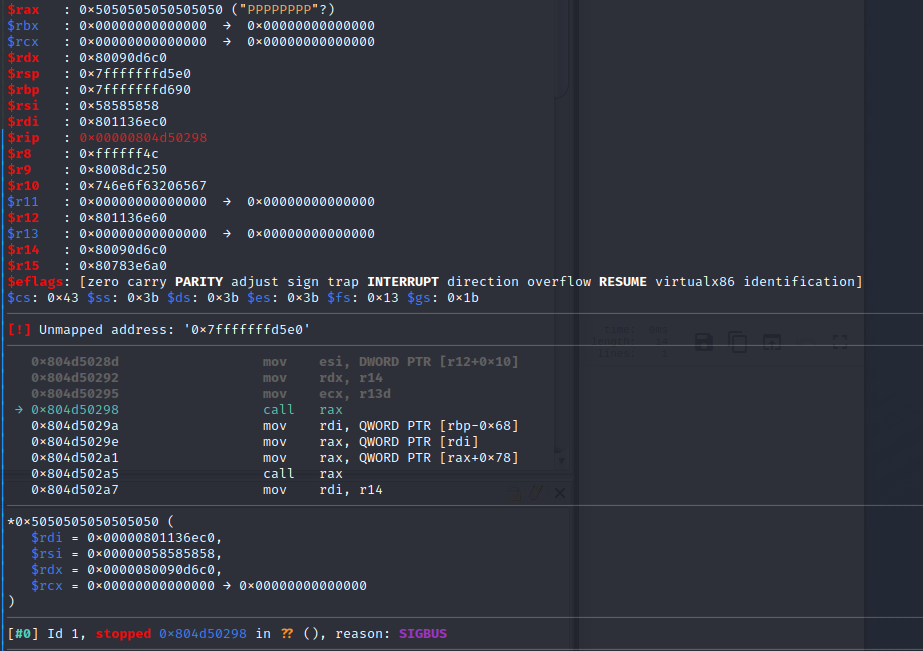 ly1g3/cisco-cve-2023-31488
Cisco Email Security Appliance: Email to zero-click RCE as root - Remote Code Execution/Memory Corruption/ROP-chain
 jump-wang-111/amzword
An automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.
 je6k/cve-2021-34473-exchange-proxyshell
对Exchange Proxyshell 做了二次修改,精确的拆分、实现辅助性安全测试。
 djackreuter/cve-2023-23397-poc
C# PoC exploit for CVE-2023-23397 that sends malicious Outlook meeting invites with a UNC path trigger for NTLM credential theft.
 amirzargham/cve-2024-37383-exploit
Roundcube mail server exploit for CVE-2024-37383 (Stored XSS)
 wyatu/cve-2018-8581
CVE-2018-8581 | Microsoft Exchange Server Elevation of Privilege Vulnerability
 trackflaw/cve-2023-23397
Simple PoC of the CVE-2023-23397 vulnerability with the payload sent by email.
 themehackers/cve-2024-21413
CVE-2024-21413 | Microsoft Outlook Remote Code Execution Vulnerability PoC