
CVE-2018-8581
 qiantu88/cve-2018-8581
CVE-2018-8581
email-securityexploitationpenetration-testing+3
57 years ago
qiantu88/cve-2018-8581CVE-2018-8581
 aahmad097/badoutlook
Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…
 qsecure-labs/overlord
Python-based CLI for automated red team infrastructure deployment on AWS and Digital Ocean, with modular support for C2, email servers, HTTP…
 trackflaw/cve-2023-23397
Simple PoC of the CVE-2023-23397 vulnerability with the payload sent by email.
 sensepost/ruler
A tool to abuse Exchange services
 tiepologian/cve-2023-23397
Proof of Concept for CVE-2023-23397 in Python
 j0eyv/cve-2023-23397
Proof-of-concept exploit for CVE-2023-23397, an Outlook/Exchange privilege escalation vulnerability that triggers NTLM credential theft via a…
 wyatu/cve-2018-8581
CVE-2018-8581 | Microsoft Exchange Server Elevation of Privilege Vulnerability
 quickbreach/exchangerelayx
An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.
 mbanyamer/cve-2026-25916-roundcube-webmail-dom-based-xss-exploit-via-svg-href-attribute
Python exploit for Roundcube Webmail DOM-based XSS (CVE-2026-25916) via SVG href attributes, enabling session hijacking and data exfiltration through…
 jishino567/cve-2026-73570
Python PoC for CVE-2026-73570, an SMTP command injection in Zimbra. Sends malformed RCPT TO payloads to trigger shell command execution via…
 jump-wang-111/amzword
An automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.
 pedro-lucas-melo/estudo-de-caso-cve-2024-21413
Um estudo de caso do CVE-2024-21413. Usado como parâmetro a sala do TryHackMe Moniker Link (CVE-2024-21413). Feito edições com claude code no exploit.
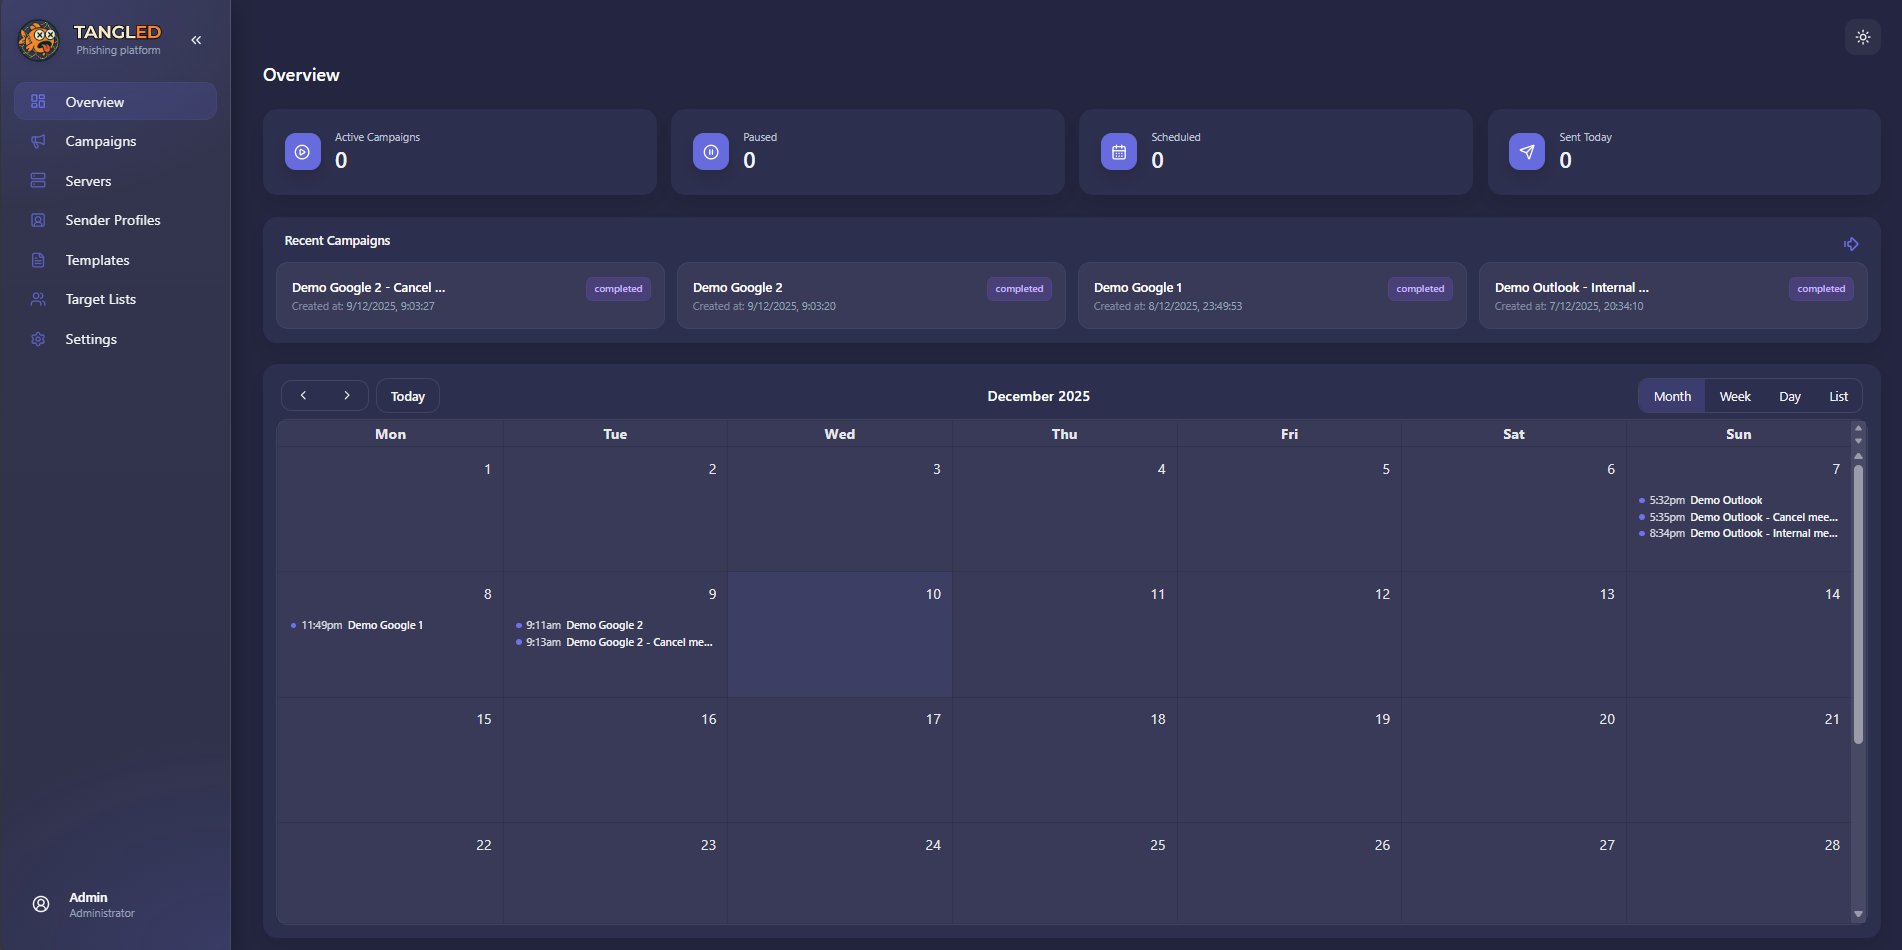 ineesdv/tangled
Open-source offensive security platform for conducting phishing campaigns that weaponizes iCalendar automatic event processing.
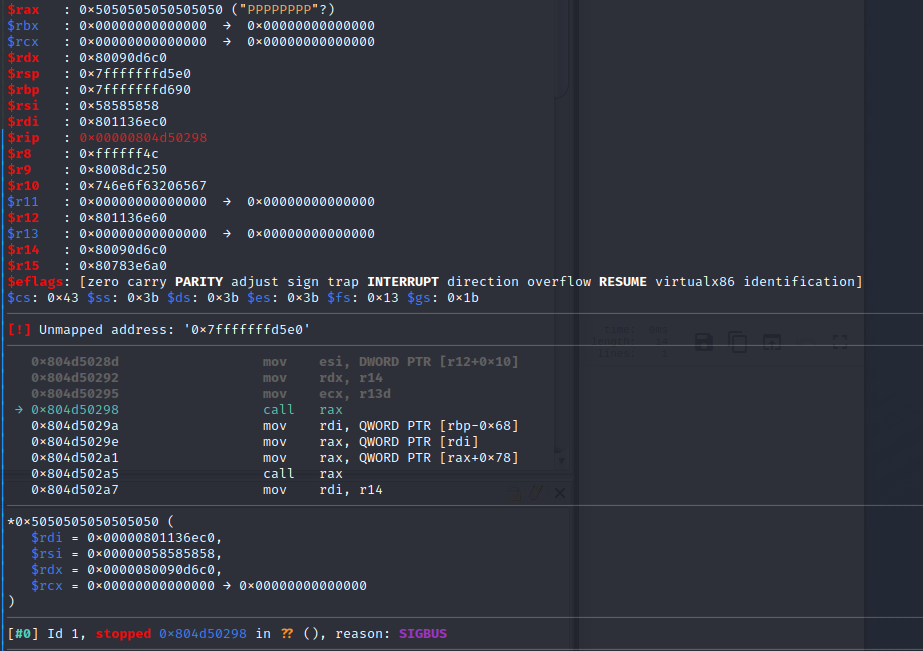 ly1g3/cisco-cve-2023-31488
Cisco Email Security Appliance: Email to zero-click RCE as root - Remote Code Execution/Memory Corruption/ROP-chain
 bhatbhupendra/moniker-link--cve-2024-21413-
Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…
 dionissh/cve-2024-21413
Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP-based phishing email delivery, malicious RTF attachment generation, and…
 themehackers/cve-2024-21413
CVE-2024-21413 | Microsoft Outlook Remote Code Execution Vulnerability PoC