
CVE-2026-54806
 joshuavanderpoll/cve-2026-54806
Proof-of-concept exploit for CVE-2026-54806: unauthenticated PHP object injection in WP Activity Log plugin enabling blind RCE via User-Agent header.…
educationexploitationlabs-practice+5
5
joshuavanderpoll/cve-2026-54806Proof-of-concept exploit for CVE-2026-54806: unauthenticated PHP object injection in WP Activity Log plugin enabling blind RCE via User-Agent header.…
 skrkcb2/cve-2025-0924-different
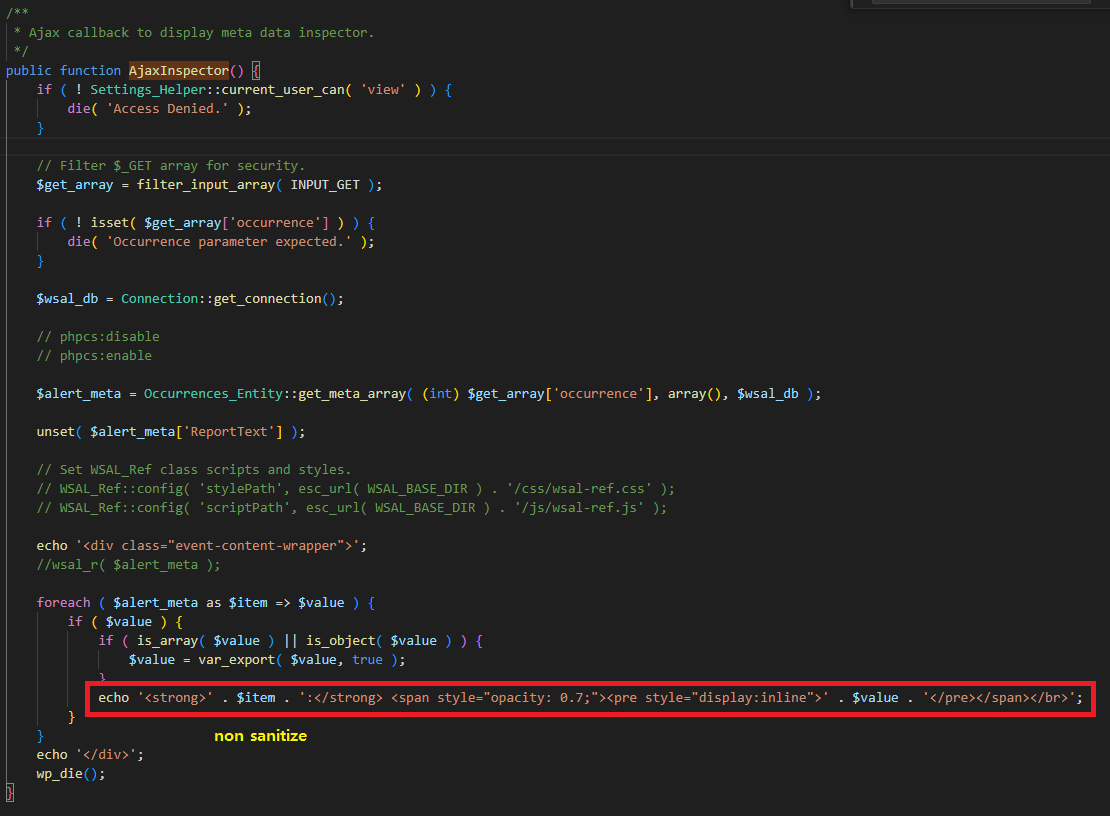
Technical analysis of CVE-2025-0924, a Stored XSS vulnerability in WP Activity Log plugin for WordPress. Includes root cause analysis, exploitation…
 ghoxtbyte/cve-2026-18464
Security advisory and technical research notes for CVE-2026-18464, an unauthenticated denial-of-service flaw in the WP Maps Pro WordPress plugin…
 ghoxtbyte/cve-2026-16265
Technical advisory and research notes for CVE-2026-16265, a Subscriber+ denial-of-service flaw in the WP Maps WordPress plugin fixed in version 4.9.7.
 dinosn/cve-2026-6379
Docker-based lab kit for CVE-2026-6379, an unauthenticated SQL injection in WP Photo Album Plus. Includes time-based blind PoC, root-cause analysis,…
 squamity/cve-2026-8181-poc
Python PoC for CVE-2026-8181, a critical authentication bypass in Burst Statistics WordPress plugin. Includes exploit automation, bulk scanning, and…
 sudo-wp/sudowp-hooks-visualizer
A security-hardened fork of "Simply Show Hooks". Replaces the compromised original (CVE-2024-6297) and patches unlisted Cross-Site Scripting (XSS)…
 dthkhang/cve-2023-5561-poc
PoC exploit for CVE-2023-5561 that enumerates WordPress user email addresses via the /wp-json/wp/v2/users API endpoint. For authorized security…
 geniuszly/cve-2024-5522
PoC exploit scanner for CVE-2024-5522 in WordPress. Scans target URLs with custom payloads to identify vulnerable sites, outputting color-coded…
 dinosn/cve-2026-87902-wordpress-lfi-lab
Reproduction lab + URL-list scanner + PoC for CVE-2026-87902 / GHSA-7hp8-65ch-5whp — WordPress get_page_template() unauthenticated LFI to conditional…
 codeb0ssx/ultimate-wp2shell
wp2shell — Pre-authentication RCE in WordPress Core (CVE-2026-60137 + CVE-2026-63030). Chains an SQL injection in author__not_in with batch-route…
 686f6c61/poc-aiowpm-cve-2026-19949
Reproducible Docker-based proof-of-concept for CVE-2026-19949, a second-order SQL injection in All-in-One WP Migration <= 7.109 that leaks the…
 nxploited/cve-2025-2266
Checkout Mestres do WP for WooCommerce 8.6.5 - 8.7.5 - Unauthenticated Arbitrary Options Update
 viardant/cve-2022-0739
Exploit for WP BookingPress (< 1.0.11) based on destr4ct POC.
 e1tex/python-cve-2020-25213
Python Interactive Exploit for WP File Manager Vulnerability. The File Manager (wp-file-manager) plugin before 6.9 for WordPress allows remote…
 aj2108/cve-2026-9848
CVE-2026-9848 is an Unauthenticated SQL Injection (SQLi) vulnerability affecting the WP Ticket (Customer Support Ticket System & Helpdesk) plugin for…
 incommatose/cve-2023-6063-poc
A Proof on Concept for CVE-2023-6063, a time-based blind SQL injection vulnerability in WP Fastest Cache ≤1.2.2.
 nxploited/cve-2025-23942-poc
WP Load Gallery <= 2.1.6 - Authenticated (Author+) Arbitrary File Upload