testenv
 sqlmapproject/testenv
A collection of web pages vulnerable to SQL injection flaws
database-securityeducationlabs-practice+3
sqlmapproject/testenvA collection of web pages vulnerable to SQL injection flaws
 compr00t/cve-2024-42327
Proof-of-concept exploit for CVE-2024-42327, an SQL injection vulnerability in Zabbix frontend API allowing non-admin users to execute arbitrary SQL…
 ivanesk315/cve-2023-25157
Local GeoServer/PostGIS lab reproducing OGC Filter SQL injection (CVE-2023-25157/25158) with vulnerable, patched, and mitigated A/B test modes.
 netw0rk7/cve-2019-9193-home-lab
This lab simulates CVE-2019-9193 - PostgreSQL COPY FROM PROGRAM RCE
 yucaerin/cve-2026-5118
Divi Form Builder <= 5.1.2 — Unauthenticated Privilege Escalation via Role Injection
 akanthed/secureai-scan
SecureAI-Scan is a CLI tool that scans TypeScript and JavaScript codebases for security issues specific to AI-powered apps — prompt injection, MCP…
 zycoder0day/cve-2026-5118
CVE-2026-5118 | Divi Form Builder <= 5.1.2 | Unauthenticated Privilege Escalation via Role Injection
 jeanback1/cve-2025-2304-exploit
Python exploit script for CVE-2025-2304, a mass assignment privilege escalation in Camaleon CMS. Automates CSRF token parsing and role parameter…
 razi-interactive/claude-project-scanner
Read-only safety scanner for Claude Code projects. Catches CVE-2025-59536, statusLine injection, prompt injection, and more.
 sarthak4126/web-app-pentesting
Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
 dwallener/entropicapublic
Public version of the Entropica repo
 bandrel/hashcatrosetta
Hashcat rule analyzer and interpreter - A Rosetta Stone for decoding hashcat rule syntax
 ethiack/cve-2023-29007
Proof-of-concept exploit for CVE-2023-29007, a Git arbitrary configuration injection vulnerability. Demonstrates exploitation via crafted repository…
 safety-research/red-teaming-auto-mode
Research code for red-teaming AI auto-mode monitors, including simulation evals, fuzzing, and monitor implementations for Claude Code and Codex…
 skorokithakis/stavrobot
An AI personal assistant with a focus on security.
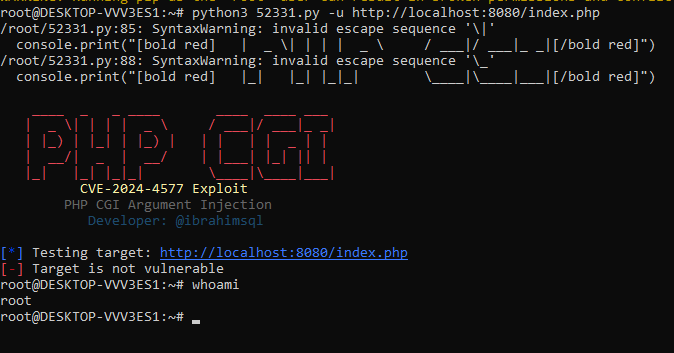 kanak-cypherx/cve-2024-4577-lab
Docker-based lab environment for studying CVE-2024-4577, a PHP-CGI argument injection vulnerability, with Apache and PHP 8.1.2 in CGI mode.
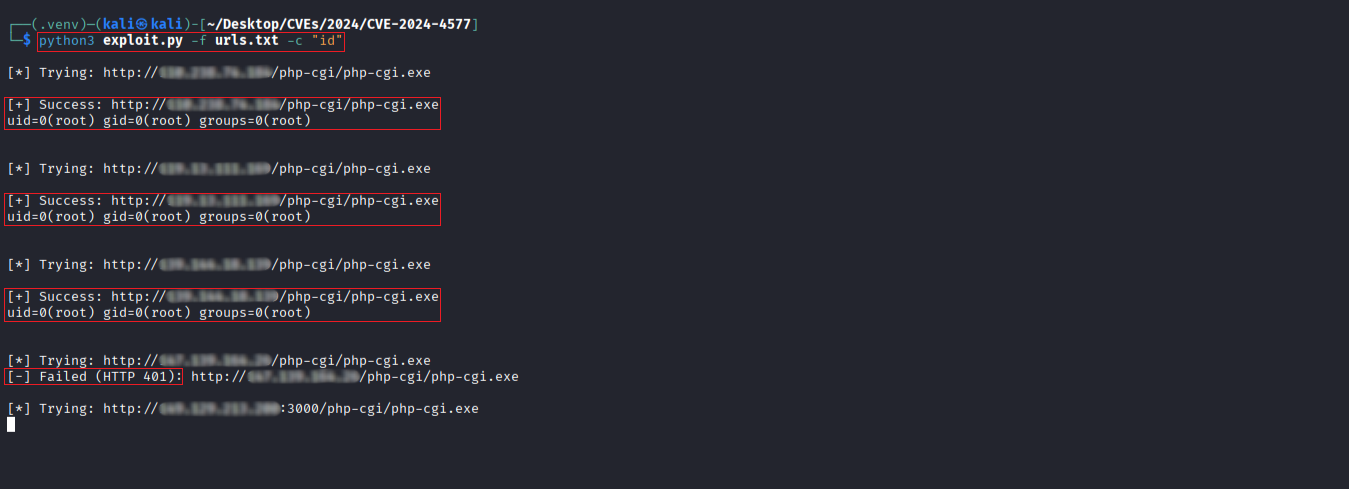 r0otk3r/cve-2024-4577
Scanner and exploit tool for CVE-2024-4577, a PHP CGI argument injection vulnerability enabling remote code execution on Windows systems. Includes…