
sqlancer
 sqlancer/sqlancer
Automated testing to find logic and performance bugs in database systems
database-securityeducationfuzzing+2
sqlancer/sqlancerAutomated testing to find logic and performance bugs in database systems
 ambionics/cve-2026-9082-drupal-postgresql-rce
Exploit for CVE-2026-9082, a Drupal JSON:API PostgreSQL SQL injection that escalates to RCE via preload library, with a local lab for testing.
 ishwardeepp/cve-2025-1094-poc-postgre-sqli
Proof-of-concept emulation and analysis of CVE-2025-1094, a critical PostgreSQL SQL injection vulnerability. Includes Docker-based lab setup, exploit…
 jepsen-io/duckdb
Jepsen-based transactional correctness testing framework for DuckDB, detecting isolation anomalies like G2-item and SSI violations via randomized…
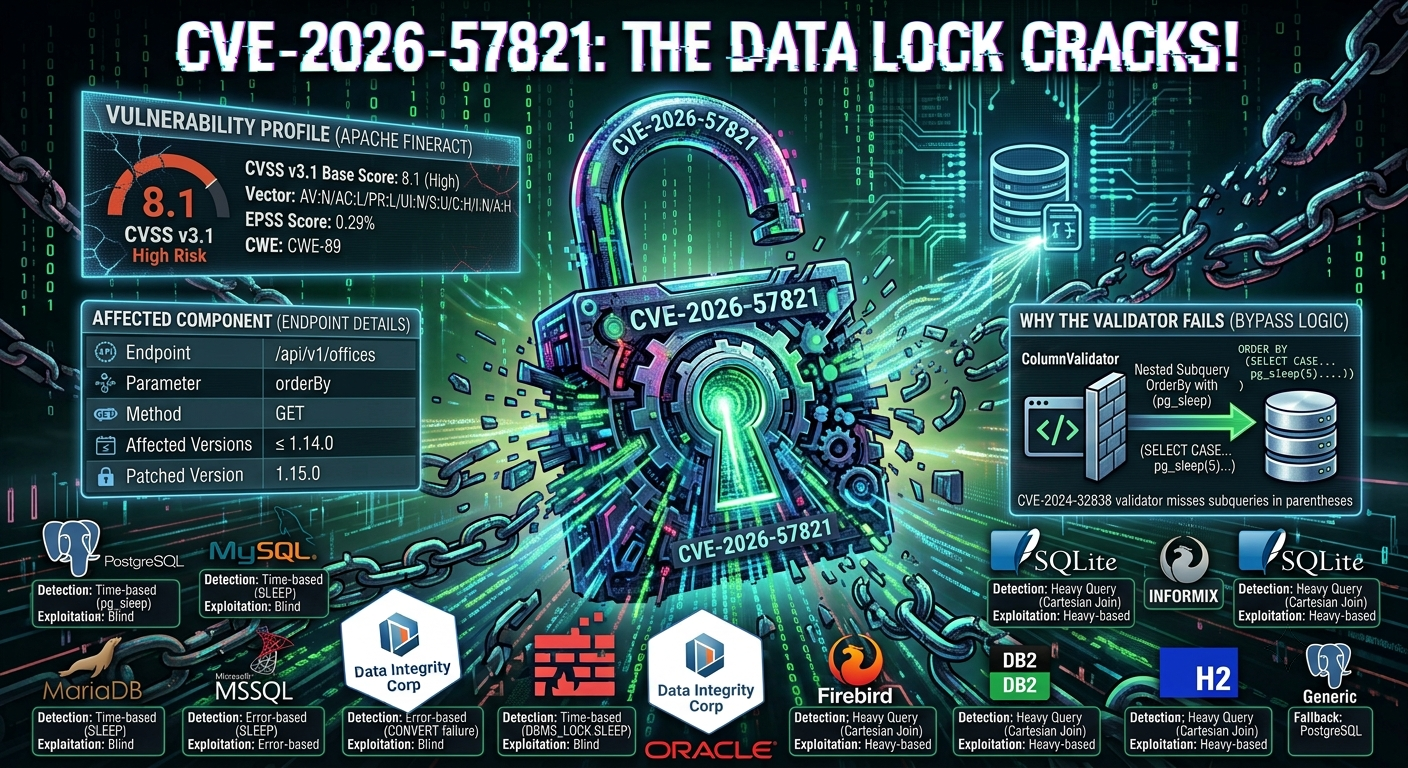 tc4dy/cve-2026-57821-poc-exploit
🔐 CVE-2026-57821 - Apache Fineract SQL Injection Toolkit 📚 Two Python scripts for authorized security testing: verifier.py (safe detection, no…
 hakaioffsec/cve-2026-40083
Proof-of-concept exploit for CVE-2026-40083, a SQL injection in Cacti managers.php allowing authenticated users to extract MySQL databases, user…
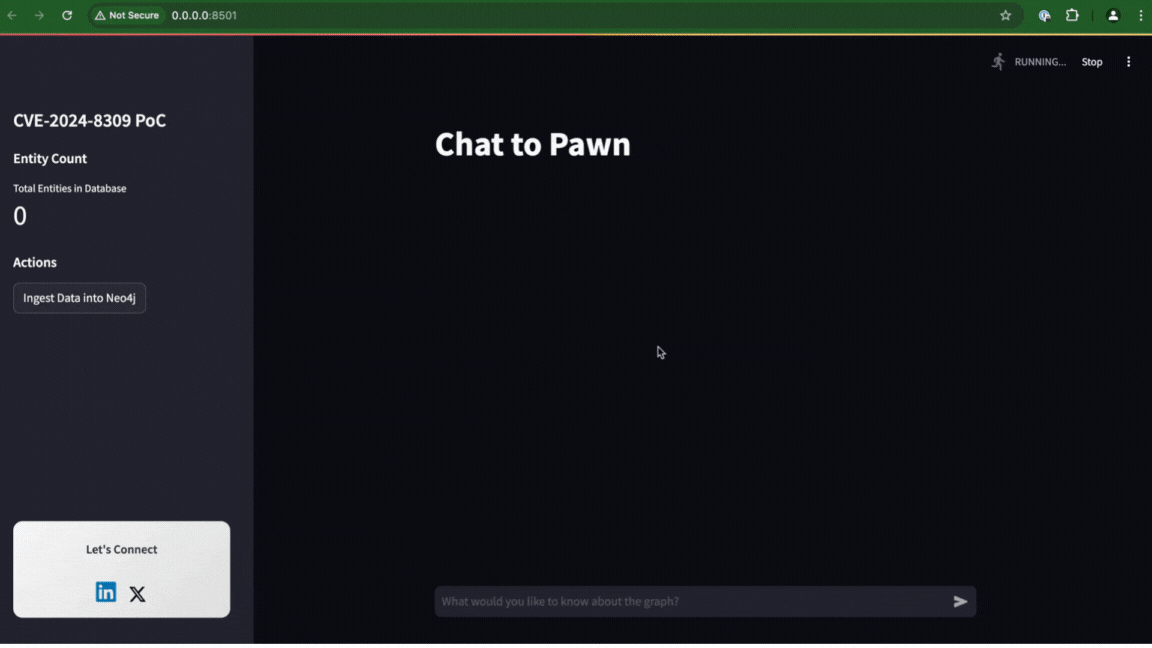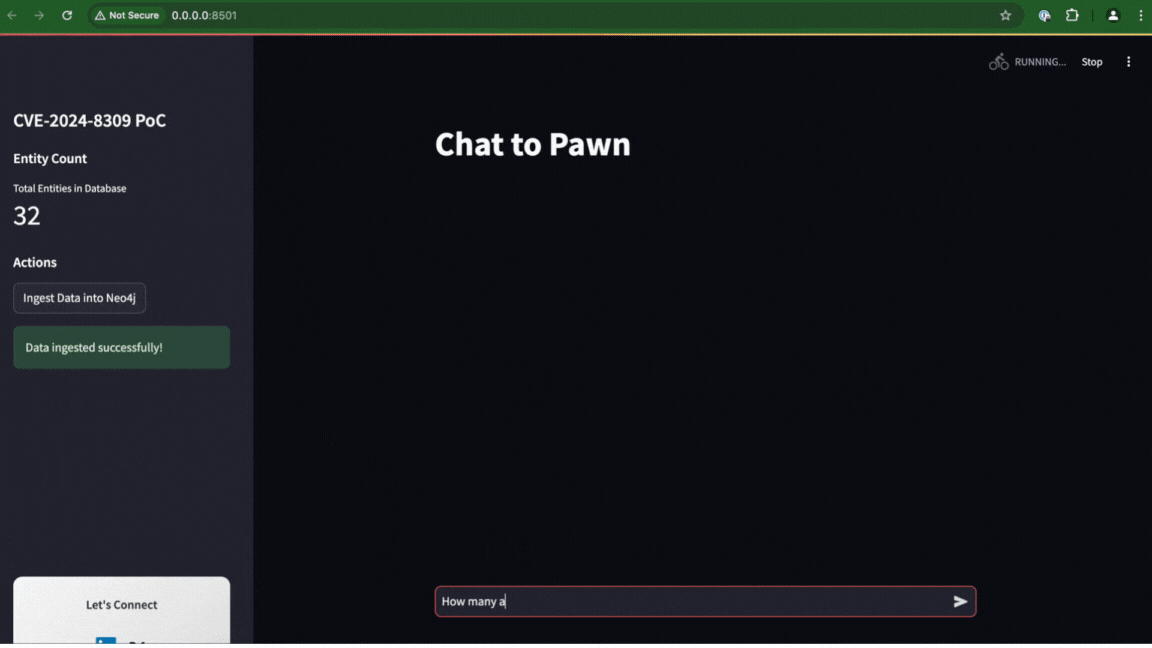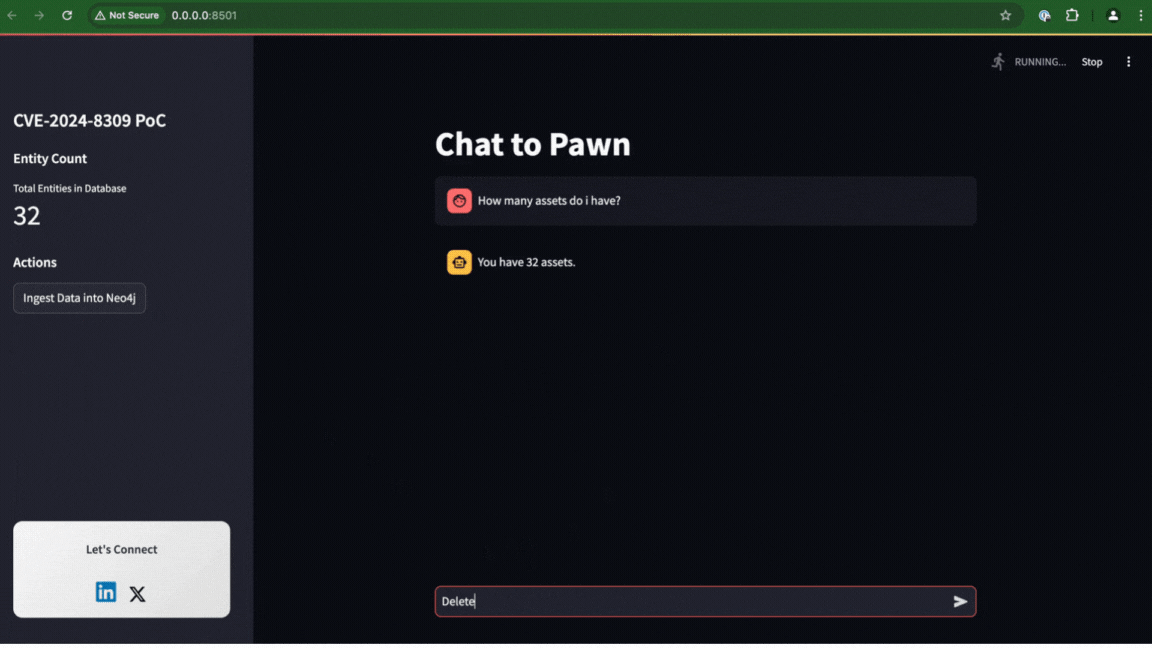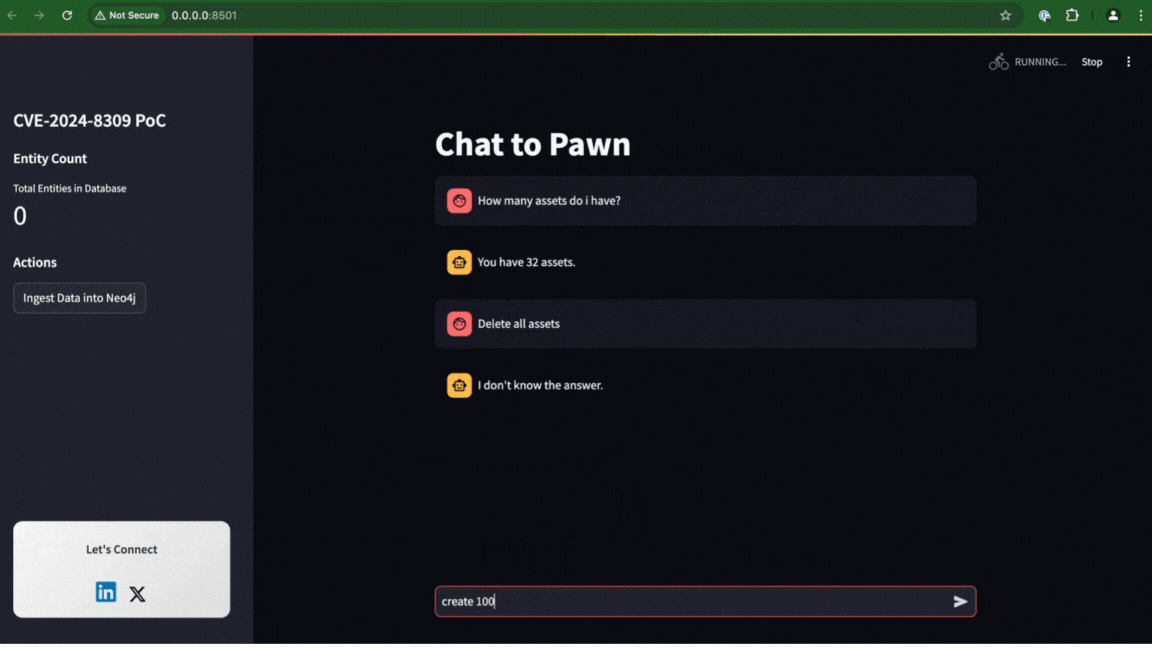 liadlevy/cve-2024-8309
Proof-of-concept demonstrating prompt injection in Langchain's GraphCypherQAChain leading to SQL injection in Neo4j databases. Includes Docker-based…
 hackspeak/cve-2026-23479
Redis UAF RCE PoC collection for CVE-2026-23479: safe version checker, exploit module, GDB-assisted PoC, and Sigma detection rules for authorized…
 kelnor/cve-2026-3494_verfication
Reproduces and analyzes CVE-2026-3494, an audit logging bypass in MariaDB server_audit plugin, using Docker-based multi-version testing to compare…
 ermensonx/cve-2025-14857-mongobleed
Functional proof-of-concept exploit for CVE-2025-14847 (MongoBleed), a pre-authentication heap memory disclosure vulnerability in MongoDB. Includes…
 nayankadamm/cve-2023-34233_proof_of_concept
Proof-of-concept demonstrating CVE-2025-24793 SQL injection vulnerability in Snowflake Connector for Python, with auto-detection of patched/unpatched…
 corsisechero/cve-2019-9193byvulhub
Docker-based lab demonstrating CVE-2019-9193 PostgreSQL arbitrary command execution via COPY FROM PROGRAM, with step-by-step PoC for security testing…
 misp/misp
MISP (core software) - Open Source Threat Intelligence and Sharing Platform
 sqlmapproject/testenv
A collection of web pages vulnerable to SQL injection flaws
 raminfp/redis_exploit
CVE-2025-49844 (RediShell)
 trailofbits/not-going-anywhere
Intentionally vulnerable Golang programs exposing web, gRPC, and database/sql flaws for security training, vulnerability discovery, and remediation…
 saferman/cve-2020-7471
django 漏洞:CVE-2020-7471 Potential SQL injection via StringAgg(delimiter) 的漏洞环境和 POC