
winrar-exploit
 skander1337/winrar-exploit
C++ implementation of CVE-2025-8088 WinRAR exploit using Alternate Data Streams to drop payloads into Windows Startup folder for persistence.
educationexploitationmalware-analysis+3
skander1337/winrar-exploitC++ implementation of CVE-2025-8088 WinRAR exploit using Alternate Data Streams to drop payloads into Windows Startup folder for persistence.
 chaudharyarjun/n0mac
Shell script that randomizes MAC addresses on system startup using macchanger, combining vendor prefixes with random suffixes for network interface…
 securitytemplates/sectemplates
Open source templates you can use to bootstrap your security programs
 xi0onamdev/winrar-cve-2025-8088-exploitation-toolkit
GUI tool for creating malicious RAR archives exploiting CVE-2025-8088 path traversal. Uses NTFS ADS stealth and RAR5 header injection for payload…
 yetazyyy/cve-2025-4606
Python-based scanner that tests WordPress sites for CVE-2025-4606, a privilege escalation vulnerability in the Sala theme allowing unauthenticated…
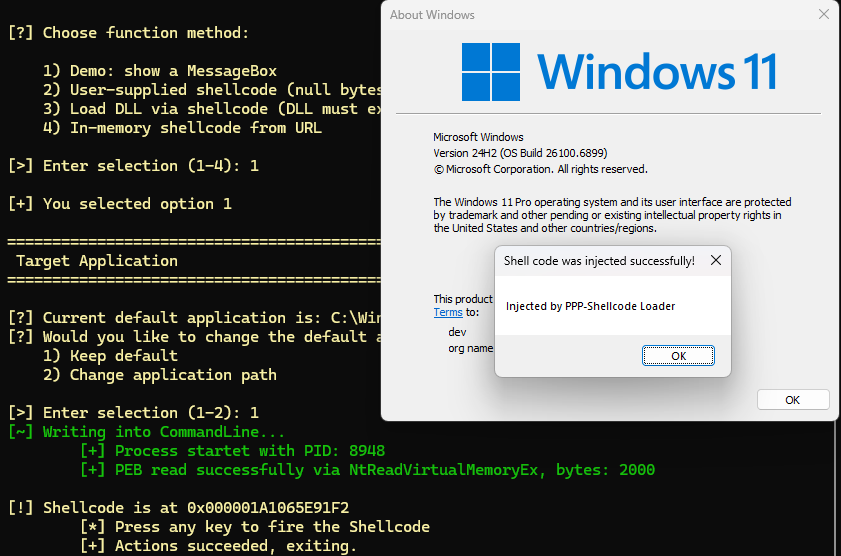 orange-cyberdefense/p3-loader
P³-Shellcode Loader is a loader that implements a code injection technique which leverages the Process Parameters structure as an execution and…