
CVE-2024-29943
 seadragnol/cve-2024-29943
Reproducing CVE-2024-29943 for Windows, based on https://github.com/bjrjk/CVE-2024-29943
binary-exploitationeducationexploitation+2
2
seadragnol/cve-2024-29943Reproducing CVE-2024-29943 for Windows, based on https://github.com/bjrjk/CVE-2024-29943
 nataliadiak/windows-x86-shellcode-poc
Windows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.
 vp777/windows-kernel-exploitation
Techniques and tools for Windows kernel exploitation, covering pool overflow exploitation, segment heap metadata abuse, and debugging scripts for…
 d0rb/packetpirate
A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
 amlweems/gringotts
proof of concept for CVE-2020-0601
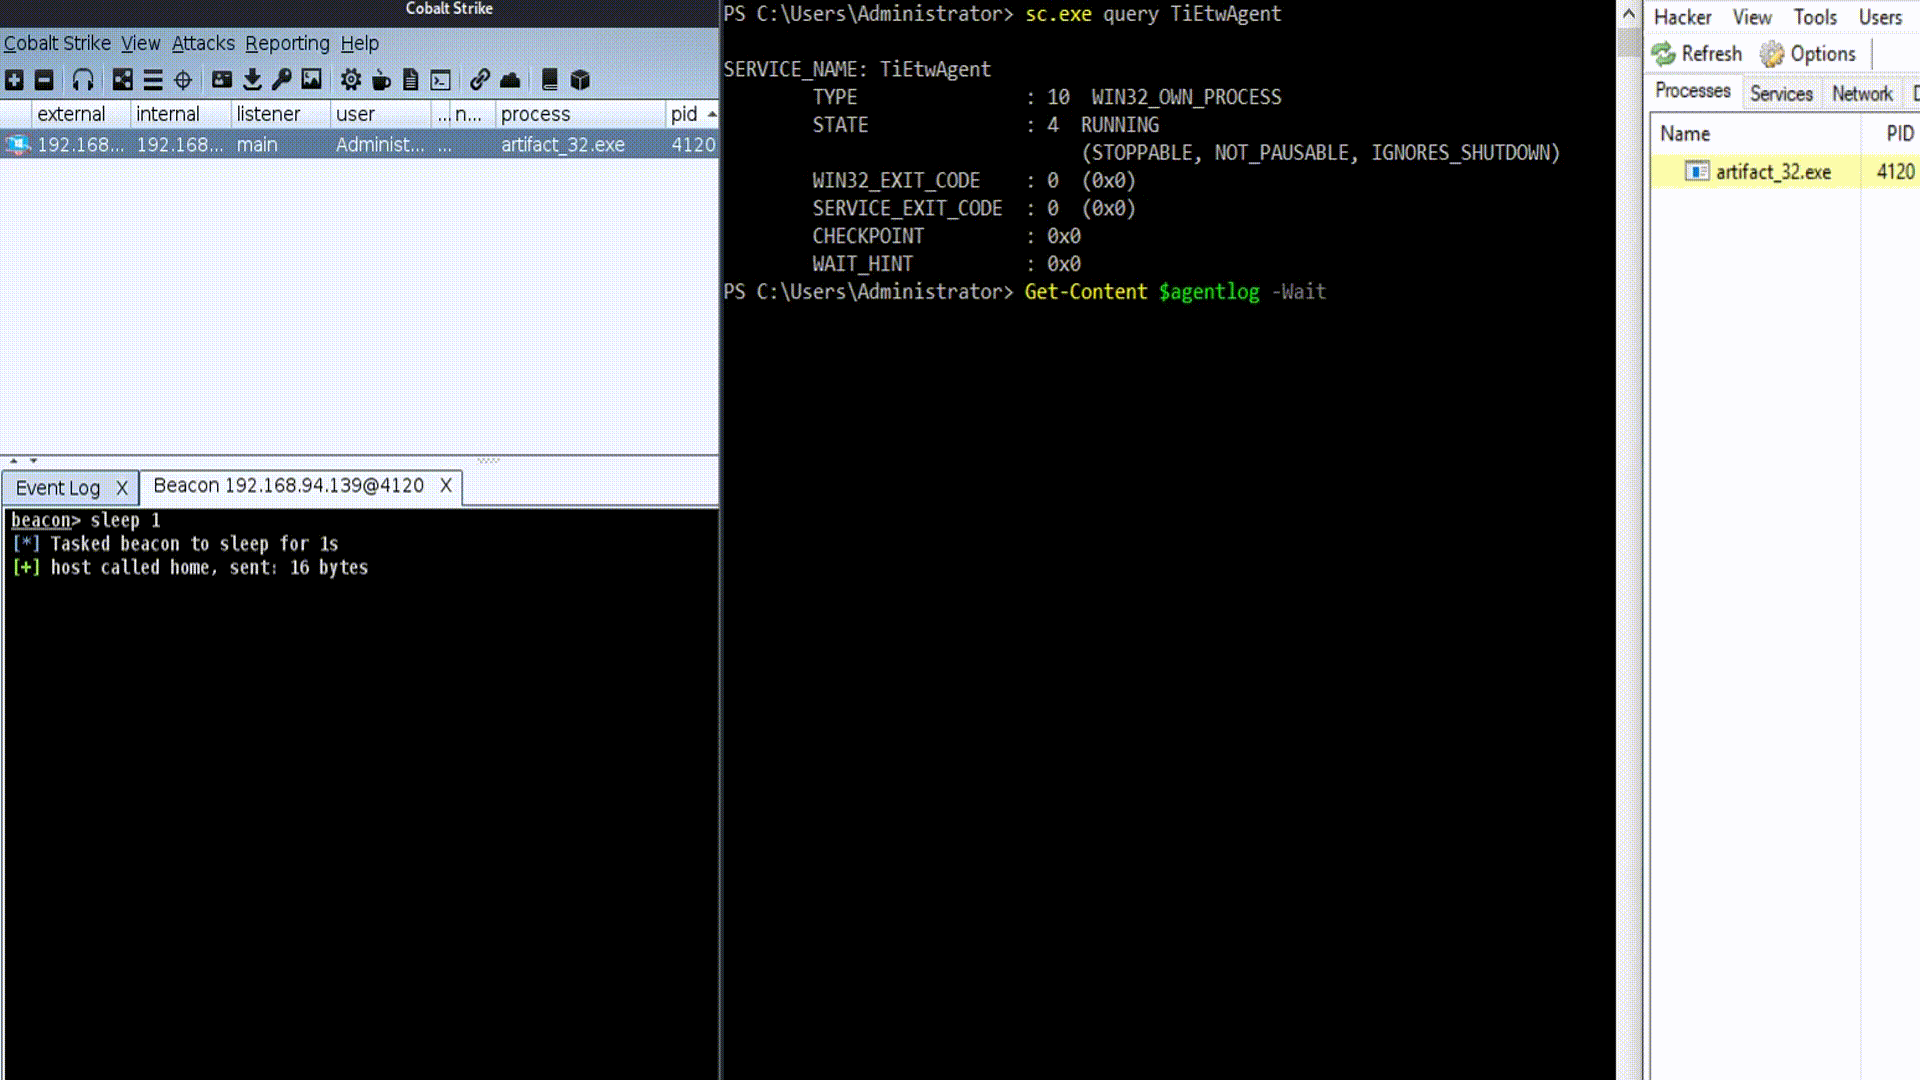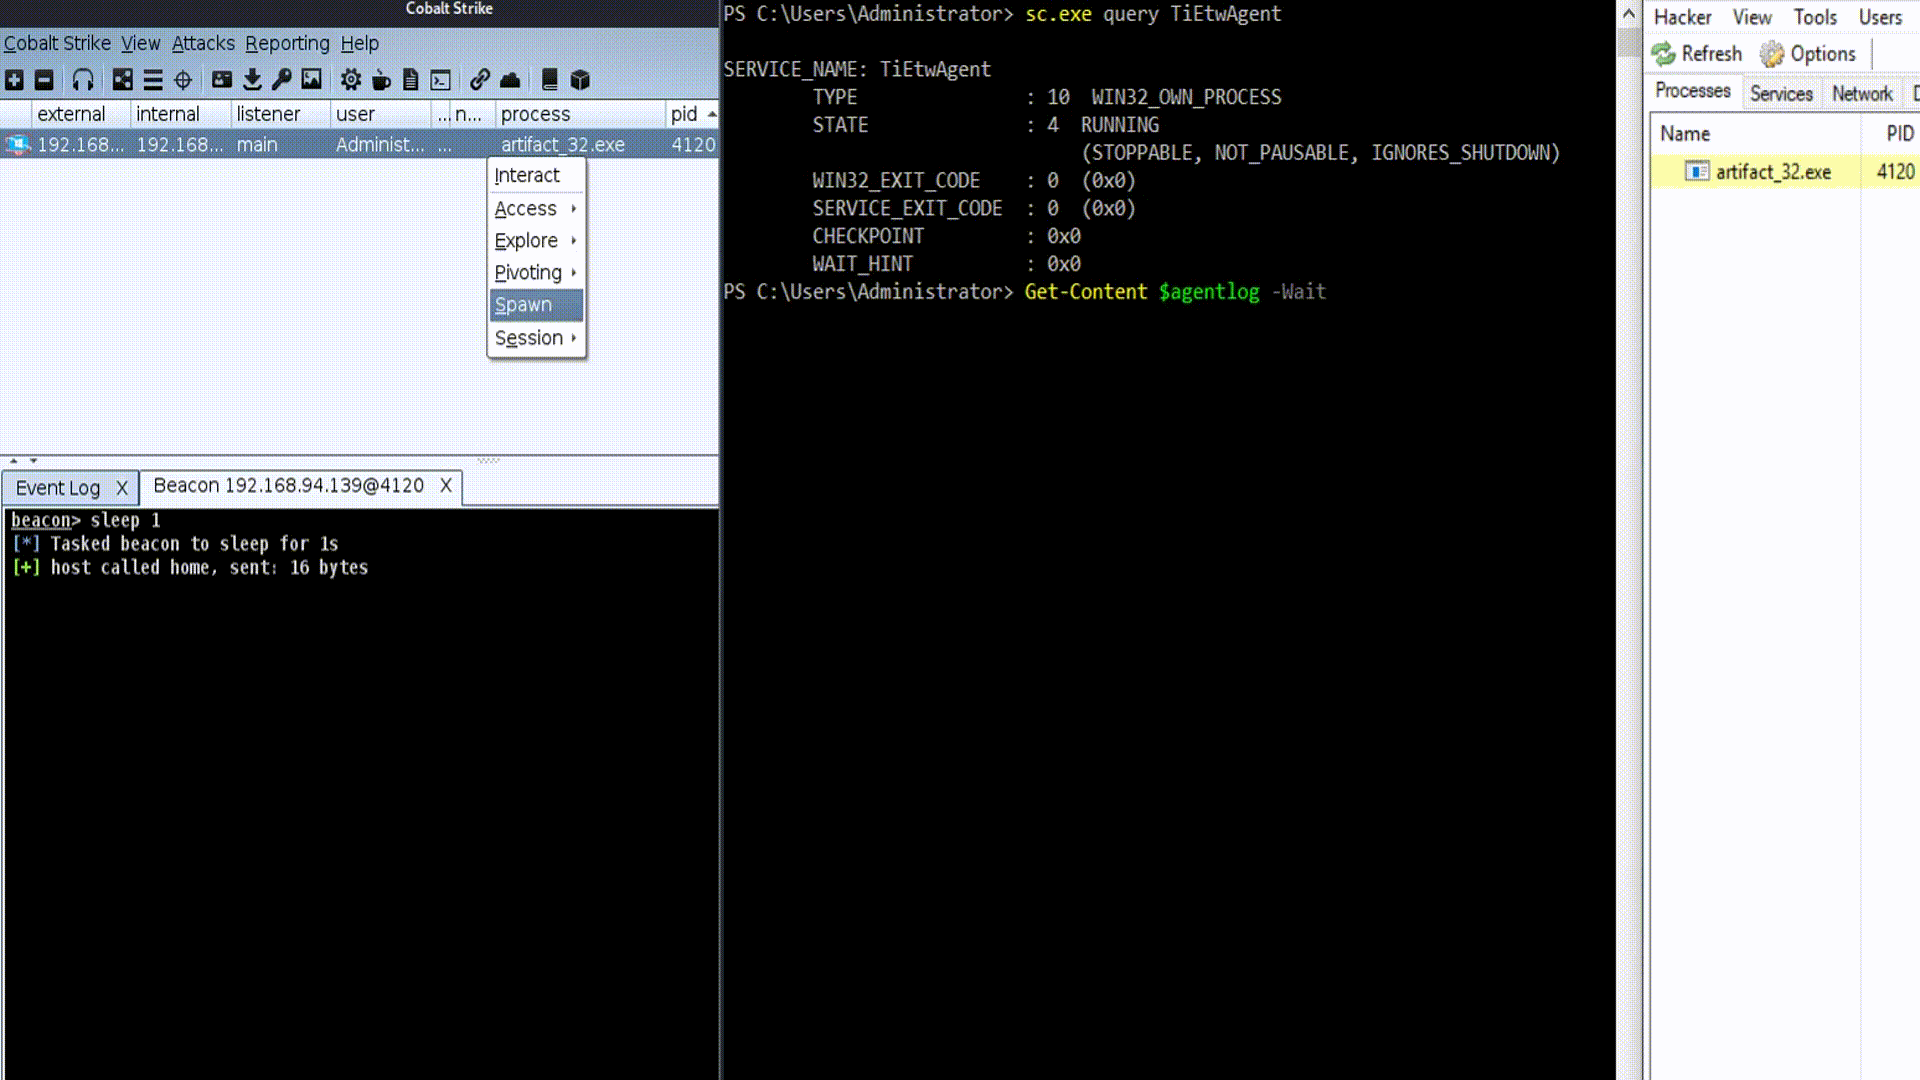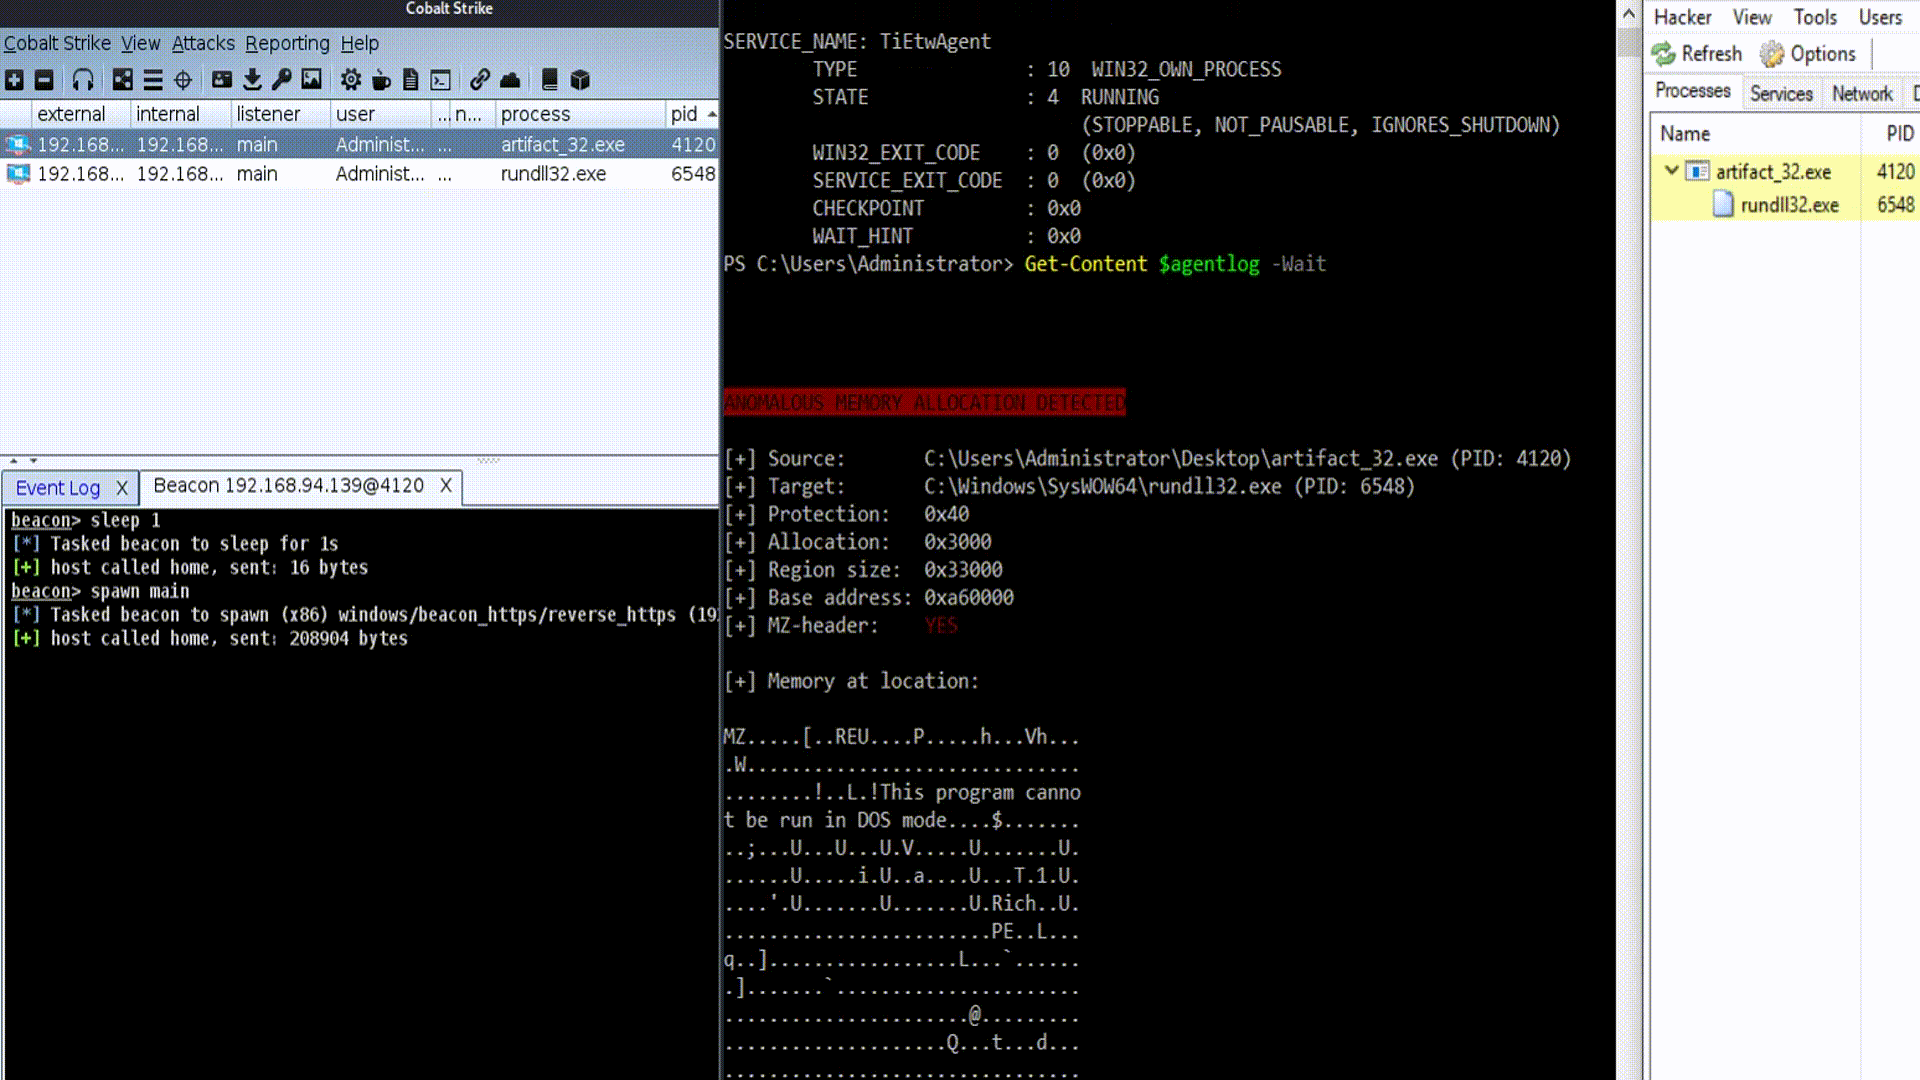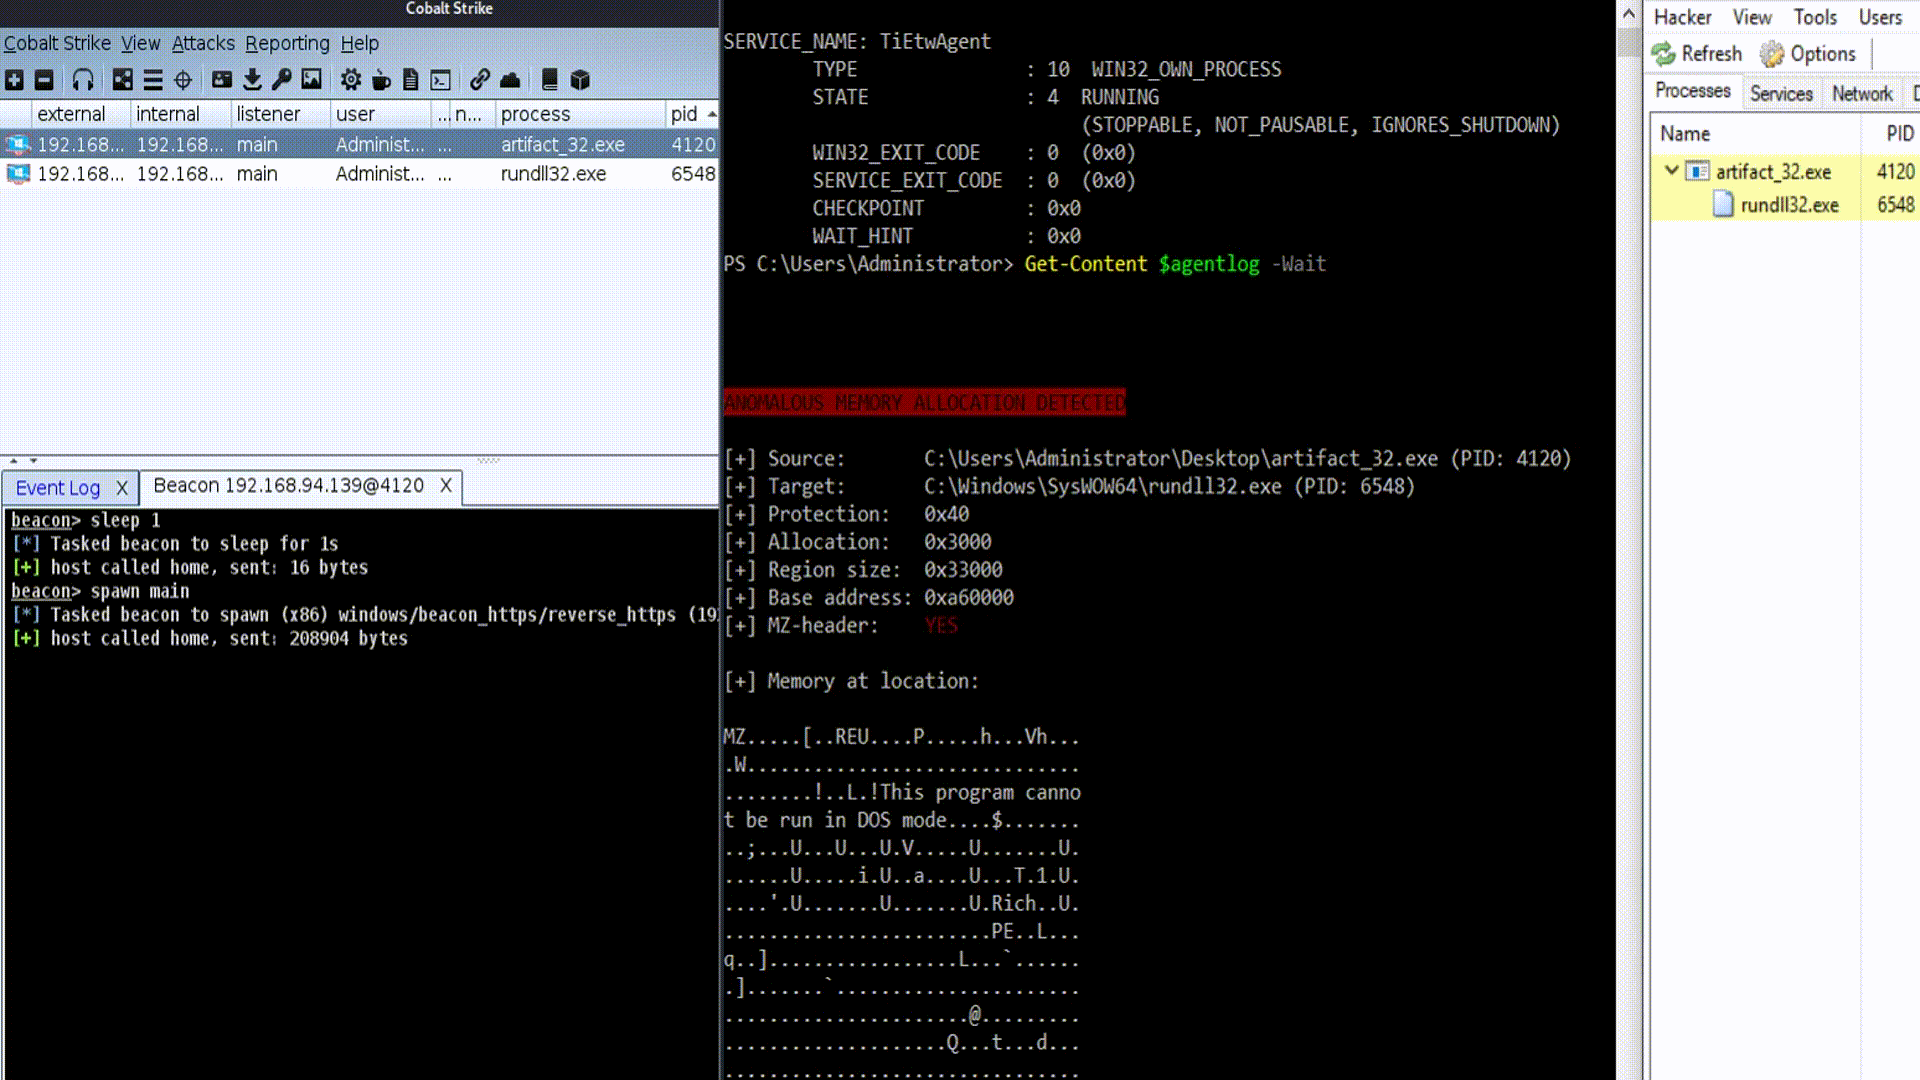 xuanxuan0/tietwagent
PoC memory injection detection agent based on ETW, for offensive and defensive research purposes
 joaoaugustom/adobe_coldfusion_rce_unauthenticated
This exploit is based on CVE-2023-26360 (https://nvd.nist.gov/vuln/detail/CVE-2023-26360) and was built on top of the Metasploit module and the…
 0xballpoint/load
Lord Of Active Directory - automatic vulnerable active directory on AWS
 h4xl0r/winrar_ace_exploit_cve-2018-20250
This program is an script developed in Python which exploit the ACE vulnerability on WinRar - Vulnerability CVE-2018-20250
 chuzoux/cve-2025-32433-exploit-edited
Based on the original version:https://github.com/vulhub/vulhub/blob/master/erlang/CVE-2025-32433/exploit.py Replace Unicode checkmark with ASCII…
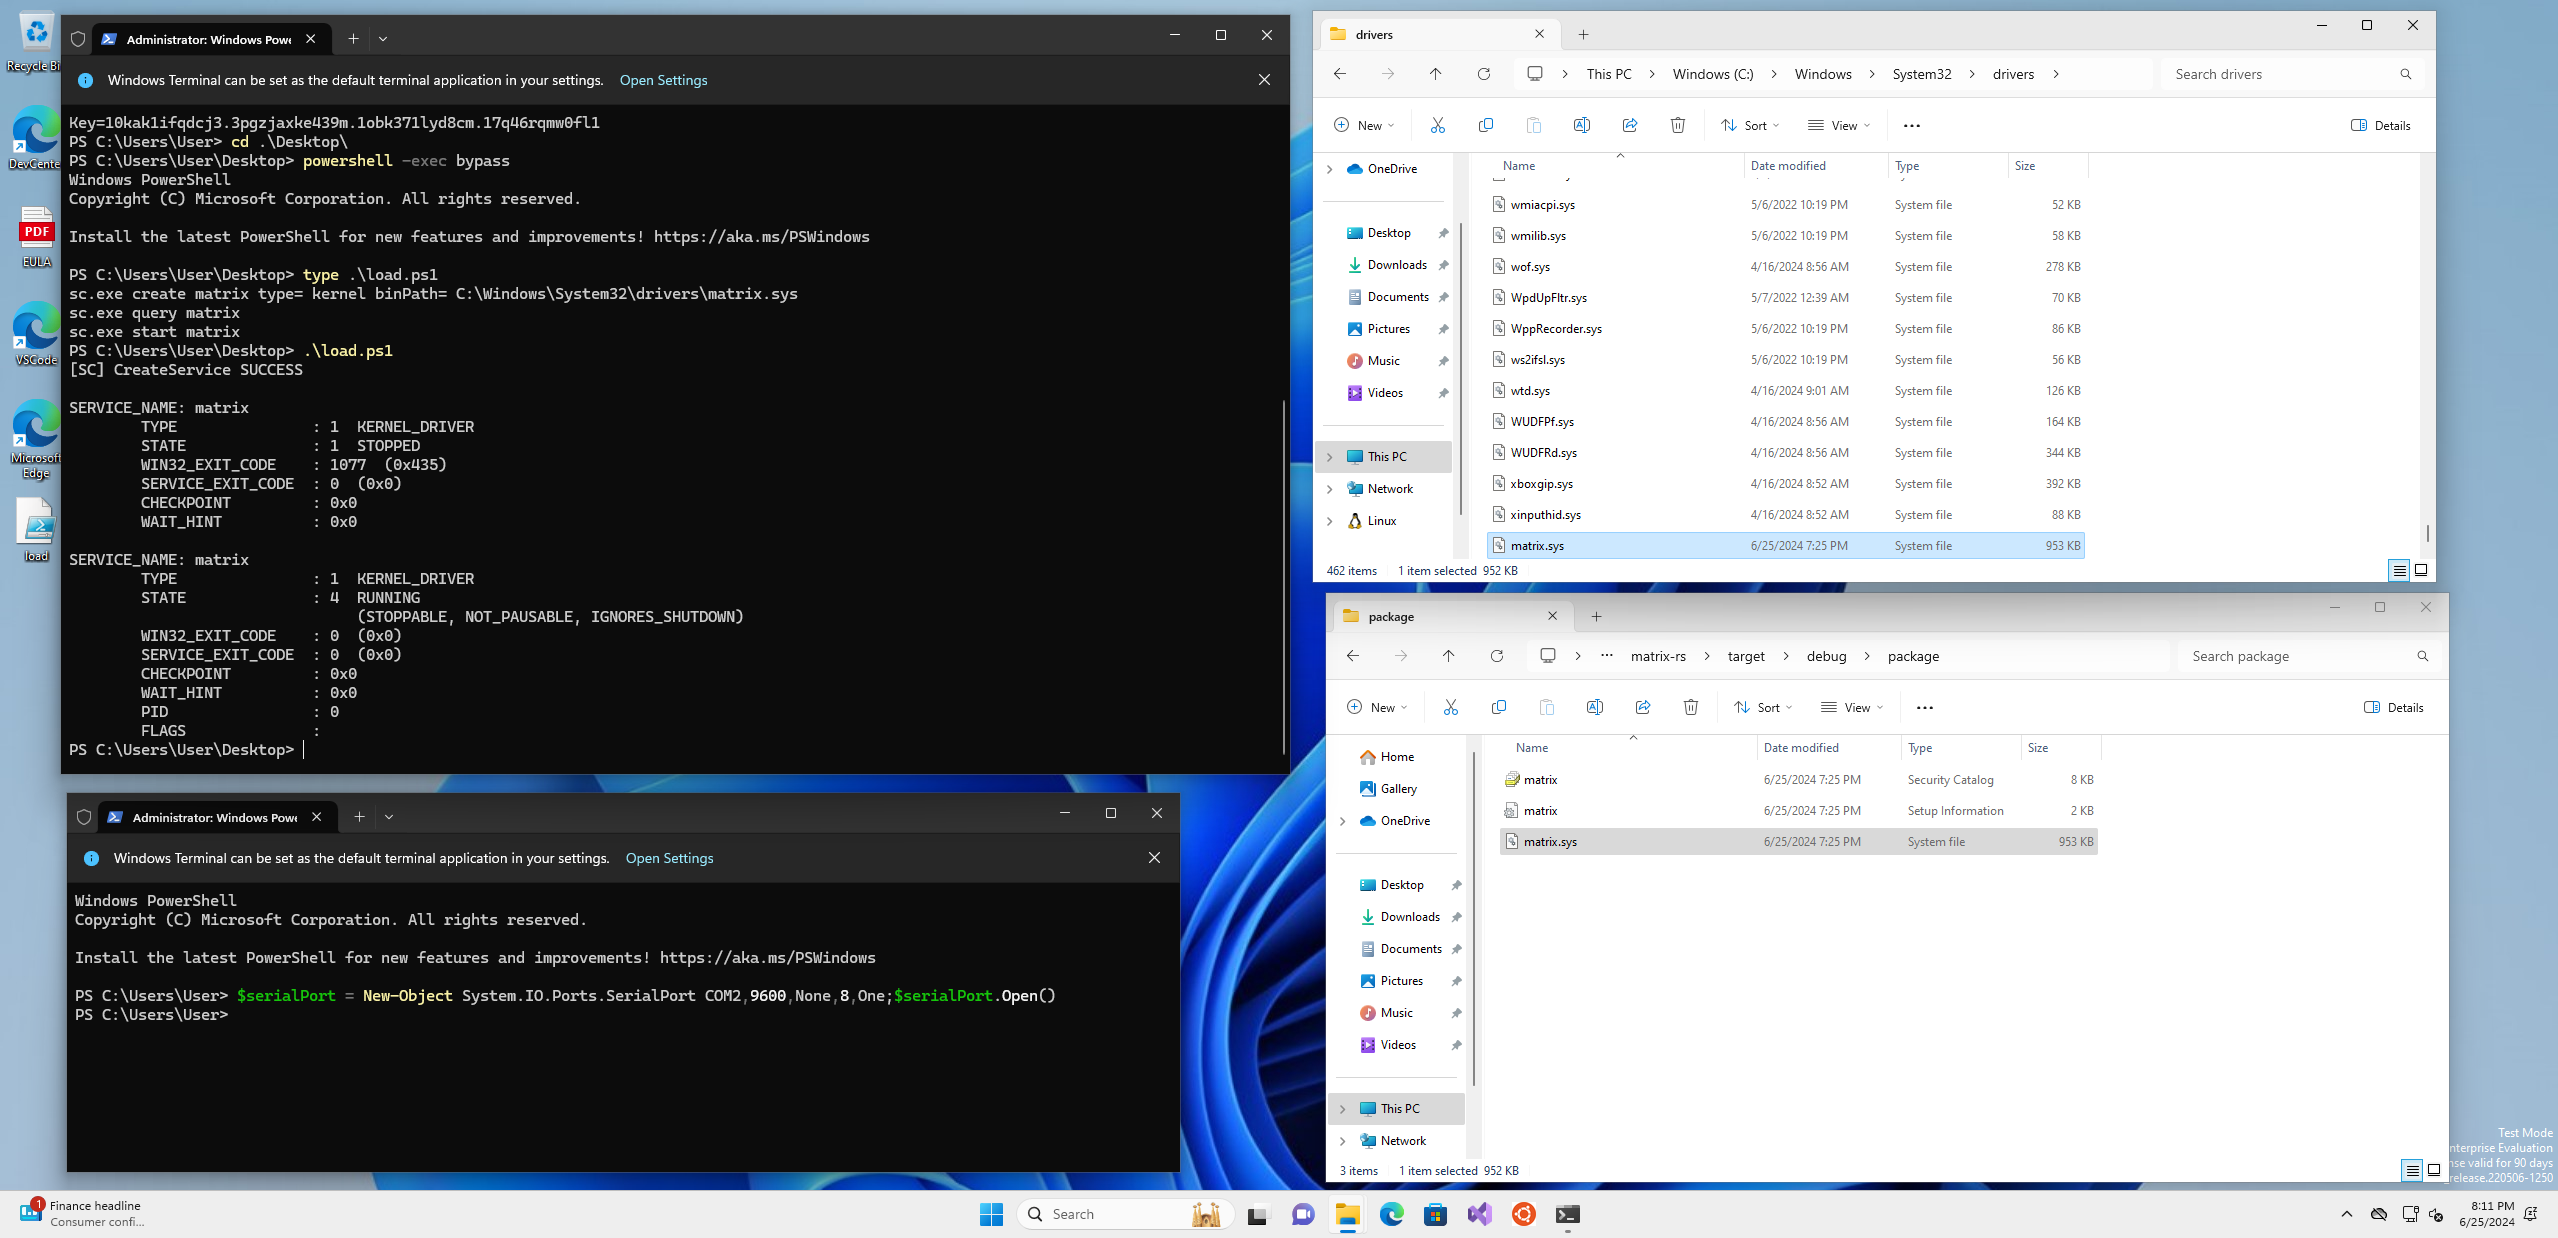 memn0ps/matrix-rs
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)
 alperenugurlu/cmd_bypass_assessment
PowerShell script that automatically tests CMD bypass methods on Windows, evaluates results, calculates a security score, and provides hardening…
 sh4hin/androl4b
A Virtual Machine For Assessing Android applications, Reverse Engineering and Malware Analysis
 cealbez/cve-2025-24813-poc
This is a PoC for the CVE-2025-24813 and tested in different environments.
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
 rohitmalik7/cve-2024-38063-detection-mitigation-system
End-to-end cybersecurity project demonstrating detection and mitigation of CVE-2024-38063 using IDS, host-based monitoring, and virtual lab attack…