
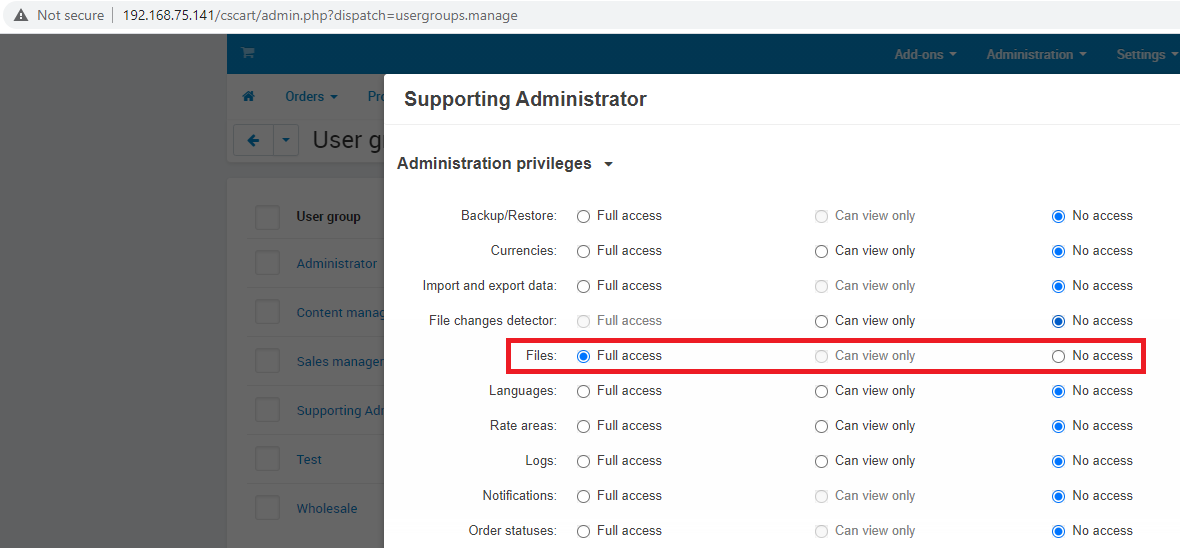
CVE-2021-26121
 sourceincite/cve-2021-26121
Proof-of-concept exploit for CVE-2021-26121: Server-Side Template Injection in CS-Cart <=4.12.x allowing shop admin to achieve remote code execution…
code-analysiseducationexploitation+3
12
sourceincite/cve-2021-26121Proof-of-concept exploit for CVE-2021-26121: Server-Side Template Injection in CS-Cart <=4.12.x allowing shop admin to achieve remote code execution…
 24520597-blip/cve-2026-999999
A critical Server-Side Template Injection (SSTI) vulnerability exists in the X-Trading Portal v1.4.2 dashboard metadata rendering engine. The flaw…