
CVE-2025-49844
 angelusrivera/cve-2025-49844
Scanner and educational guide for CVE-2025-49844 (RediShell), a Redis Lua scripting use-after-free vulnerability. Checks Redis servers for exposure,…
database-securityeducationexploitation+4
1
angelusrivera/cve-2025-49844Scanner and educational guide for CVE-2025-49844 (RediShell), a Redis Lua scripting use-after-free vulnerability. Checks Redis servers for exposure,…
 b-abderrahmane/cve-2021-44228-playground
Docker-based lab to validate CVE-2021-44228 (Log4Shell) in Java apps, test mitigations, and simulate RCE via LDAP and HTTP payloads.
 vedantrana73/cve-2019-9053-py3
Unauthenticated time-based blind SQL injection exploit for CMS Made Simple ≤ 2.2.9 (CVE-2019-9053), ported to Python 3.
 la3b0z/cve-2025-24813-poc
CVE-2025-24813-POC JSP Web Shell Uploader
 drackyjr/cve-2020-15778-scp-command-injection-check
This script is a safe and simple tool that helps system users, students, and administrators check if their SCP (Secure Copy) client is vulnerable to…
 maradonam18/-cve-2025-59528-poc
A simple python script to exploit CVE-2025-59528, this an Authenticated RCE vulnerability in Flowise application, a popular AI tool. That is also…
 blipzip/cve-2022-31692
A project demonstrating an app that is vulnerable to Spring Security authorization bypass CVE-2022-31692
 h8su/wordpress-cve-2024-10924-exploit
A Proof-of-Concept (PoC) exploit for CVE-2024-10924, a vulnerability in the Really Simple SSL WordPress plugin that allows bypassing two-factor…
 nxploited/cve-2024-10924-exploit
Really Simple Security (Free, Pro, and Pro Multisite) 9.0.0 - 9.1.1.1 - Authentication Bypass
 paulameg/simplectf-thm-walkthrough
First CTF successfully completed! This repo documents my walkthrough of TryHackMe's Simple CTF. It covers network reconnaissance (Nmap), web…
 mrcl0wnlab/simplesapachepathtraversal
Tool check: CVE-2021-41773, CVE-2021-42013, CVE-2020-17519
 hamm0nz/cve-2020-18326
Proof-of-concept exploit for CVE-2020-18326 demonstrating Cross-Site Request Forgery (CSRF) in Subrion CMS 4.2.1 to create an unauthorized…
 pratikshad19/cve-2020-15053
Artica Proxy before 4.30.000000 Community Edition allows Reflected Cross Site Scripting.
 hamm0nz/cve-2020-18325
Proof-of-concept exploit for reflected XSS vulnerabilities in Subrion CMS v4.2.1 configuration panel, demonstrating JavaScript injection via POST…
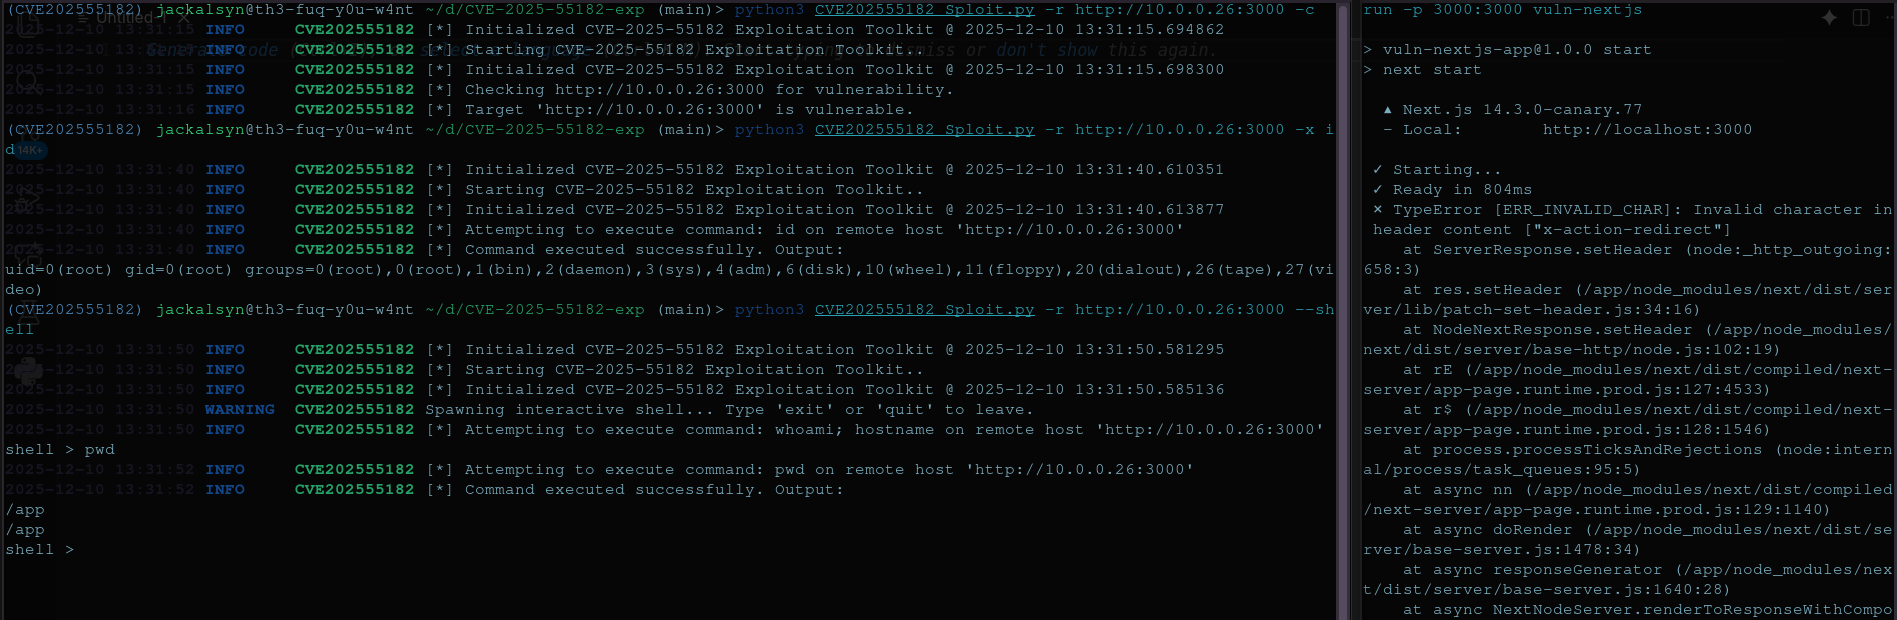 j4ck3lsyn-gen2/cve-2025-55182
A simple toolkit to validate, exploit & gain an interactive shell via the react2Shell Next.js RCE.
 cberman/cve-2023-2822-demo
Simple flask application to implement an intentionally vulnerable web app to demo CVE-2023-2822.
 behindsecurity/htb-wifinetictwo-exploit
A simple python script to exploit CVE-2021-31630 on HTB WifineticTwo CTF