

coraza
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
api-securityapi-security-testingdefensive-tools+7
4.0k
corazawaf/corazaGo-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 trusted-ai/aif360
A comprehensive set of fairness metrics for datasets and machine learning models, explanations for these metrics, and algorithms to mitigate bias in…
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
 duc-nt/cve-2020-6287-exploit
PoC for CVE-2020-6287 The PoC in python for add user only, no administrator permission set. Inspired by @zeroSteiner from metasploit. Original…
 amnestytech/inside-pegasus
A curated set of NSO Group internal documents, product materials and sworn testimony that entered the public record in WhatsApp Inc. and Meta…
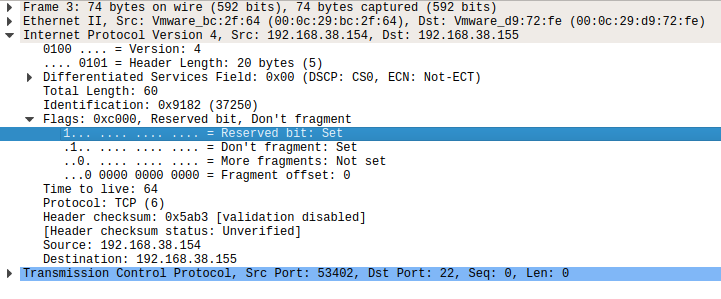 flamingspork/iptable_evil
Kernel-level iptables backdoor that accepts all packets with the RFC 3514 evil bit set, bypassing firewall rules. Includes in-tree and out-of-tree…
 xalicex/kernel-debug-lab-for-virtual-box
How to set up 2 VirtualBox VM to debug kernel driver using windbg
 cyb3rmik3/prompt-injection-email-samples
Open .eml test set for evaluating how email security controls and AI mailbox assistants handle indirect prompt injection across disclosure,…
 hullabrian/eventhorizon
Tool that gathers a customizable set of ETW telemetry and generates user-defined detections
 roddhjav/apparmor.d
Comprehensive set of over 1500 AppArmor profiles to confine Linux system processes, desktops, and services, with support for multiple distributions…
 mkway/cve-2025-57833
We've set up an environment to test CVE-2025-57833. This environment was built using AI, so it's subject to ongoing modification.
 syn-4ck/wvctf
WVCTF or WebVulnCTF is a gamified web platform which promotes training in pentesting and web application development security in an entertaining way.…
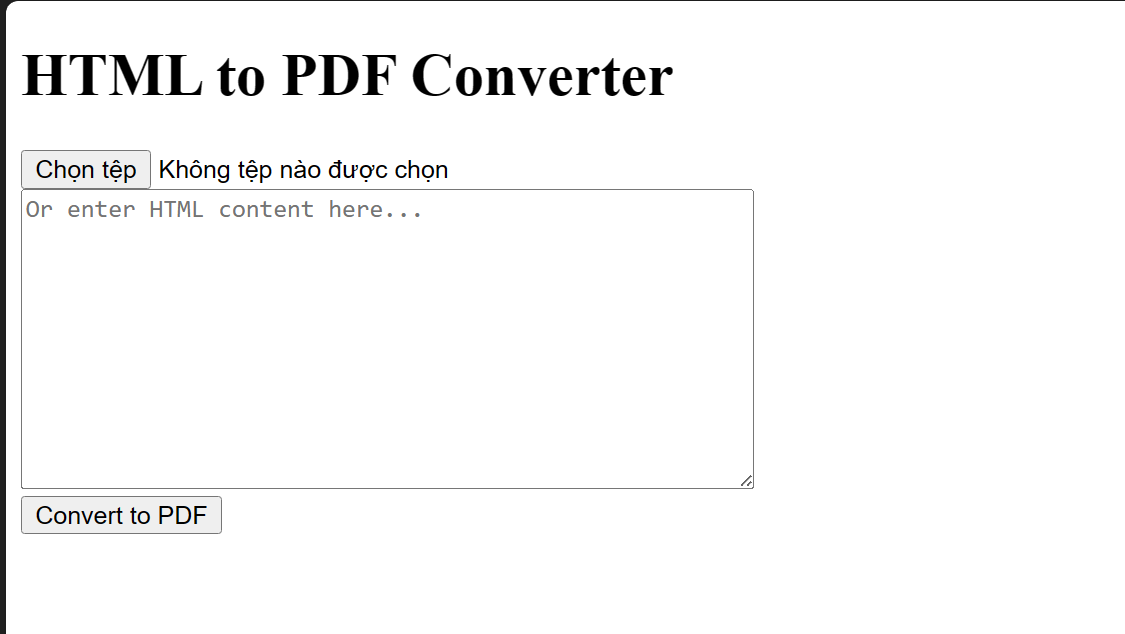 onion2203/lab_reportlab
This lab was set up to test CVE-2023-33733
 rishipatidar/cve-2023-30212-poc-docker-file
This repository provides a Docker container for simulating the CVE-2023-30212 vulnerability, allowing you to practice and understand its impact. It…
 brendonlee20042004-sys/weakrng-sweep
Weak-RNG stream-sweep research (CVE-2026-71851 class): PRNG schemes x seeds -> BIP39 -> victim set membership
 nxploited/cve-2025-2563
The User Registration & Membership WordPress plugin before 4.1.2 does not prevent users to set their account role when the Membership Addon is…
 abdullahmaqbool22/explosive-as-hell-mcs-qualifer-web-500
[First-Blood-XO] React Server Component endpoint vulnerable to CVE-2025-55182 (RCE) → enumerated SUID binaries → /usr/bin/perl had SUID set → used…
 alexs18/cve-2021-4773
Step-by-step tutorial demonstrating how to set up a vulnerable Apache 2.4.49 environment and exploit CVE-2021-41773 path traversal using Kali Linux…