
CVE-2023-28467
 ahmetaltuntas/cve-2023-28467
Proof-of-concept for a persistent XSS vulnerability in MyBB 1.8.33 User CP, allowing authenticated users to inject HTML via the email field, with…
ctfeducationpenetration-testing+2
4
ahmetaltuntas/cve-2023-28467Proof-of-concept for a persistent XSS vulnerability in MyBB 1.8.33 User CP, allowing authenticated users to inject HTML via the email field, with…
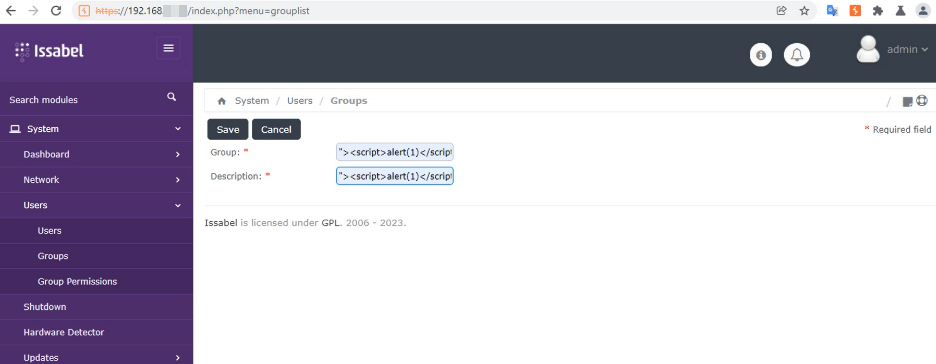 sahiloj/cve-2023-37191
A Stored Cross-Site Scripting (XSS) vulnerability exists in Issabel PBX version 4.0.0-6. This allows an authenticated attacker to inject arbitrary…
 0xdtc/below-logger-symlink-attack_cve-2025-27591
A Bash-based privilege escalation exploit targeting the `below` system performance monitoring tool. This refurbished exploit leverages a symlink…
 theethat-thamwasin/cve-2025-63307
An authenticated Stored Cross-site Scripting (XSS) vulnerability in laravel-file-manager v3.3.1 and below allows attackers with access to the file…
 mohnad-al-saif/gitea-git-hooks-rce-cve-2020-14144-
Gitea versions 1.1.0 → 1.12.5 allow authenticated users with "May create git hooks" permission to inject arbitrary shell commands into post-receive…
 thekin-ctrl/cve-2025-27591-below
Proof-of-concept exploit for CVE-2025-27591, a local privilege escalation in the 'below' system monitor. Demonstrates symlink attack on log file to…
 rrespxwnss/cve-2025-56771
During analysis of the ecodotempo.com.br website, a Stored Cross-Site Scripting (XSS) vulnerability was discovered. This vulnerability allows an…
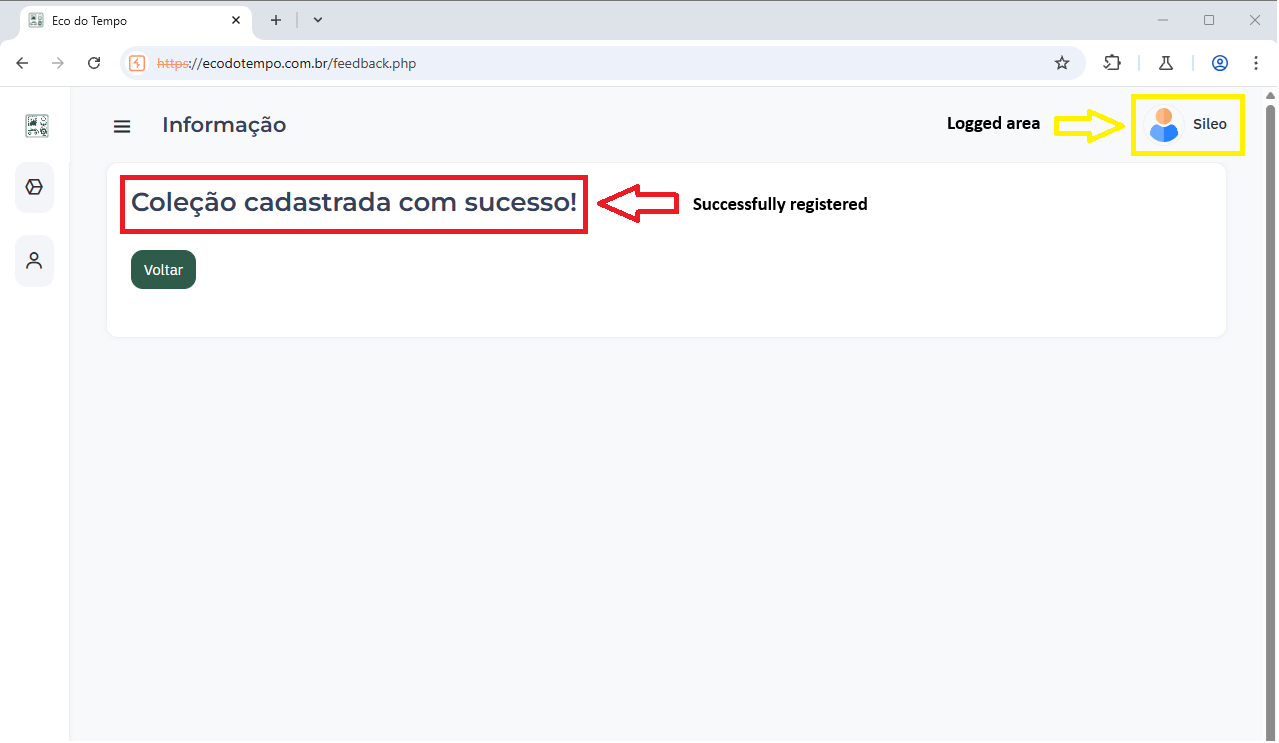 rrespxwnss/cve-2025-56772
During the analysis of the website ecodotempo.com.br, a Stored Cross-Site Scripting (XSS) vulnerability was discovered. This vulnerability allows an…
 shree-chandragiri/cve-2024-51032
A Cross-site Scripting (XSS) vulnerability in manage_recipient.php of Sourcecodester Toll Tax Management System 1.0 allows remote authenticated users…
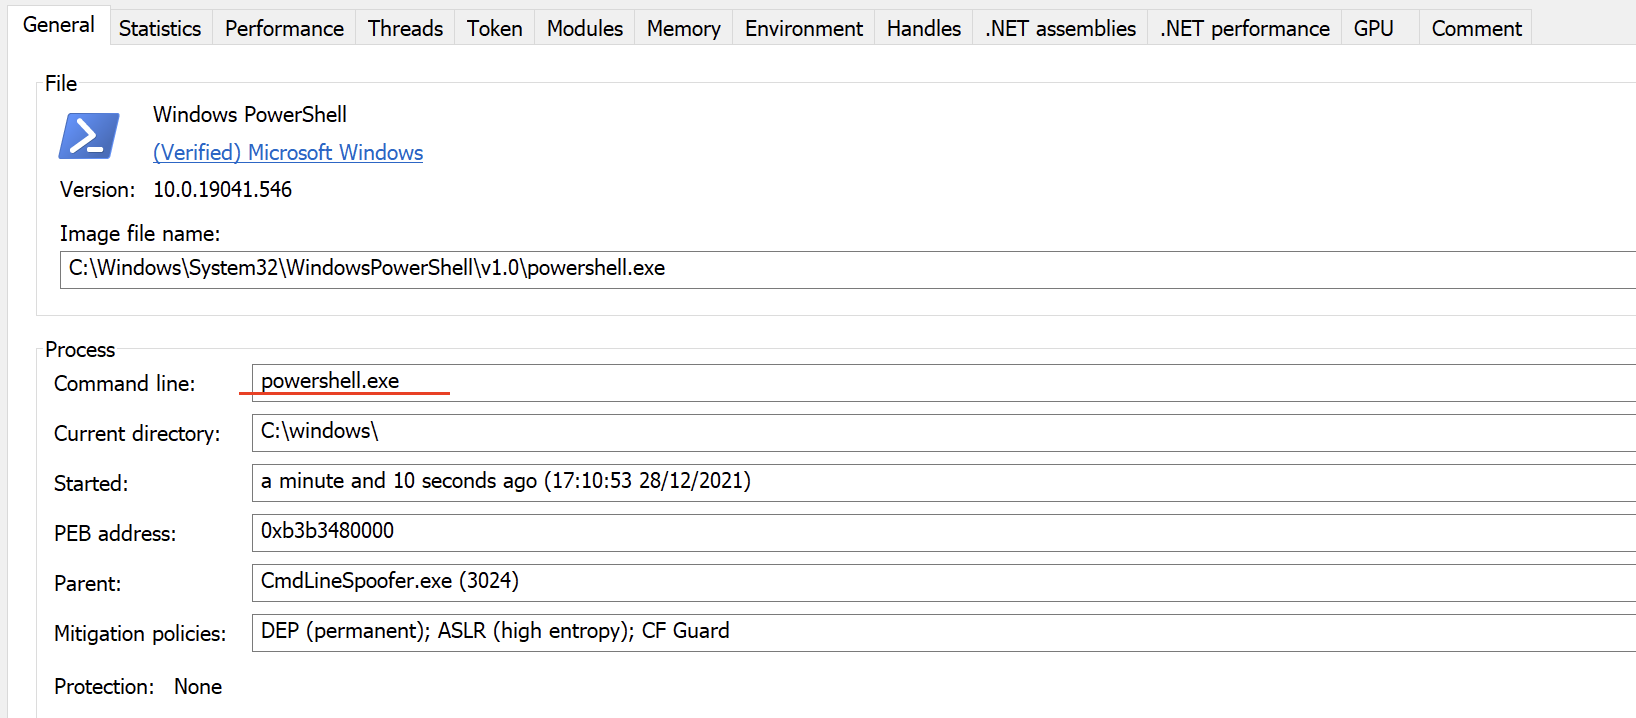 plackyhacker/cmdlinespoofer
How to spoof the command line when spawning a new process from C#.
 zeropathai/proftpd-cve-2026-42167-poc
POCs to demonstrate CVE-2026-42167 in ProFTPD
 hadrian3689/phpipam_1.4.4
Exploit script for CVE-2022-23046 SQL injection in phpIPAM 1.4.4. Allows authenticated admin users to extract database info, read files, and write to…
 joshuavanderpoll/cve-2025-66398
CVE-2025-66398 — Signal K Server ≤ 2.18.0 RCE PoC
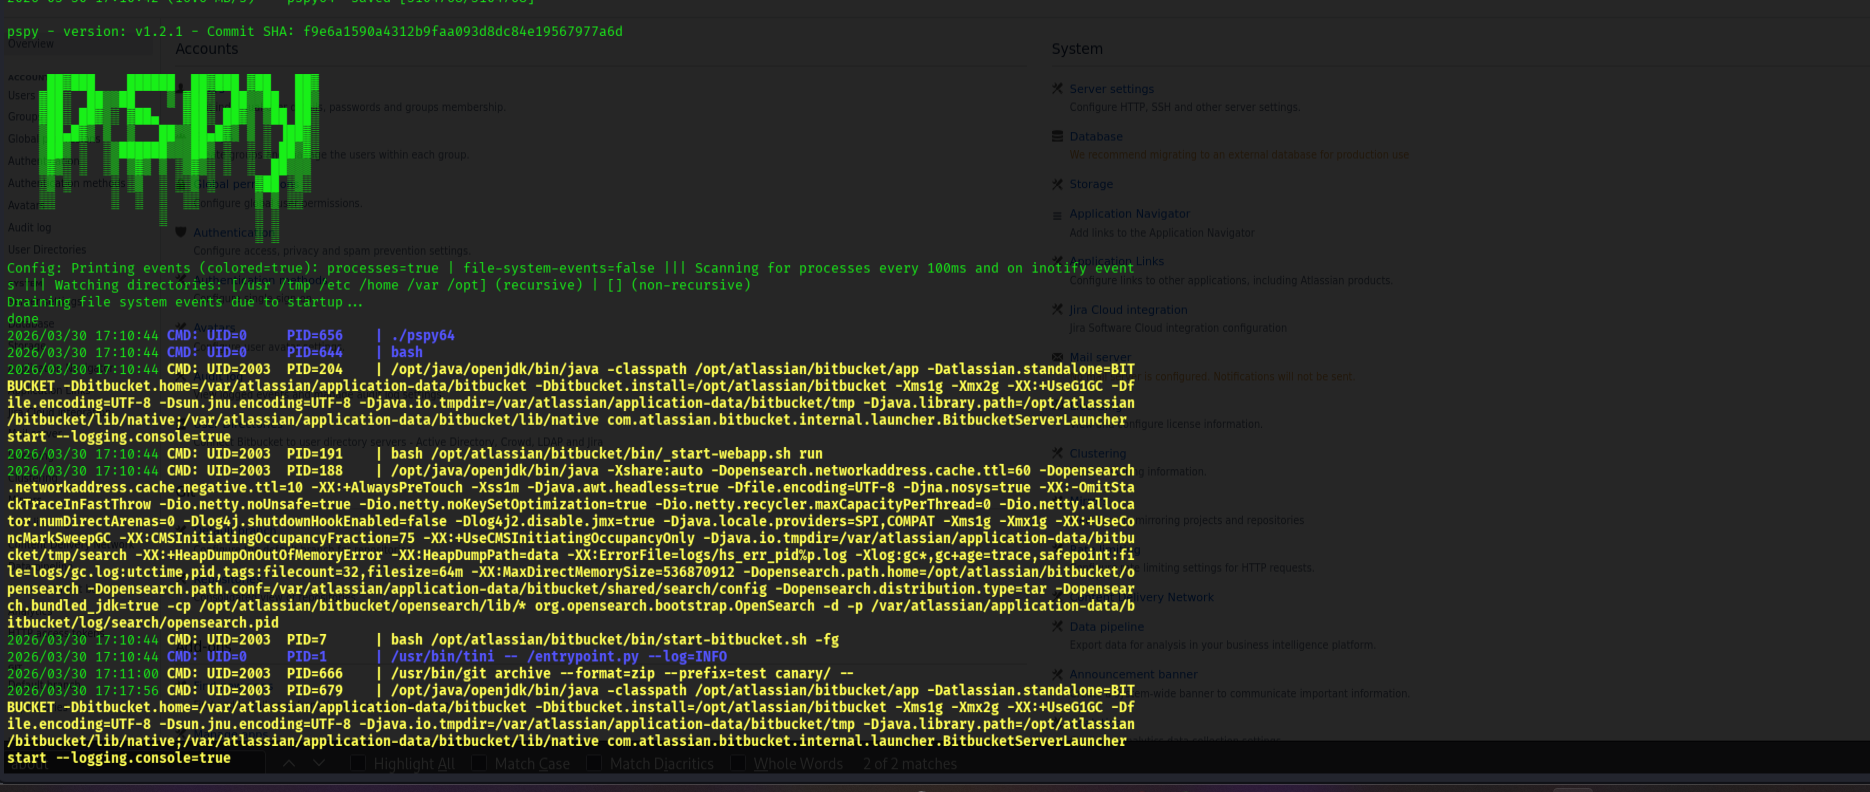 johangabrielson/bitbucket-test
Investigating CVE-2022-36804
 stigtsp/cve-2019-6690-python-gnupg-vulnerability
Proof-of-concept exploit for CVE-2019-6690, demonstrating input validation bypass in python-gnupg symmetric encryption via newline injection in…
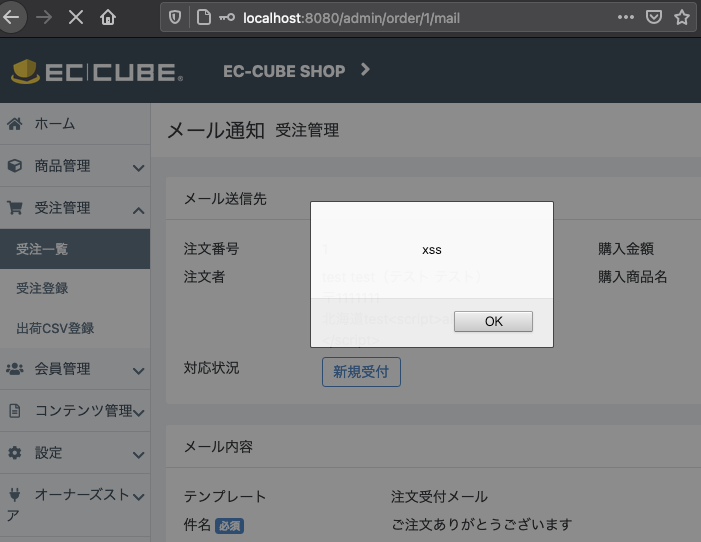 s-index/cve-2021-20717
CVE-2021-20717-EC-CUBE-XSS
 dharan10/cve-2025-67730
A public disclourse of CVE-2025-67730 in Frape lms By dharan ragunathan
 snailsploit/cve-2025-12163
CVE-2025-12163: Stored Cross-Site Scripting in Omnipress WordPress Plugin