
Firefox-CVE-2024-9680
 tdonaworth/firefox-cve-2024-9680
Educational analysis of CVE-2024-9680, a use-after-free vulnerability in Firefox's CSS Animation Timeline, with detailed exploit mechanics and…
binary-exploitationeducationexploitation+3
11
tdonaworth/firefox-cve-2024-9680Educational analysis of CVE-2024-9680, a use-after-free vulnerability in Firefox's CSS Animation Timeline, with detailed exploit mechanics and…
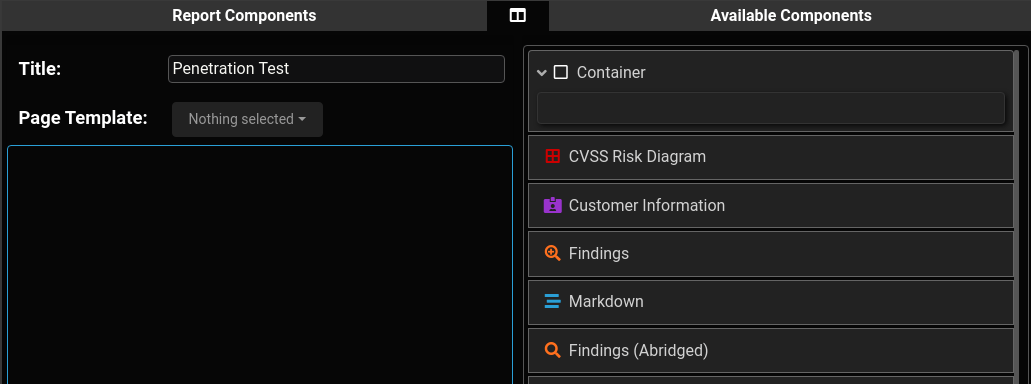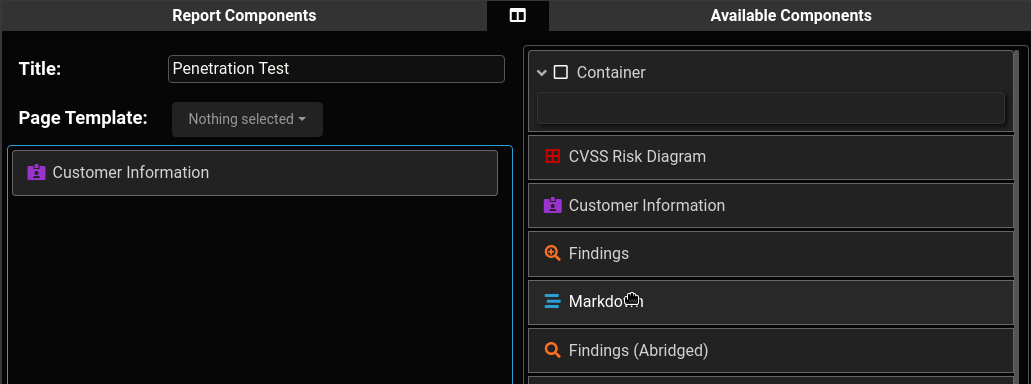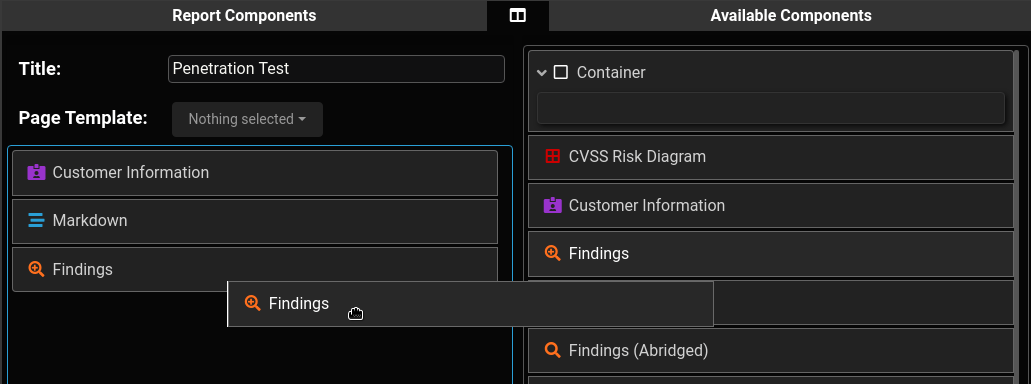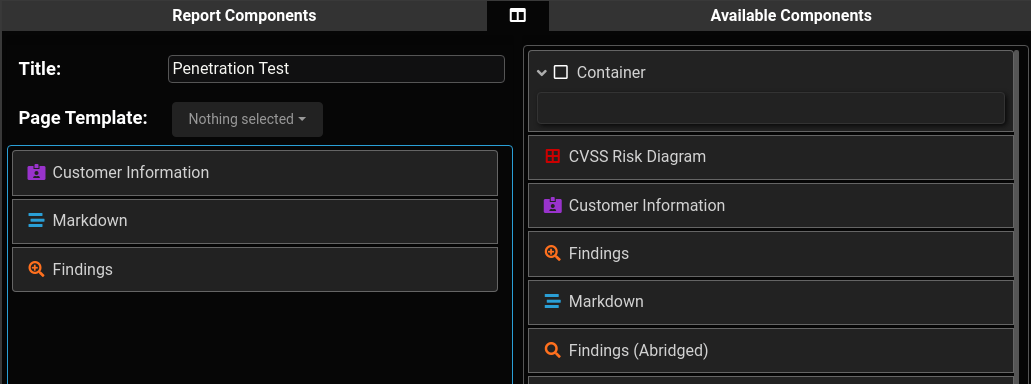 blacklanternsecurity/writehat
A pentest reporting tool written in Python. Free yourself from Microsoft Word.
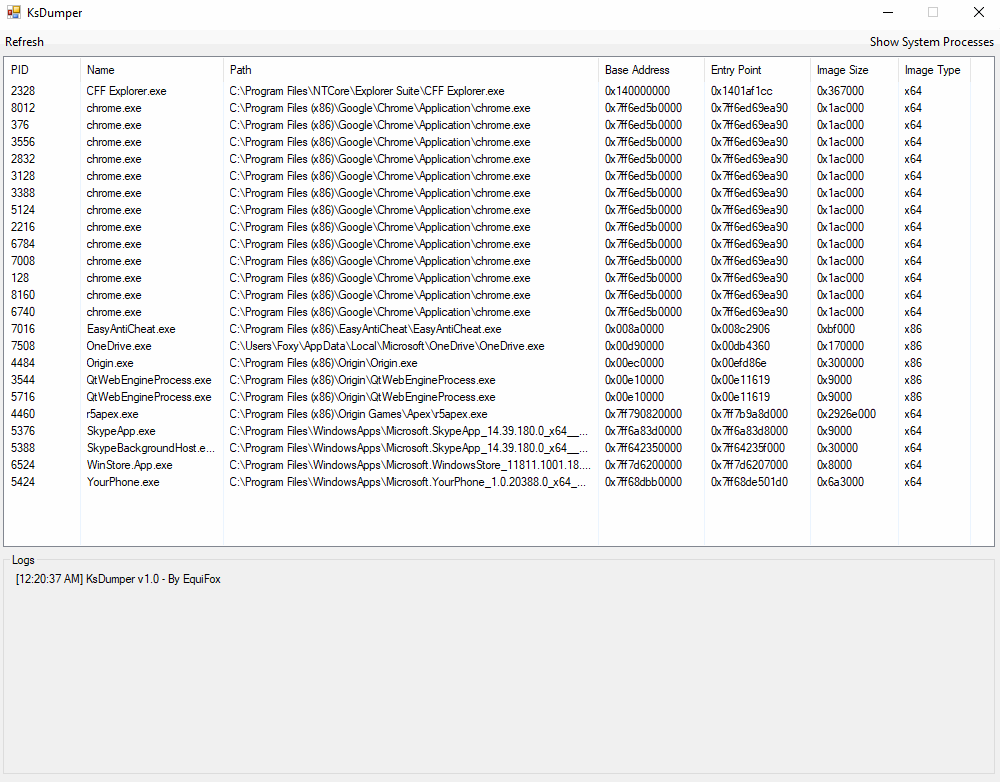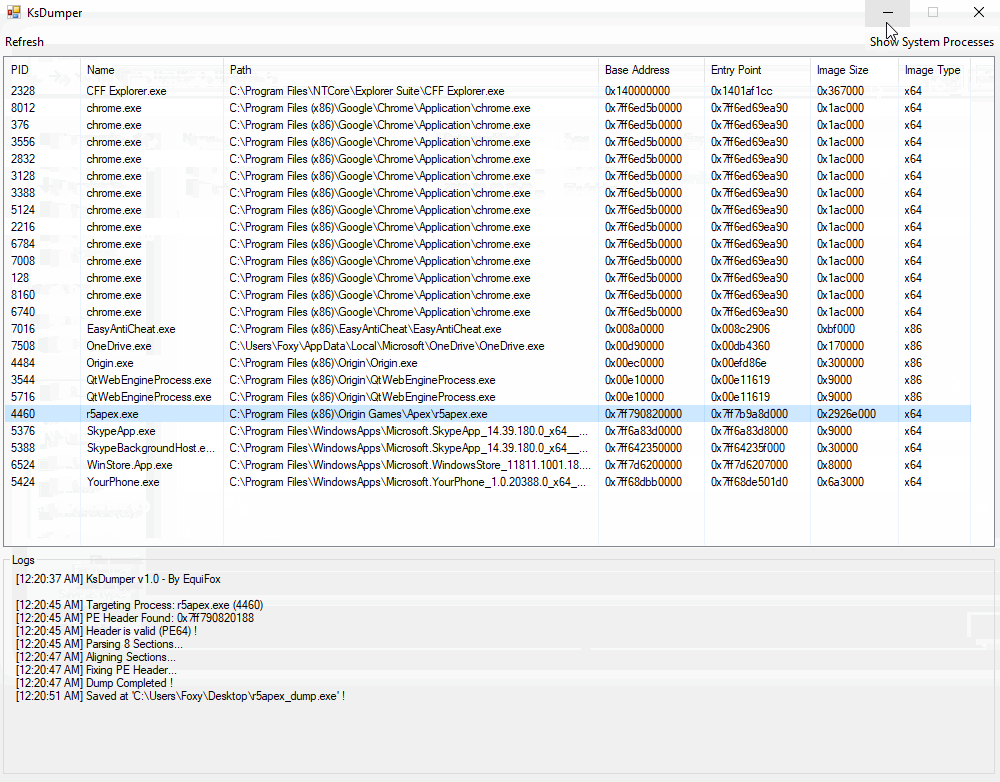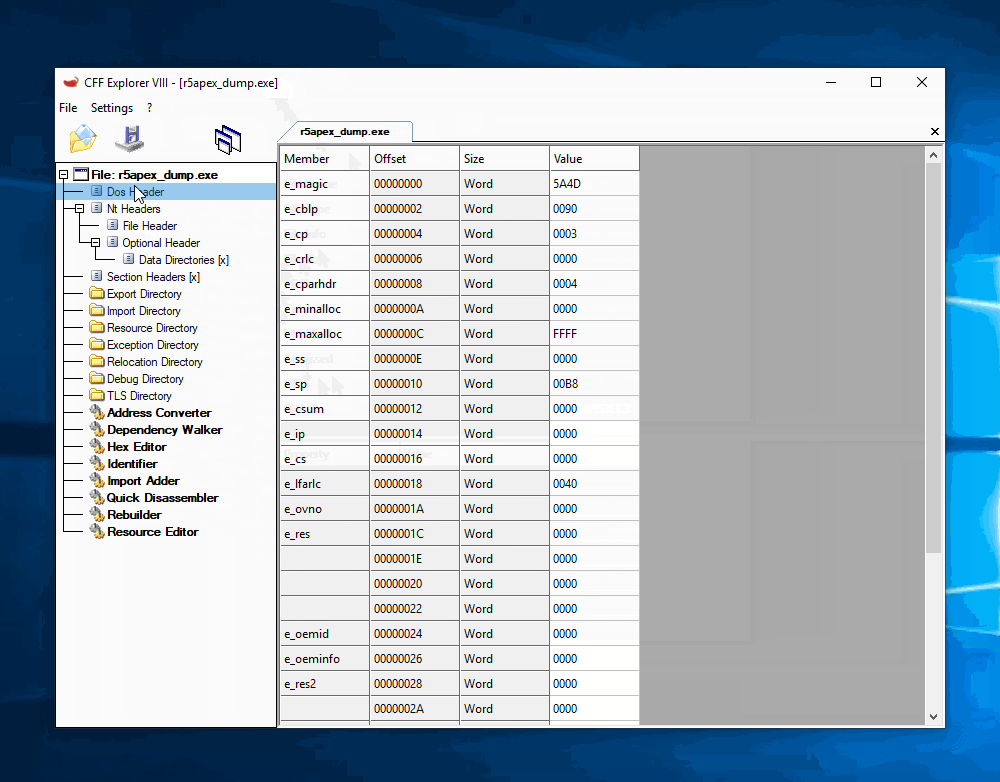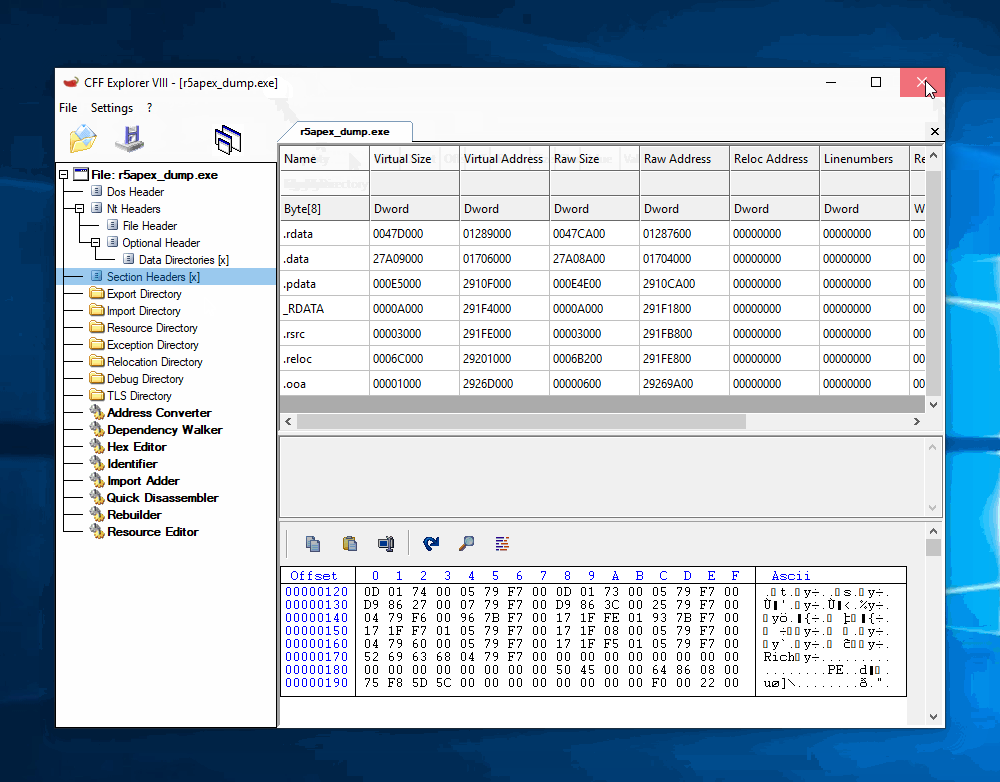 equifox/ksdumper
Dumping processes using the power of kernel space !
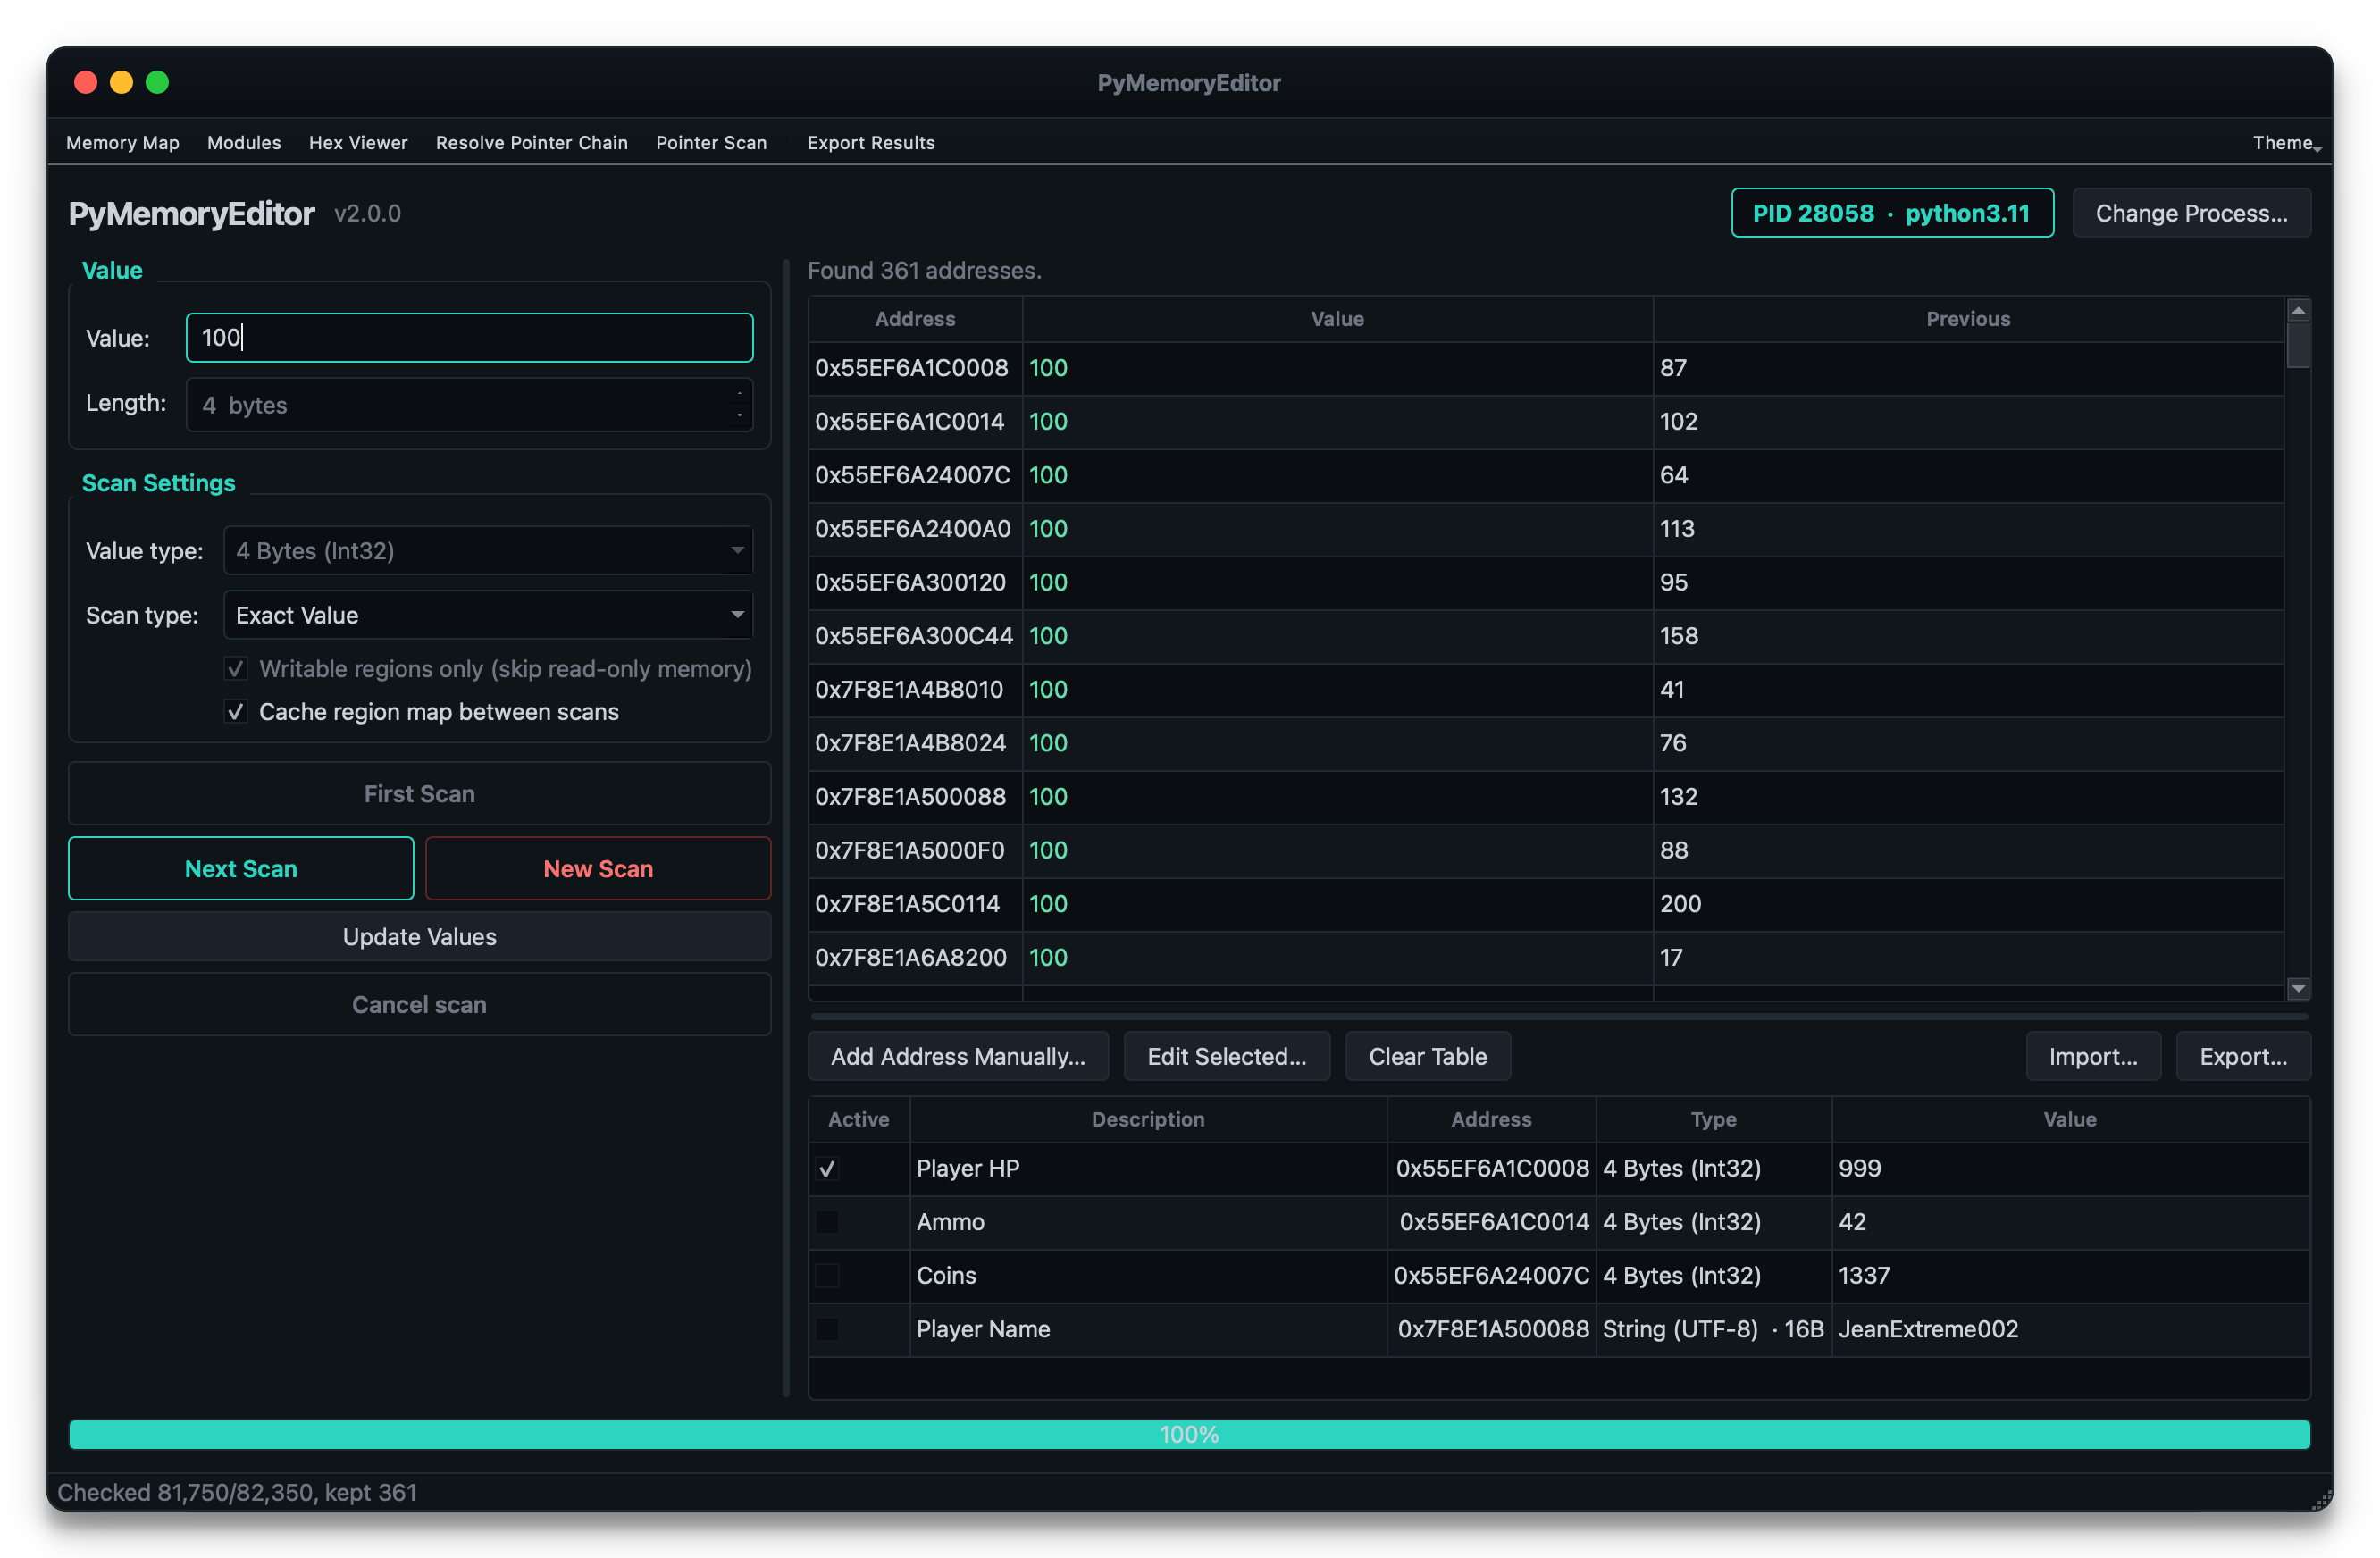 jeanextreme002/pymemoryeditor
A pure-Python library, app and MCP that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 dana-at-cp/backdoor-apk
backdoor-apk is a shell script that simplifies the process of adding a backdoor to any Android APK file. Users of this shell script should have…
 endgameinc/rta
Scripted framework for simulating over 50 MITRE ATT&CK techniques to test blue team detection capabilities. Includes Python scripts and a compiled…
 3xpl01tc0d3r/processinjection
This program is designed to demonstrate various process injection techniques
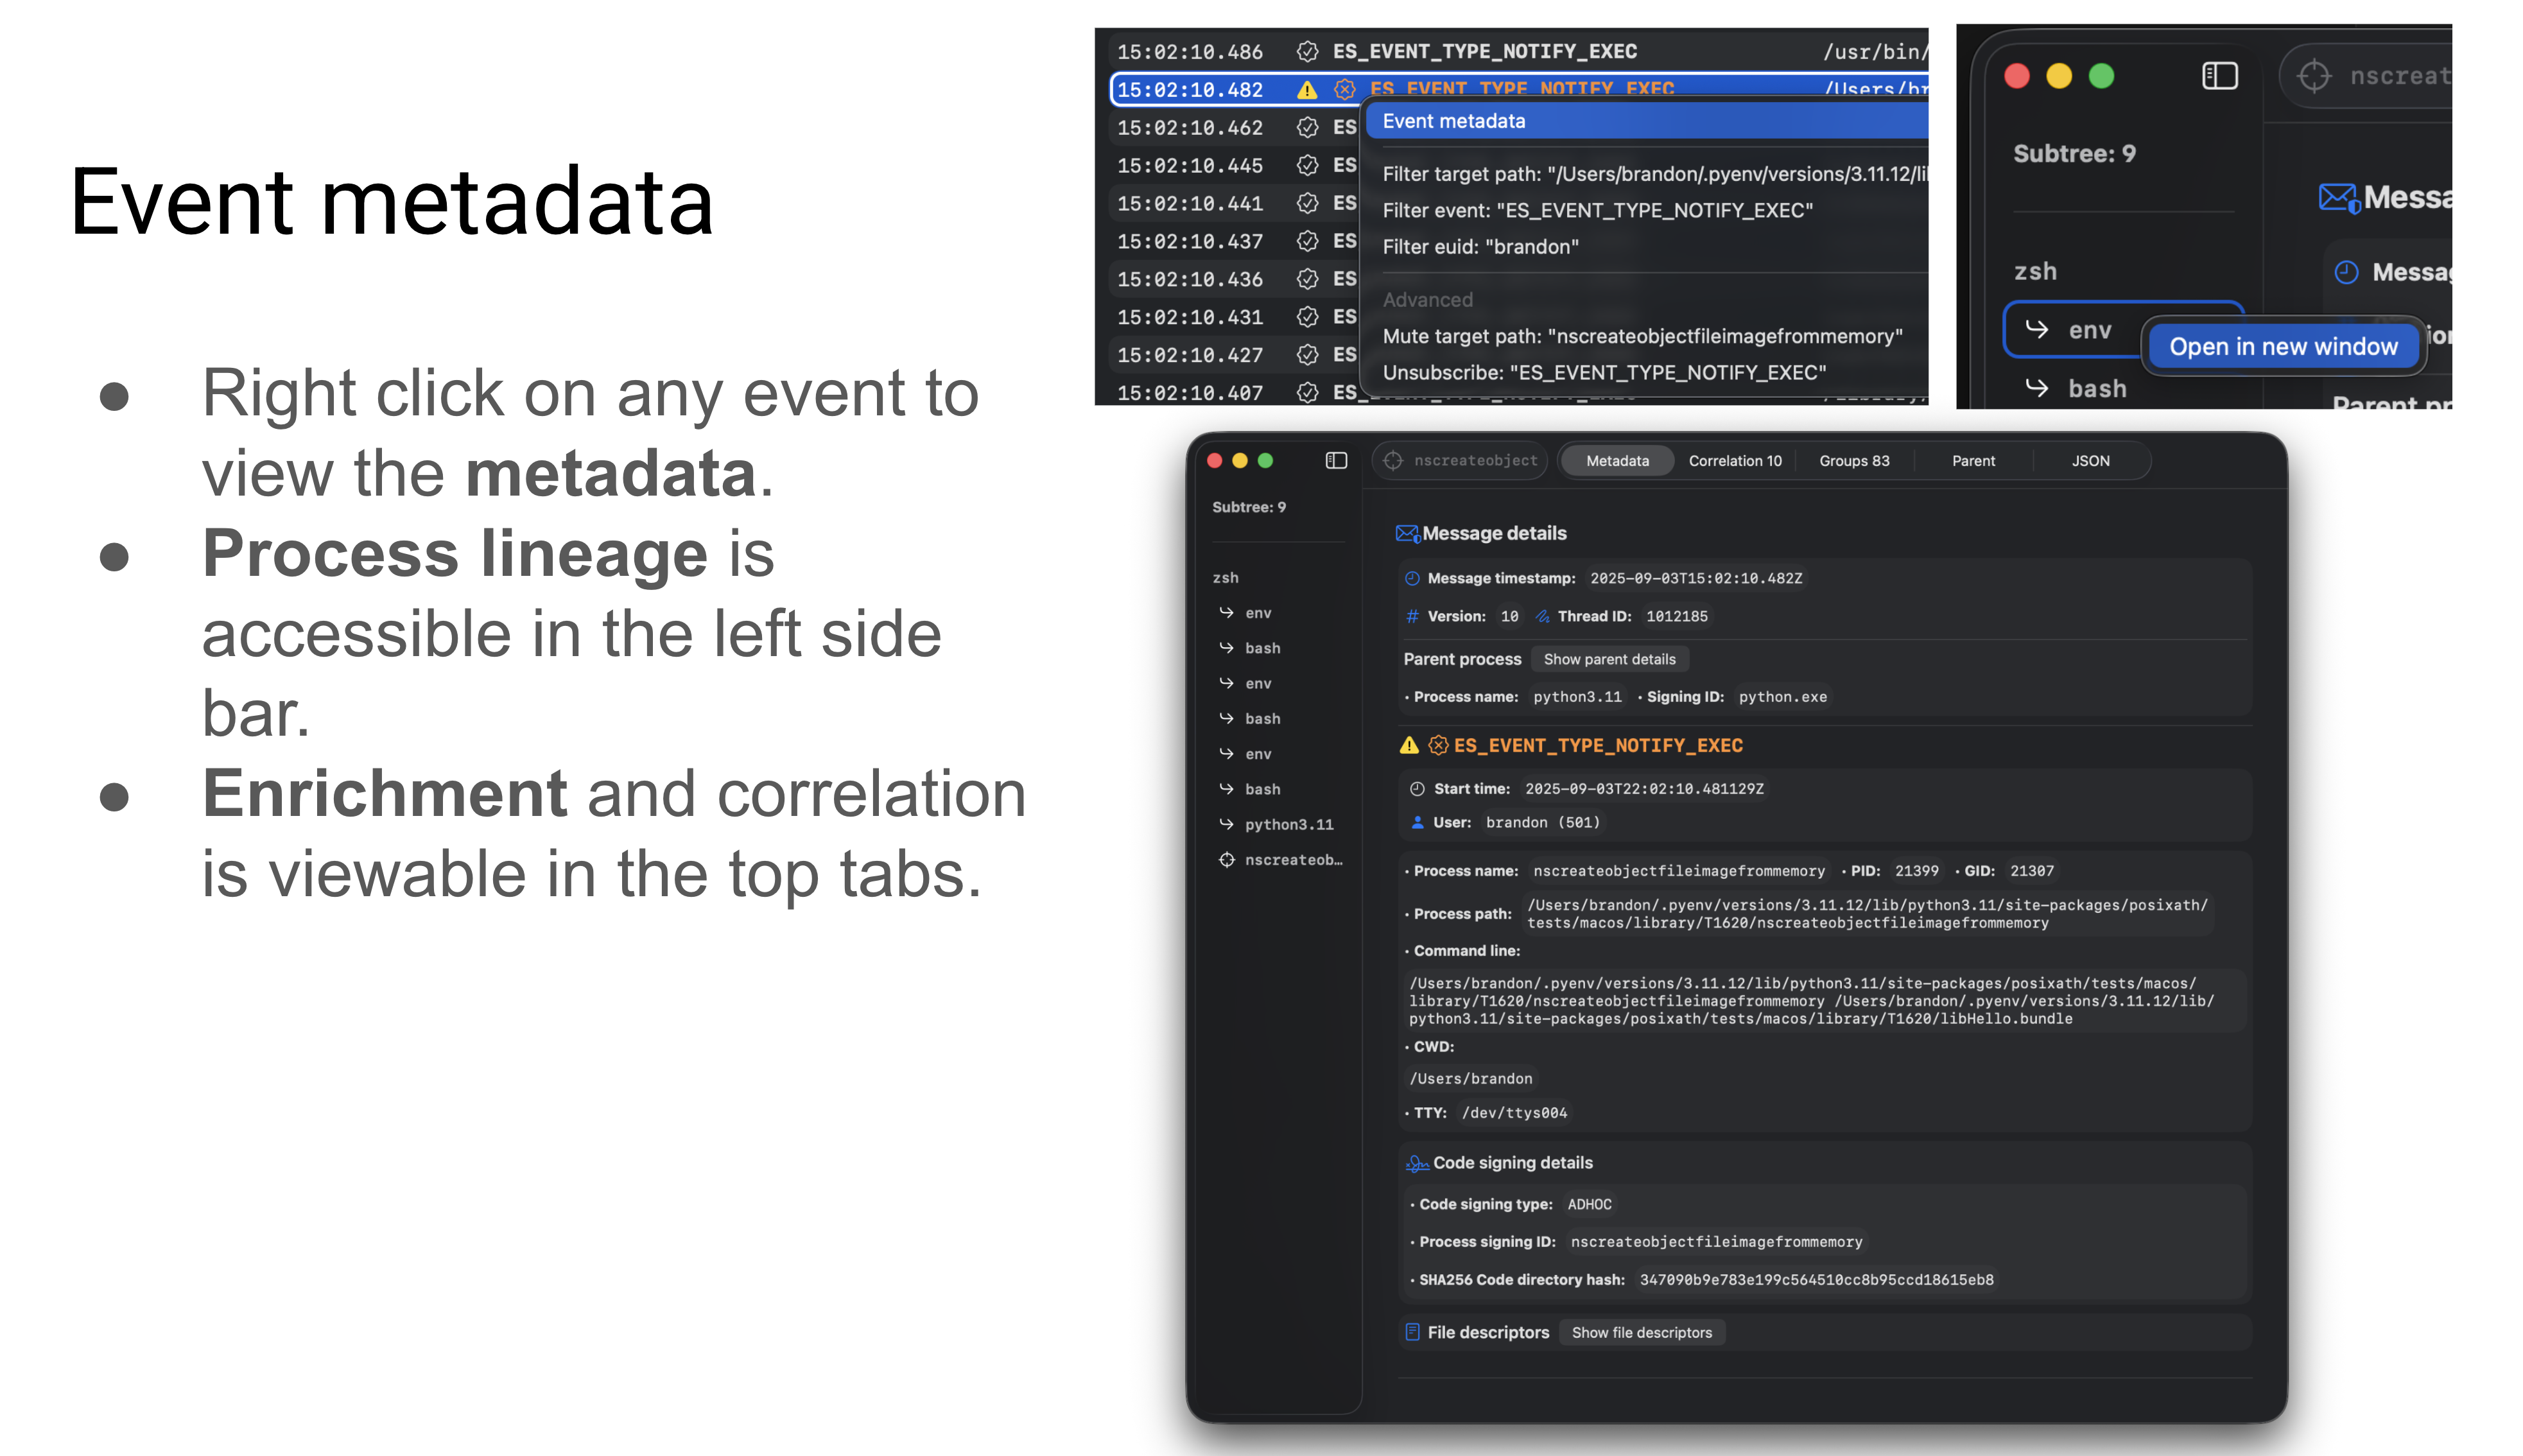 brandon7cc/mac-monitor
Advanced macOS system monitor leveraging Apple Endpoint Security to collect, enrich, and display process, file, memory, and XPC events for malware…
 xacone/bestedrofthemarket
Open-source Windows kernel-level EDR lab for understanding and testing detection methods against process injection, credential dumping, and other…
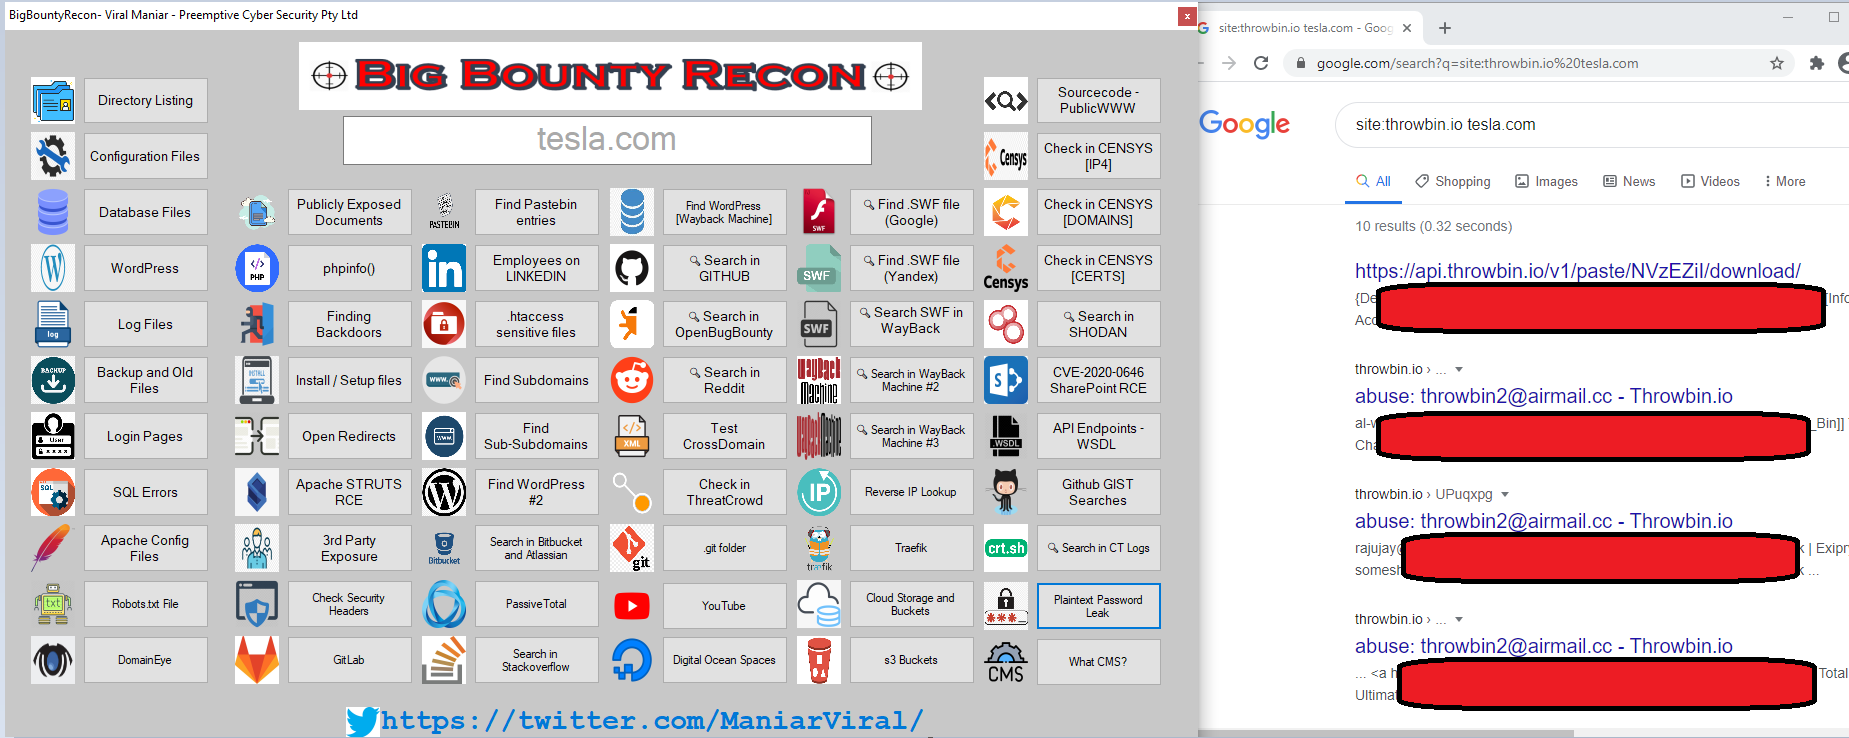 viralmaniar/bigbountyrecon
BigBountyRecon tool utilises 58 different techniques using various Google dorks and open source tools to expedite the process of initial…
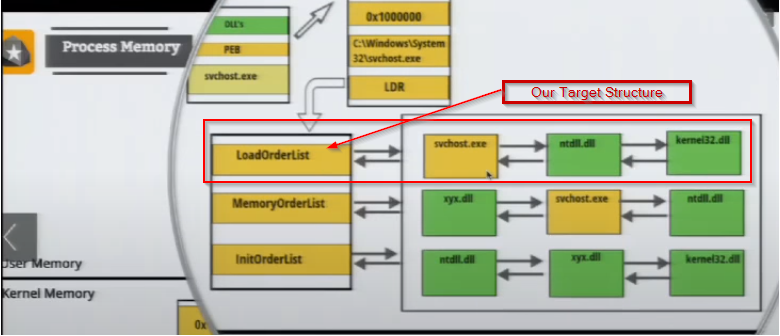 reveng007/darkwidow
Indirect Dynamic Syscall, SSN + Syscall address sorting via Modified TartarusGate approach + Remote Process Injection via APC Early Bird + Spawns a…
 cisagov/decider
A web application that assists network defenders, analysts, and researchers in the process of mapping adversary behaviors to the MITRE ATT&CK®…
 secrary/injectproc
InjectProc - Process Injection Techniques [This project is not maintained anymore]
 rajanagori/nightingale
Nightingale Docker for Pentesters is a comprehensive Dockerized environment tailored for penetration testing and vulnerability assessment. It comes…
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
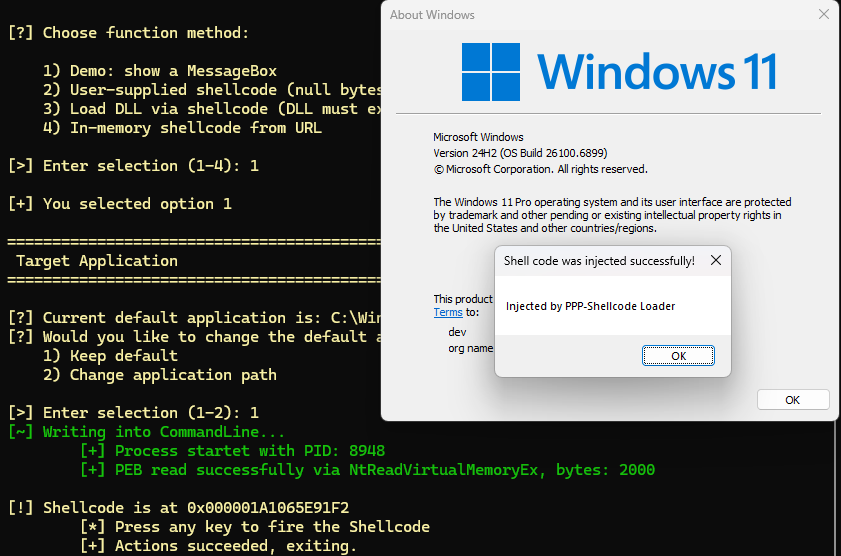 orange-cyberdefense/p3-loader
P³-Shellcode Loader is a loader that implements a code injection technique which leverages the Process Parameters structure as an execution and…
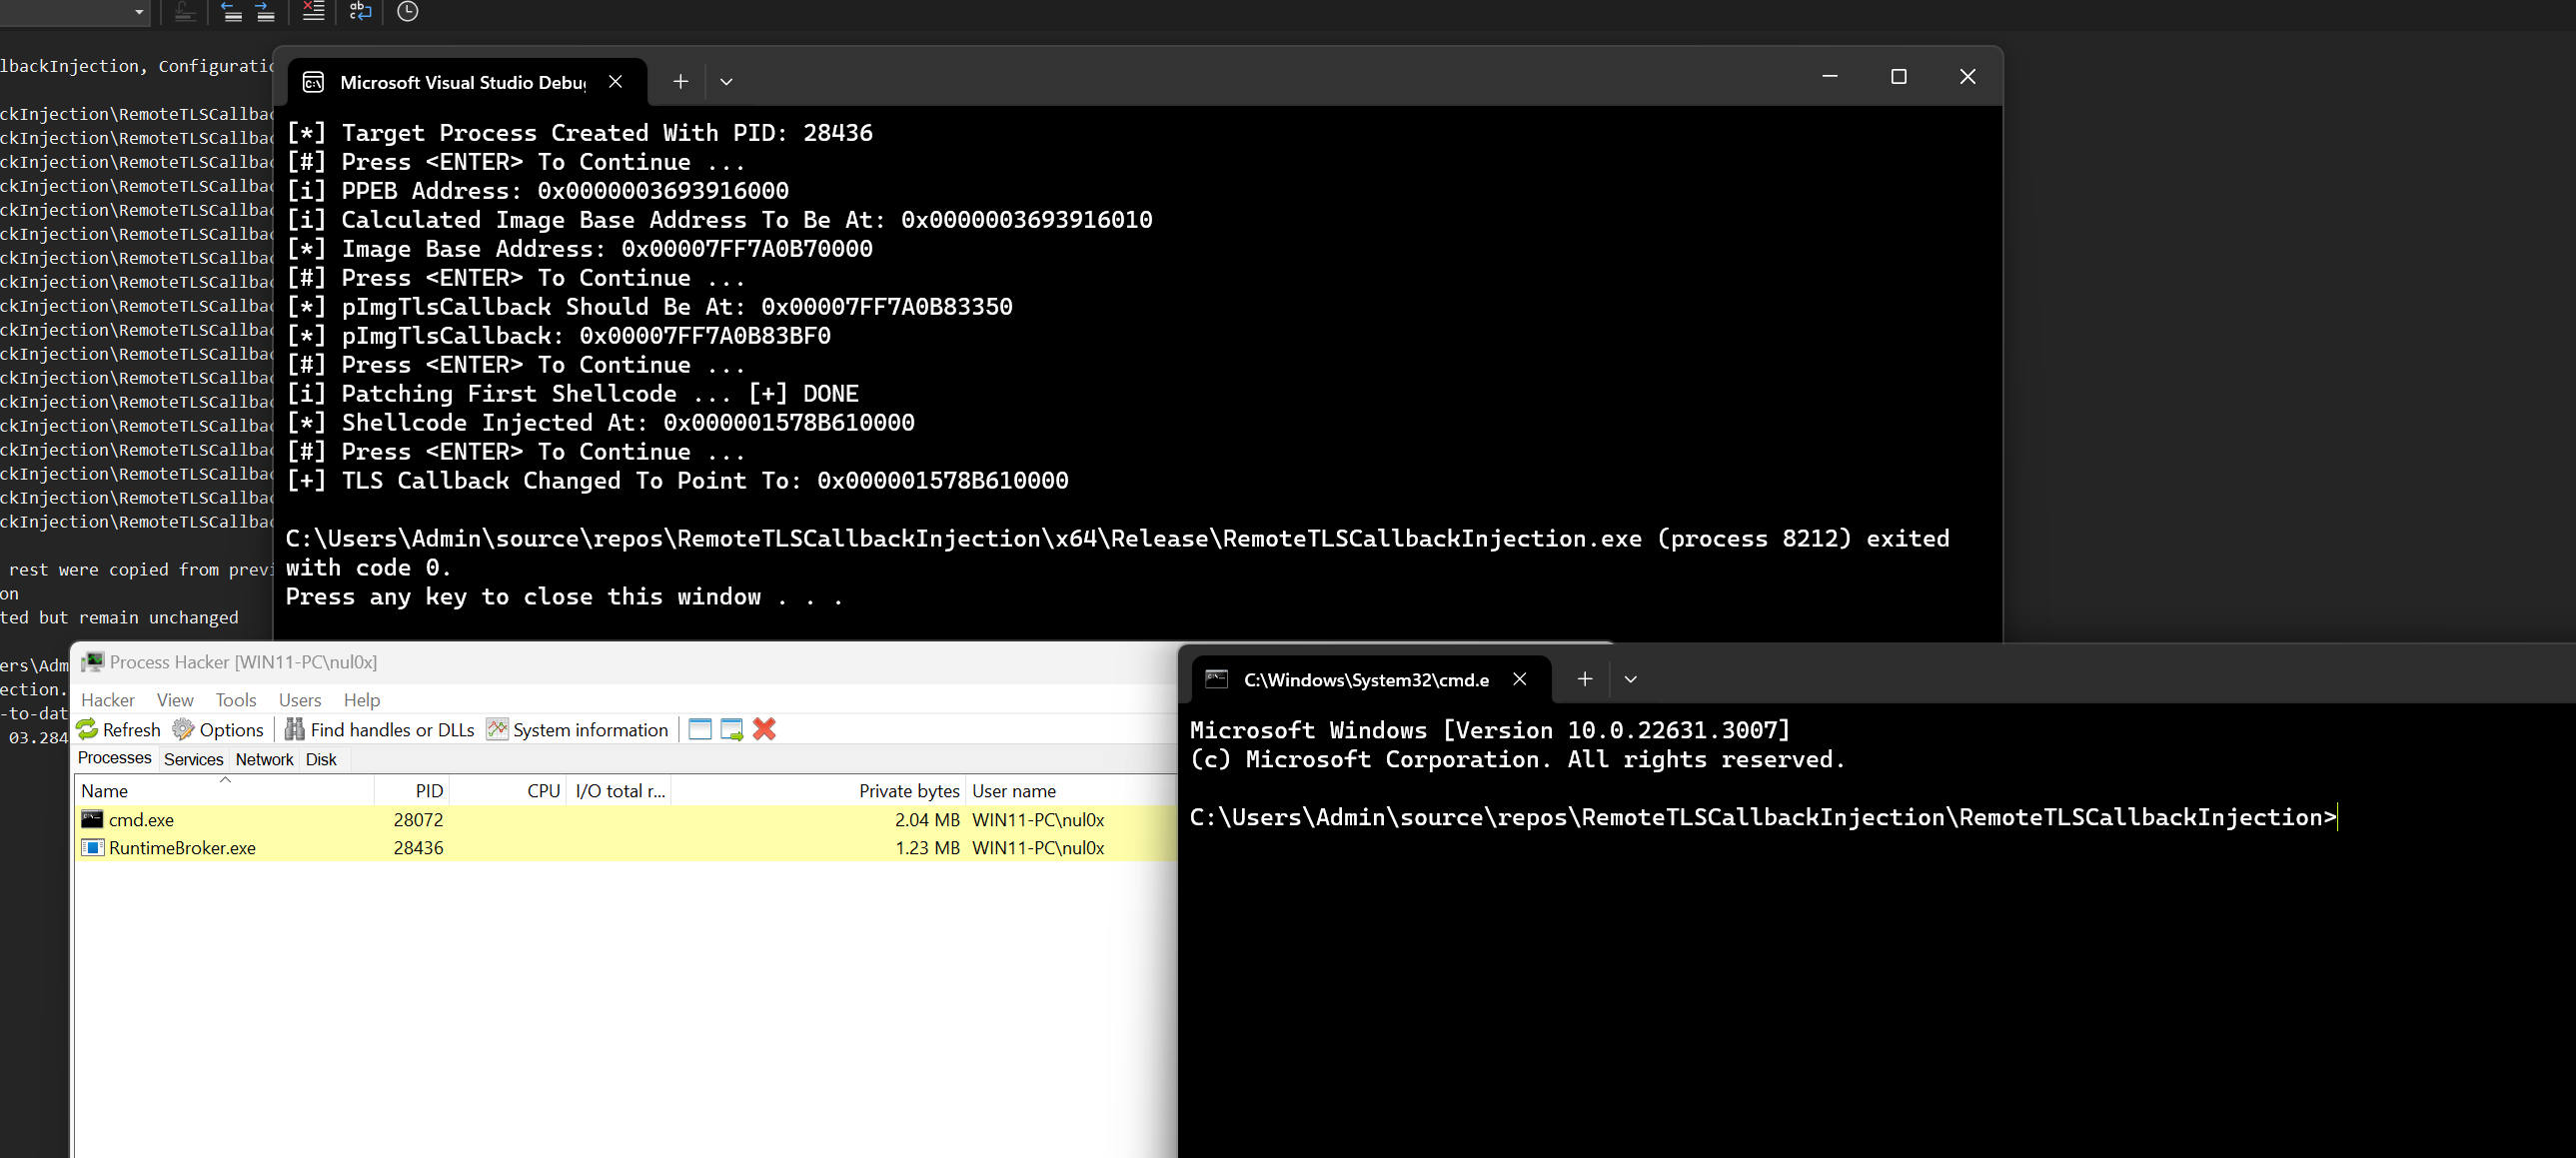 maldev-academy/remotetlscallbackinjection
Utilizing TLS callbacks to execute a payload without spawning any threads in a remote process
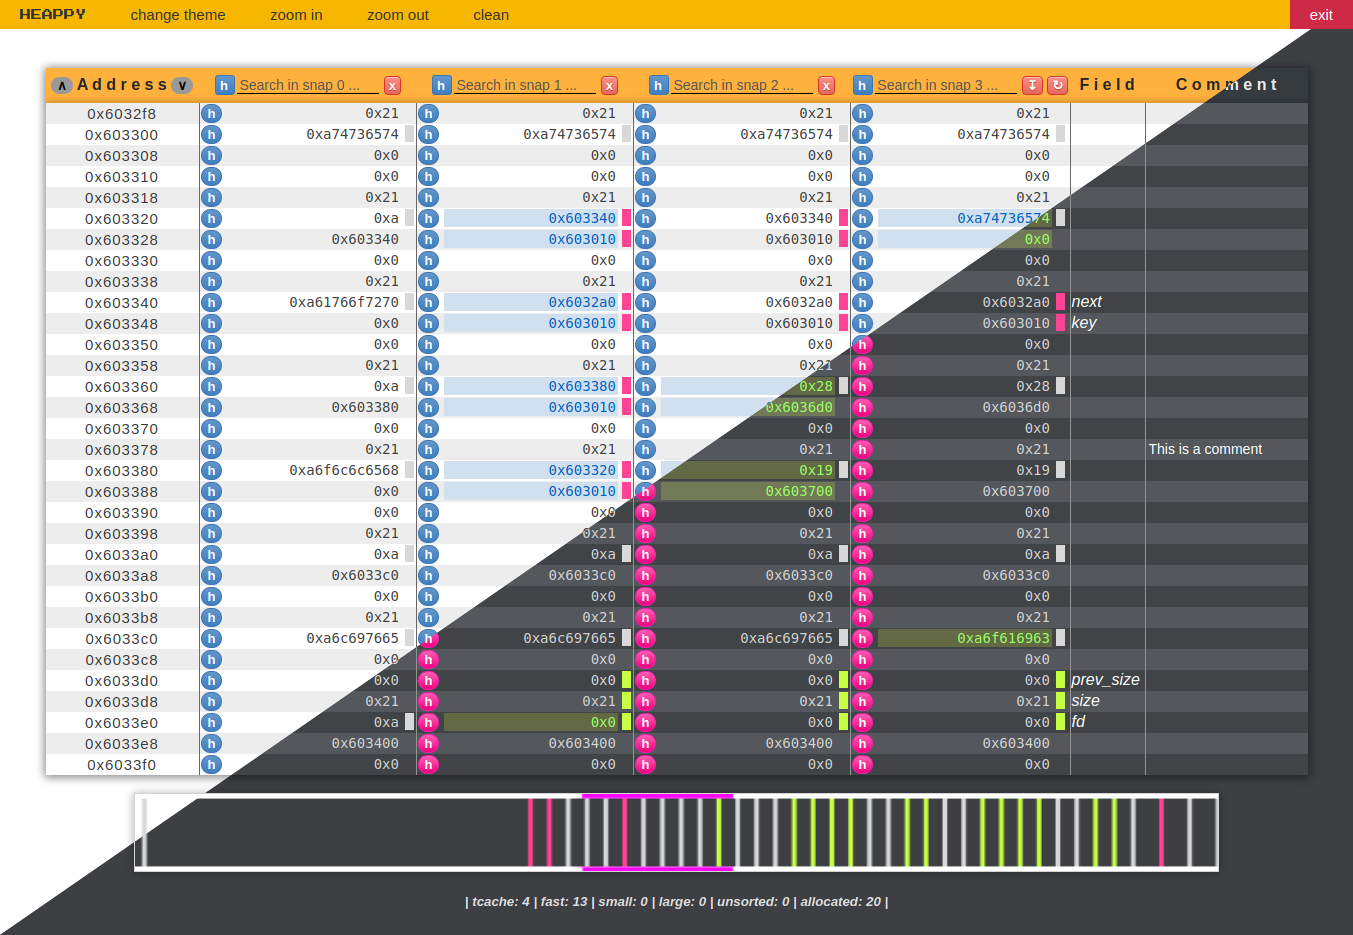 gand3lf/heappy
A happy heap editor to support your exploitation process :slightly_smiling_face: