

Nest
 owasp/nest
Your gateway to OWASP. Discover, engage, and help shape the future!
api-securitycurated-resourceseducation+2
owasp/nestYour gateway to OWASP. Discover, engage, and help shape the future!
 j-dahl7/mcp-attack-detection-sentinel
Sentinel detection lab for MCP attack chains: CVE-2026-26118 SSRF token theft, tool poisoning, cross-server exfiltration, identity post-exploitation.…
 owasp/owaspbugbounty
This is a container of web applications that work with OWASP Bug Bounty for Projects
 scriptingxss/iotgoat
IoTGoat is a deliberately insecure firmware based on OpenWrt.
 owasp/iotgoat
Deliberately insecure OpenWrt-based firmware for hands-on IoT security training. Features vulnerability challenges mapped to the OWASP IoT Top 10 for…
 dheeraj-jayaswal/cicd-goat-vapt-writeup
Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…
 waburig/open-worldwide-application-security-project-owasp-
Automated Web Vulnerability Assessment of DVWA using OWASP ZAP to identify and analyze critical security flaws like Remote Code Execution…
 owasp/secure-coding-practices-quick-reference-guide
The Secure Coding Practices Quick-reference Guide from OWASP
 owasp/security-champions
OWASP guide for security champions, providing curated resources and learning paths to foster security culture and practices within development teams.
 owasp/owaspwebgoatphp
A deliberately vulnerable web application for learning web application security.
 webgoat/webgoat
Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
 owasp/cornucopia
The source files and tools needed to build the OWASP Cornucopia decks in various languages
 owasp/nodegoat
The OWASP NodeGoat project provides an environment to learn how OWASP Top 10 security risks apply to web applications developed using Node.js and how…
 owasp/benchmark
The OWASP Benchmark GitHub repo has moved to: https://github.com/OWASP-Benchmark/BenchmarkJava
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
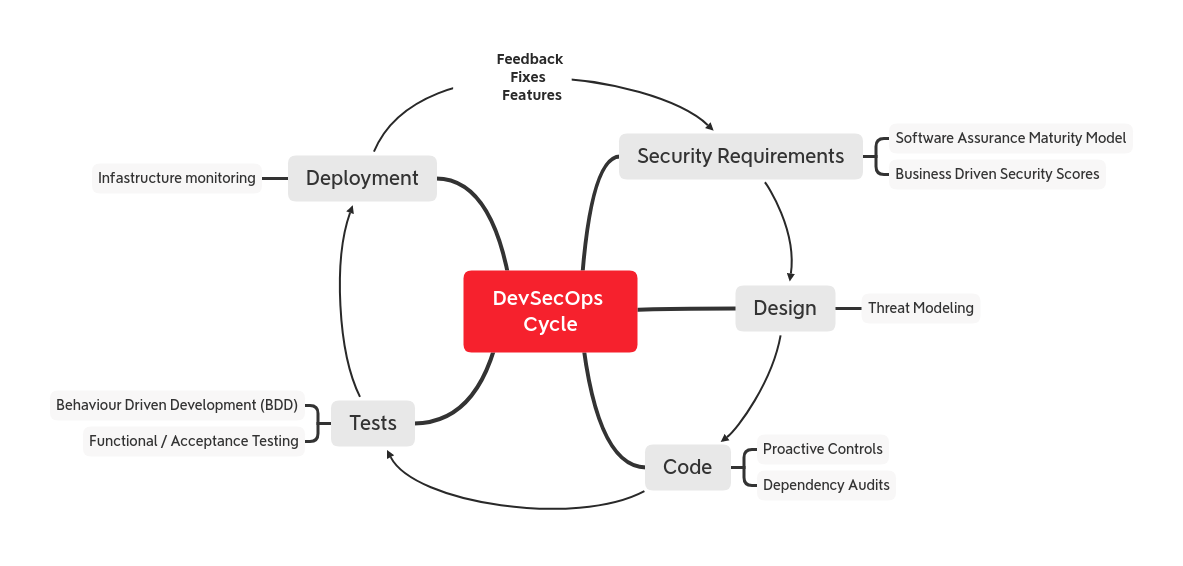 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.