CVE-2025-27480-The-Silent-Gateway-Risk

Letting attackers run malicious code without needing a cracked password, user interaction, or even a foothold in your network. That’s CVE-2025-27480

Letting attackers run malicious code without needing a cracked password, user interaction, or even a foothold in your network. That’s CVE-2025-27480

Simple Windows and Linux keystroke injection tool that exfiltrates stored WiFi data (SSID and password).

One place for all the default credentials to assist the Blue/Red teamers identifying devices with default password 🛡️

Comprehensive penetration testing cheat sheet for PWK/OSCP exam preparation, covering privilege escalation, password cracking, payload generation,…

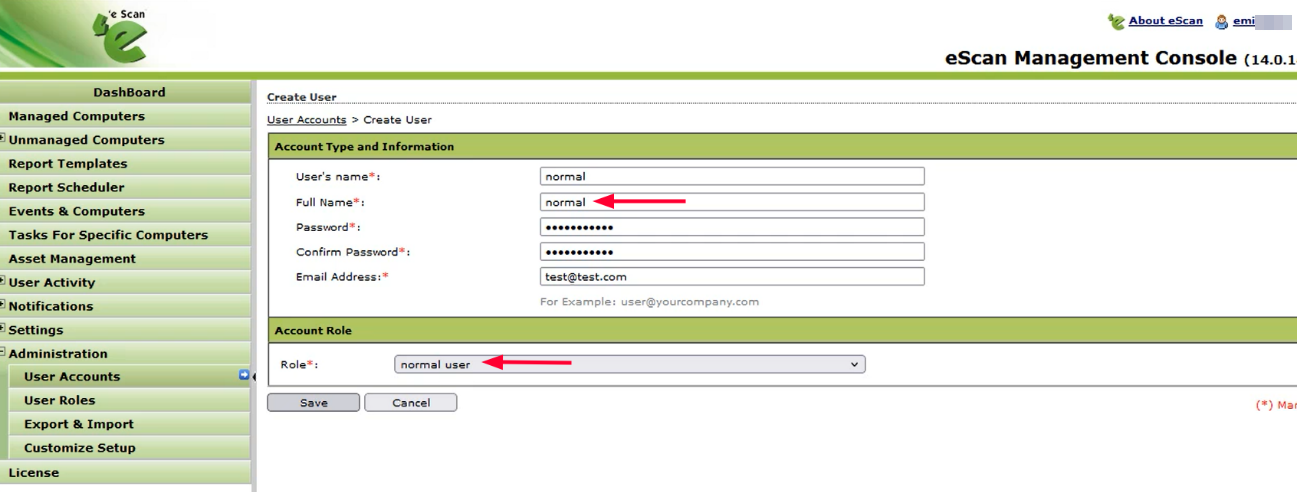
eScan Management Console version 14.0.1400.2281 contains privilege escalation via `GetUserCurrentPwd` function lets attackers retrieve any user's…

Exploitation and defense-in-depth mitigation strategies for the KeePass memory leakage vulnerability (CVE-2023-32784).

Detailed CVE-2026-8697 writeup with POC exploit for a login rate-limit bypass on TP-Link Archer C64 routers via a debug SSH service, enabling…

VulnHub DC-1 boot-to-root — exploiting CVE-2018-7600 (Drupalgeddon2) for RCE, extracting DB credentials from settings.php, forging admin password…

SecRep Is a Repository That Contain Useful Intrusion, Penetration and Hacking Archive Including Tools List, Cheetsheet and Payloads

An open source implementation of Apple's Wi-Fi Password Sharing protocol in Python.

DDOS Tool: To take down small websites with HTTP FLOOD. Port scanner: To know the open ports of a site. FTP Password Cracker: To hack file system of…

Automated OSINT framework for ethical hacking audits. Collects employee emails, password hashes, subdomains, and IPs via BreachDirectory and…

Microsoft Outlook Information Disclosure Vulnerability (leak password hash) - CVE-2024-21413 POC

Just a PoC tool to extract password using CVE-2019-1653.

PoC Script for CVE-2024-25832: Exploit chain reverse shell, information disclosure (root password leak) + unrestricted file upload in DataCube3

HTB_Enigma Security Assessment – Full pentest completed, chaining NFS disclosure, IMAPS password reuse, and OS Command Injection in OpenSTAManager…

A vulnerable Boot-to-Root CTF lab machine simulating a hospital environment. Features a realistic 17-step attack chain including SQL Injection, XSS,…

This project simulates a real-world attack-and-defend scenario across two virtual machines. You will exploit a critical pre-authentication RCE…