mediatek-wlan-heap-overflow-cve-2026-20452-filogic-router-rce

Proof-of-concept exploit for CVE-2026-20452, a heap-based buffer overflow in MediaTek WLAN AP drivers. Uses scapy to send crafted Wi-Fi management…

Proof-of-concept exploit for CVE-2026-20452, a heap-based buffer overflow in MediaTek WLAN AP drivers. Uses scapy to send crafted Wi-Fi management…

PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…

This technical research and review is for educational purposes on public code and constitutes Fair Dealing under the Copyright Act (Canada).

Proof-of-concept exploit for CVE-2023-36003, a Windows Defender security feature bypass enabling privilege escalation and code execution evasion on…

Stack buffer overflow PoC in an embedded TLS certificate parser using a crafted X.509 SAN extension for remote code execution on IoT and industrial…

Technical analysis and proof-of-concept for Apache Struts 1 class parameter manipulation (CVE-2014-0114), demonstrating remote code execution on…

Proof-of-concept exploit for CVE-2021-42013, demonstrating path traversal and remote code execution on Apache 2.4.50 via double URL encoding bypass…

Python source code auditing and static analysis on a large scale

Curated directory of static analysis (SAST) tools and linters for programming languages, configs, build tools, and CI, focused on improving code…

A curated list of public TEE resources for learning how to reverse-engineer and achieve trusted code execution on ARM devices

Step-by-step reproduction guide for CVE-2024-37742, a clipboard exploit in Safe Exam Browser (SEB) ≤ 3.5.0 on Windows, with PoC code and analysis.

Bash exploit for CVE-2011-2553 enabling remote code execution and privilege escalation on vulnerable FTP services via a special character in the USER…

This is poc of CVE-2022-46169 authentication bypass and remote code execution

Unauthenticated Command Injection in Cacti <= 1.2.22

Educational Redis rogue server tool for post-exploitation. Deploys a malicious Redis server to achieve remote code execution and execute arbitrary…

This repository details a SQL Injection vulnerability in Inventio Lite v4's, including exploitation steps and a Python script to automate the attack.…

The code of VulTriage: Triple-Path Context Augmentation for LLM-Based Vulnerability Detection

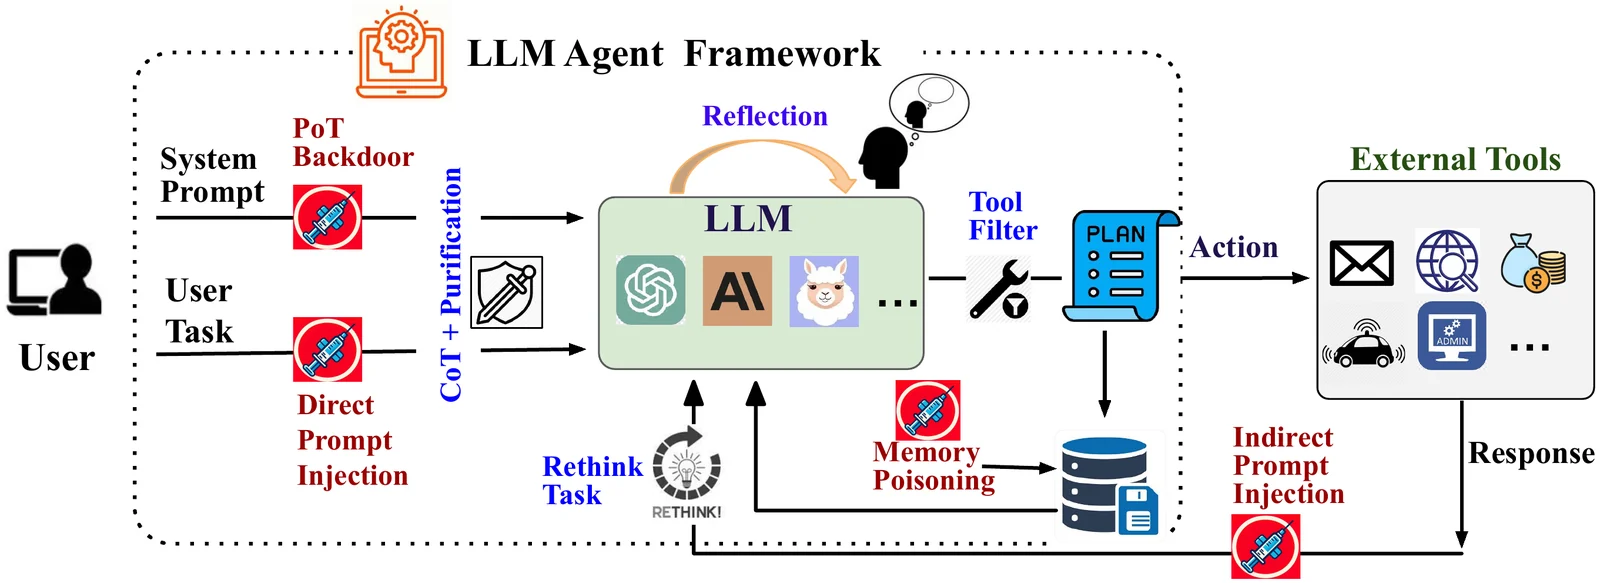
Research code and experiments for defending tool-integrated LLM agents against adversarial attacks, extending Agent Security Bench with new defense…