osint-menace
 awesom3alex/osint-menace
Passive OSINT triage console for email, username, domain, IP, and crypto wallet reconnaissance. Features case management, curated resource links, and…
cryptographycurated-resourcesdns-analysis+5
9
awesom3alex/osint-menacePassive OSINT triage console for email, username, domain, IP, and crypto wallet reconnaissance. Features case management, curated resource links, and…
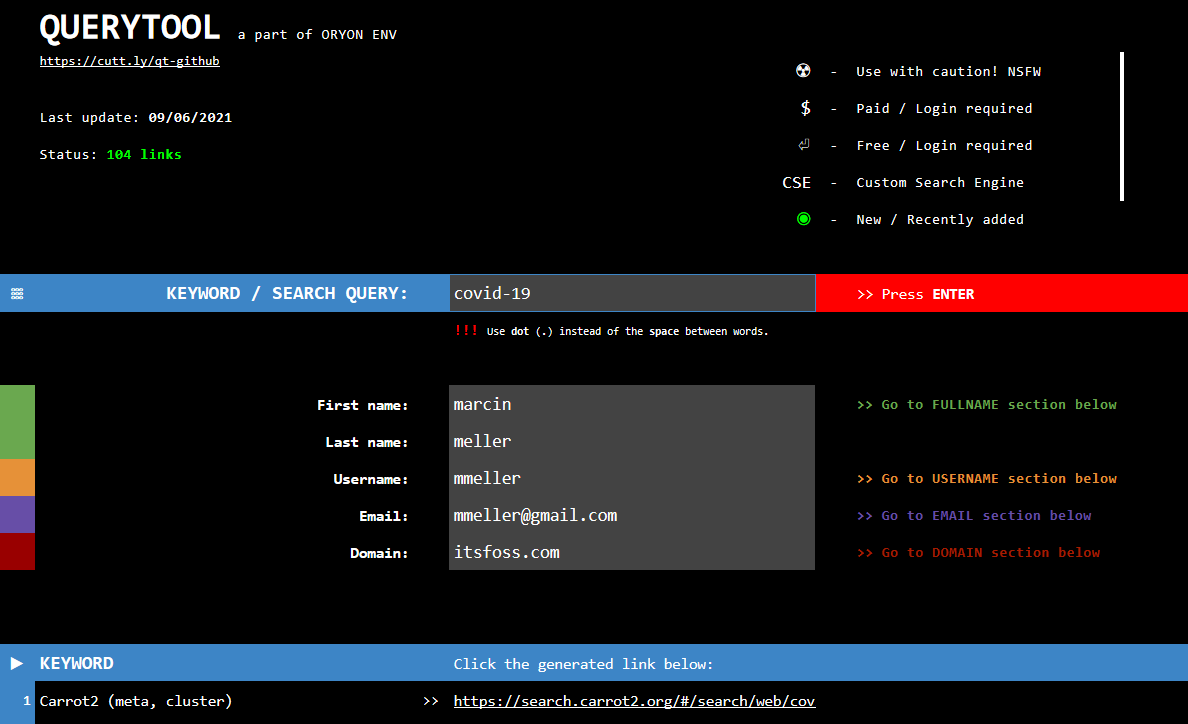 oryon-osint/querytool
Querytool is an OSINT framework based on Google Spreadsheet. With this tool you can perform complex search of terms, people, email addresses, files…
 t-beckett/h-osint
Local-first, keyboard-driven OSINT workbench for the terminal with 28 modules covering username, domain, IP, email, breach, and geolocation lookups…
 mouna23/osint-with-llm
It’s an OSINT reconnaissance poc powered by Local LLMs (Ollama). You can feed it an email, domain, or IP, and it automatically performs multiple…
 fknmega/aether
AI-driven OSINT and security research agent that builds a live knowledge graph from public data, with bundled recon tools and offensive-security…
 cure53/httpleaks
Enumerates all HTML elements and attributes that can leak HTTP requests, enabling testing of browsers, web proxies, and email clients for unintended…
 0xdims/cve-2019-16759
This tools will extracts and dumps Email + SMTP from vBulletin database server
 0x00phantom-hat/cve-2026-12400-exploit
Authenticated WordPress IDOR exploit for CVE-2026-12400; enumerates FlowForms REST form IDs and modifies form content or hijacks email notifications.
 dthkhang/cve-2023-5561-poc
PoC exploit for CVE-2023-5561 that enumerates WordPress user email addresses via the /wp-json/wp/v2/users API endpoint. For authorized security…
 bhanunamikaze/cve-2024-42009
This Proof of Concept (PoC) demonstrates an exploit for CVE-2024-42009, leveraging a cross-site scripting (XSS) vulnerability to extract emails from…
 woj-ciech/pepe
Collect information about email addresses from Pastebin
 ritvikb99/dark-fantasy-hack-tool
DDOS Tool: To take down small websites with HTTP FLOOD. Port scanner: To know the open ports of a site. FTP Password Cracker: To hack file system of…
 hamed233/cybersecurity-mastery-roadmap
A comprehensive, step-by-step guide to mastering cybersecurity from beginner to expert level with curated resources, tools, and career guidance
 cyberleelawat/cve-2025-20393
Cisco is aware of a potential vulnerability. Cisco is currently investigating and will update these details as appropriate as more…
 randomrobbiebf/cve-2024-0368
Hustle Plugin <= 7.8.3 contains hardcoded HubSpot API credentials in inc/providers/hubspot/hustle-hubspot-api.php
 artemcyberlab/project-ntlm-hash-capture-and-phishing-email-exploitation-for-cve-2024-21413
Demonstrates capturing NTLM hashes via Responder and executing phishing emails exploiting CVE-2024-21413 to compromise systems.