
CVE-2022-27254
 nonamecoder/cve-2022-27254
Proof-of-concept demonstrating RF replay attack on Honda's remote keyless entry system (CVE-2022-27254) using HackRF One and GNU Radio for signal…
educationexploitationhardware-security+1
461
nonamecoder/cve-2022-27254Proof-of-concept demonstrating RF replay attack on Honda's remote keyless entry system (CVE-2022-27254) using HackRF One and GNU Radio for signal…
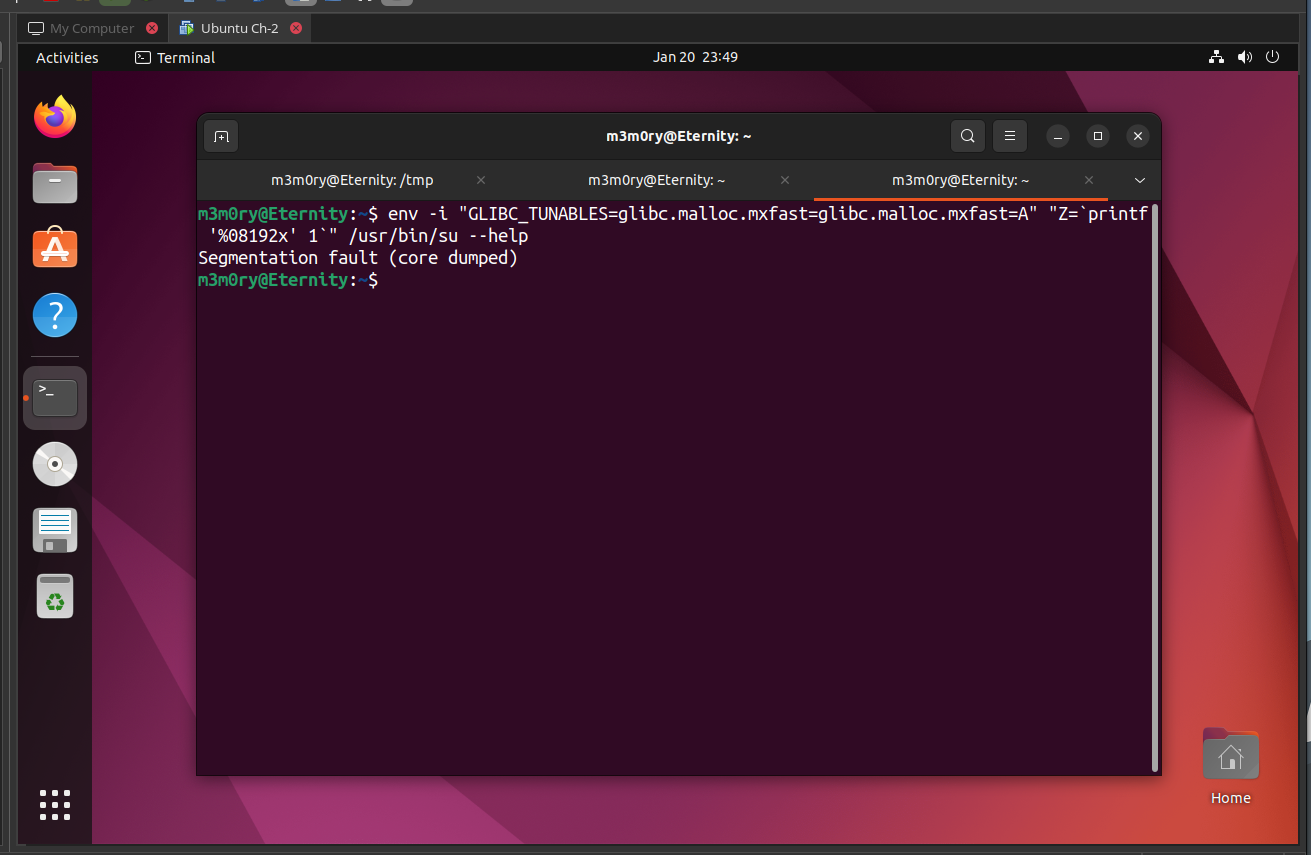 nishanthanand21/cve-2023-4911-poc
Repository containing a Proof of Concept (PoC) demonstrating the impact of CVE-2023-4911, a vulnerability in glibc's ld.so dynamic loader, exposing…
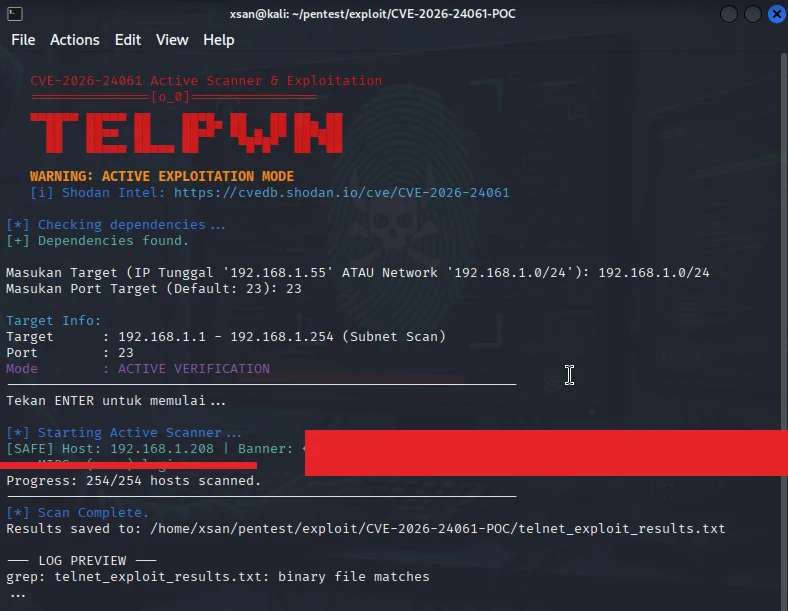 xsanflip/cve-2026-24061-scanner
Bash-based scanner for CVE-2026-24061 that performs subnet reconnaissance, banner grabbing, and active exploitation checks against GNU Inetutils…
 jedai47/cve-2018-17182
Proof-of-concept exploit for CVE-2018-17182, a Linux kernel use-after-free vulnerability in the mm subsystem, demonstrating privilege escalation via…
 akpmarcelin/cve-2026-24061-lab
Reproduction lab for CVE-2026-24061, an authentication bypass in GNU InetUtils telnetd. Provides a Vagrant-based isolated environment and…
 cumakurt/tscan
Python-based scanner that detects and exploits CVE-2026-24061 telnetd authentication bypass, enabling root shell access on vulnerable GNU Inetutils…
 w00t3k/awesome-cellular-hacking
Awesome-Cellular-Hacking
 ekomssavior/telnet_scan
scanner/exploiter CVE-2026-24061 & CVE-2026-32746
 chosenonehacks/cve-2026-32746
Proof-of-concept exploit for a pre-authentication buffer overflow in GNU InetUtils telnetd (CVE-2026-32746), including a Docker lab environment and…
 chocapikk/cve-2026-24061
Proof-of-concept exploit for GNU Inetutils telnetd authentication bypass (CVE-2026-24061) with Docker lab setup and Go PoC. Exploits NEW-ENVIRON…
 haitam-lazaar/libextractor-privesc
Proof-of-concept for CVE-2026-100310, a local privilege escalation in GNU libextractor ≤1.15 via the LIBEXTRACTOR_PREFIX untrusted search path, with…
 kaleth4/cve-2026-32746
Proof-of-concept exploit for CVE-2026-32746, a critical remote code execution vulnerability in GNU Inetutils telnetd via LINEMODE SLC buffer…
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 cao-wuhui/cve-2025-69720
Advisory for CVE-2025-69720: stack-based buffer overflow in GNU ncurses infocmp (CWE-121)
 jakeswiz/telnet-inetutils-auth-bypass-cve-2026-24061
This is a simple PoC that allows you to highlight the severity of the ongoing and actively exploited Telnet bug that is going on right now. Why…
 0xmoga/cve-2023-4911-lab
Docker-based CVE-2023-4911 lab for analyzing glibc ld.so buffer overflow and developing a local privilege escalation exploit with GDB debugging.
 hironull/cve-2018-1207-better
Reverse Shell CVE for iDRAC 7 & 8 with firmware 2.52.52.52 and below.
 knightc0de/shellshock_vuln_exploit
Python exploit for CVE-2014-6271 (Shellshock) targeting vulnerable CGI scripts with reverse shell handler, supporting HTTP/HTTPS, custom paths, and…