FallingSkies-CVE-2023-35885

Python exploit for CVE-2023-35885 targeting CloudPanel v2.0.0–v2.3.0. Injects a webshell via a crafted serialized cookie to achieve remote code…

Python exploit for CVE-2023-35885 targeting CloudPanel v2.0.0–v2.3.0. Injects a webshell via a crafted serialized cookie to achieve remote code…

CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…

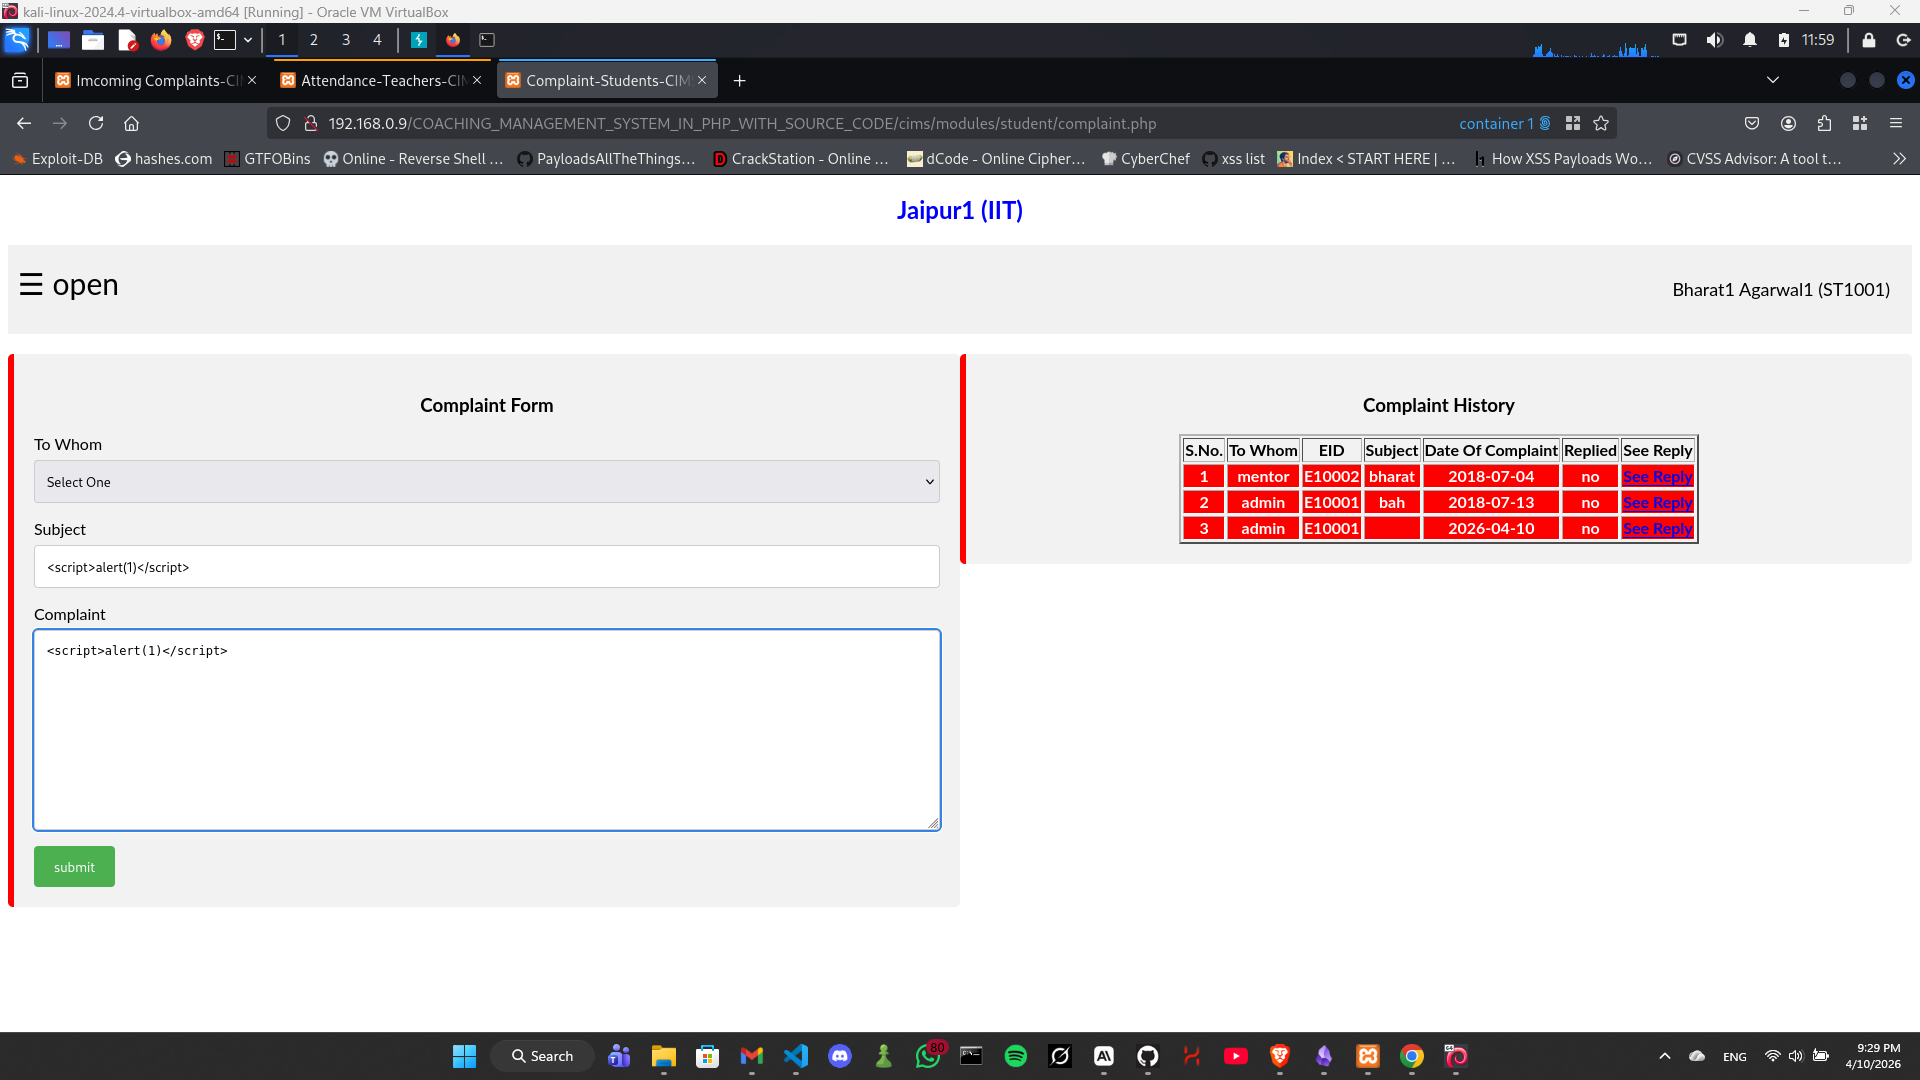
Proof-of-concept exploit for stored XSS (CWE-79) in a PHP coaching management system, demonstrating session hijacking and privilege escalation from…

SetCookie Analysis in Browser Research Results

Patched tough-cookie v2.5.0 fixing CVE-2023-26136 prototype pollution vulnerability with Object.create(null) in MemoryCookieStore, including exploit…

Exploiting WordPress vulnerabilities (CVE-2025-34077), authentication bypass via cookie injection, and privilege escalation to root. Part of my…

Researching on the vulnrability CVE-2023-26136

This repository contains a solution for the CVE-2023-26136 vulnerability.

Browser extension that automatically fills out cookie popups based on your preferences

Demo app to exploit CVE-2025-29927: NextJS middleware bypass via proxy-injected headers for unauthorized /admin access. Includes vulnerable app and…

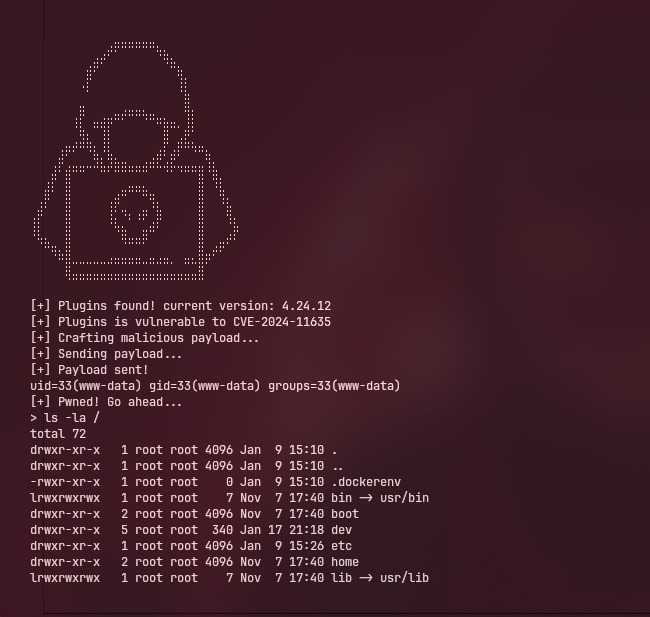
The WordPress File Upload plugin for WordPress is vulnerable to Remote Code Execution in all versions up to, and including, 4.24.12 via the…

Unauthenticated arbitrary file upload -> RCE in WPLP Cookie Consent (gdpr-cookie-consent) <= 4.4.1 - technical write-up and PoC

CVE-2008-1930 is a critical improper authentication vulnerability affecting the core cookie integrity mechanism in WordPress version 2.5. It allows…

Reflected Cross Site Scripting (XSS) in Intermesh BV Group-Office version 6.6.145, allows attackers to gain escalated privileges and gain sensitive…

In-depth technical analysis and proof-of-concept for CVE-2017-9822, an insecure deserialization vulnerability in DotNetNuke leading to remote code…

Interactive demo for CVE-2023-45857 (axios XSRF token bypass). Step-by-step guide to reproduce the vulnerability in a controlled dev container…

A POC for the all new CVE-2023-27524 which allows for authentication bypass and gaining access to the admin dashboard.

Technical analysis of CVE-2026-52924, a critical use-after-free in Linux kernel SCTP stale cookie handling, including root cause, attack flow, fix,…