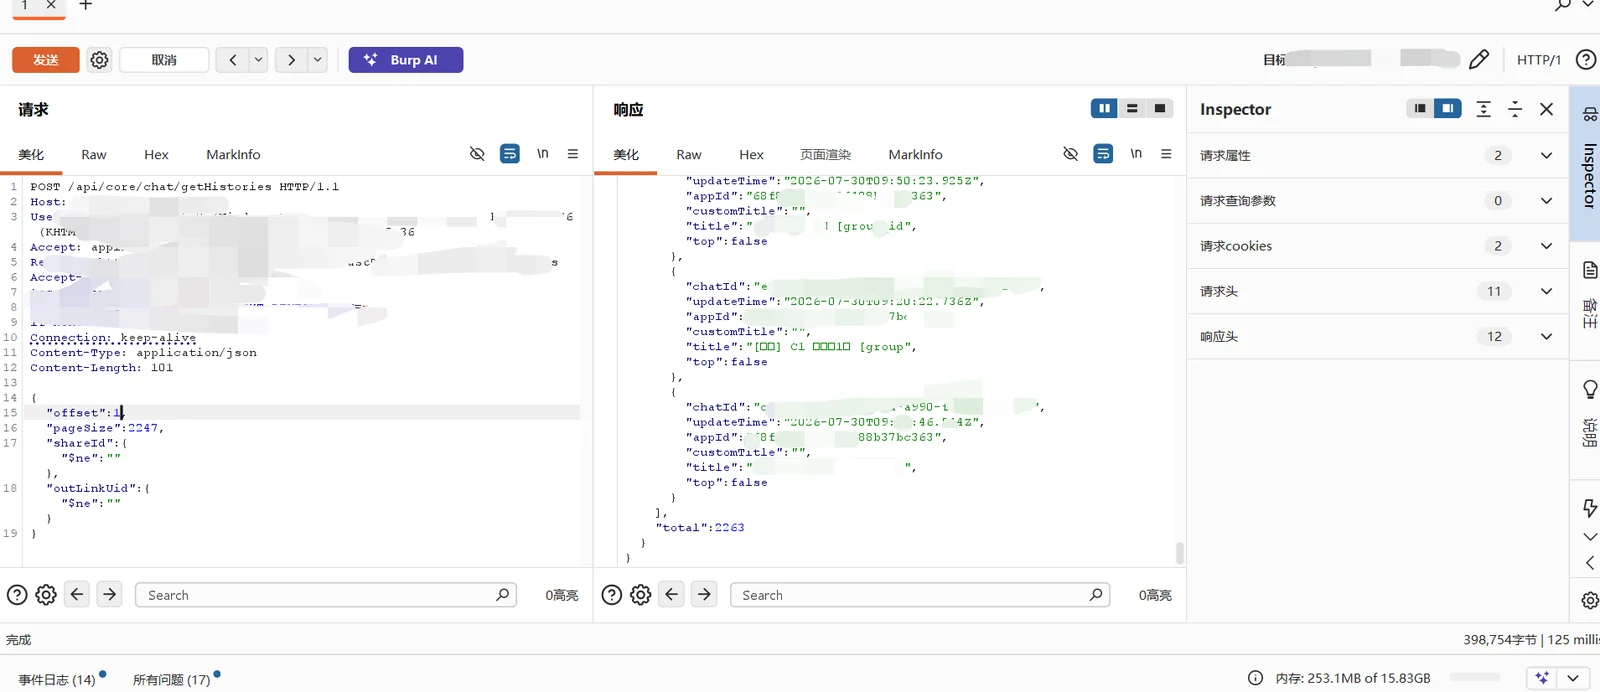
CVE-2026-79483-FastGPT-NoSQL-Injection

Proof-of-concept for CVE-2026-79483, a NoSQL injection in FastGPT Community Edition allowing unauthenticated access to chat history titles. Includes…

Proof-of-concept for CVE-2026-79483, a NoSQL injection in FastGPT Community Edition allowing unauthenticated access to chat history titles. Includes…

AI powered security analysis extension for Mobile Security Framework MobSF

Provides a chat-based, LLM-assisted reverse engineering experience within Ghidra

RSC Detect CVE 2025 55182

Security Advisory: Insufficient Access Controls Allow for Unauthorized File Downloads (Let's Chat)

Security Advisory: Unchecked Room Lookup Leads to Server Crash (Let's Chat)

Security Advisory: Insufficient Access Controls Allow for Unauthorized Room Deletion (Let's Chat)

Proof-of-concept for CVE-2026-36228 demonstrating a denial-of-service vulnerability in Easy Chat Server 3.1 via oversized mtowho parameter. Dry-run…

Demonstrates an Insecure Direct Object Reference (IDOR) vulnerability in Ai2's playground chat, allowing attackers to brute-force predictable message…

Benign proof-of-concept for CVE-2026-36227, a path traversal vulnerability in Easy Chat Server 3.1 user registration. Demonstrates unauthorized file…

Proof-of-concept demonstrating remote code execution via prompt injection in GitHub Copilot Chat, using a crafted Python file to trigger a…

Proof-of-concept for a reflected XSS vulnerability in AIBOX's chat component, demonstrating JWT token theft and account hijacking via crafted…

CAWODOG is a proof-of-concept project demonstrating how to protect Python-based AI models deployed on offline industrial machines. Across three…

An inventory of tools and resources about CyberSecurity that aims to help people to find everything related to CyberSecurity.

CLI tool for structured Telegram OSINT data collection. Scrapes members, messages, invite links, and user metadata from public/private groups,…

Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.

PoC for iTerm2 CVEs CVE-2024-38396 and CVE-2024-38395 which allow code execution

UnrealIRCd 3.2.8.1 backdoor exploit — reverse shell via AB; trigger, built from scratch in Python using raw sockets. No Metasploit.