
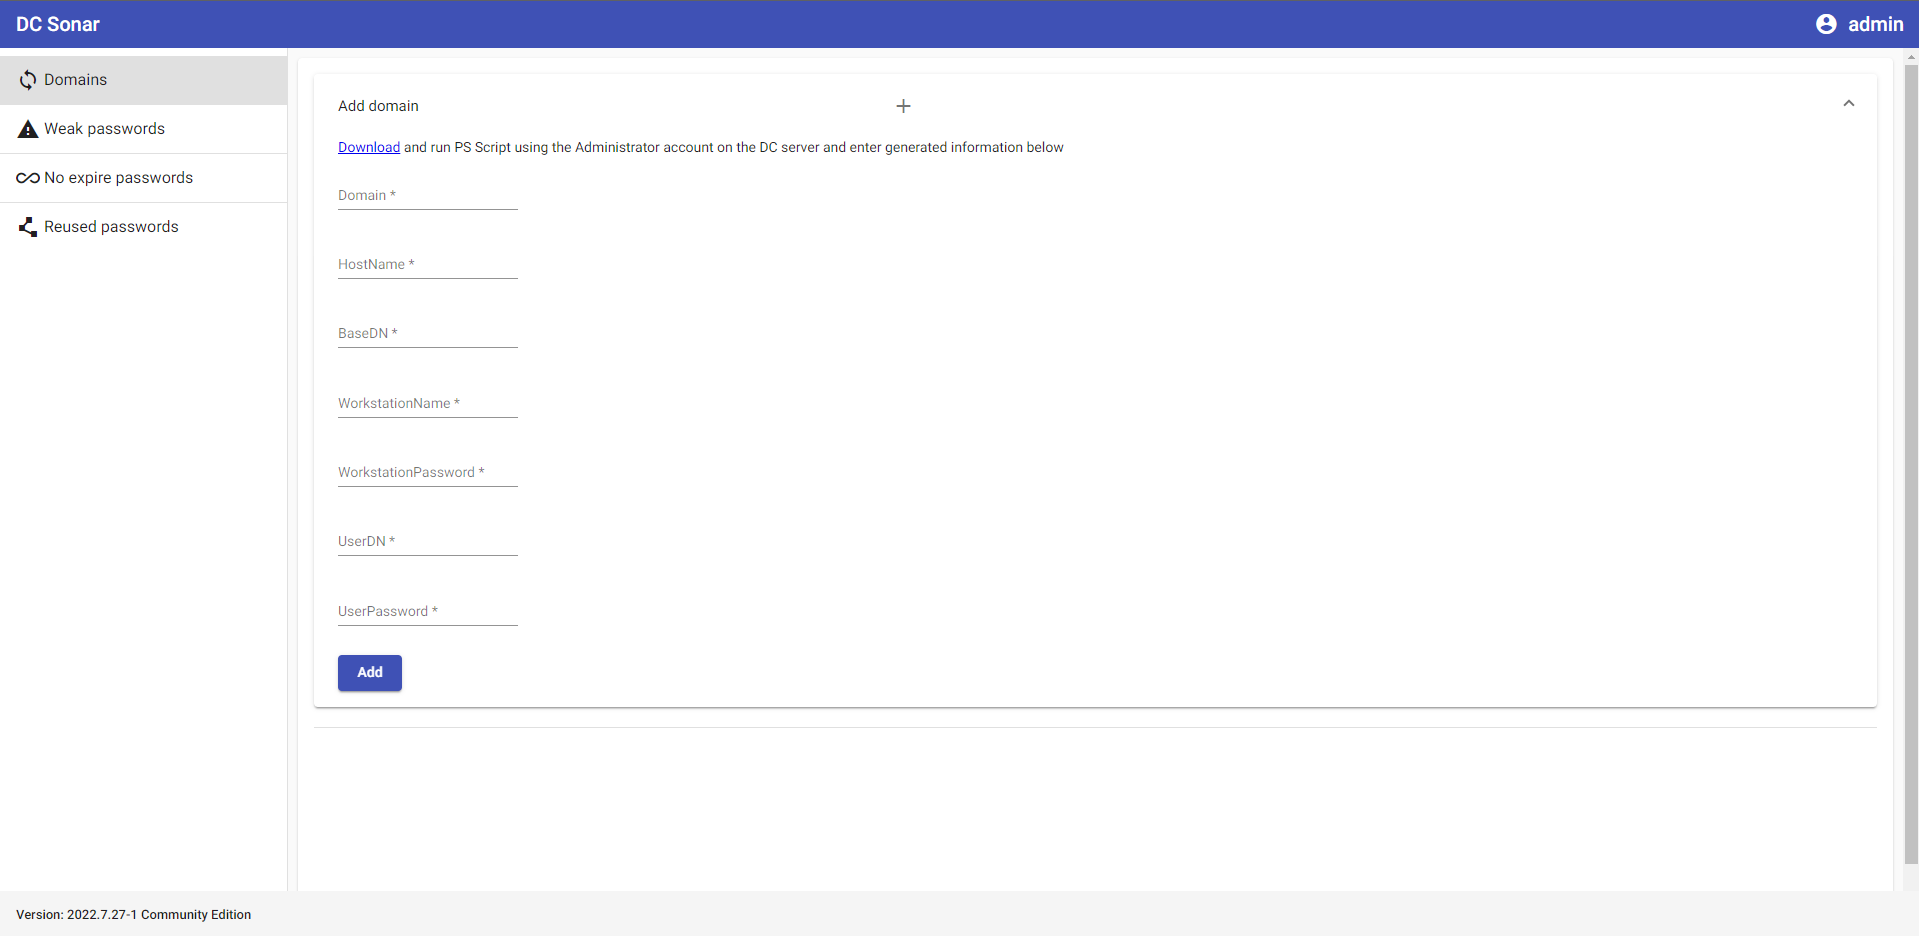
dc-sonar
 st1lly/dc-sonar
Analyzing AD domains for security risks related to user accounts
educationpassword-crackingvulnerability-analysis
st1lly/dc-sonarAnalyzing AD domains for security risks related to user accounts
 chpratik/cve-2026-54121
Improper authorization in Active Directory Certificate Services (AD CS) allows an authorized attacker to elevate privileges over a network.
 0xblackash/cve-2026-54121
CVE-2026-54121
 gh-badr/cve-2022-26923
A proof of concept exploiting CVE-2022-26923.
 rayngnpc/cve-2024-49019-rayng
Exploitation for CVE-2024-49019
 nefhara/cve-2022-26923
Automated CVE-2022-26923 Exploitation (Certifried)
 rayngnpc/cve-2022-26923-rayng
Exploitation for CVE-2022-26923
 ad-security/ad_miner
AD Miner is an Active Directory audit tool that leverages cypher queries to crunch data from the #Bloodhound graph database to uncover security…
 safebuffer/vulnerable-ad
Create a vulnerable active directory that's allowing you to test most of the active directory attacks in a local lab
 browninfosecguy/adlab
Active Directory Lab for Penetration Testing
 automatedlab/automatedlab
PowerShell-based provisioning framework for deploying complex lab environments on Hyper-V and Azure. Supports Windows, Linux, and products like AD,…
 snailsploit/claude-red
Curated library of 78 offensive security SKILL.md modules that prime Claude with expert red team methodology across web, AD, wireless, cloud, and…
 r1skkam/tryhackme-cve-2022-26923
Walkthrough on the exploitation of CVE-2022-26923, a vulnerability in AD Certificate Services
 dotadrien/cve-2025-60654
Proof-of-concept for CVE-2025-60654: stored cross-site scripting (XSS) in Script Pag ad description field. Demonstrates filter bypass using HTML tags…
 mvelazc0/badzure
BadZure automates the deployment of intentionally misconfigured Entra ID tenants and Azure subscriptions, populating them with diverse entities and…
 nebulock-inc/agentic-threat-hunting-framework
ATHF is a framework for agentic threat hunting - building systems that can remember, learn, and act with increasing autonomy.
 flx-0x00/cve-2026-59550
Unauthenticated time-based blind SQL injection PoC for AWP Classifieds <= 4.4.7, with a Docker lab, full writeup, and patch diff.
 shcesama/cve-2023-4863-analysis
Educational analysis of CVE-2023-4863 (libwebp heap buffer overflow) with Blue Team detection tools, static WebP scanner, defensive Java validator,…