
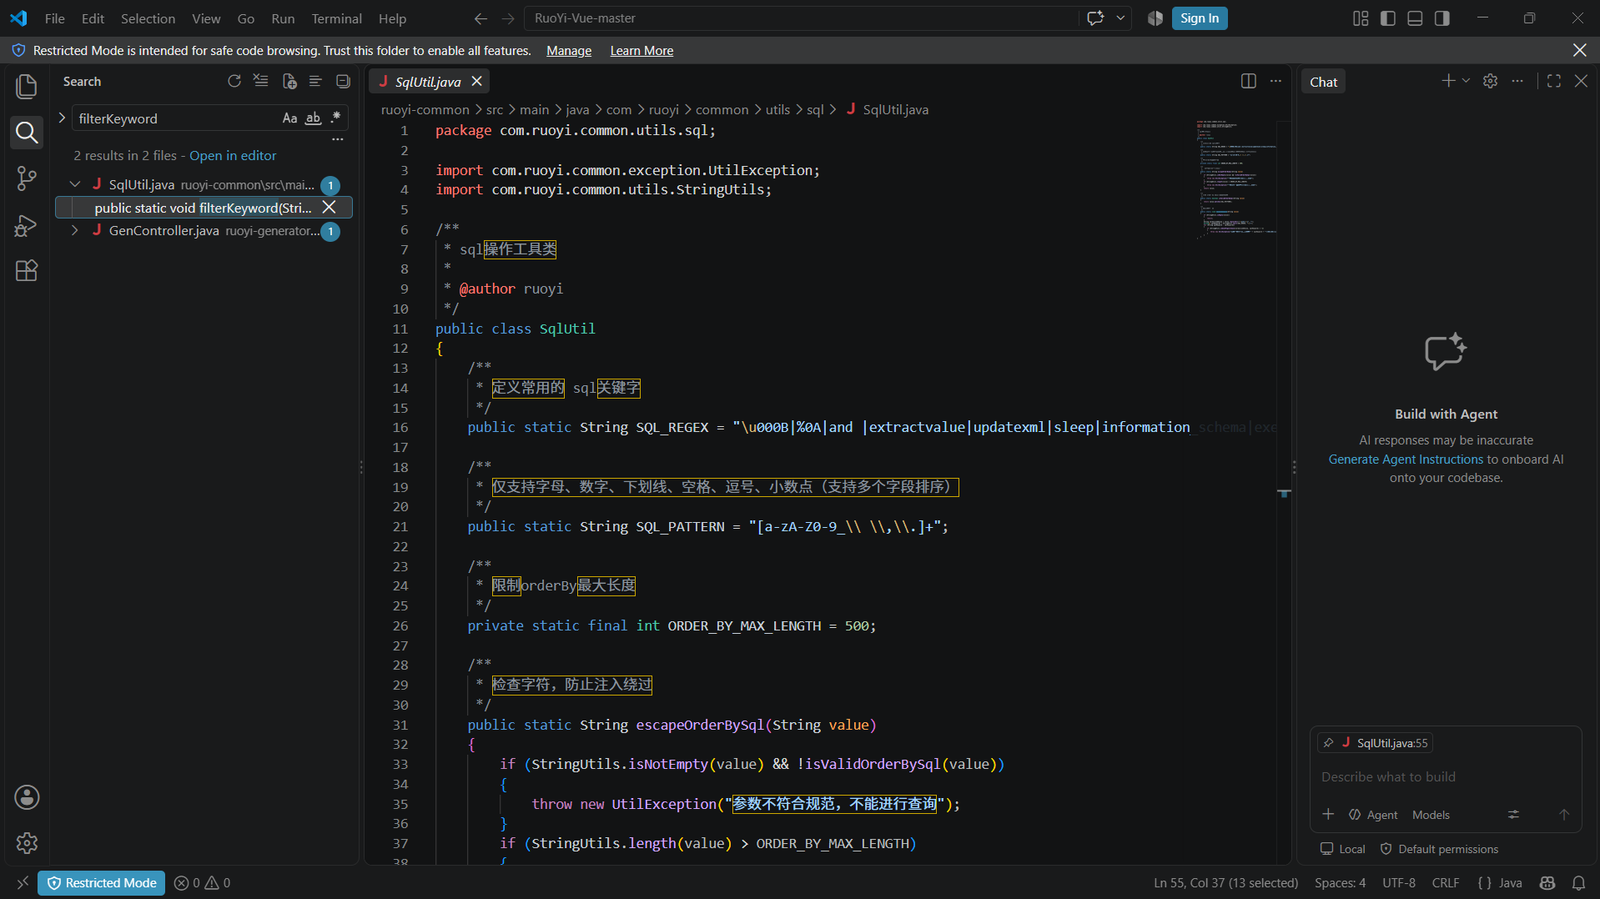
CVE-2024-57521-RuoYi-SQLi
 xs2024770/cve-2024-57521-ruoyi-sqli
Static code audit of CVE-2024-57521, an authenticated SQL injection in RuoYi-Vue's generator module, with source-to-sink analysis and a %0b filter…
educationexploitationpapers-research+4
xs2024770/cve-2024-57521-ruoyi-sqliStatic code audit of CVE-2024-57521, an authenticated SQL injection in RuoYi-Vue's generator module, with source-to-sink analysis and a %0b filter…
 hotpotcookie/cve-2021-44228-white-box
Log4j vulner testing environment based on CVE-2021-44228. It provide guidance to build the sample infrastructure and the exploit scripts. Supporting…
 sma-das/log4j-poc
An educational Proof of Concept for the Log4j Vulnerability (CVE-2021-44228) in Minecraft
 av4nth1ka/jinjava-cve-2026-25526-poc
Step-by-step exploit harness and proof-of-concept for CVE-2026-25526 in Jinjava, demonstrating file read, file creation, and info disclosure with…
 1in9e/apache-log4j2-rce
Apache Log4j2 RCE( CVE-2021-44228)验证环境
 nikolas-charalambidis/cve-2021-44228
A simple simulation of the infamous CVE-2021-44228 issue.
 cbuschka/log4j2-rce-recap
Little recap of the log4j2 remote code execution (CVE-2021-44228)
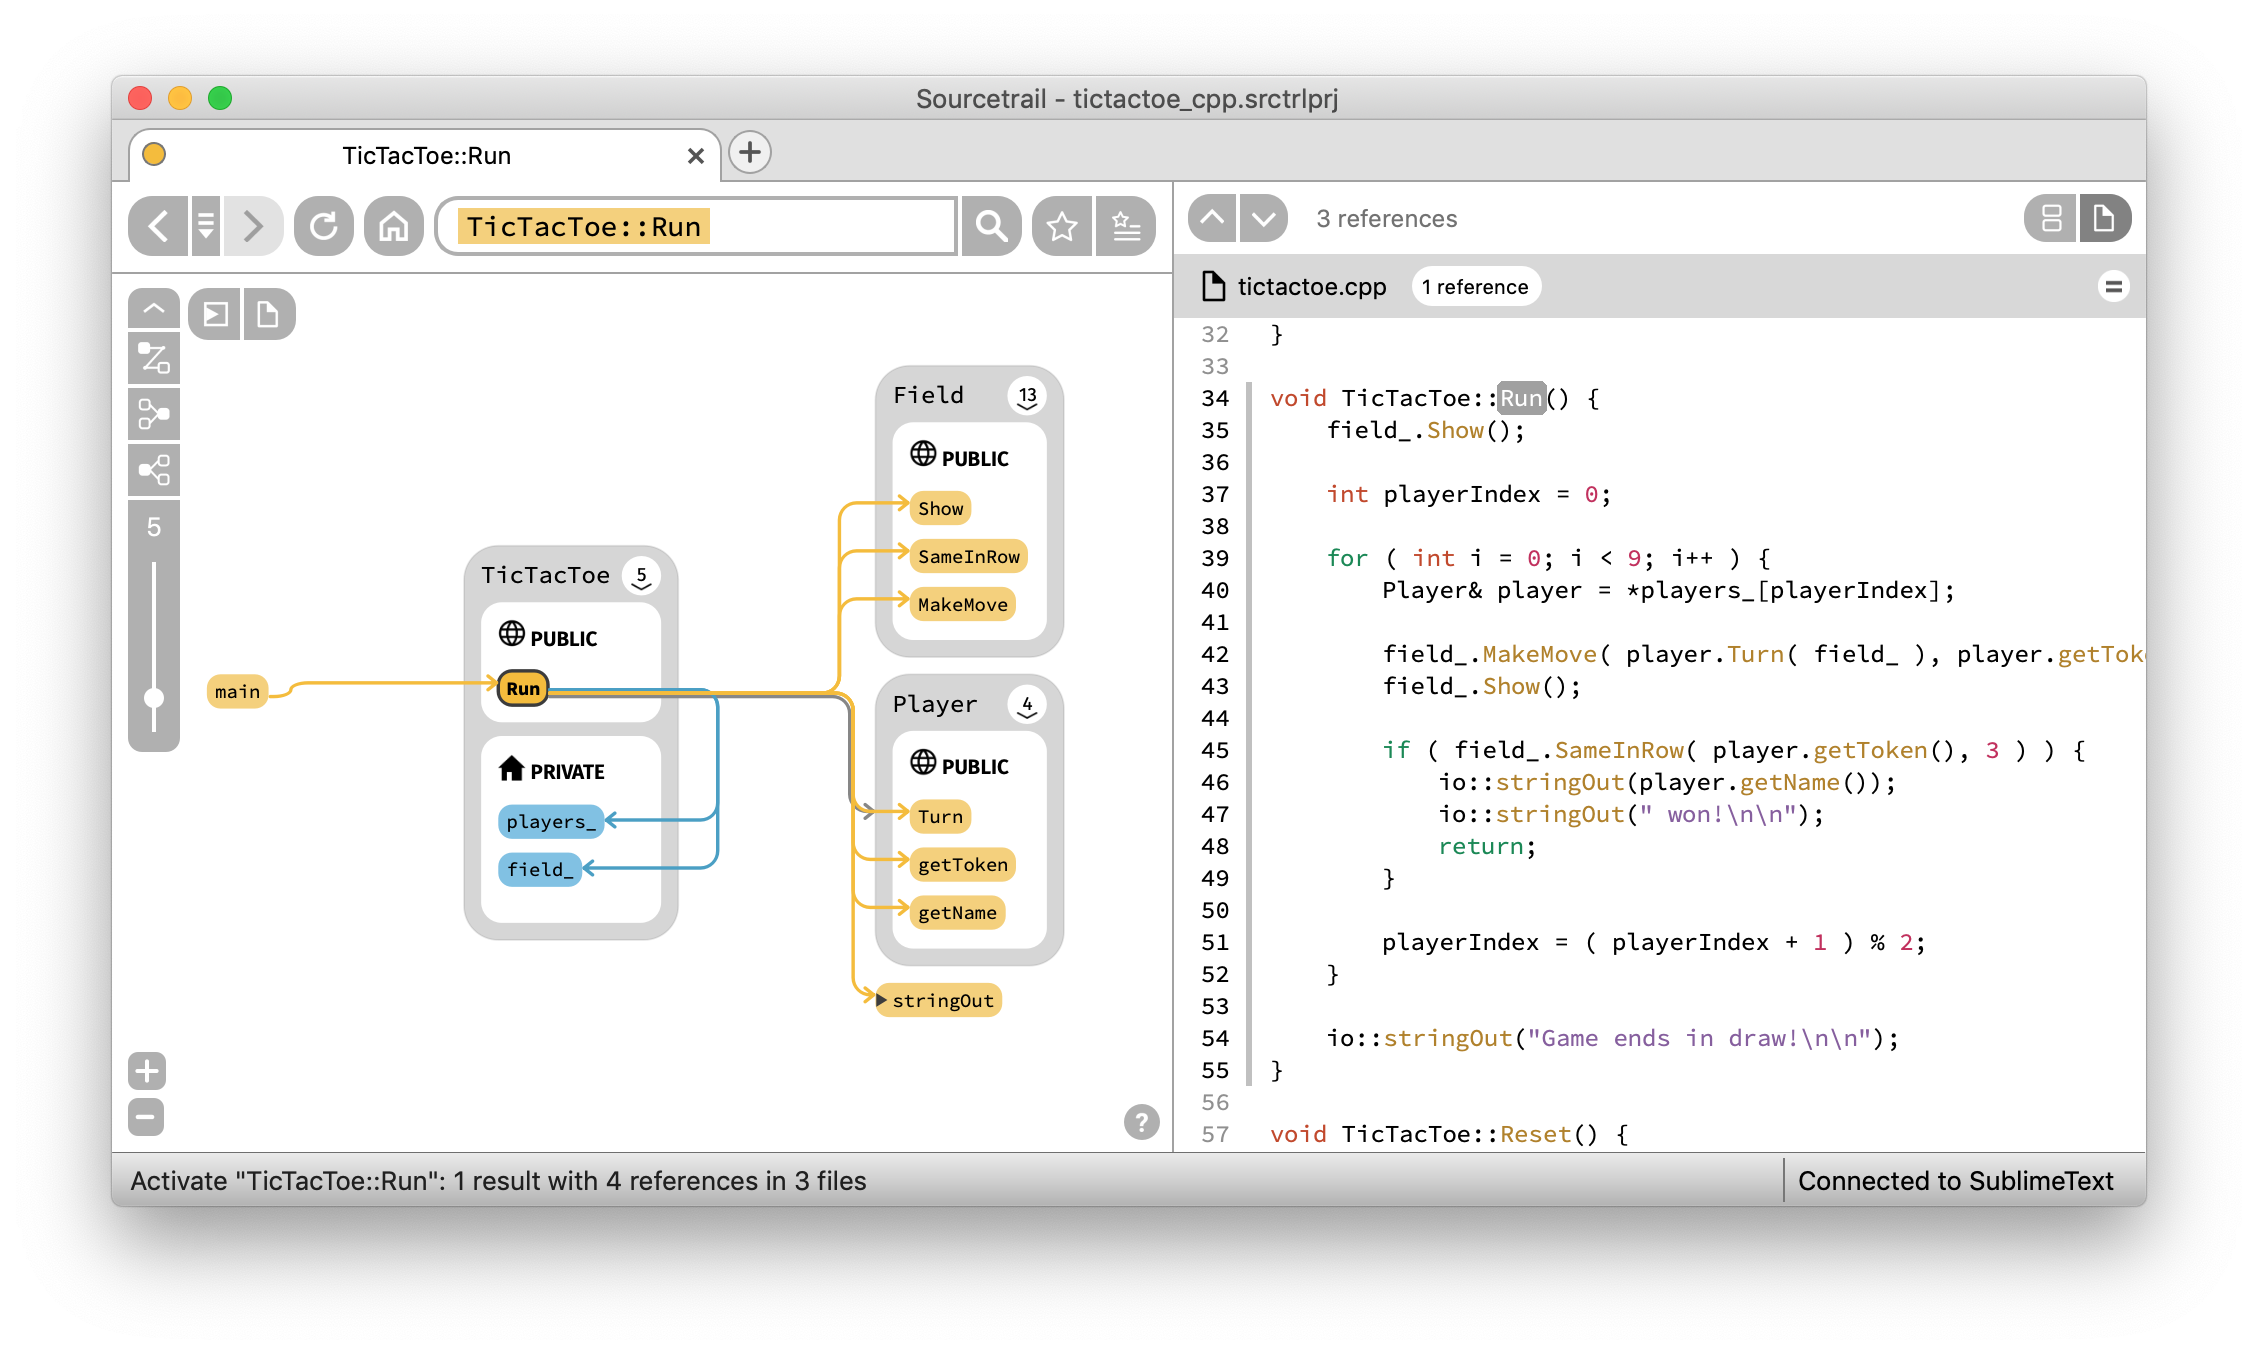 coatisoftware/sourcetrail
Sourcetrail - free and open-source interactive source explorer
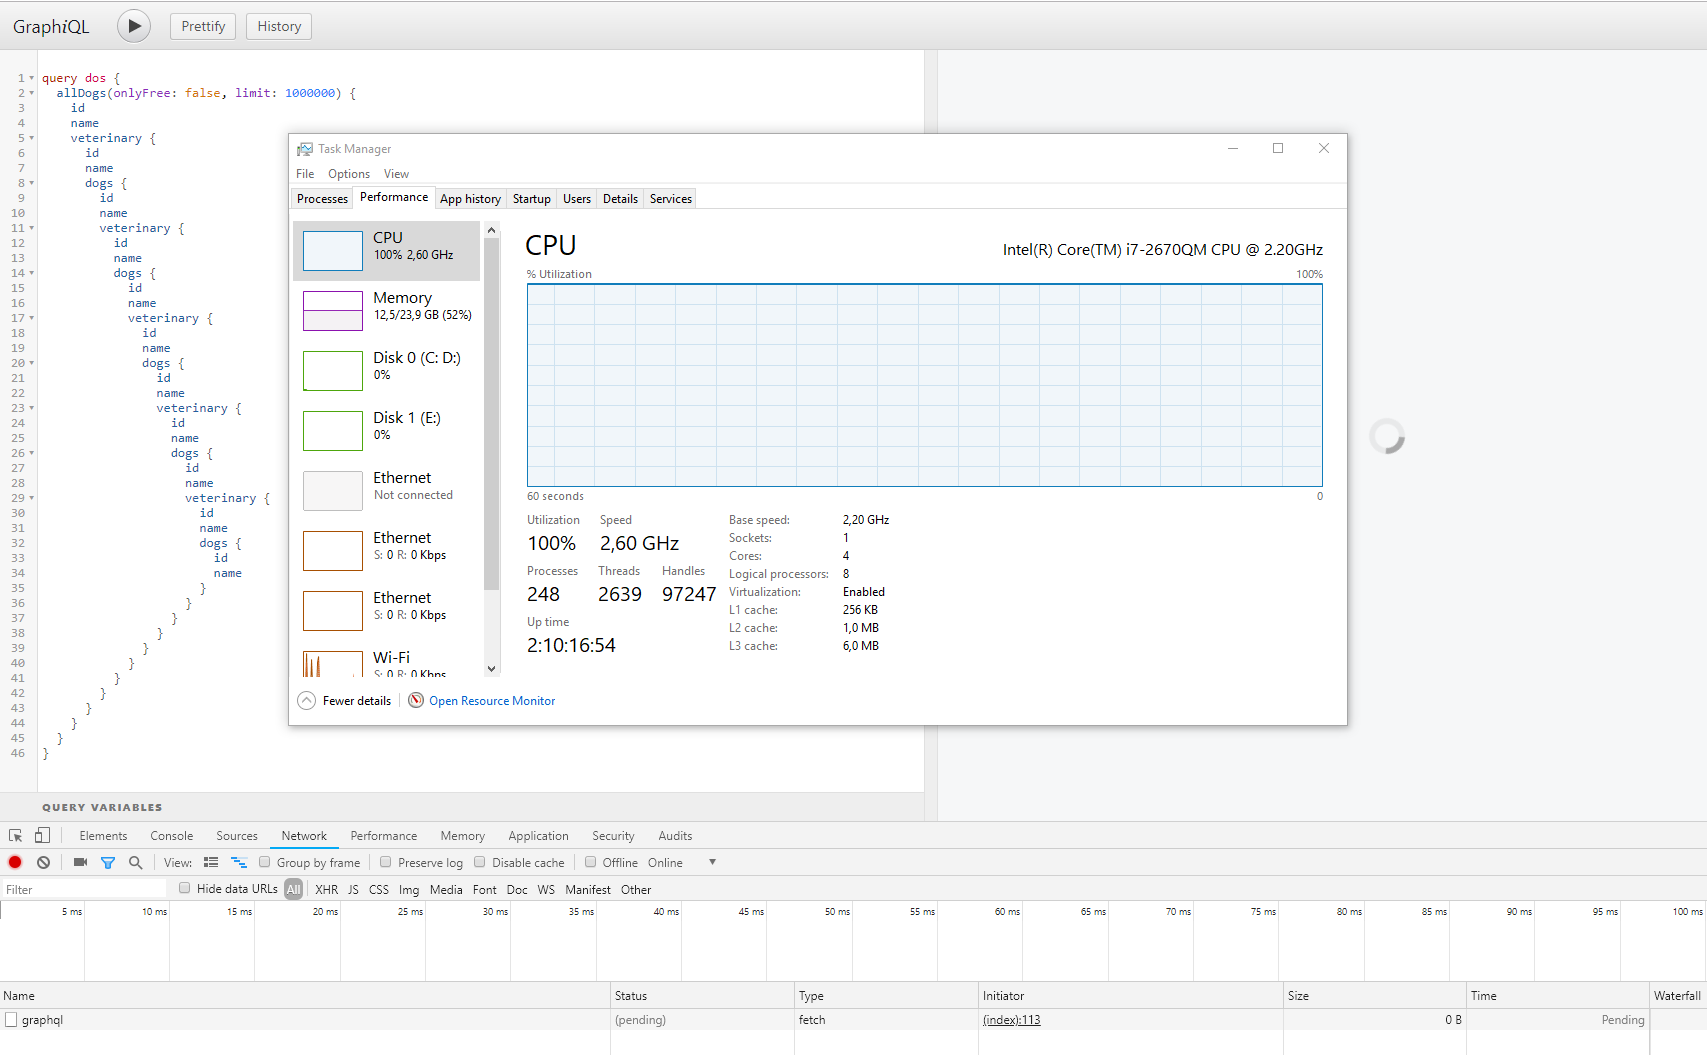 righettod/poc-graphql
Research on GraphQL from an AppSec point of view.
 kozmer/log4j-shell-poc
A Proof-Of-Concept for the CVE-2021-44228 vulnerability.
 tom0li/collection-document
Collection of quality safety articles. Awesome articles.
 warxim/vucsa
Deliberately vulnerable client-server application for learning penetration testing of non-HTTP thick clients. Includes challenges for SQL injection,…
 biitts/cve-2026-58138-conductor-unauth-rce
CVE-2026-58138 — Conductor (3.21.21..<3.30.2) unauthenticated RCE via INLINE GraalVM evaluator (HostAccess.ALL). Lab + PoC, verified e2e (root).
 bhanunamikaze/cve-2026-2587-exploit-poc
CVE-2026-2587 PoC validator for Eclipse GlassFish EL Injection RCE in the admin console gadget.jsf handler. Safe authenticated vulnerability scanner…
 aipeacs/sc3010-computer-security
Using Struts2 and PowerShell to recreate CVE-2017-5638 OGNL Injection vulnerability.