
cve-2023-50164
 aaronm-sysdig/cve-2023-50164
Demonstrates detection of CVE-2023-50164 (Apache Struts RCE) with a simple Java app, intended for security testing and educational purposes.
educationexploitationpenetration-testing+2
1
aaronm-sysdig/cve-2023-50164Demonstrates detection of CVE-2023-50164 (Apache Struts RCE) with a simple Java app, intended for security testing and educational purposes.
 datadavev/test-44228
Simple demo of CVE-2021-44228
 hunt3r850/cve-2024-10924-wordpress-docker
Dockerized exploit environment for CVE-2024-10924, an authentication bypass in WordPress Really Simple Security plugin (versions 9.0.0-9.1.1.1)…
 julesbsz/cve-2024-10924
POC for CVE-2024-10924 written in Python
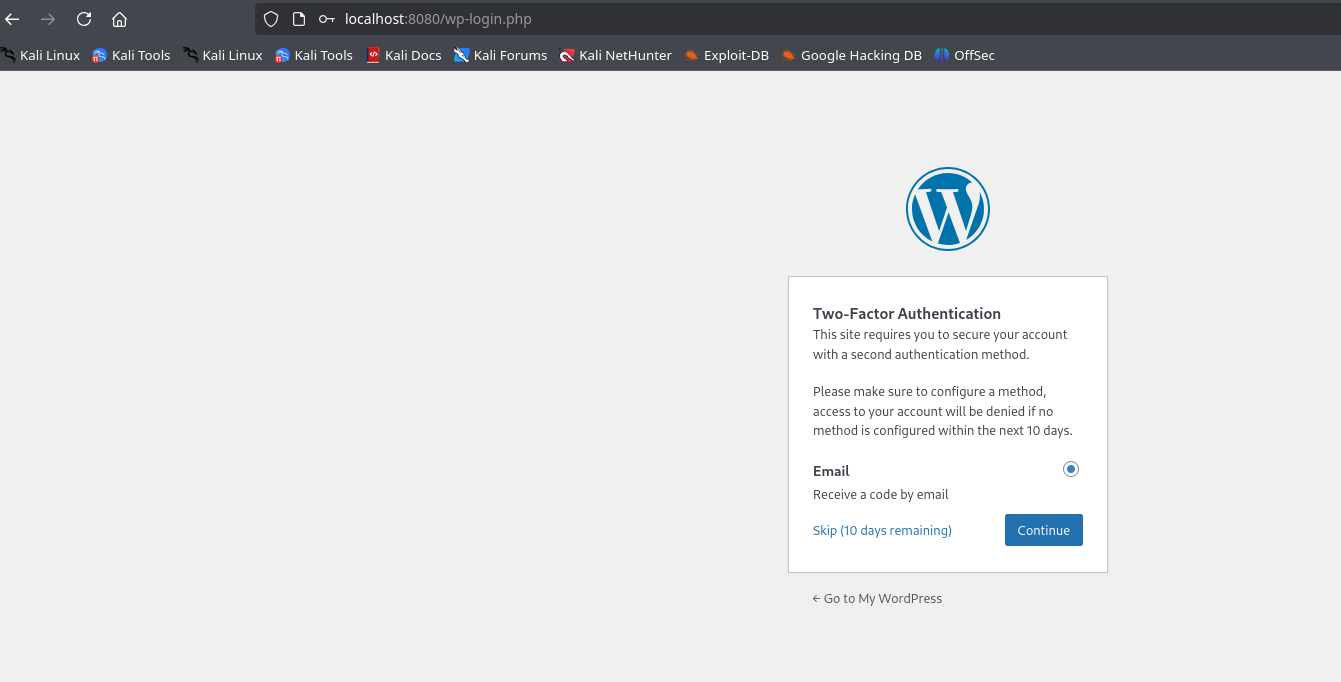 maalfer/cve-2024-10924-poc
Bypass del MFA en WordPress con el plugin Really Simple Security instalado entre las versiones 9.0.0 – 9.1.1.1.
 sariamubeen/cve-2024-10924
Python exploit for CVE-2024-10924 that bypasses Two-Factor Authentication in the Really Simple SSL WordPress plugin, enabling unauthorized…
 kazuya256/next-js-auth-bypass
🔓 Next.js Auth Bypass Demo - Educational application demonstrating CVE-2025-29927 middleware authentication bypass vulnerability . ⚠️ For…
 x3rx3ssec/cve-2022-0169
CVE-2022-0169 - WordPress Photo Gallery SQLi PoC
 brianwrf/s2-057-cve-2018-11776
A simple exploit for Apache Struts RCE S2-057 (CVE-2018-11776)
 g0vguy/cve-2025-61922-poc
A simple, educational proof-of-concept script demonstrating the zero-click account takeover vulnerability in the PrestaShop Checkout module…
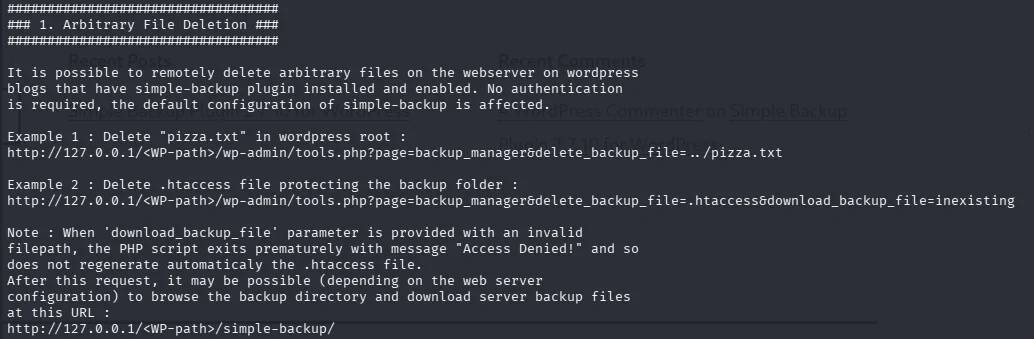 capivara-research/wordpress-path-traversal-cve-2019-11447
Detailed penetration test report demonstrating unauthenticated path traversal (CVE-2019-11447) in WordPress Simple Backup plugin, including…
 0xgh057r3c0n/cve-2025-34085
WordPress Simple File List Unauthenticated RCE Exploit
 wildwestcybersecurity/cve-2019-5420-poc
cve-2019-5420 POC simple ruby script
 ademto/wordpress-cve-2024-10924-pentest
Penetration testing report and exploit for CVE-2024-10924, a 2FA bypass in Really Simple SSL, including reconnaissance, exploitation, and remediation…
 jagdeepsinghceh/cms-made-simple-python3
Python3-converted exploit and research notes for CMS Made Simple (CVE-2019-9053) — Unauthenticated SQL Injection vulnerability. Includes original…
 kelvinwin10/cve-2017-7921-rewrite
simple CVE-2017-7921 rewrite in python by me. for educational purposes only!
 flaviupopescu/cve-2022-28986
A Insecure direct object references (IDOR) vulnerability in "Simple 2FA Plugin for Moodle" by LMS Doctor
 itzr1g/cve-2019-9053
Python exploit for CVE-2019-9053 targeting CMS Made Simple with SQL injection detection and password hash cracking via wordlist, featuring argparse…