
PaperCut-Authentication_Bypass_and_RCE
 joaoaugustom/papercut-authentication_bypass_and_rce
This exploit is based on CVE-2023-27350 and was built upon the original exploit by horizon3ai and the Metasploit module.
authenticationeducationexploitation+5
joaoaugustom/papercut-authentication_bypass_and_rceThis exploit is based on CVE-2023-27350 and was built upon the original exploit by horizon3ai and the Metasploit module.
 yashswarup12/cve-2021-27877-poc
A modified version of the Rapid7 Metasploit module for CVE-2021-27877 that supports direct command execution for reliable vulnerability validation.…
 joaoaugustom/drupal_rest-rce_unauthenticated
This exploit is based on CVE-2019-6340 and was built upon the original exploit by leonjza and the Metasploit module, extending it can be executed…
 mkps/cve-2026-38751-openstamanager-arbitrary-file-upload-poc
This repository contains a proof-of-concept (PoC) exploit for CVE-2026-38751, affecting OpenSTAManager ≤ 2.10. The vulnerability allows an…
 tieupham267/log4shell-coraza
Log4Shell (CVE-2021-44228) defense lab — nginx + Coraza WAF dynamic module + OWASP CRS v4. Educational use only.
 alvaroguzmancode/cve-2026-31431-mitigacion
Technical analysis of CVE-2026-31431, a Linux kernel local privilege escalation in the algif_aead module, including root cause, affected versions,…
 supermagnum/gr-qradiolink
GNU Radio out-of-tree (OOT) module for QRadioLink blocks.
 mrowkoob/cve-2023-33538-msf
CVE-2023-33538 - TP-Link Command Injection Ruby module for Metasploit Framework
 bohemianhacks/cve-2024-21534-poc
Proof-of-concept exploit for CVE-2024-21534, a critical RCE in jsonpath-plus, demonstrating arbitrary code execution via the VM module and providing…
 aniket2912/internal-network-penetration-testing
Educational module on internal network penetration testing: methodology, attack vectors, enumeration, exploitation, privilege escalation, and…
 adel-hx0d/cve-2025-59287
Exploitation toolkit for CVE-2025-59287 RCE in WSUS. Includes AES payload encryption and an exploitation module for authorized penetration testing.
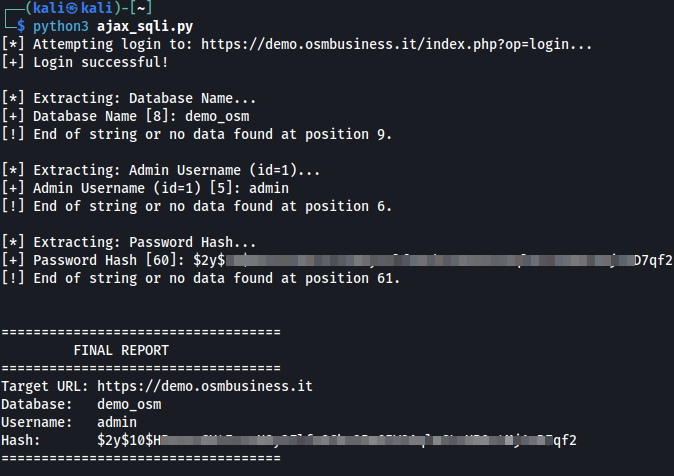 lukasz-rybak/cve-2026-24416
CVE-2026-24416 - OpenSTAManager has a Time-Based Blind SQL Injection in Article Pricing Module
 joaomorenorf/cve-2014-3704
This code is taken from "Drupal 7.0 < 7.31 - 'Drupalgeddon' SQL Injection (Add Admin User)" and was converted to Python 3 to suit the exercise in…
 lukasz-rybak/cve-2026-24418
CVE-2026-24418 - OpenSTAManager has a SQL Injection vulnerability in the Scadenzario bulk operations module
 mrowkoob/cve-2025-26466-msf
CVE-2025-26466 - SSH Ping DoS Ruby module for Metasploit Framework
 morphine009/cve-2025-46157
Proof-of-concept exploit for CVE-2025-46157: Remote code execution via insecure file upload in Timetrax V1 Attendance module, with EfsPotato-based…
 dotadrien/cve-2025-60656
Stored XSS vulnerability proof-of-concept for Script Pag's 'Recent Ads' module, exploiting unsanitized double quotes in image URL fields to execute…
 d3vn0mi/cve-2025-4138-poc
Python PoC for CVE-2025-4138, a path traversal in Python's tarfile module abusing symlink chains to bypass PATH_MAX for arbitrary file write