
CVE-2021-43141
 jeromeyoung/cve-2021-43141
Information about CVE-2021-43141, a reflected XSS in the plan_application section.
educationpapers-researchvulnerability-analysis+2
jeromeyoung/cve-2021-43141Information about CVE-2021-43141, a reflected XSS in the plan_application section.
 devengpk/cve-2022-22965
Dockerized Spring4Shell (CVE-2022-22965) proof-of-concept with Python exploit script and webshell deployment for educational vulnerability testing.
 wajda/log4shell-test-exploit
Test exploit of CVE-2021-44228
 axelcurmi/log4shell-docker-lab
Log4Shell (CVE-2021-44228) docker lab
 pwnxpl0it/react2shell-lab
React2shell vulnerable lab (CVE-2025-55182)
 huynguyen12536/cve-2025-2995
Reproduction of CVE-2025-29927 authorization bypass in Next.js middleware, with curl-based exploitation payloads for multiple versions.
 performant-labs/cve-2024-22262
Proof-of-concept exploit for CVE-2024-22262 in Spring applications, with a Dev Container environment for hands-on vulnerability exploration and…
 snicoll-scratches/spring-boot-cve-2022-22965
Showcase of overridding the Spring Framework version in older Spring Boot versions
 astrowmist/poc-cve-2016-10033
Proof Of Concept for the CVE-2016-10033 (PHPMailer)
 all3njk/nextjs_cve-2025-29927
Demonstrates the x-middleware-subrequest header bypass in Next.js 13.4.19, allowing unauthorized access to protected routes. Includes setup, normal…
 mbadanoiu/mal-011
MAL-011: Log4J Misconfiguration Allows Malicious JavaScript in Red Hat AMQ
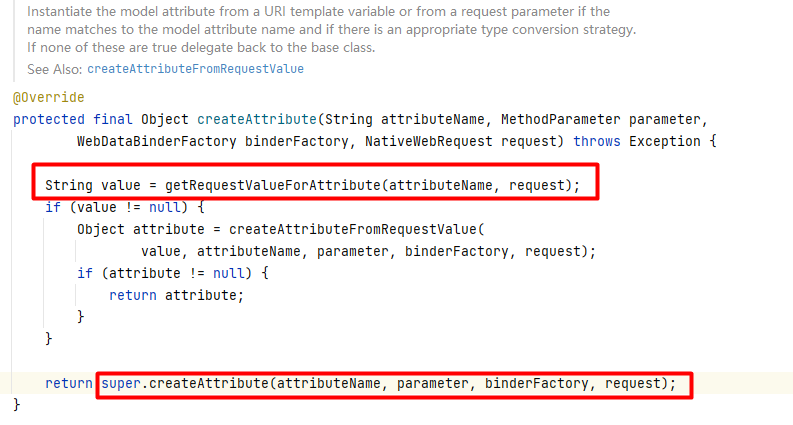 enokiy/spring-rce-cve-2022-22965
Educational analysis and proof-of-concept exploit for CVE-2022-22965, a Spring MVC/WebFlux remote code execution vulnerability via data binding on…
 kavidk/cve-2019-6447-in-mobile-application
Research report detailing CVE-2019-6447 exploitation in real-world mobile applications, including practical examples and a demonstration video.
 necroteddy/cve-2022-42889
docker for CVE-2022-42889
 war4uthor/cve-2021-40513
CVE-2021-40513 OSCAR McMaster 19.40~1235 Reflected Cross Site Scripting Vulnerability.
 z3usx01/cve-2025-0054
Lightweight Python scanner for detecting stored XSS (CVE-2025-0054) in SAP NetWeaver Java. Submits customizable payloads and checks for script…
 stefandorresteijn/cve-2021-39408
XSS vulnerability in Online Student Rate System1.0